chore(deps): bump source-map-js from 1.2.1 to 1.2.2 - #2791
Conversation


 dependabot
Bot
added
dependencies


There was a problem hiding this comment.
LGTM: No qualifying code-review defects in the dependency patch; known screenshot drift still needs regeneration and green CI.
Note
Approved · head b8d5d9d · no findings
Full review
No code-review findings; the coding leg still needs to run npm run screenshots:gen and restore green CI, preserving the dependency update and hash guard.


Bumps [source-map-js](https://github.com/7rulnik/source-map-js) from 1.2.1 to 1.2.2.
- [Release notes](https://github.com/7rulnik/source-map-js/releases)
- [Changelog](https://github.com/7rulnik/source-map-js/blob/main/CHANGELOG.md)
- [Commits](7rulnik/source-map-js@v1.2.1...v1.2.2)

Co-Authored-By: coreplane-switchboard[bot] <318072483+coreplane-switchboard[bot]@users.noreply.github.com>

---
updated-dependencies:
- dependency-name: source-map-js
  dependency-version: 1.2.2
  dependency-type: indirect
...

Signed-off-by: dependabot[bot] <[email protected]>

Co-Authored-By: coreplane-switchboard[bot] <318072483+coreplane-switchboard[bot]@users.noreply.github.com>

b8d5d9d to
4155d11
Compare

|
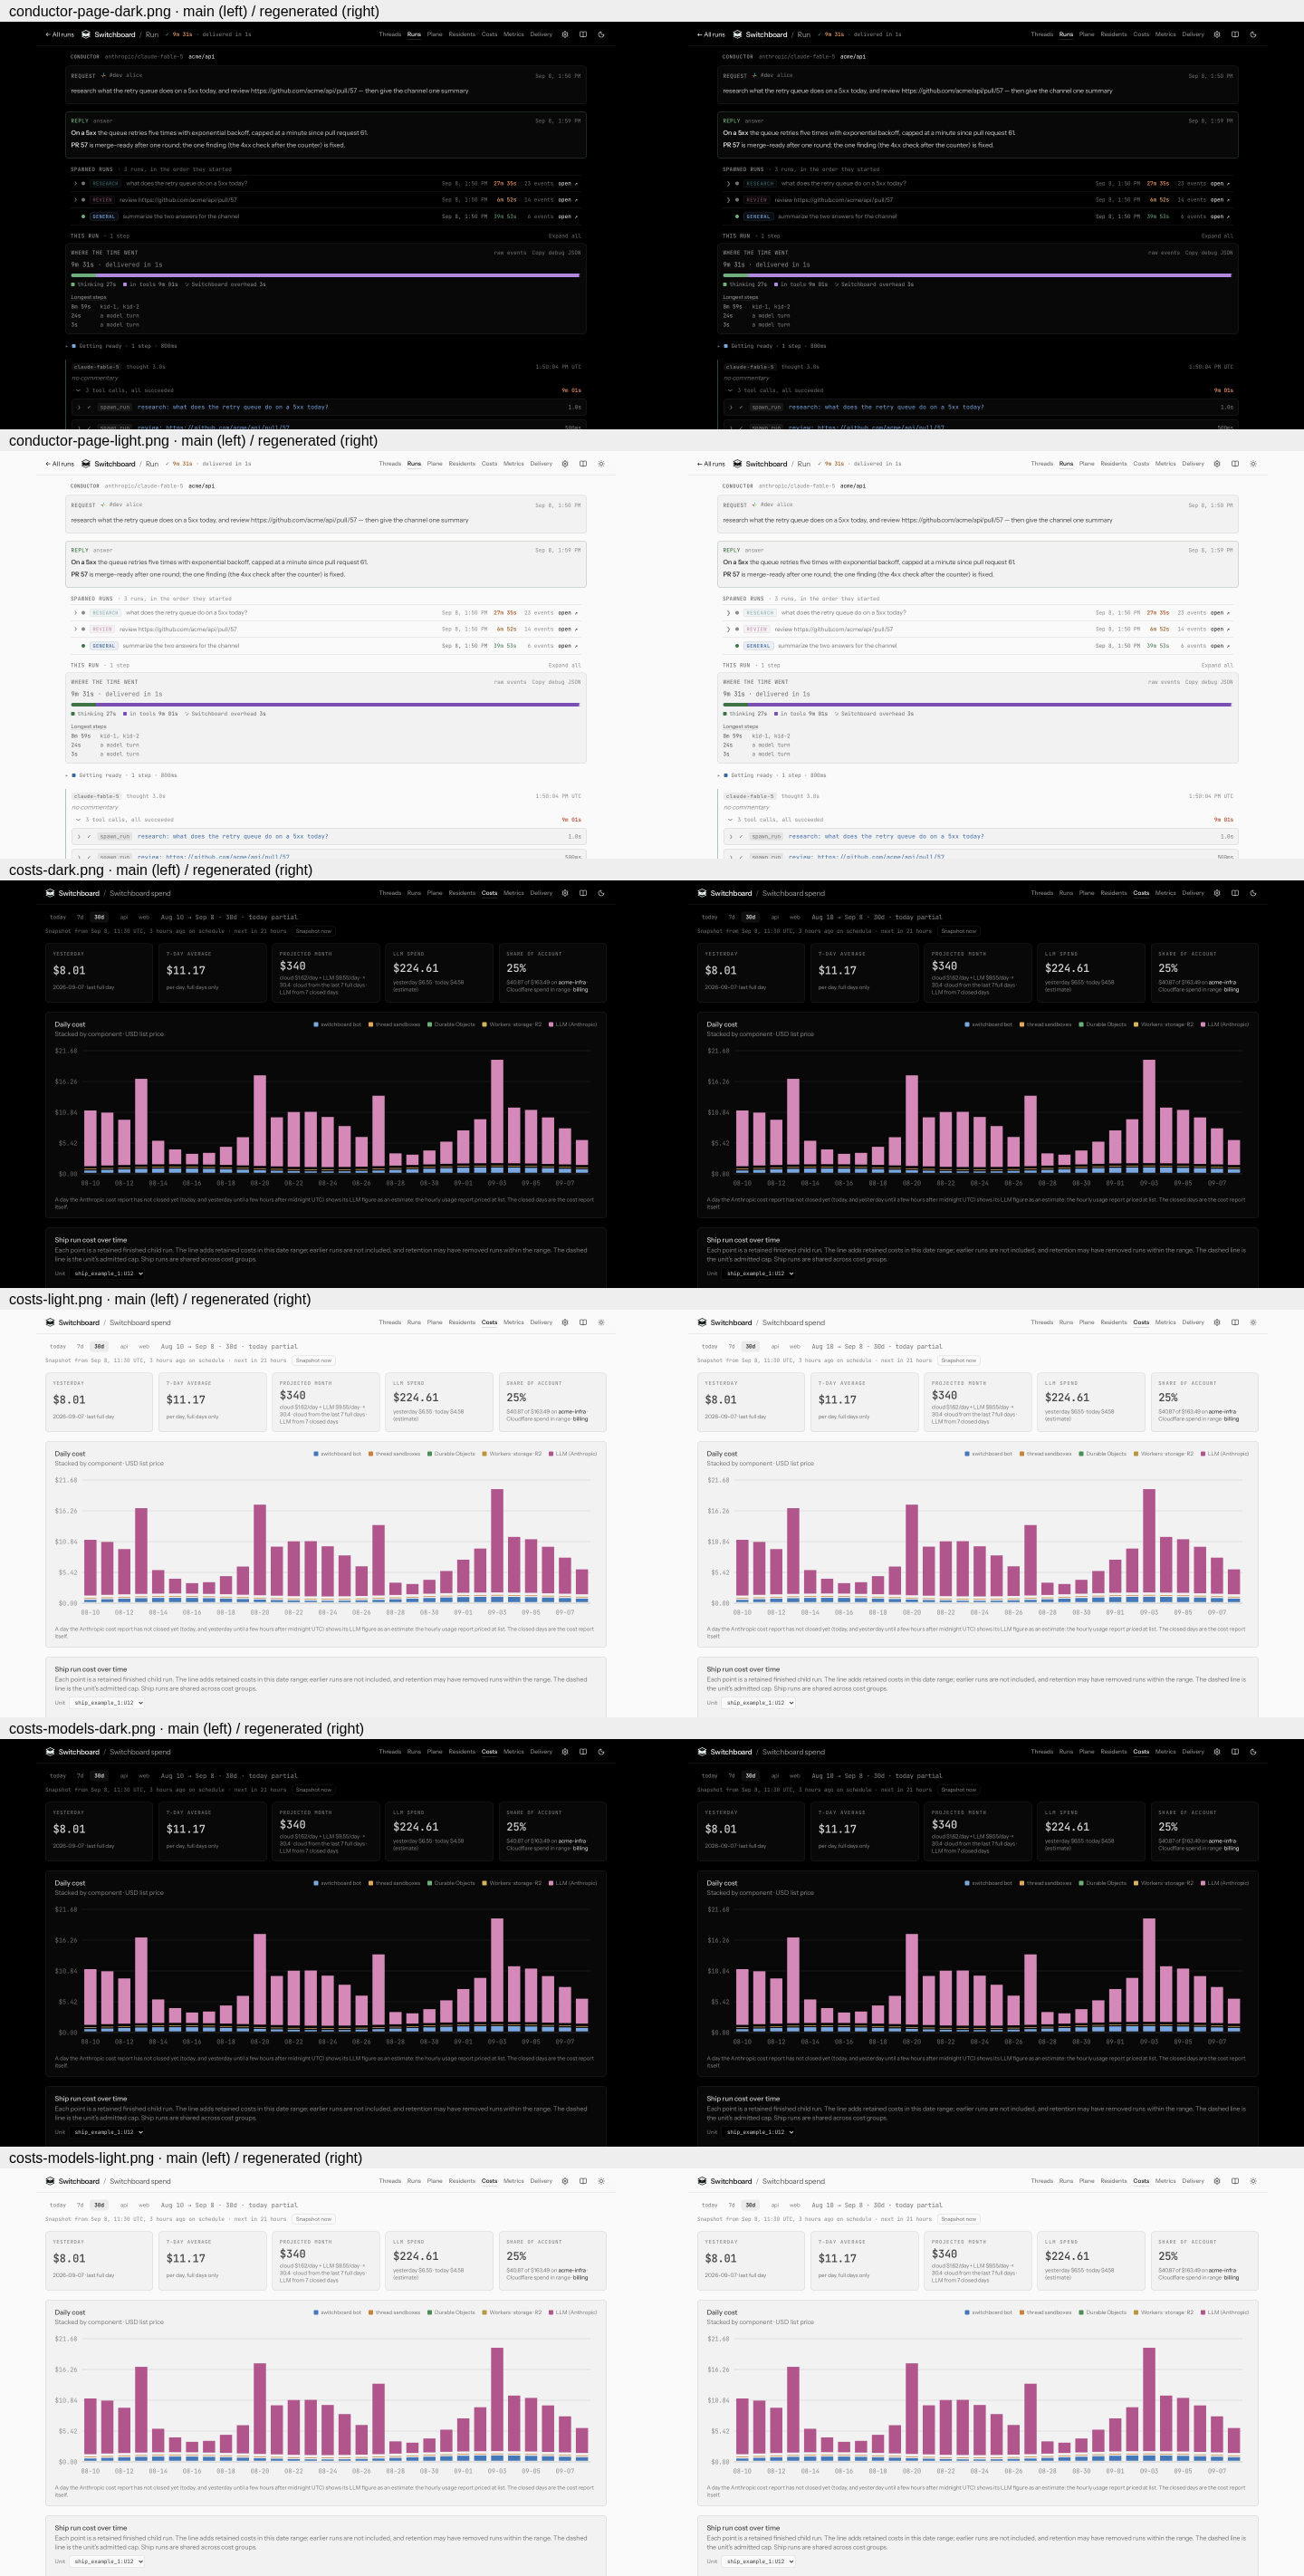
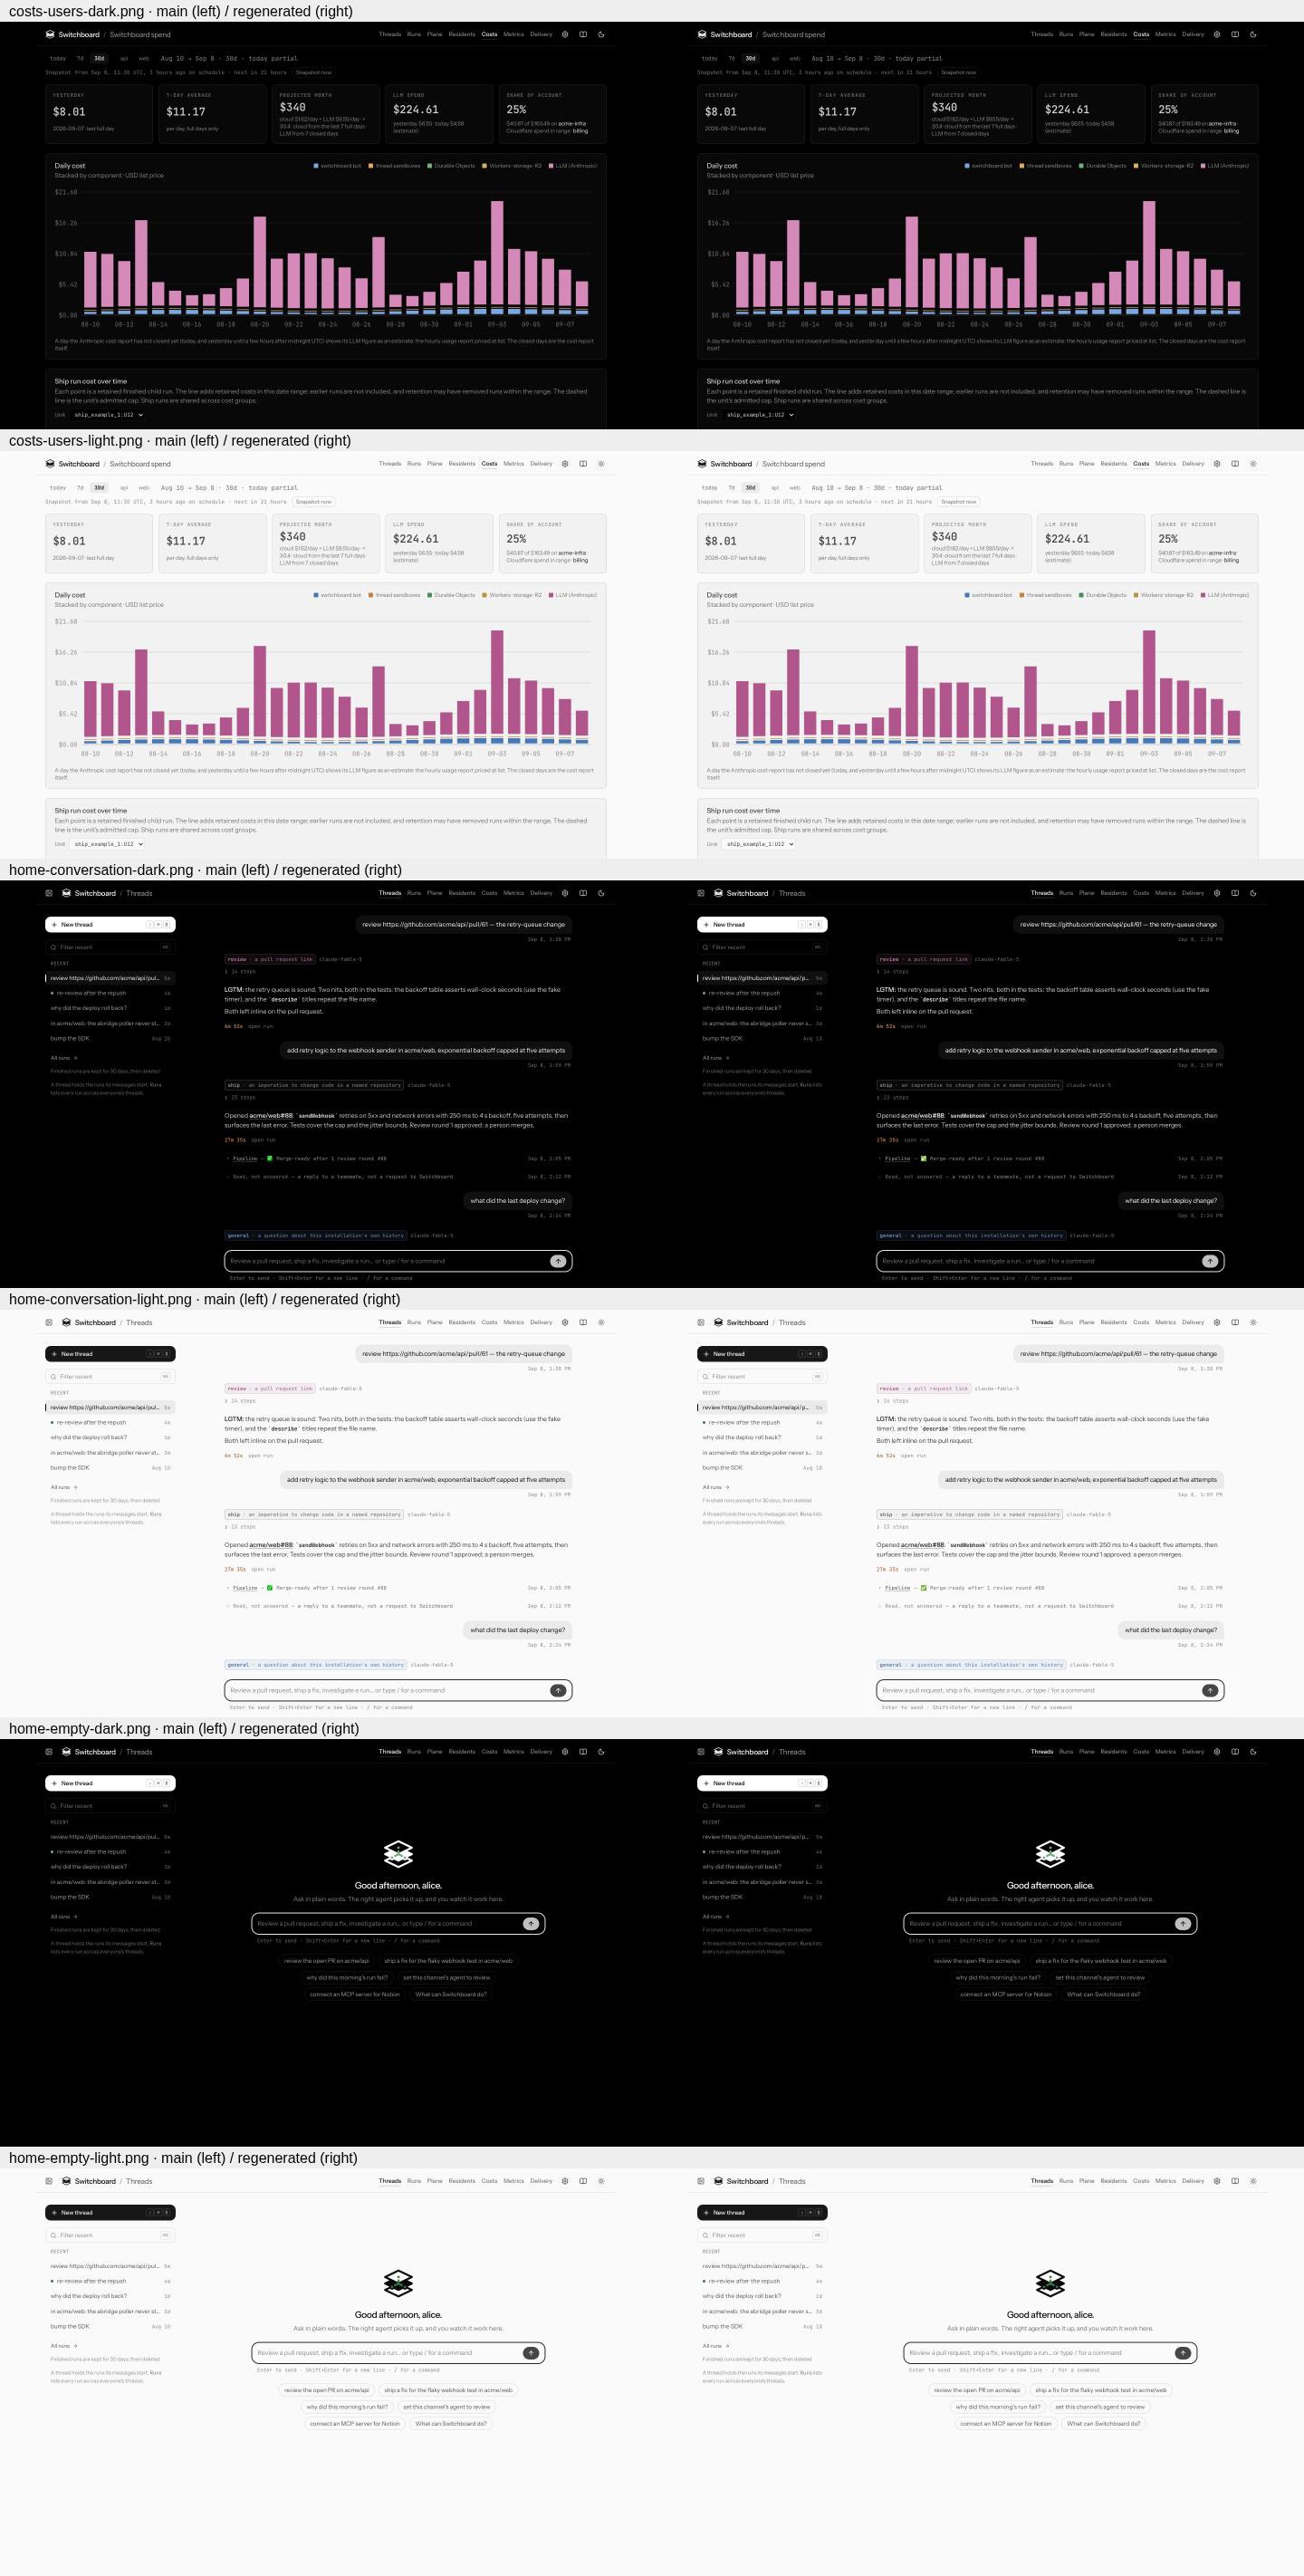
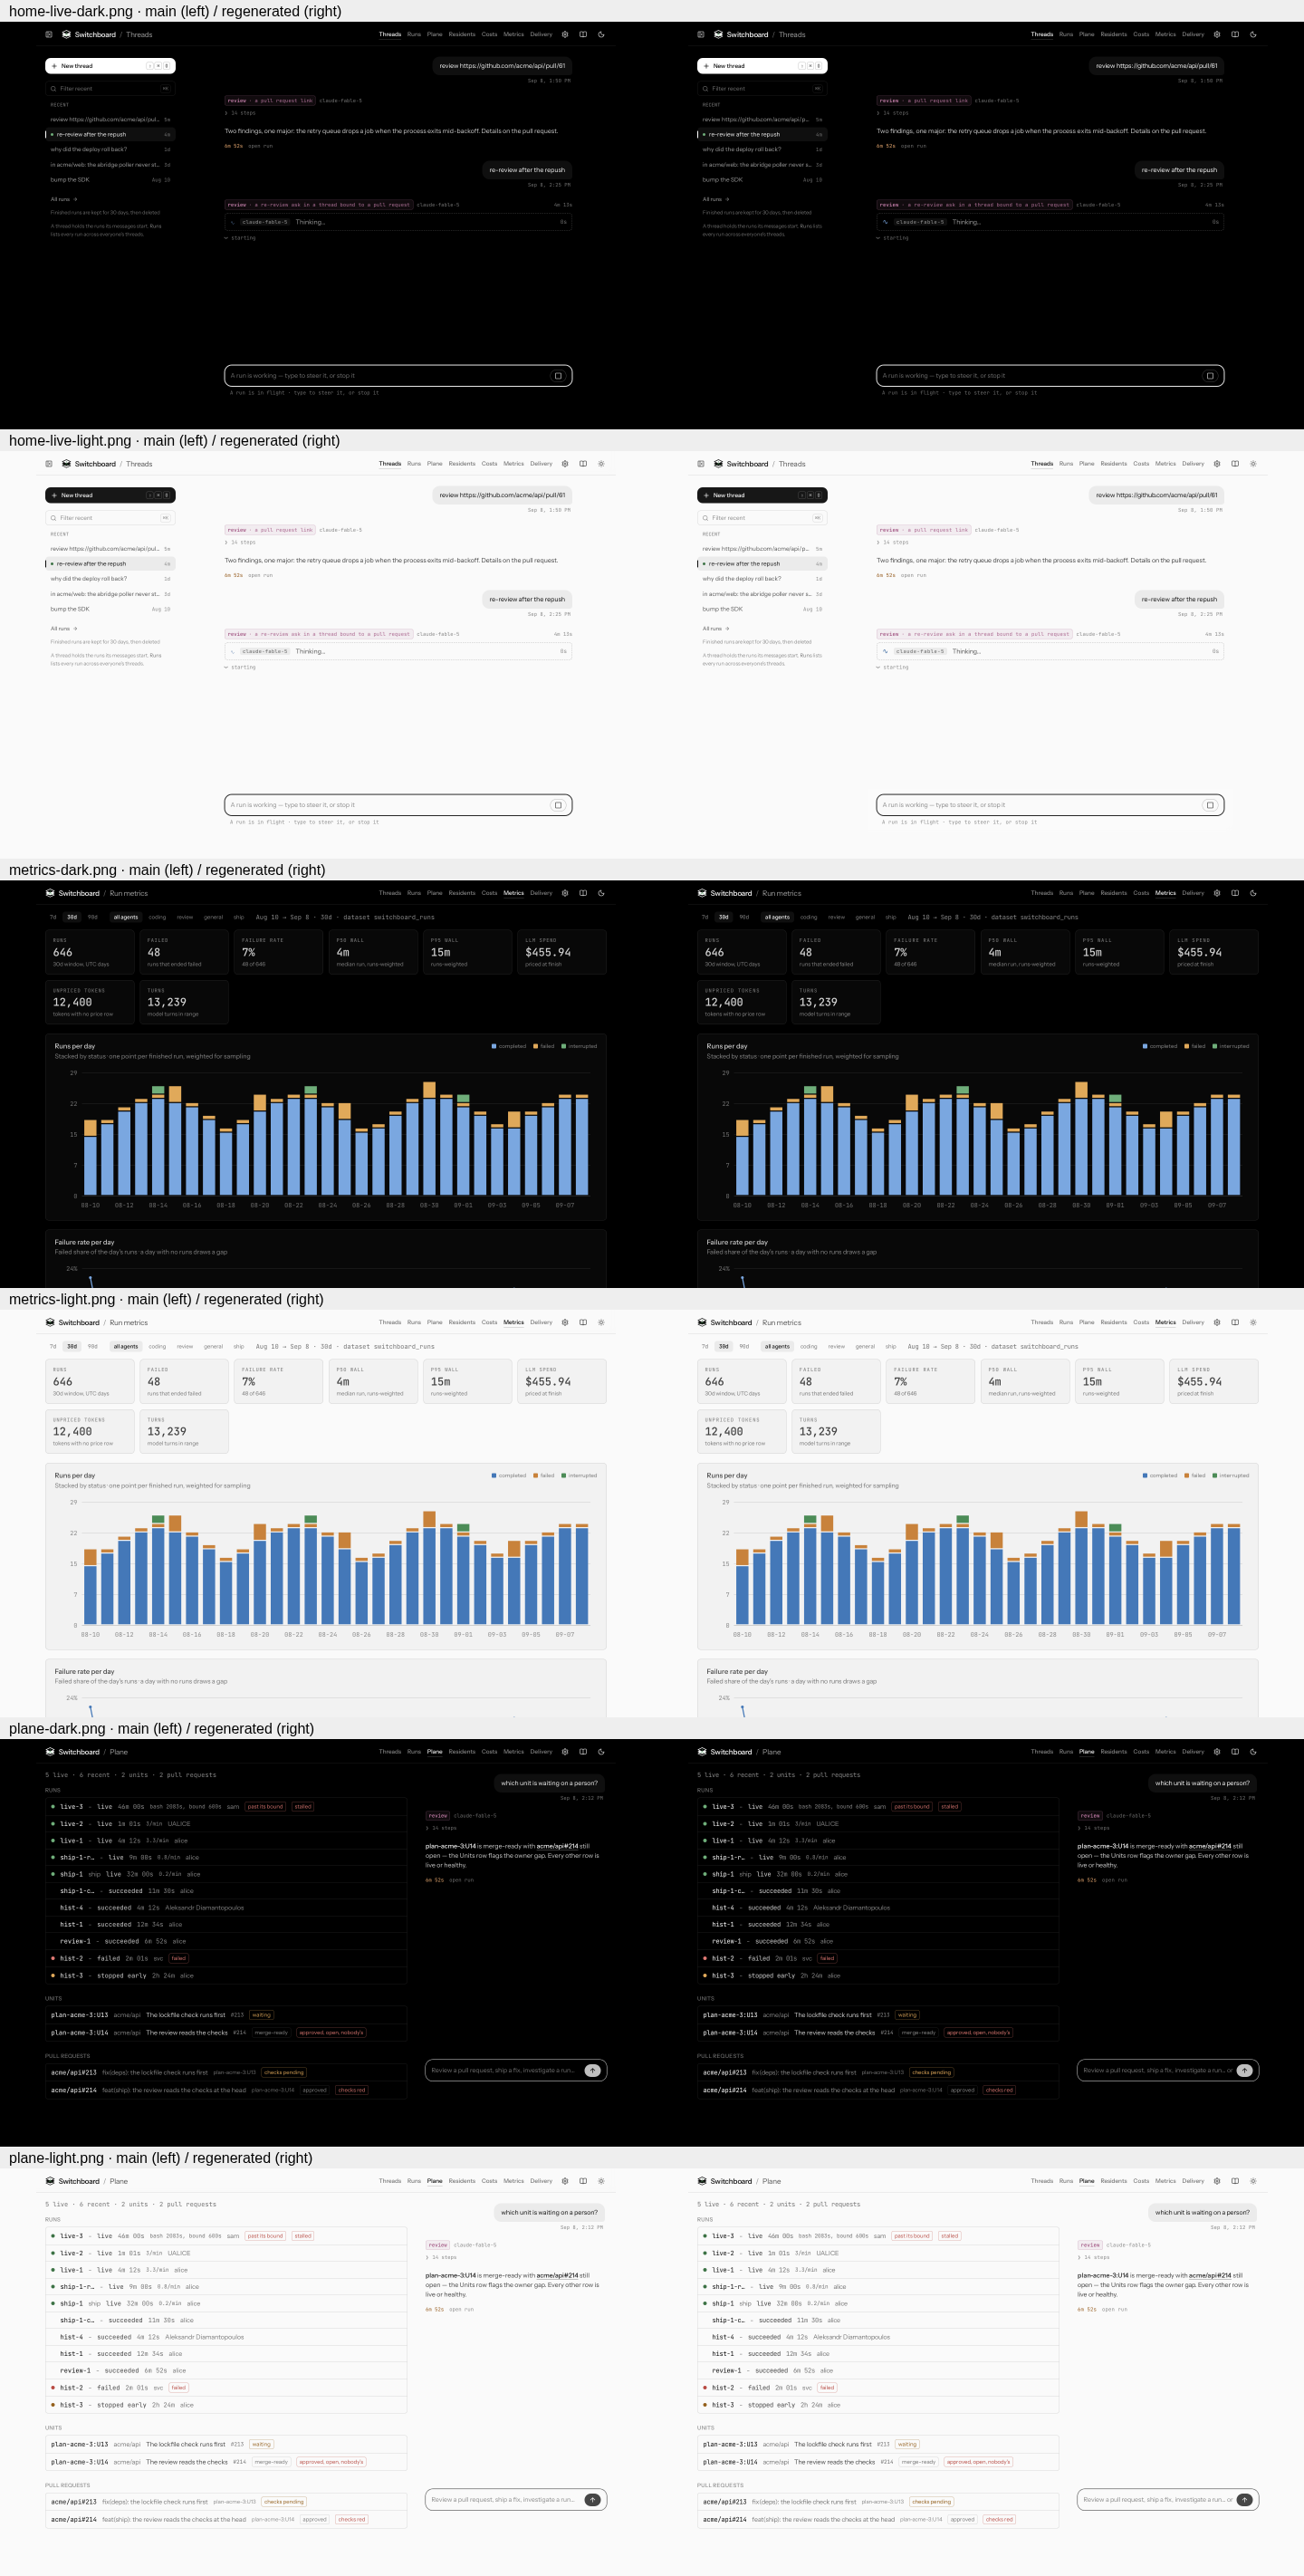
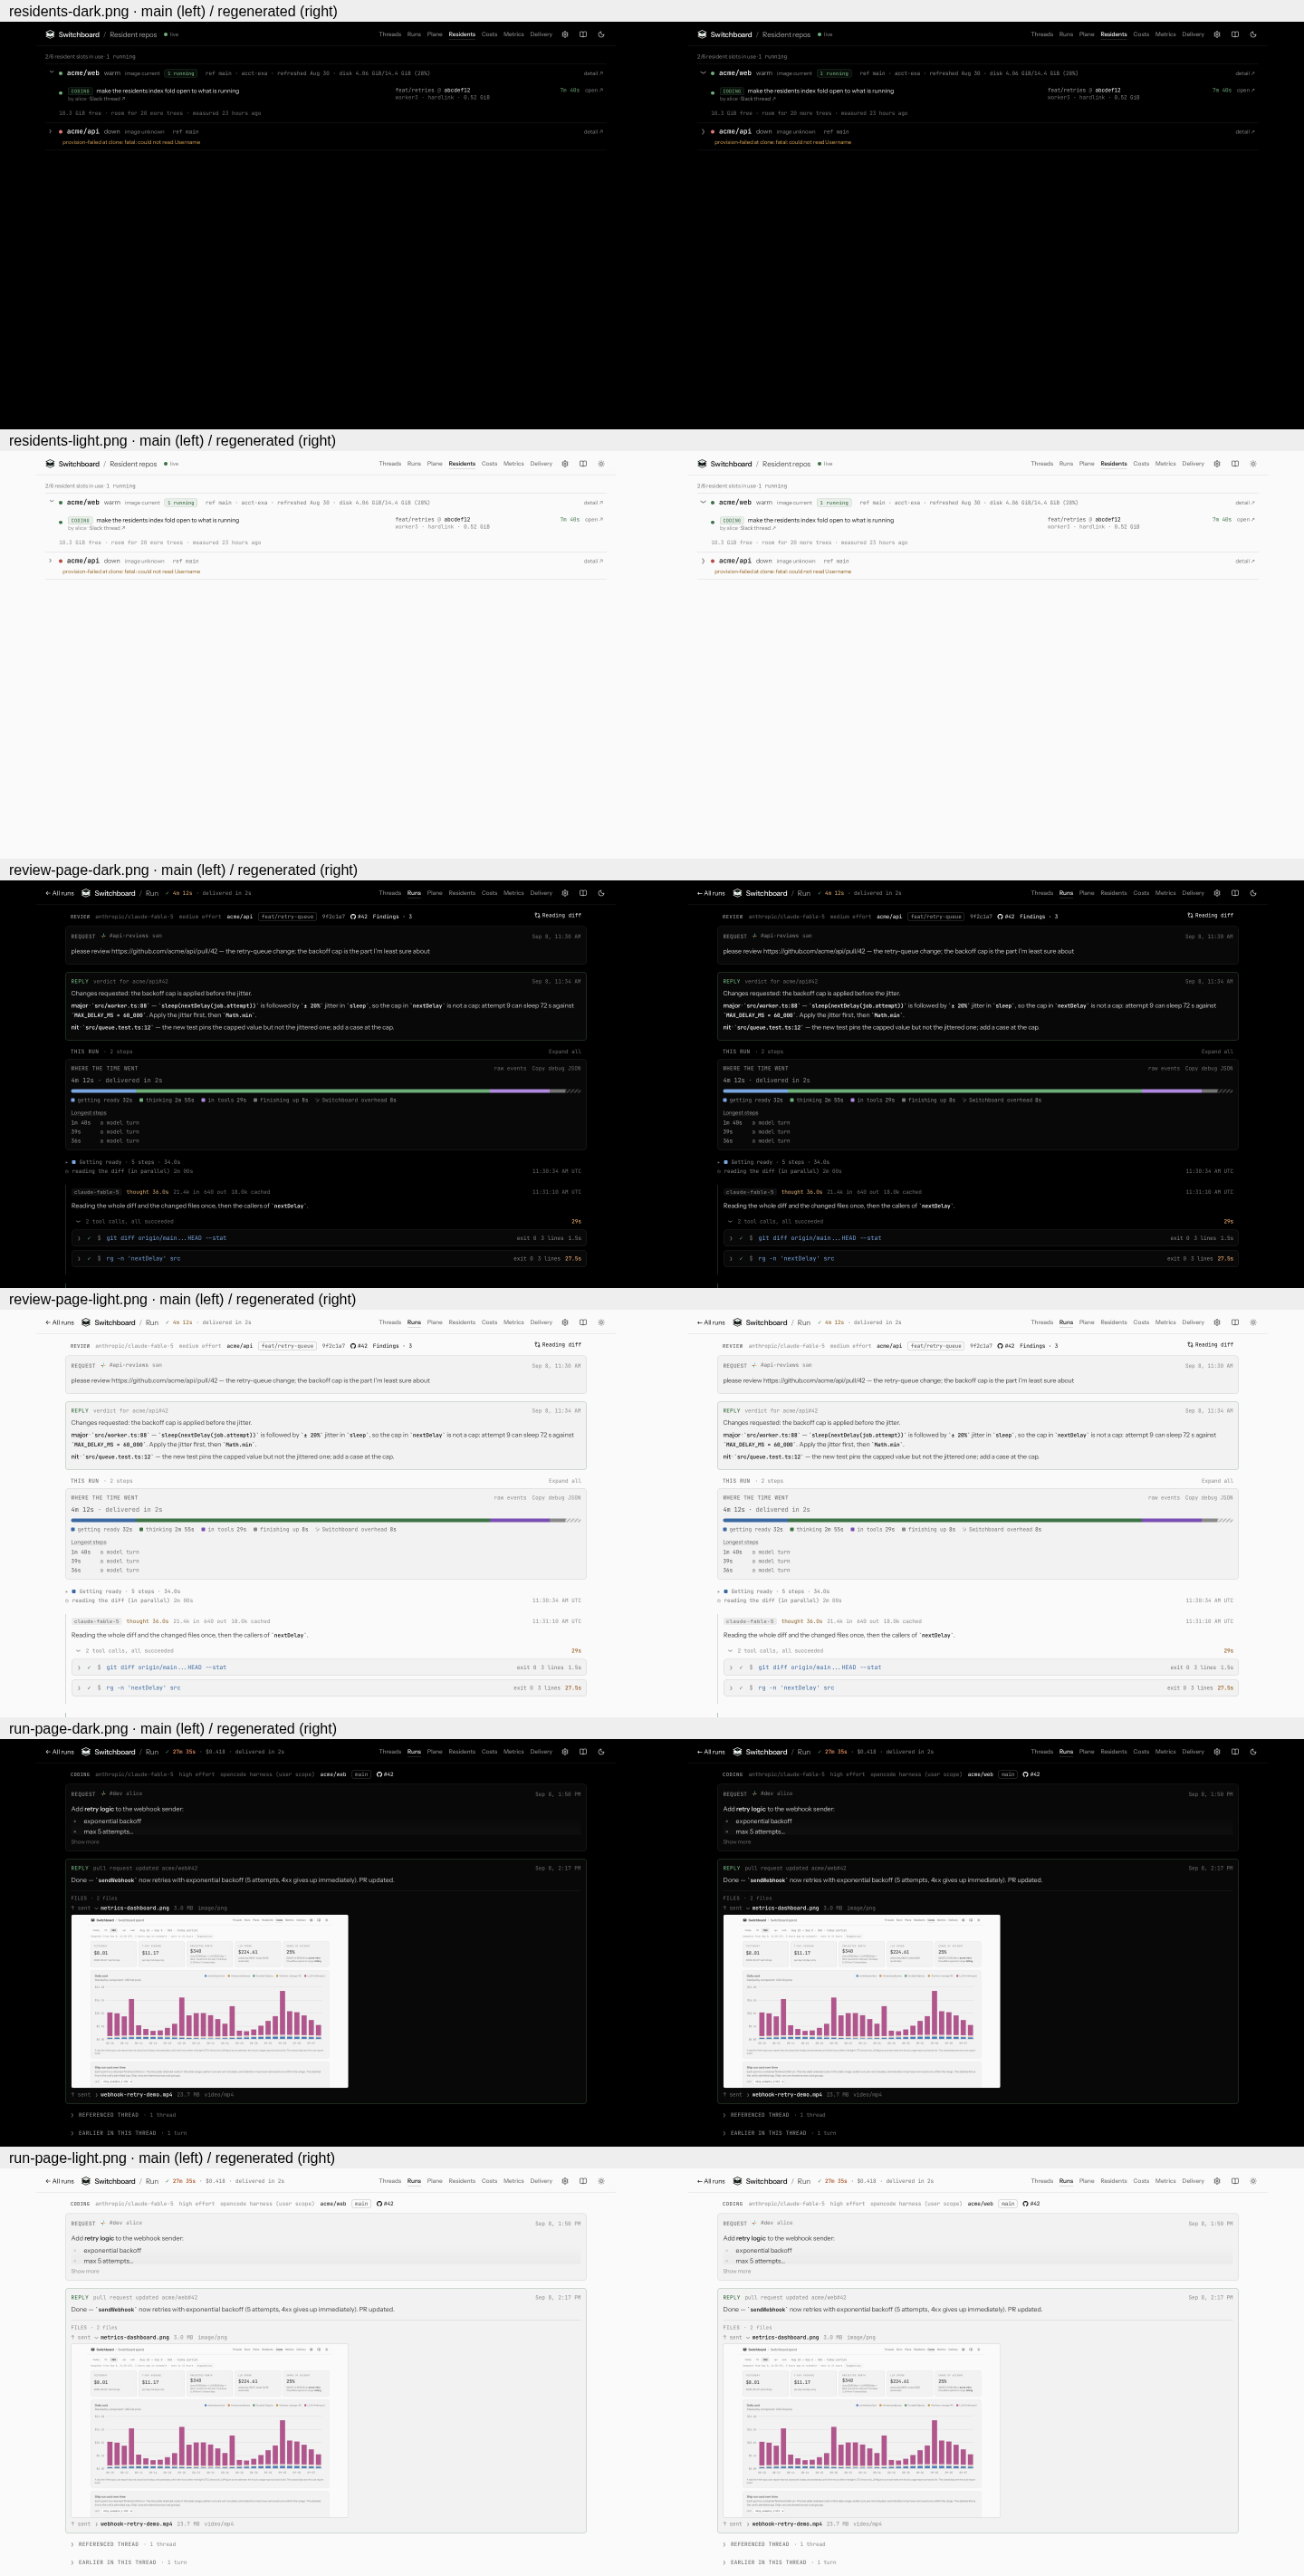
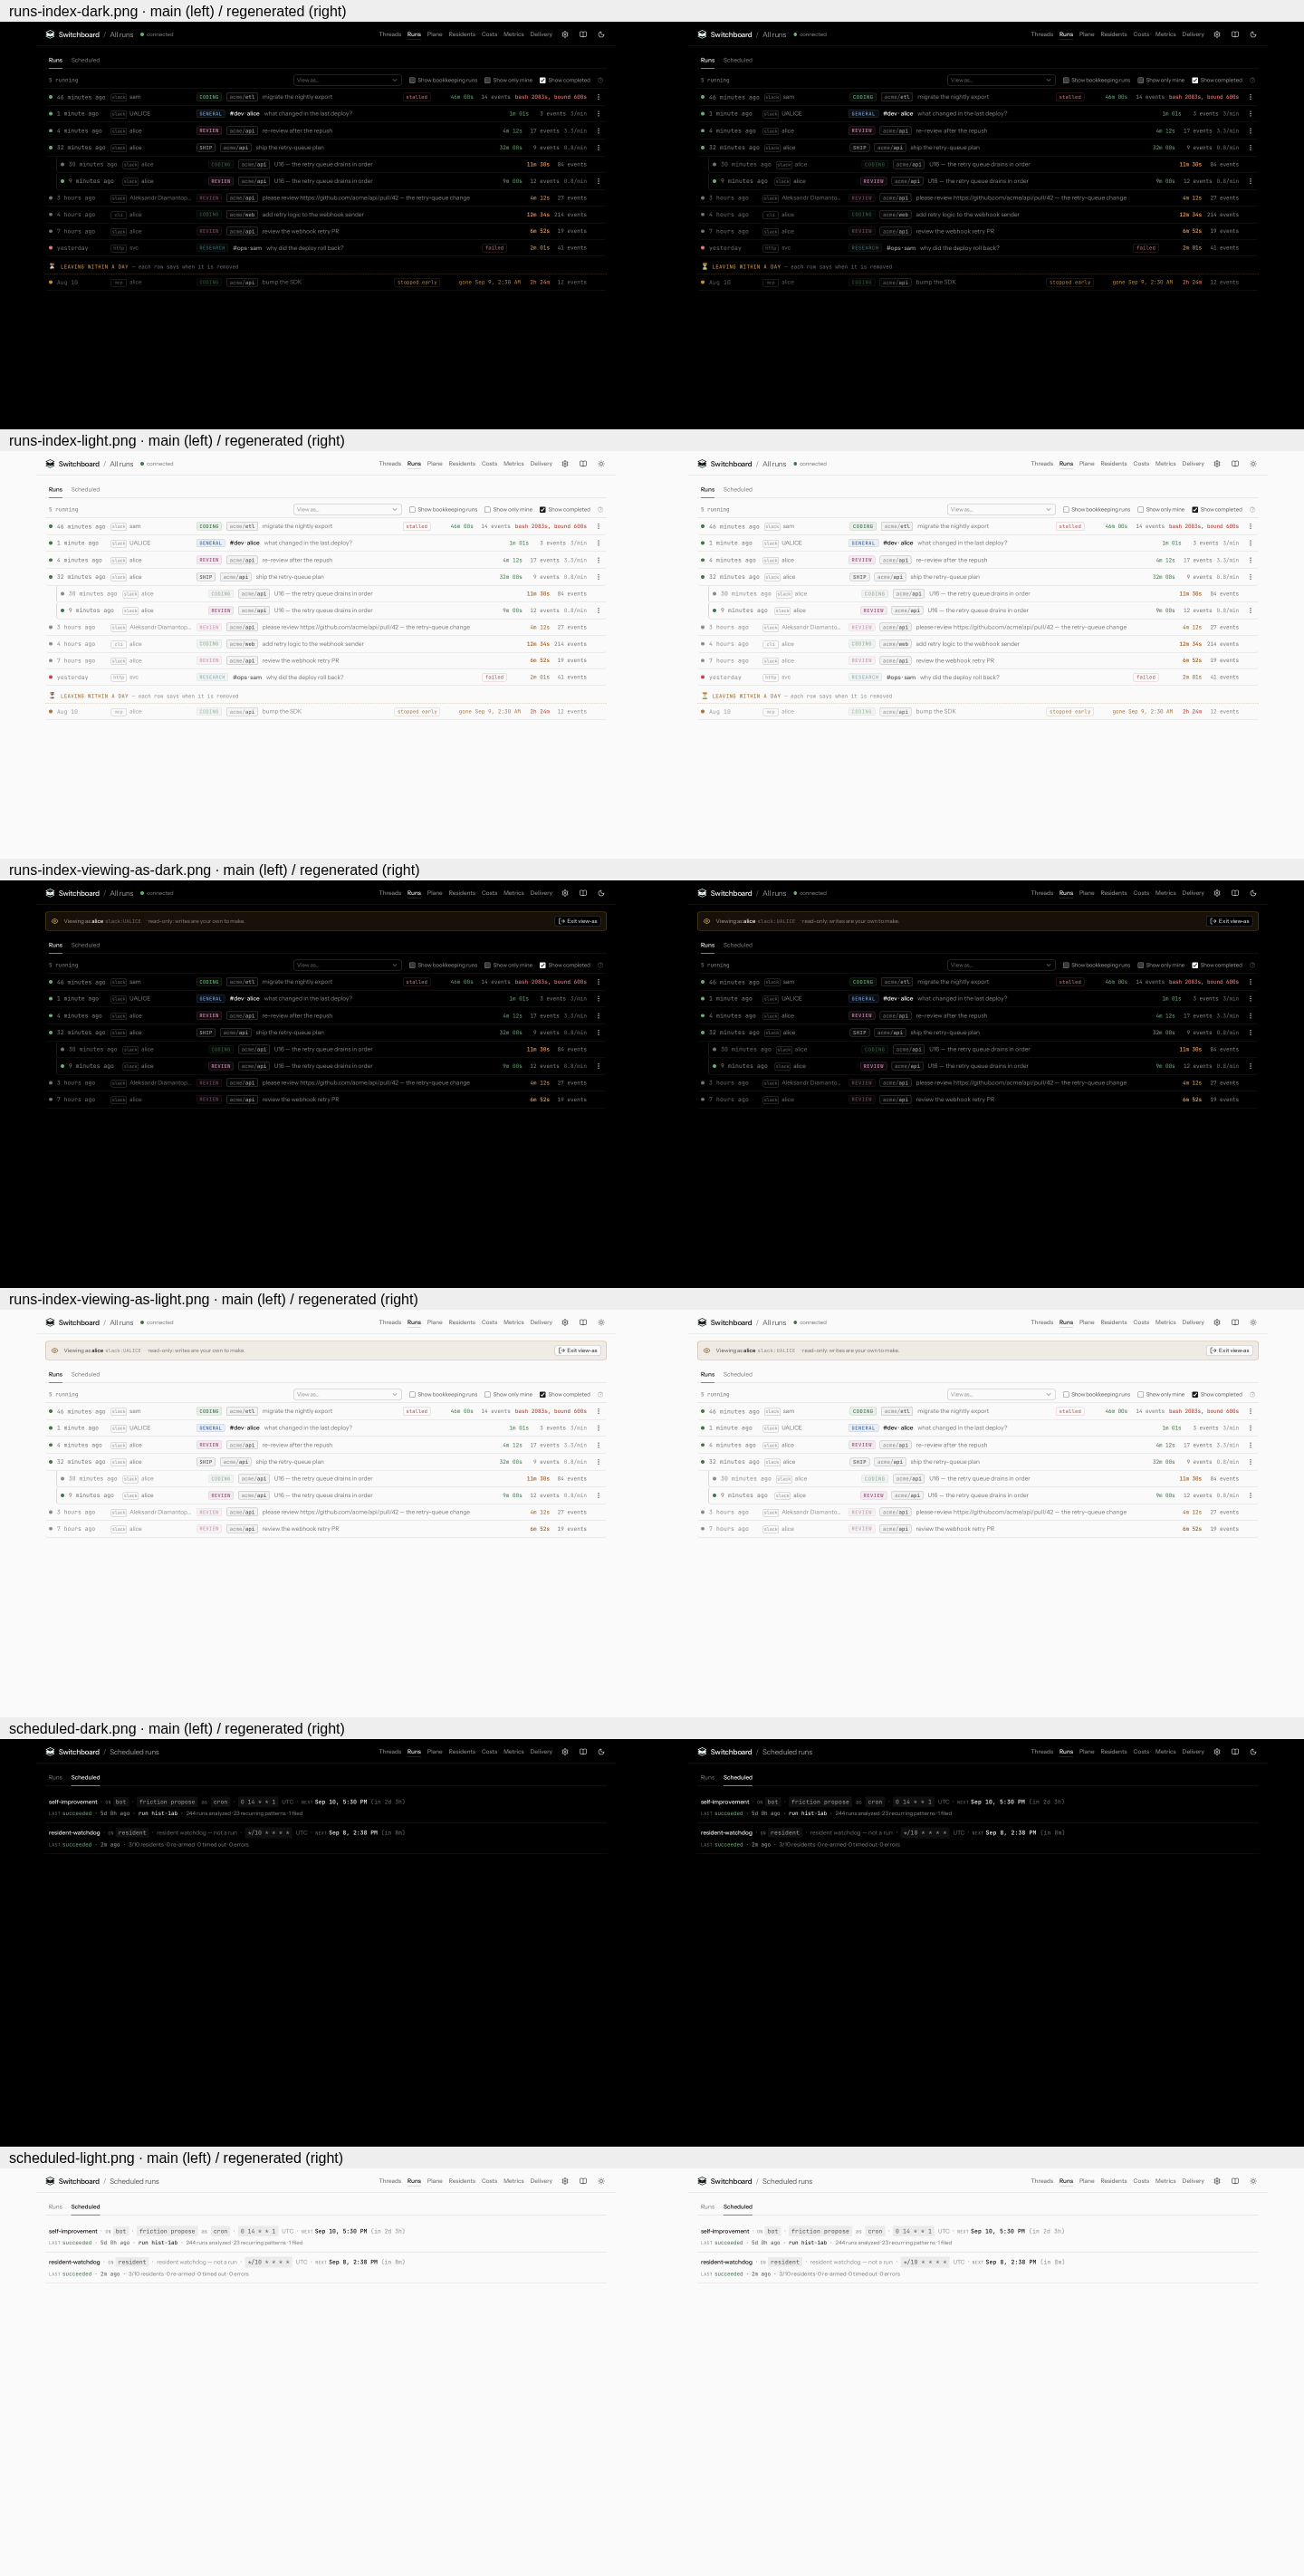
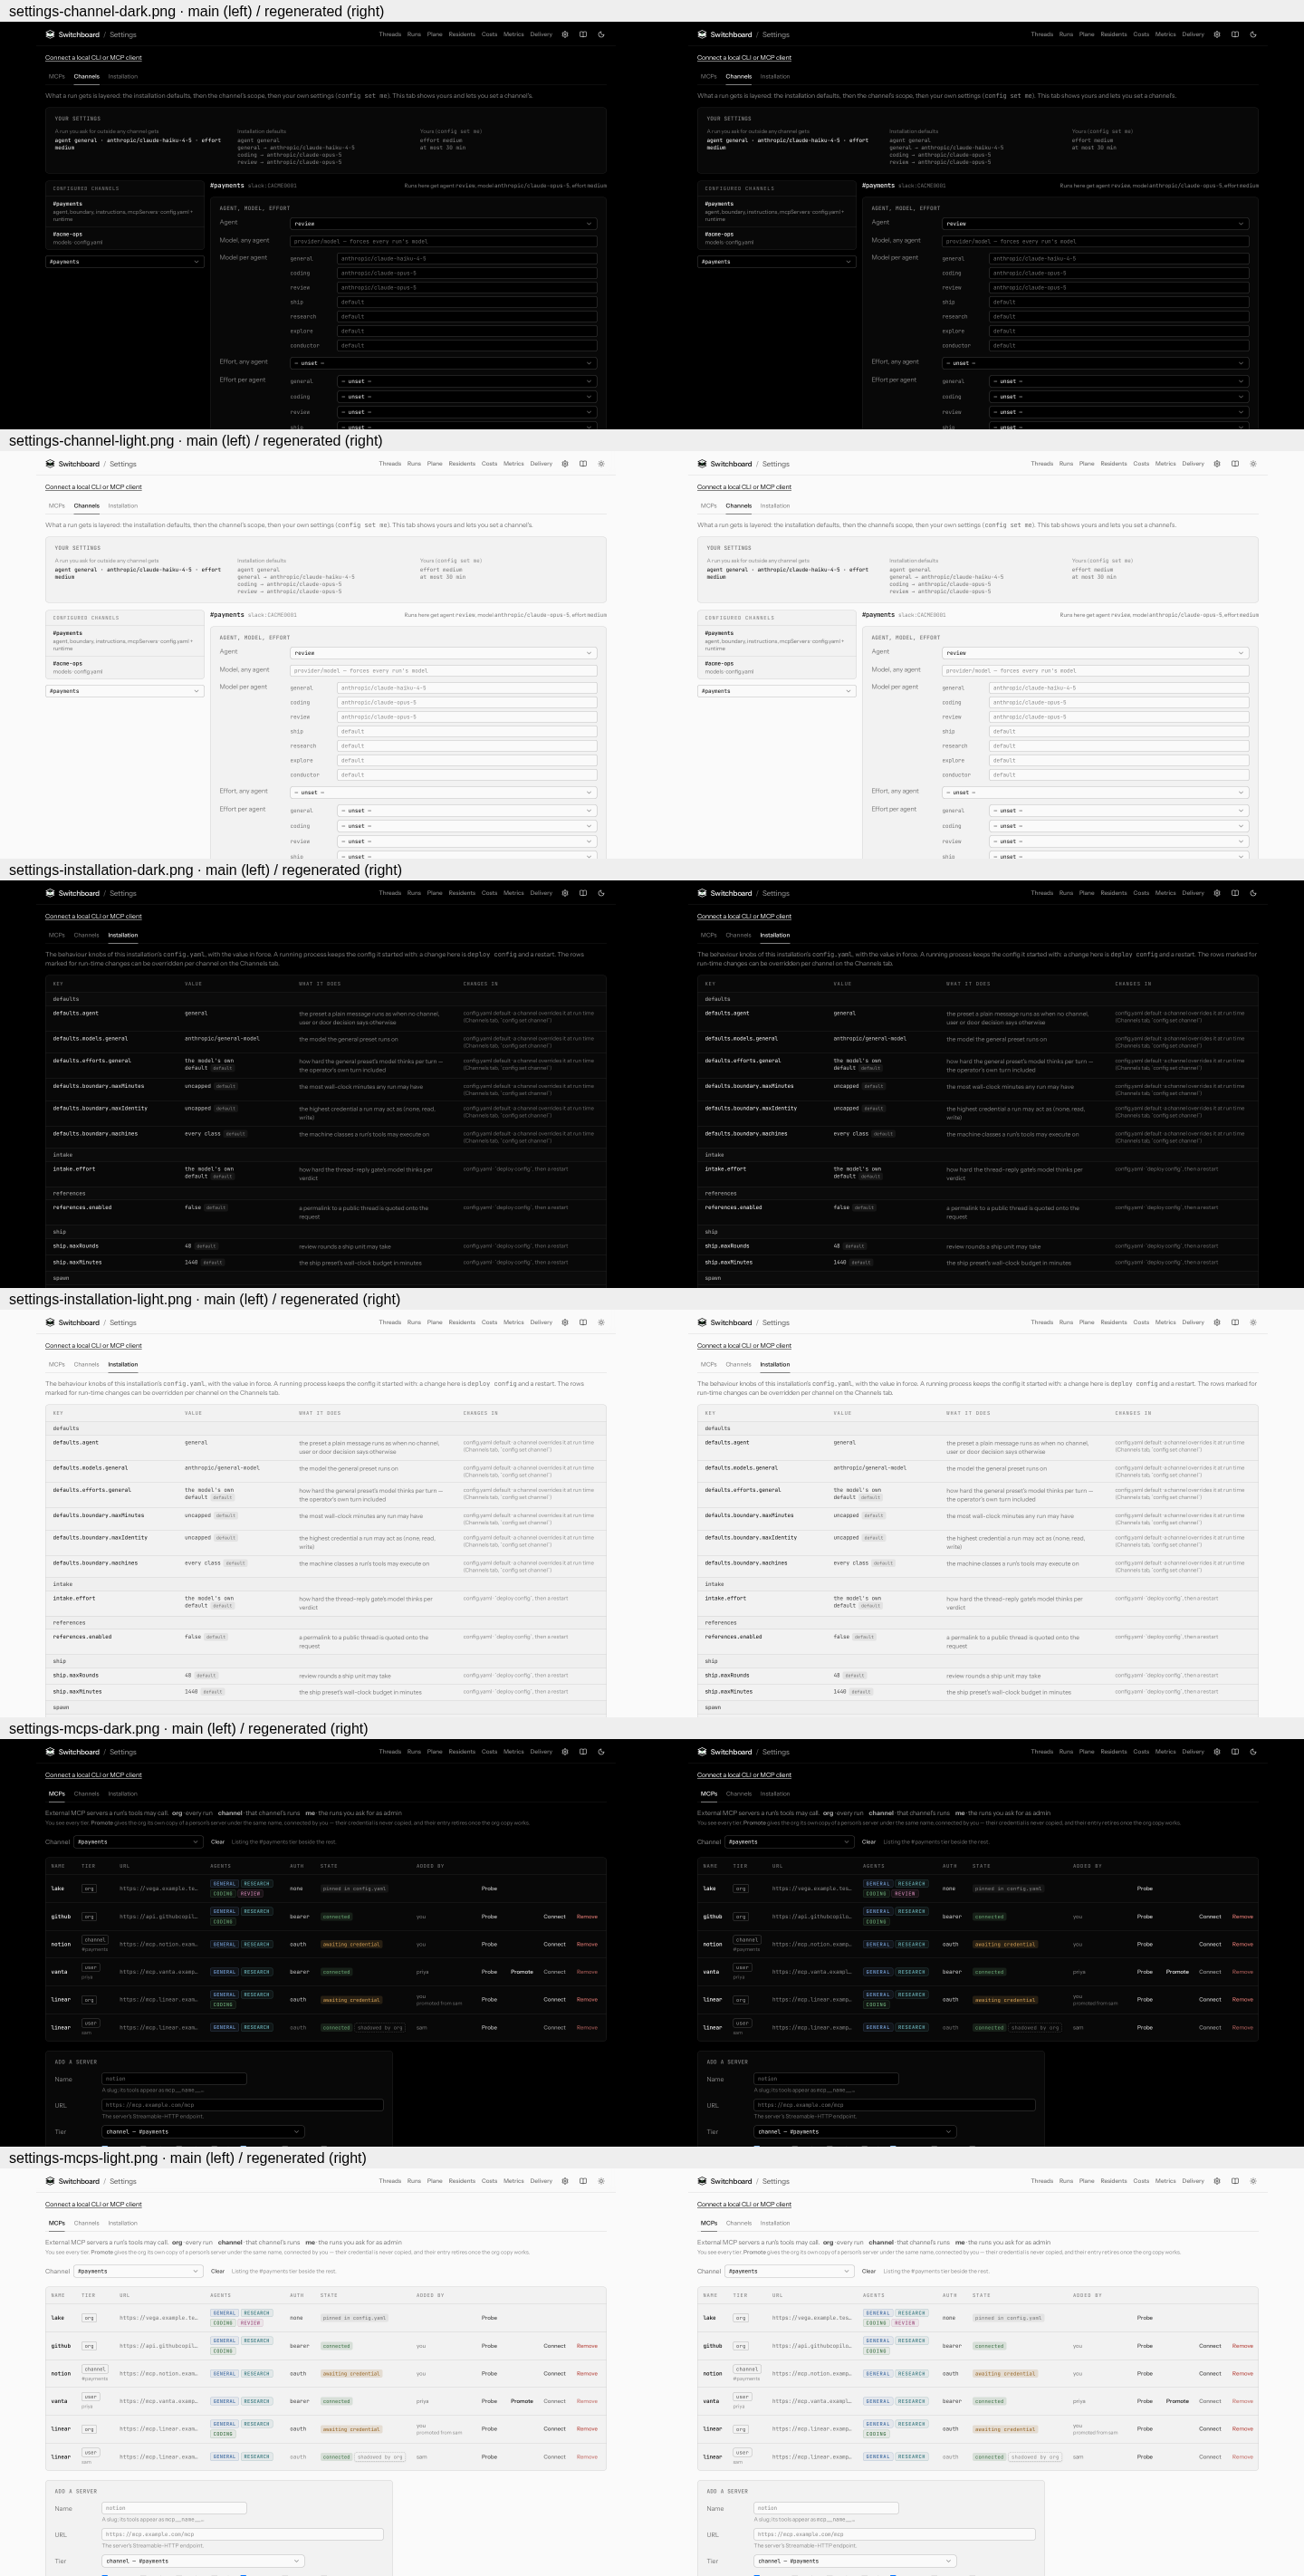
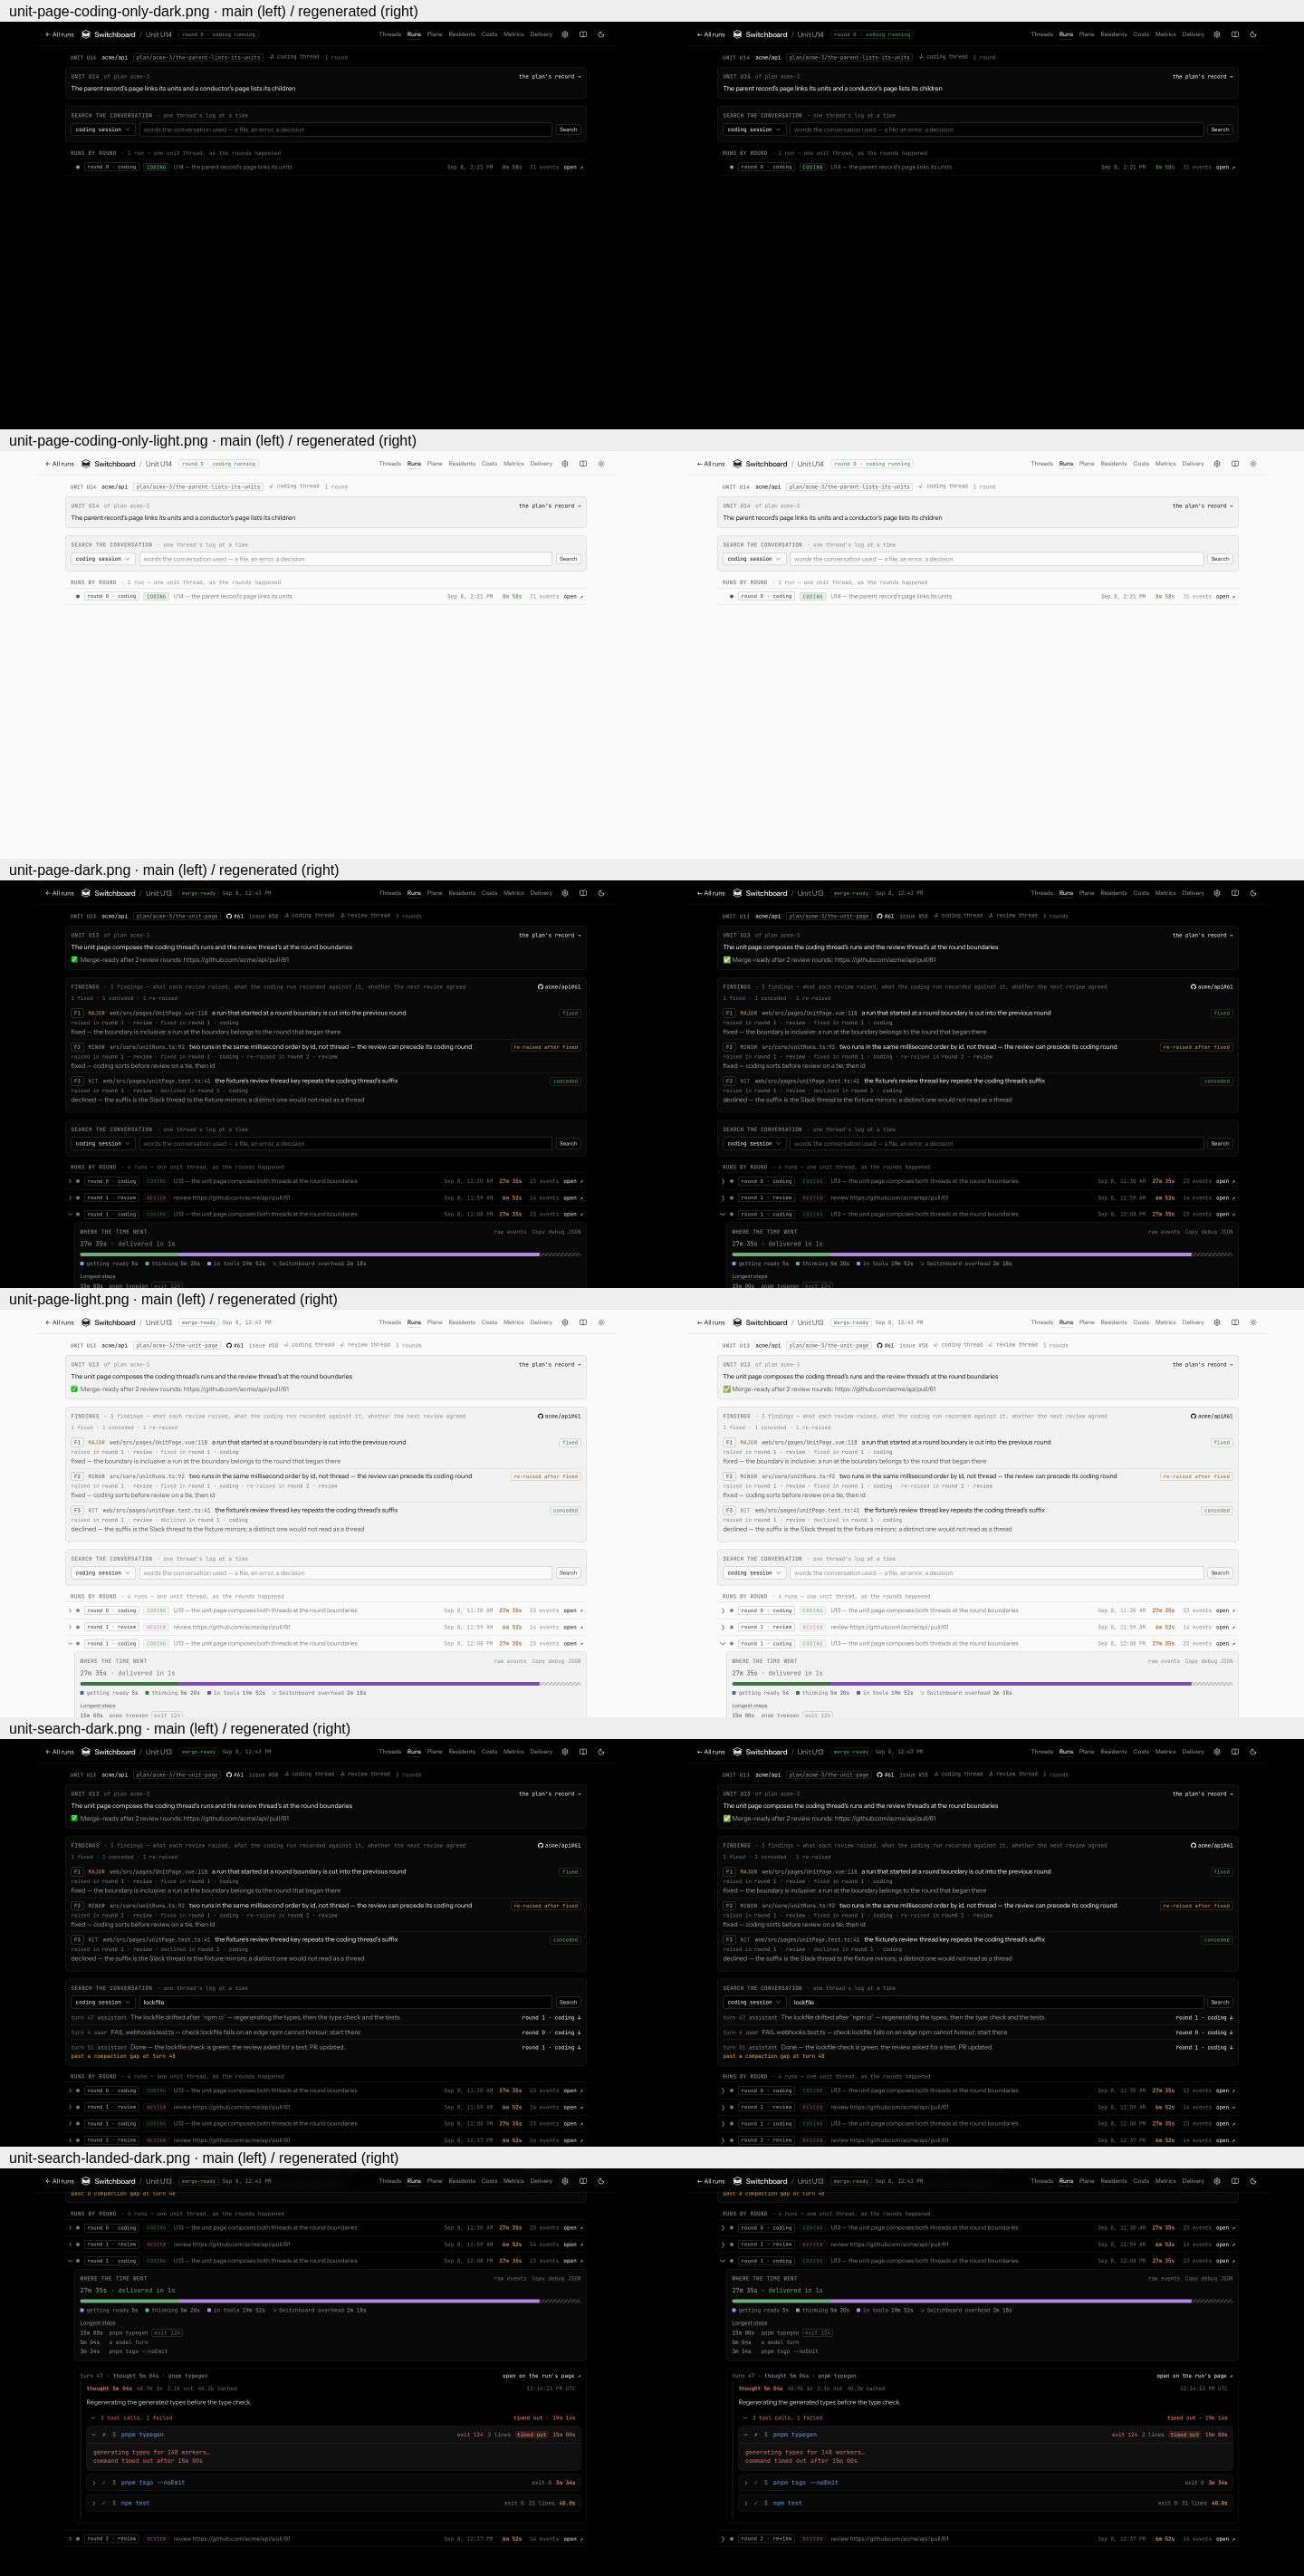
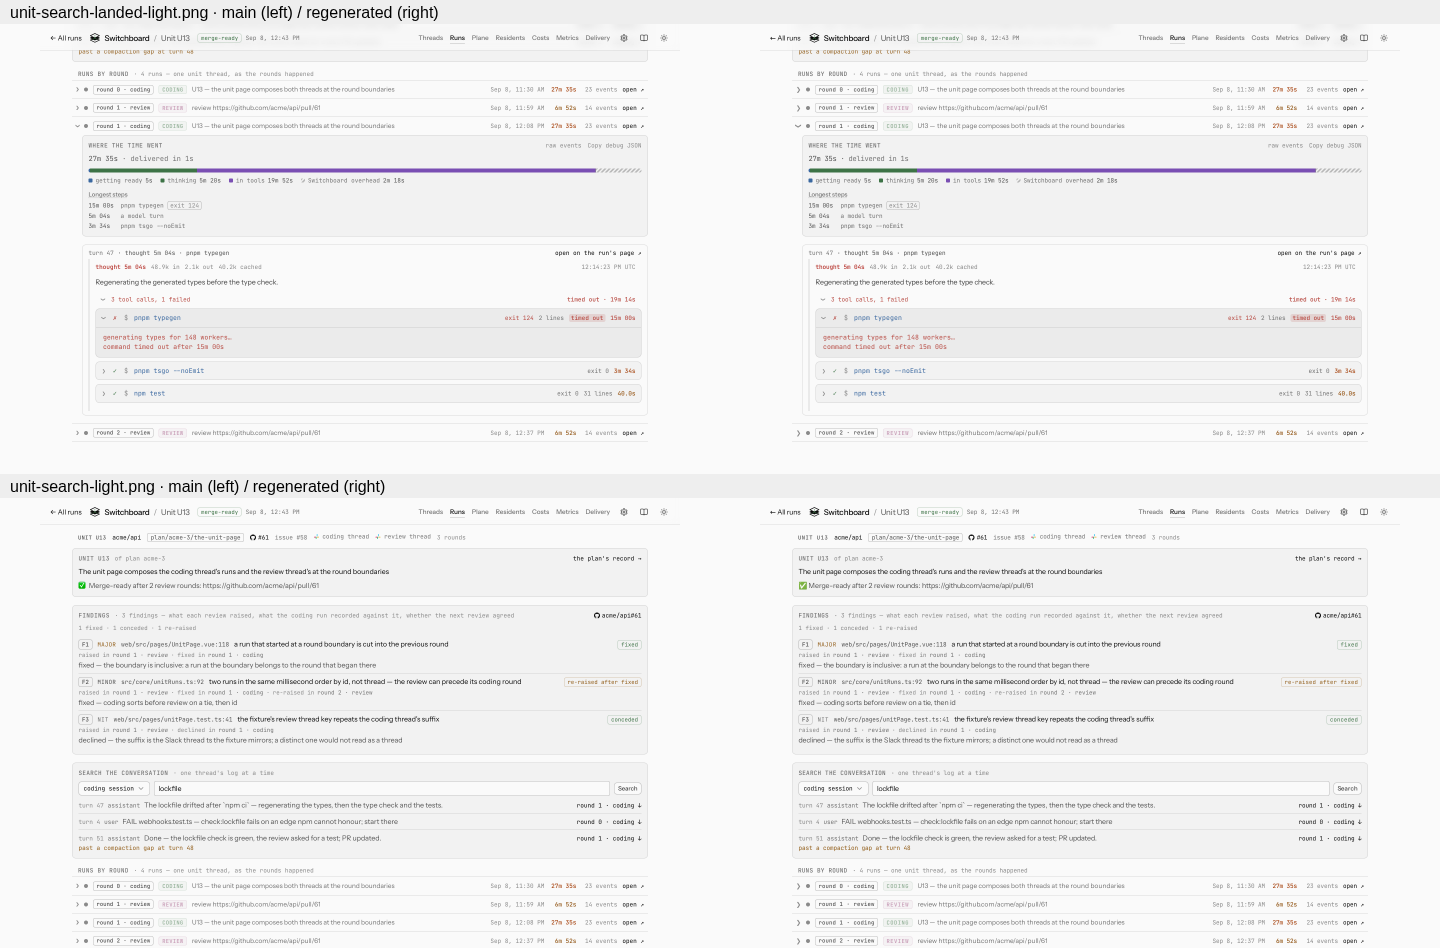
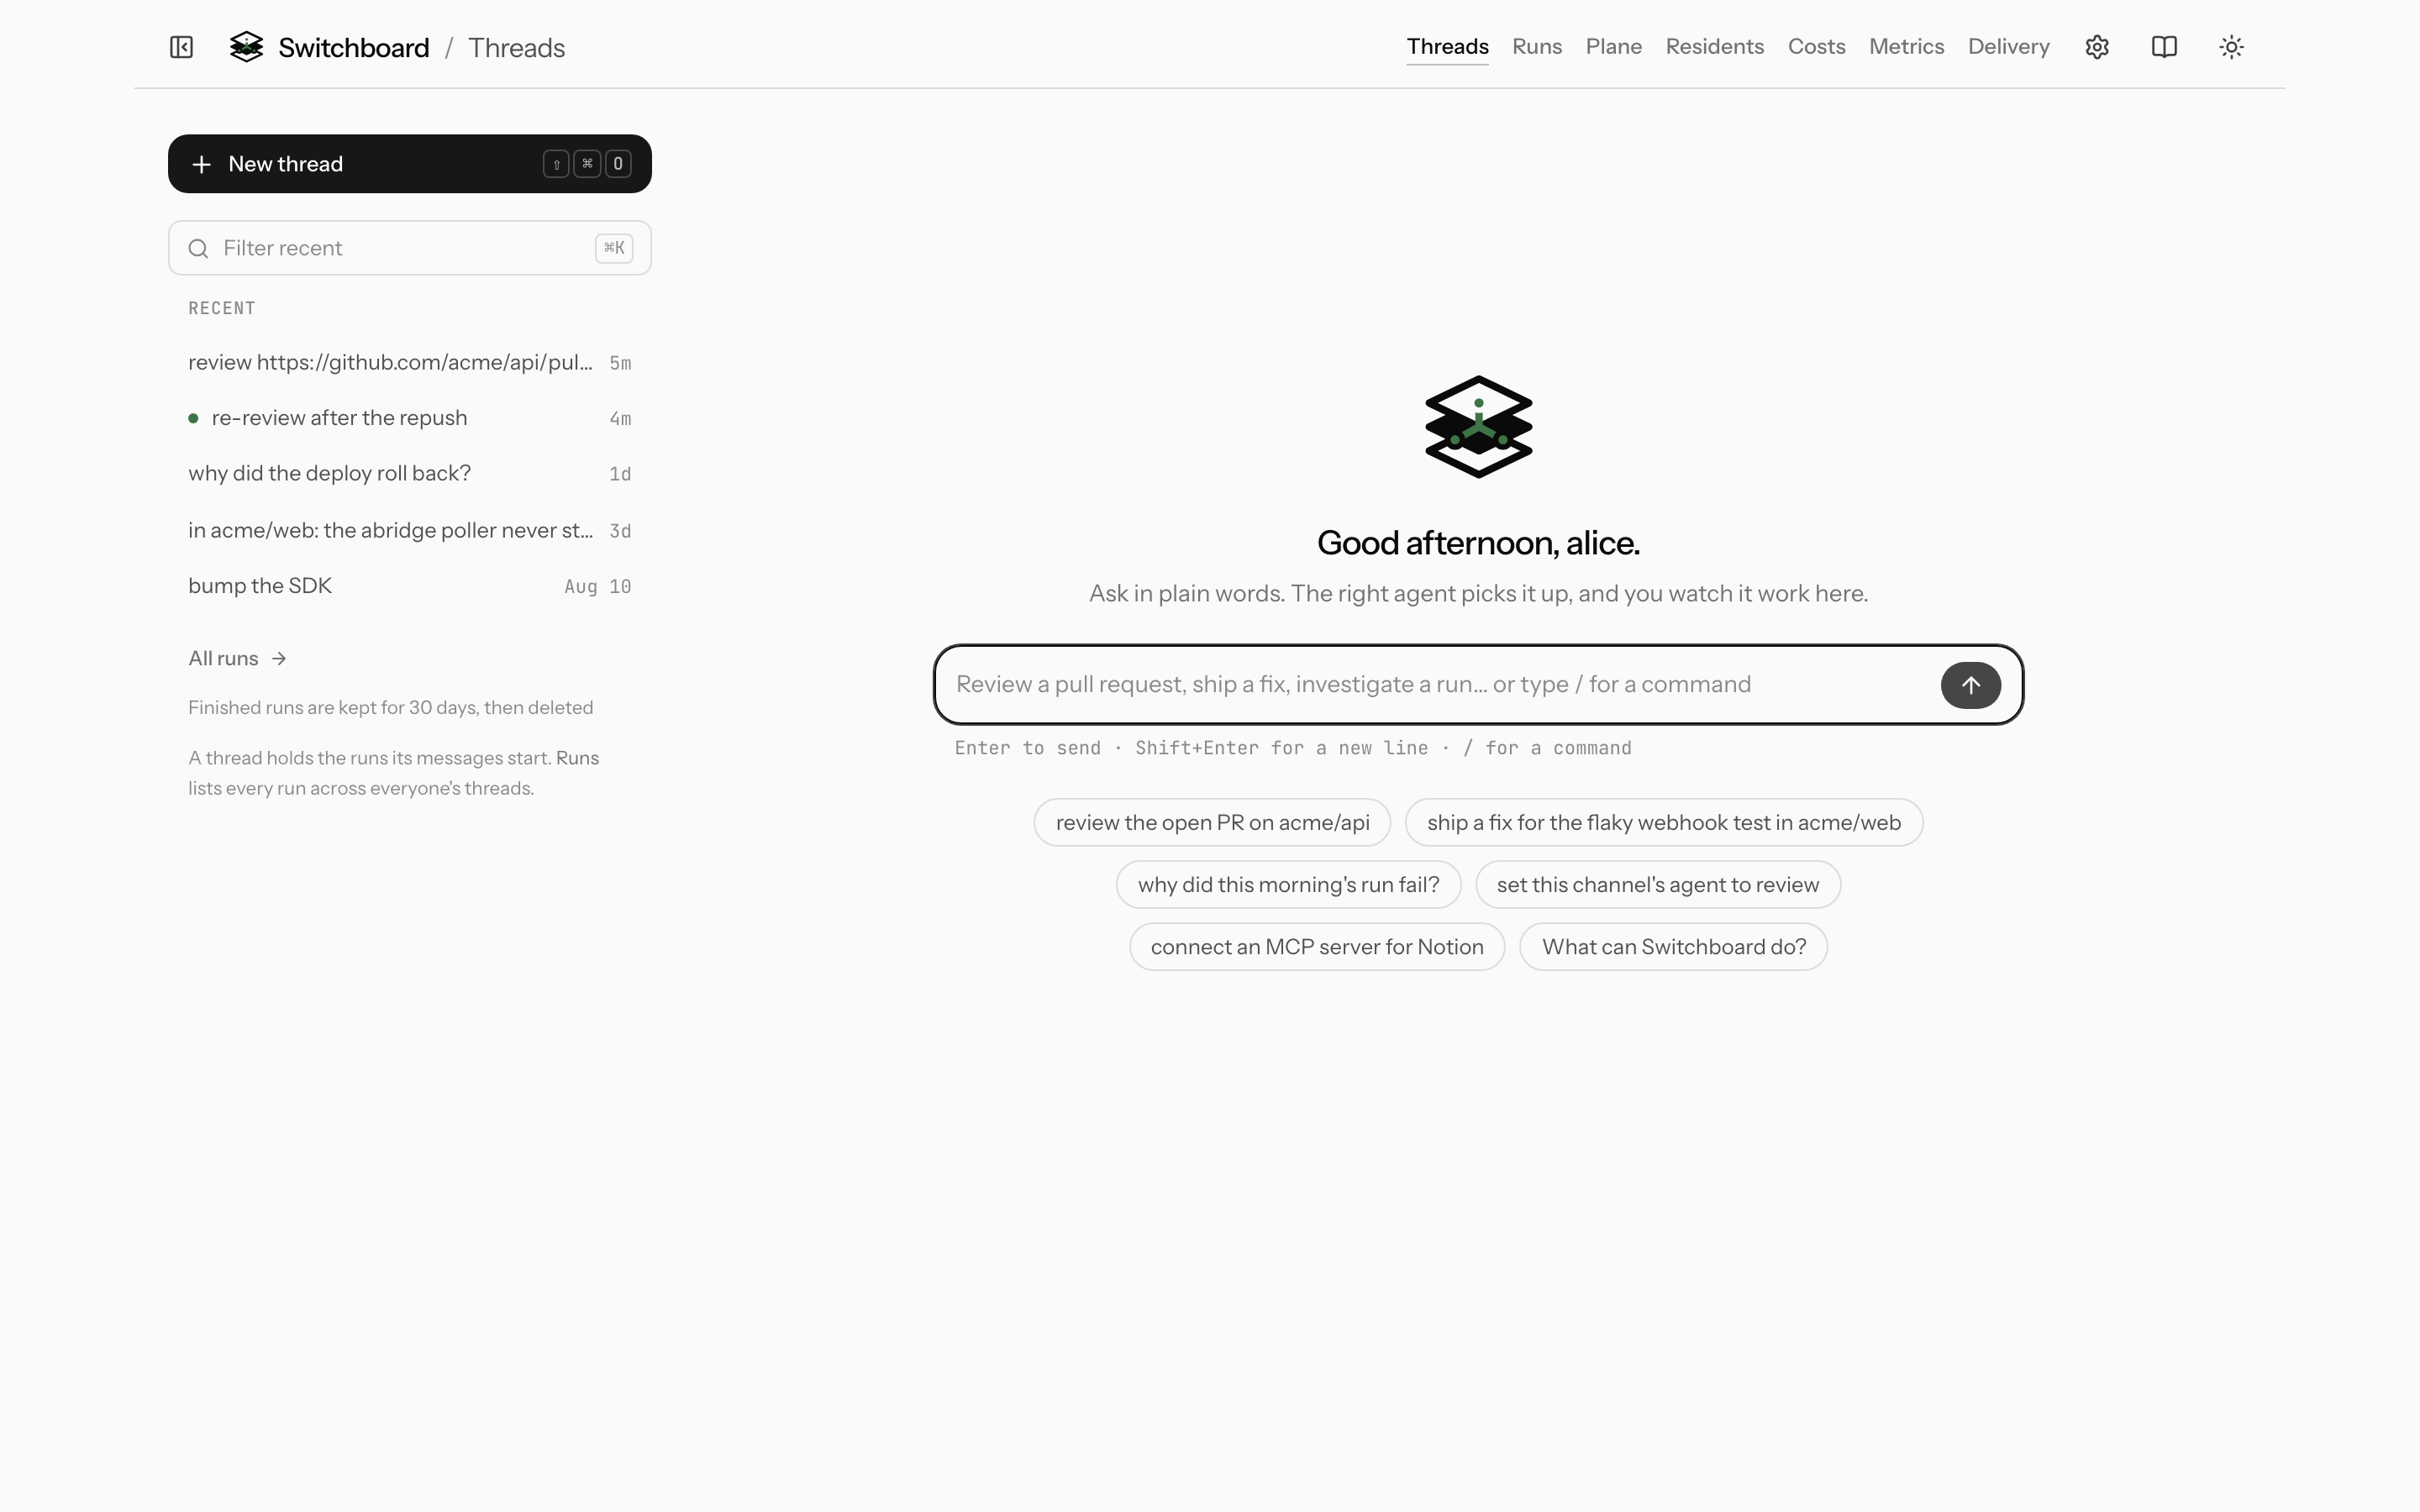
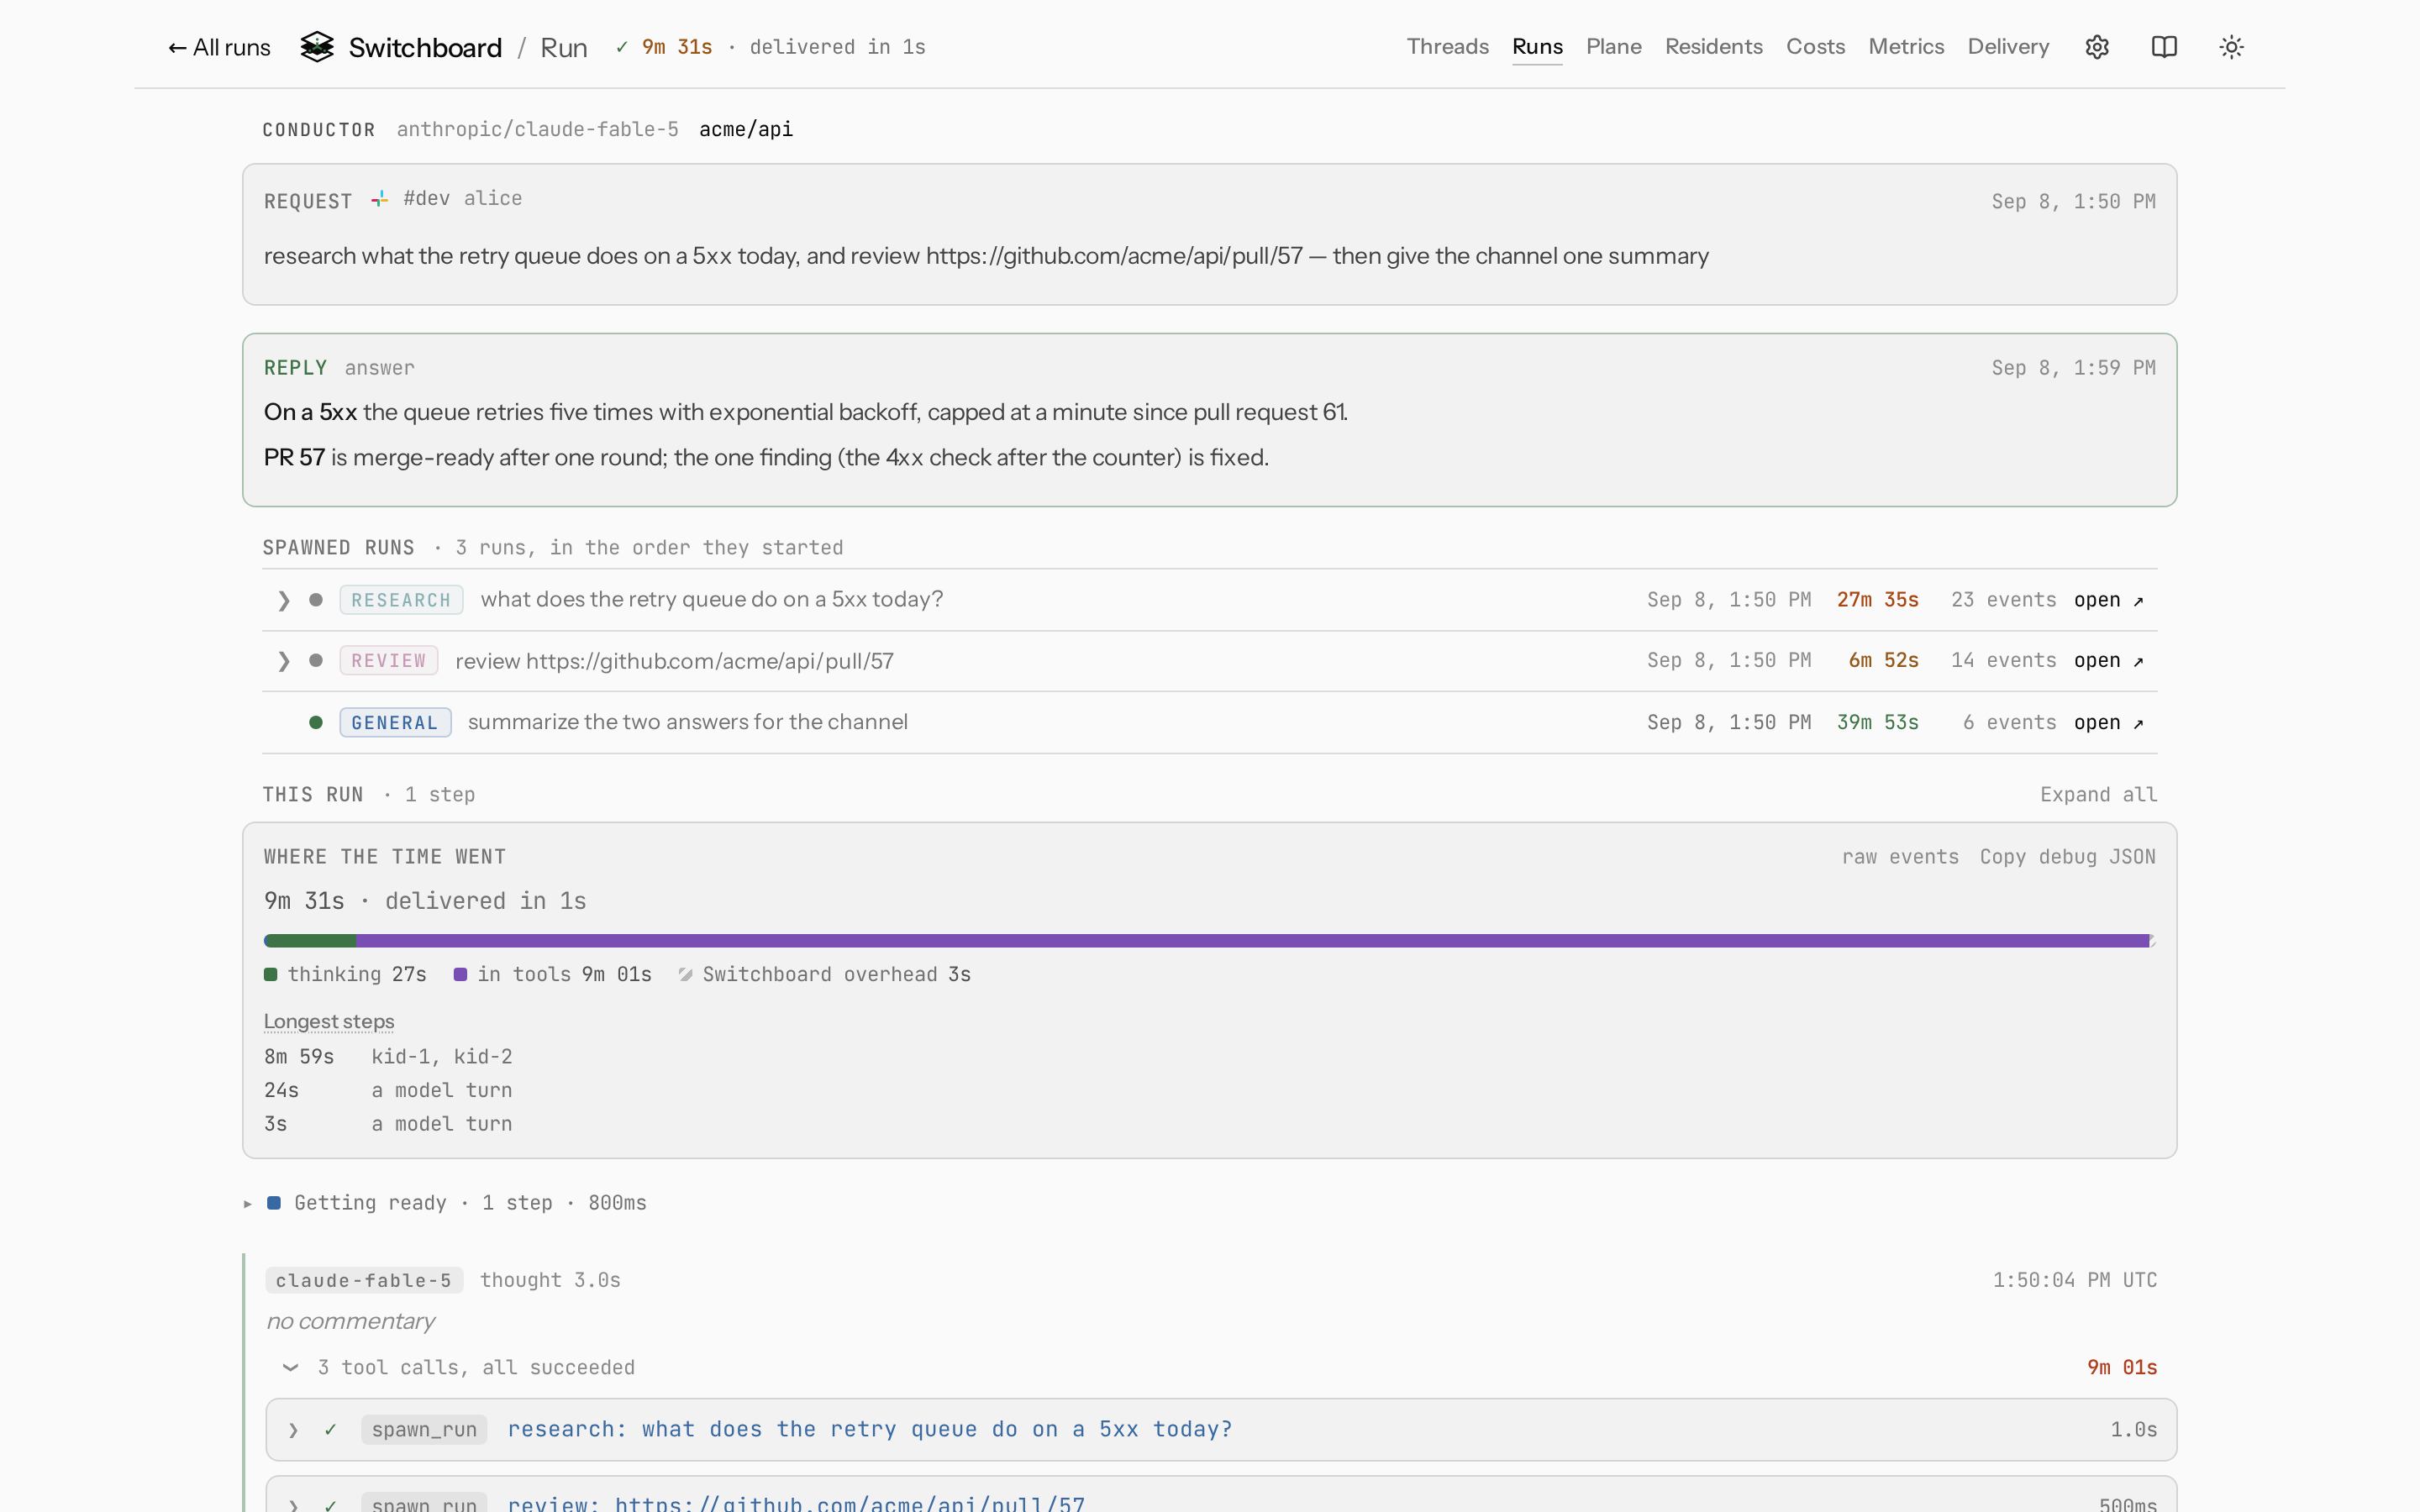
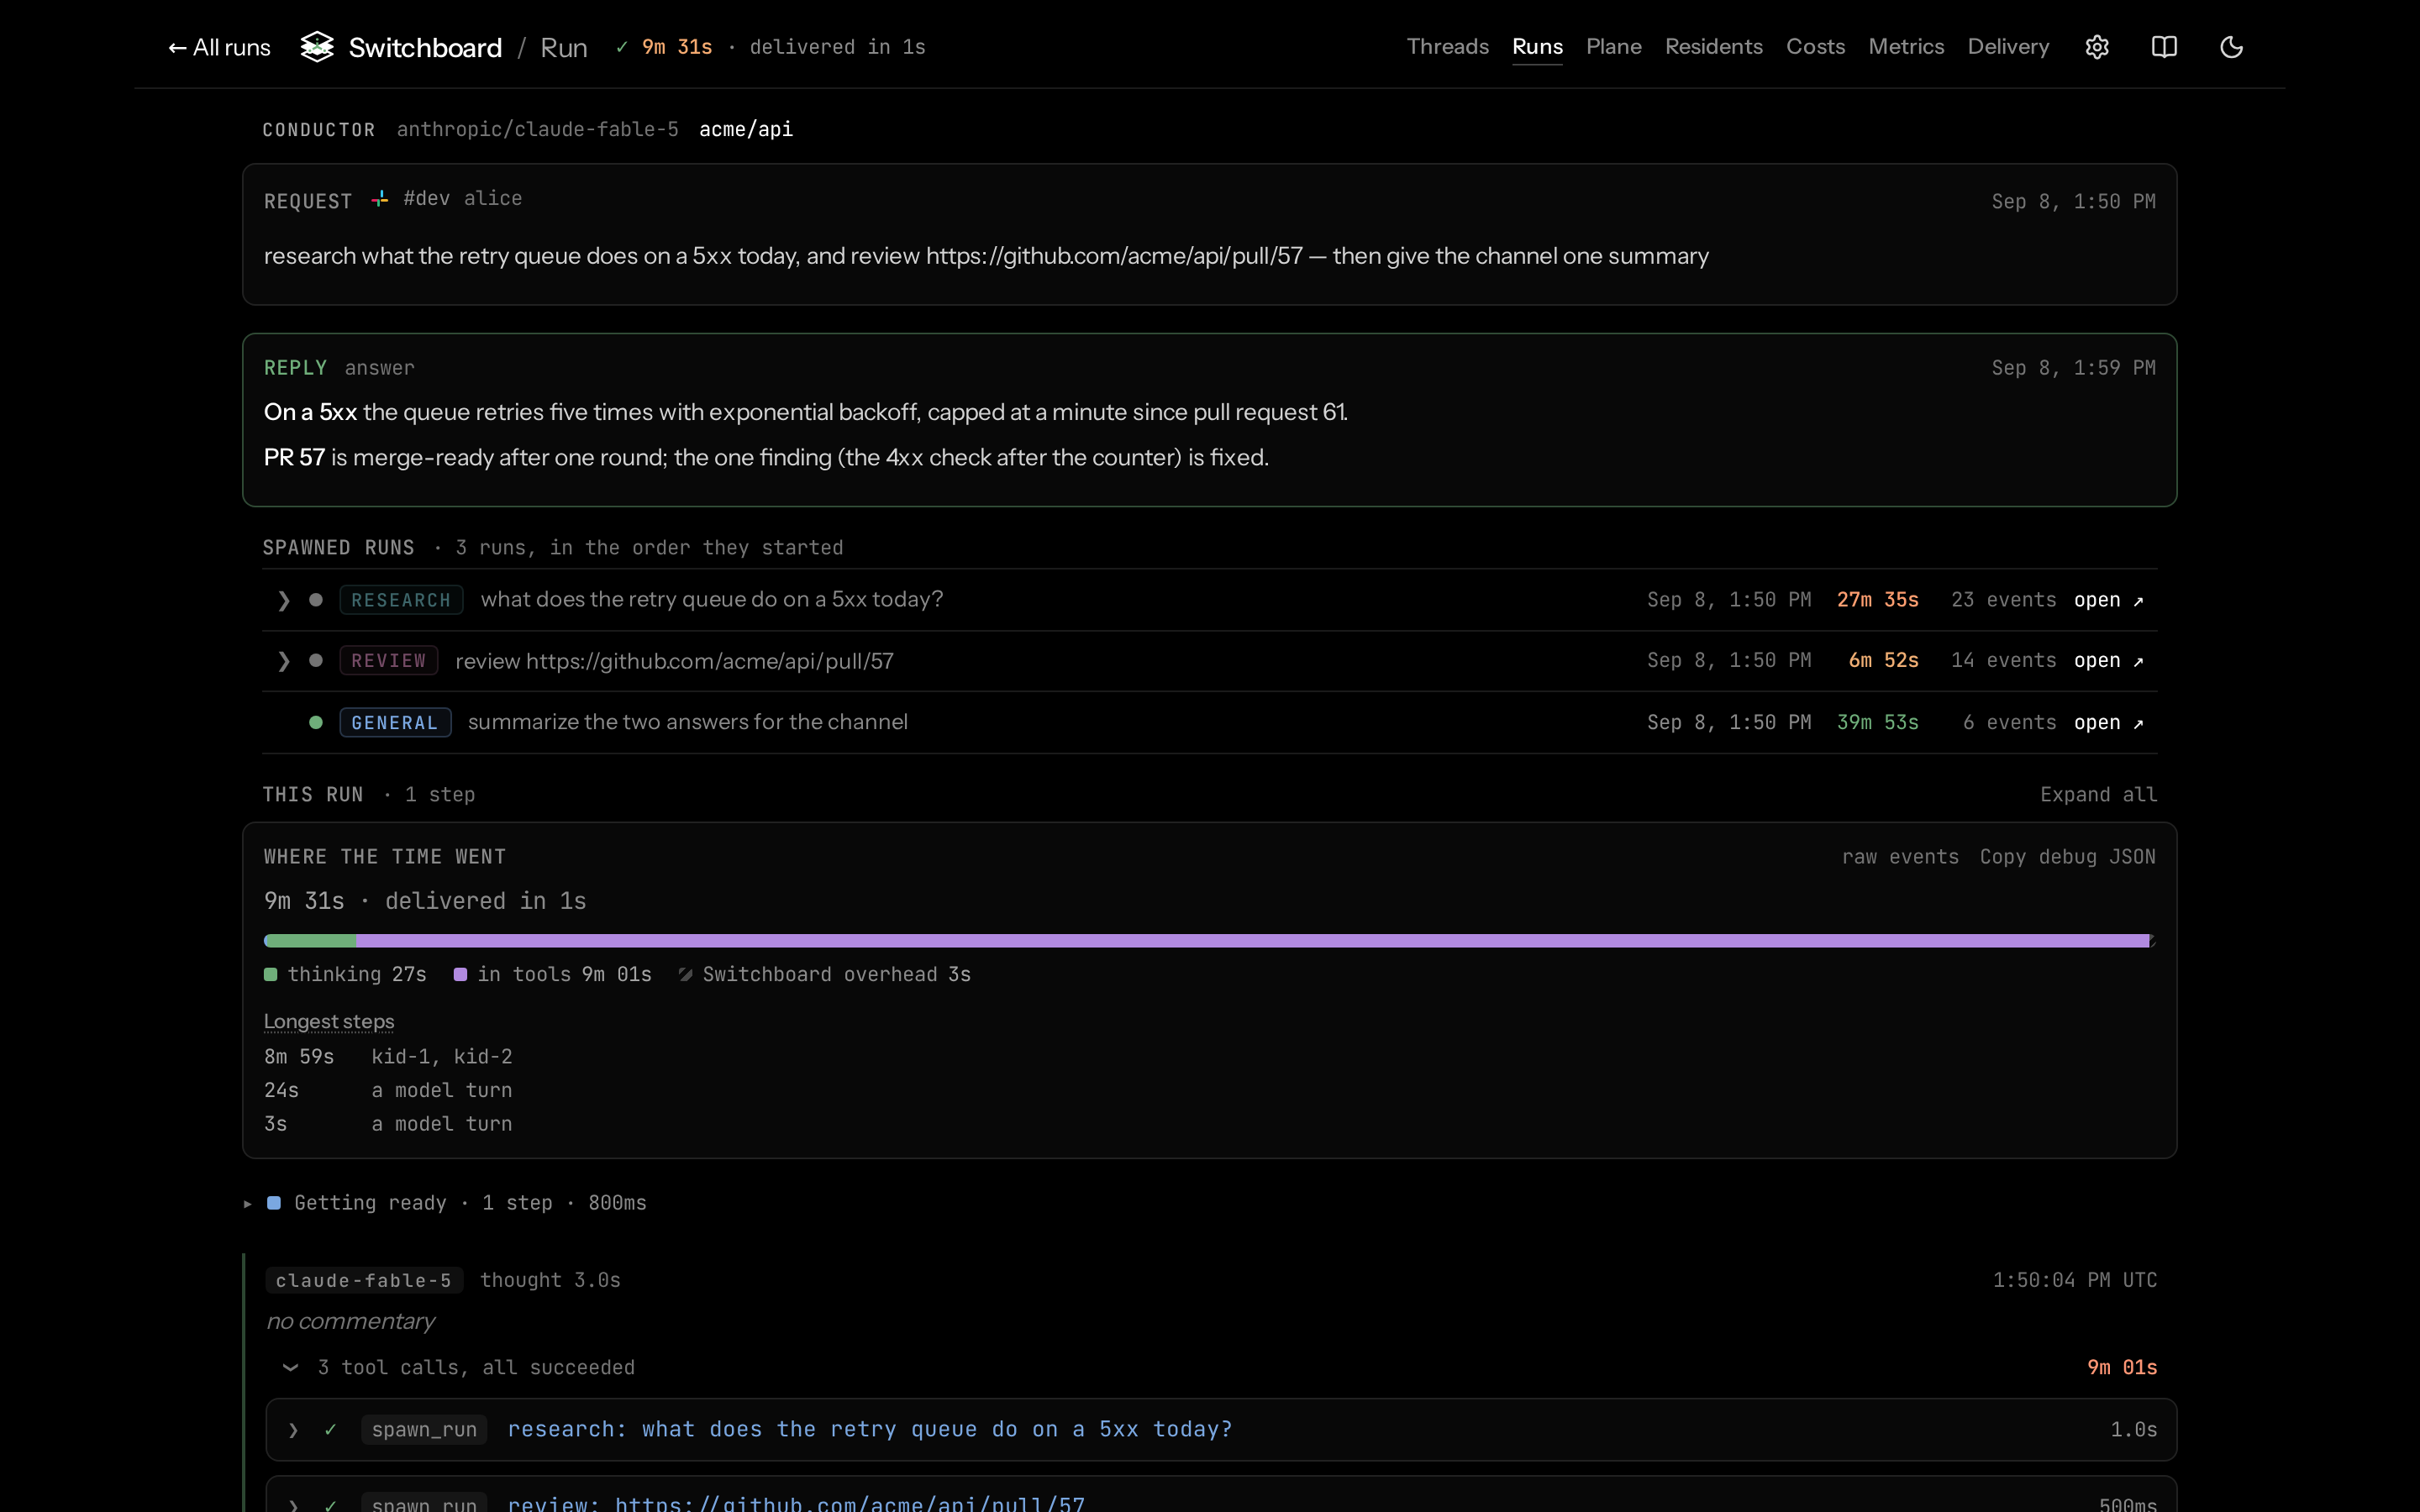
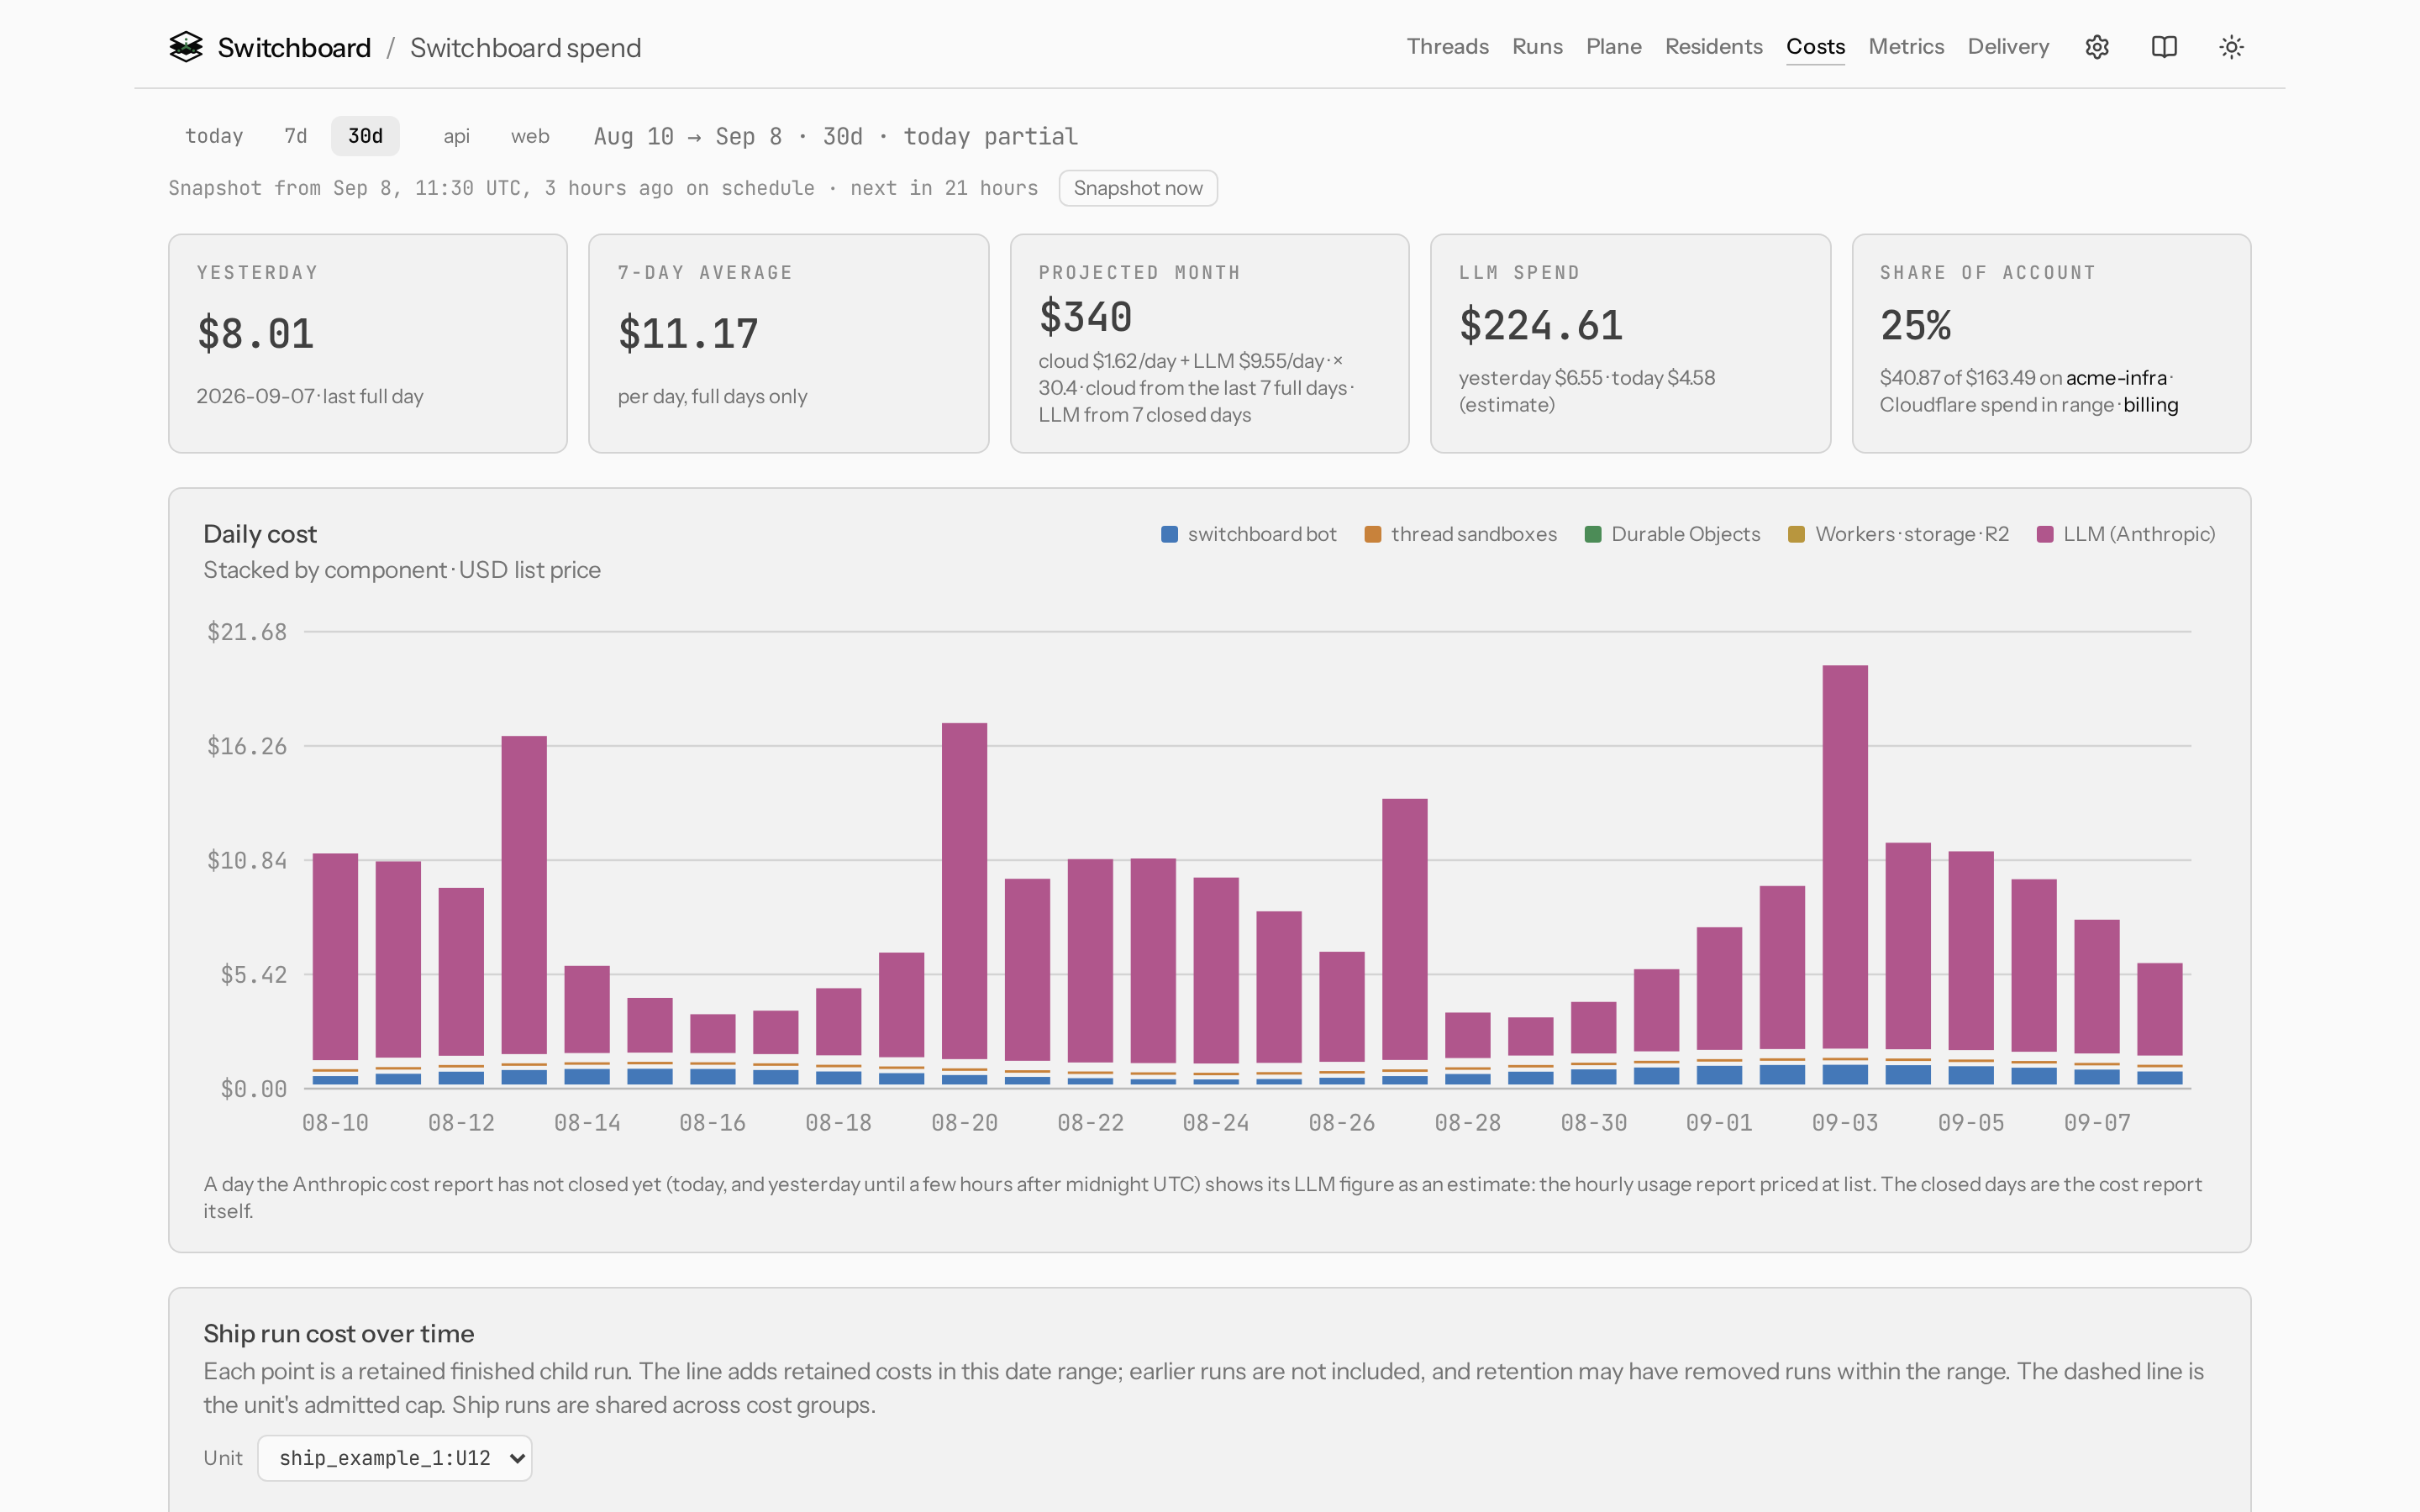
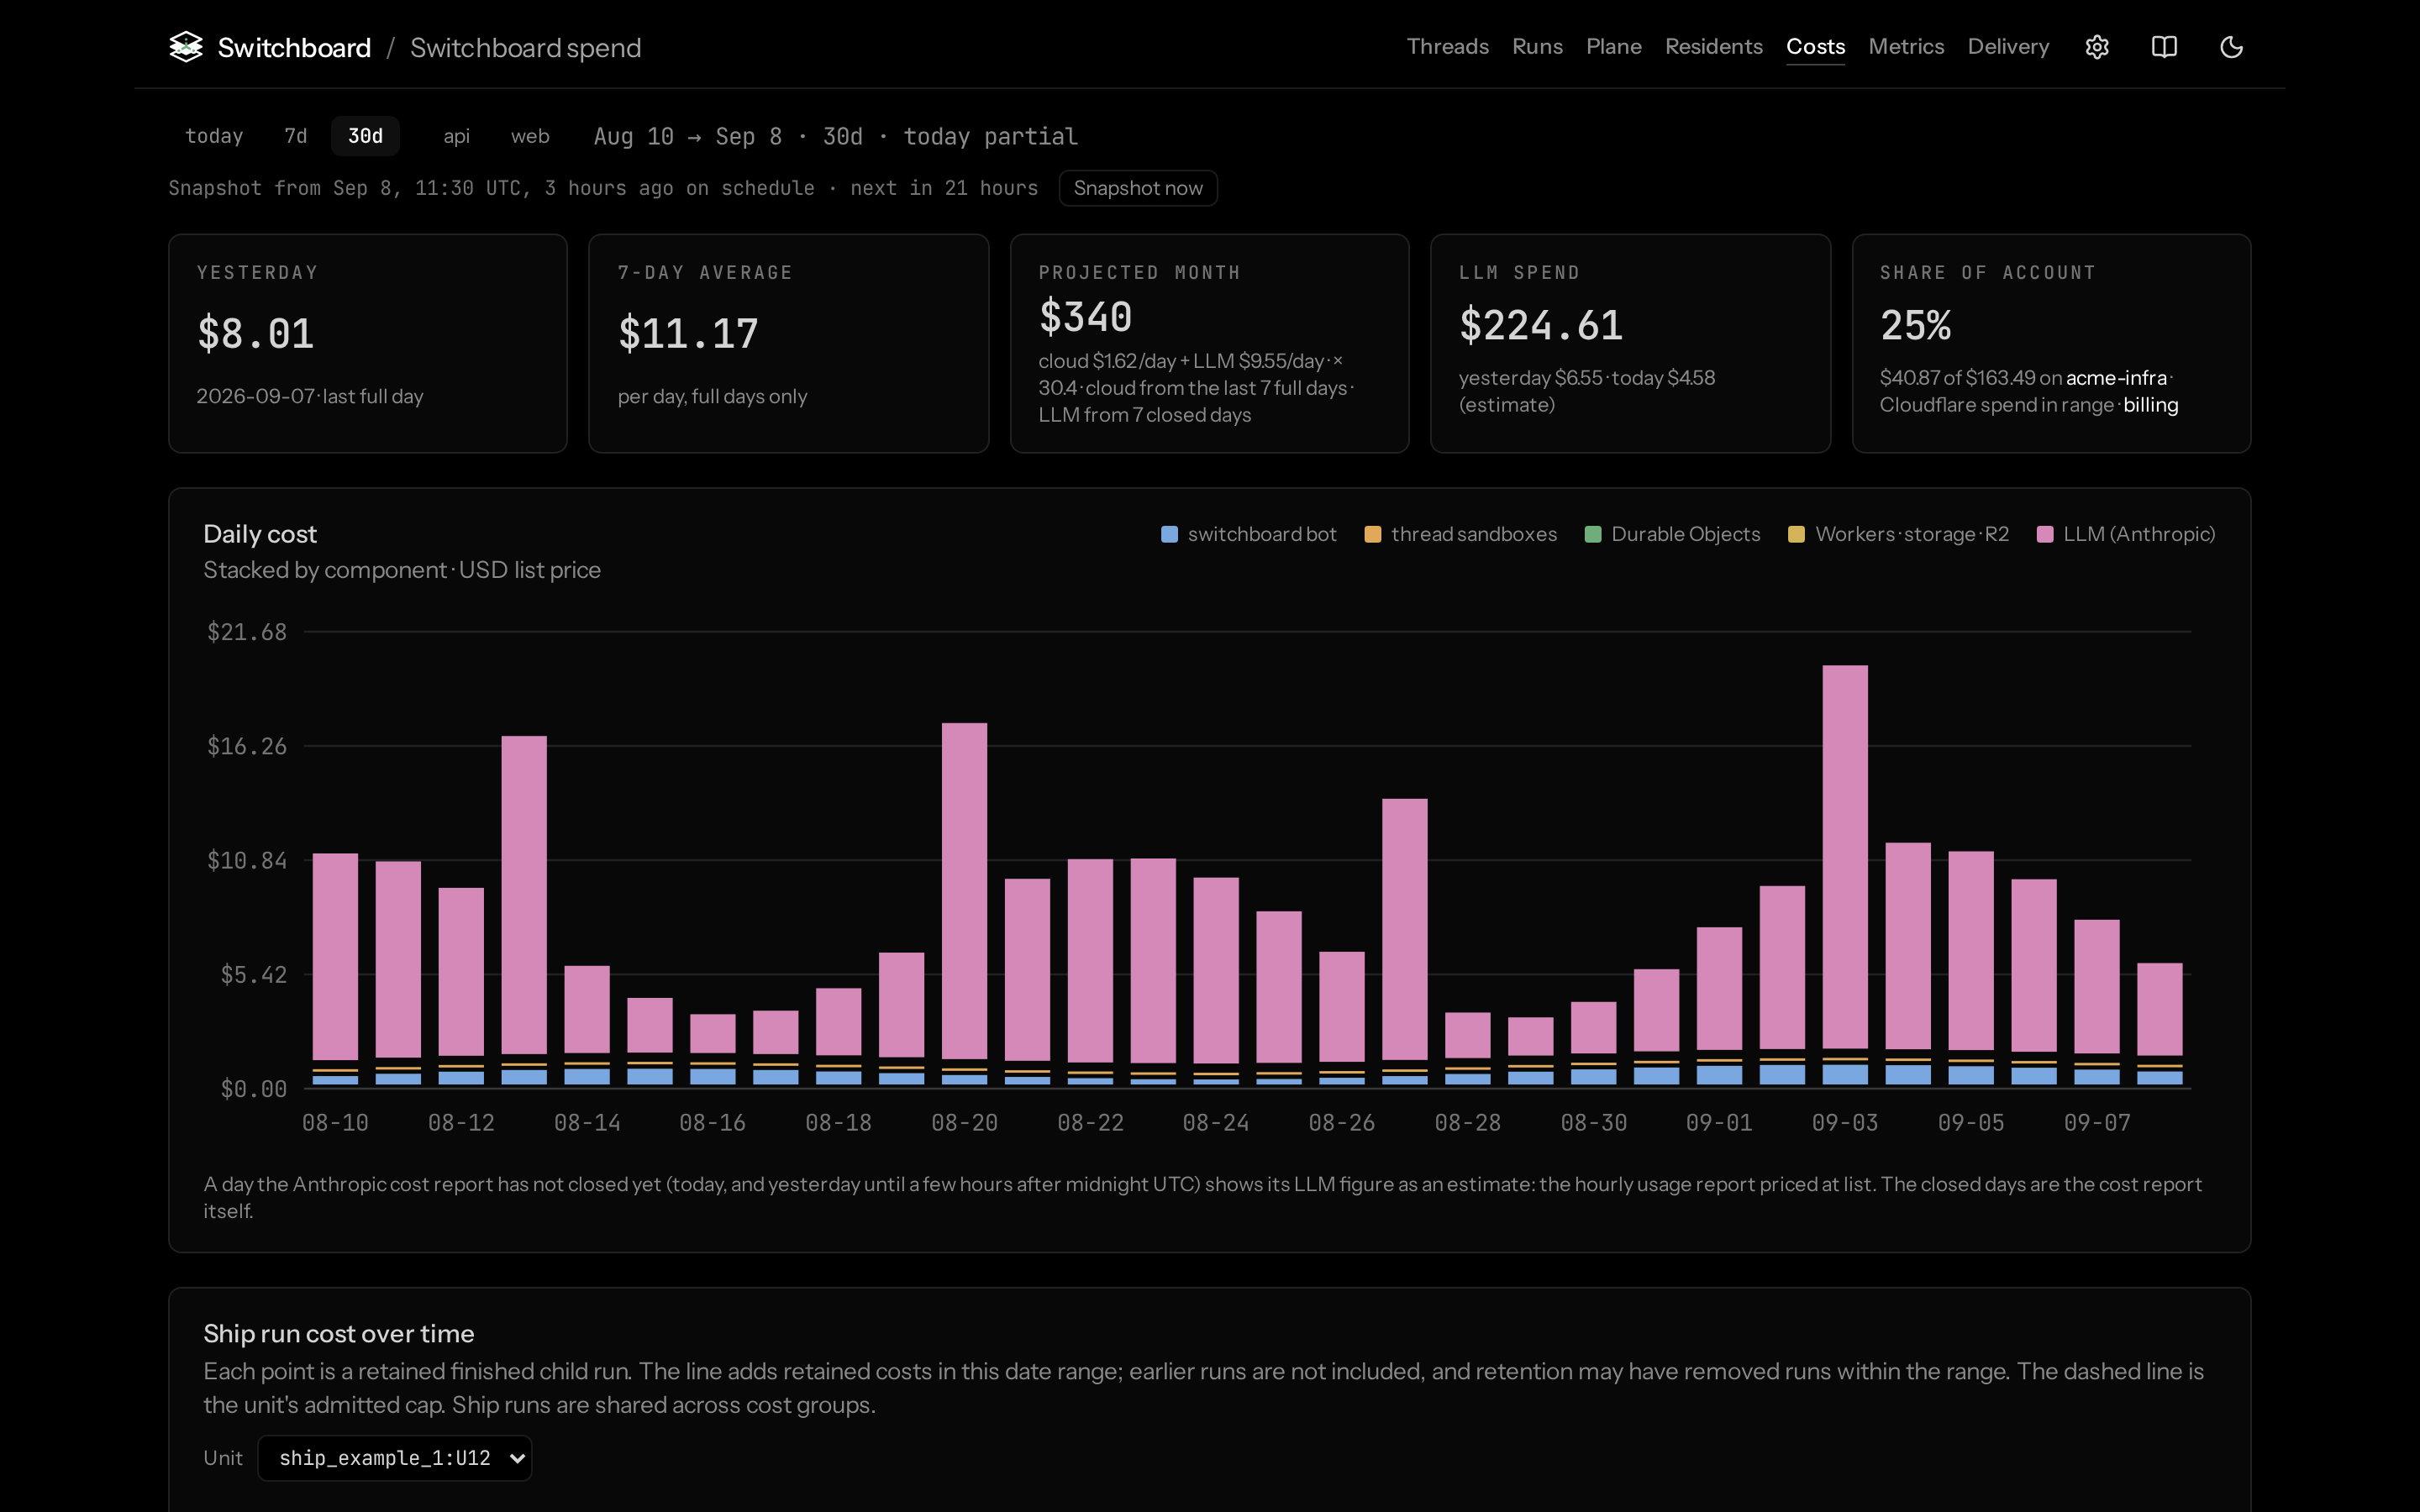
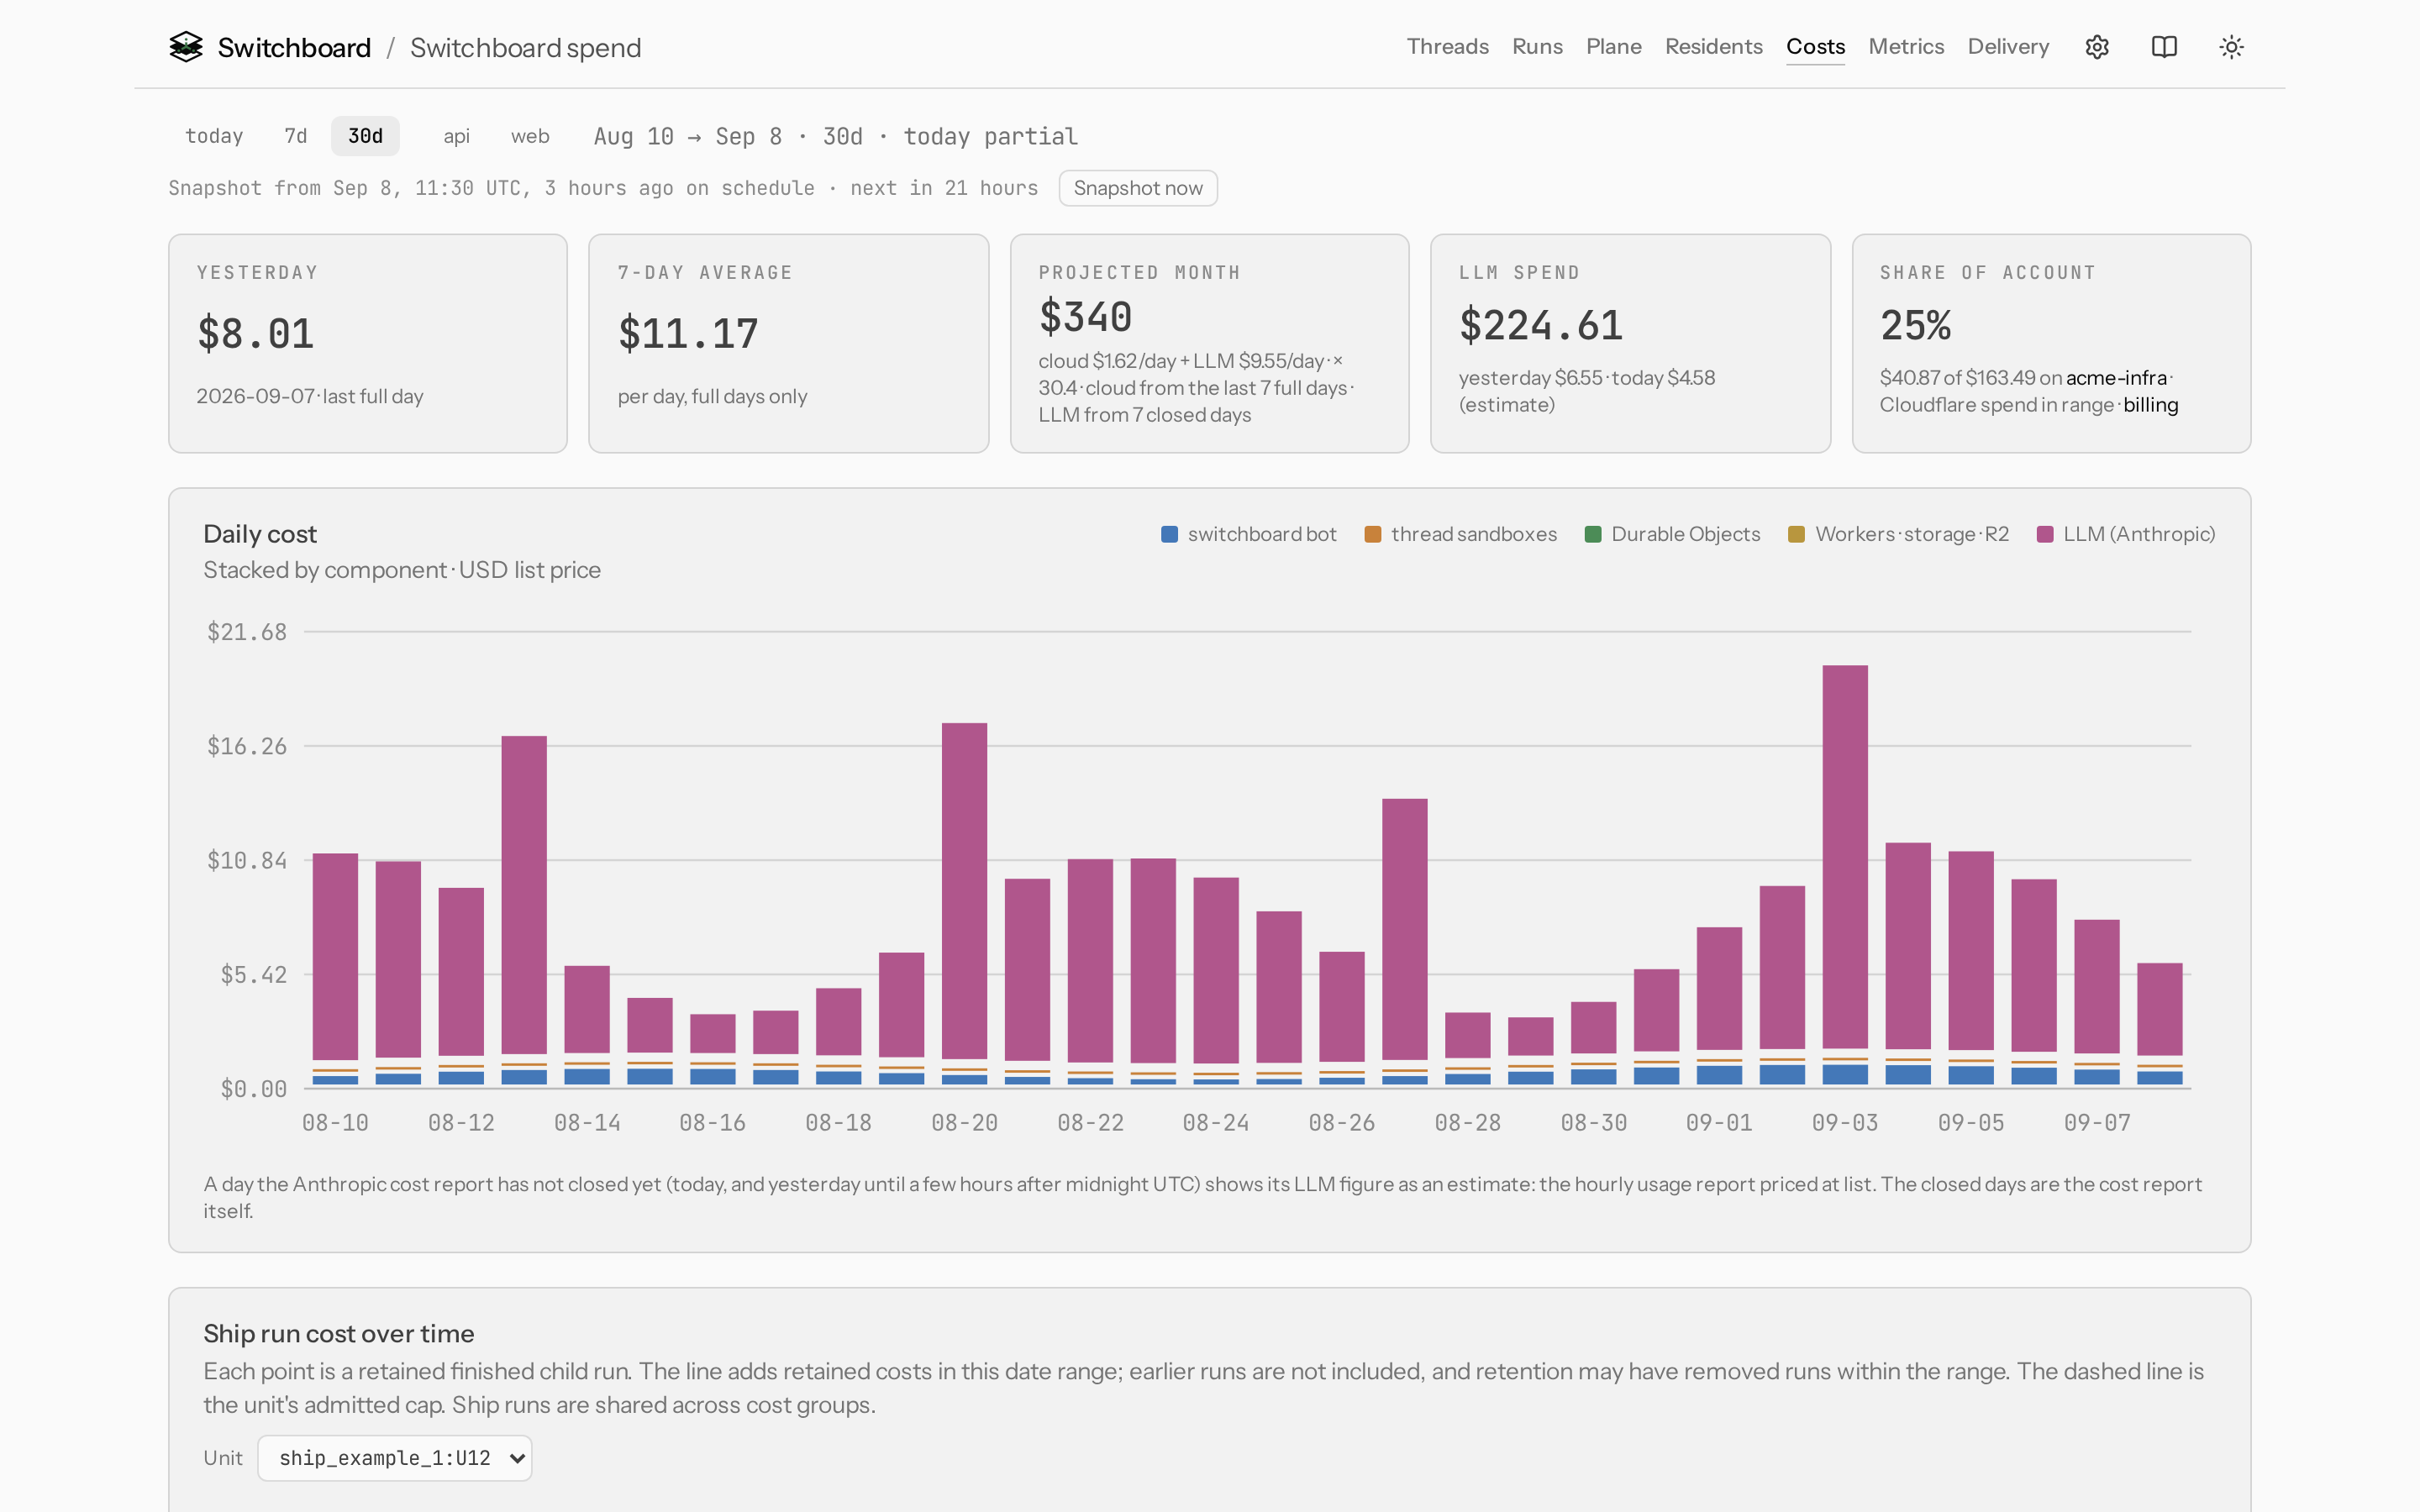
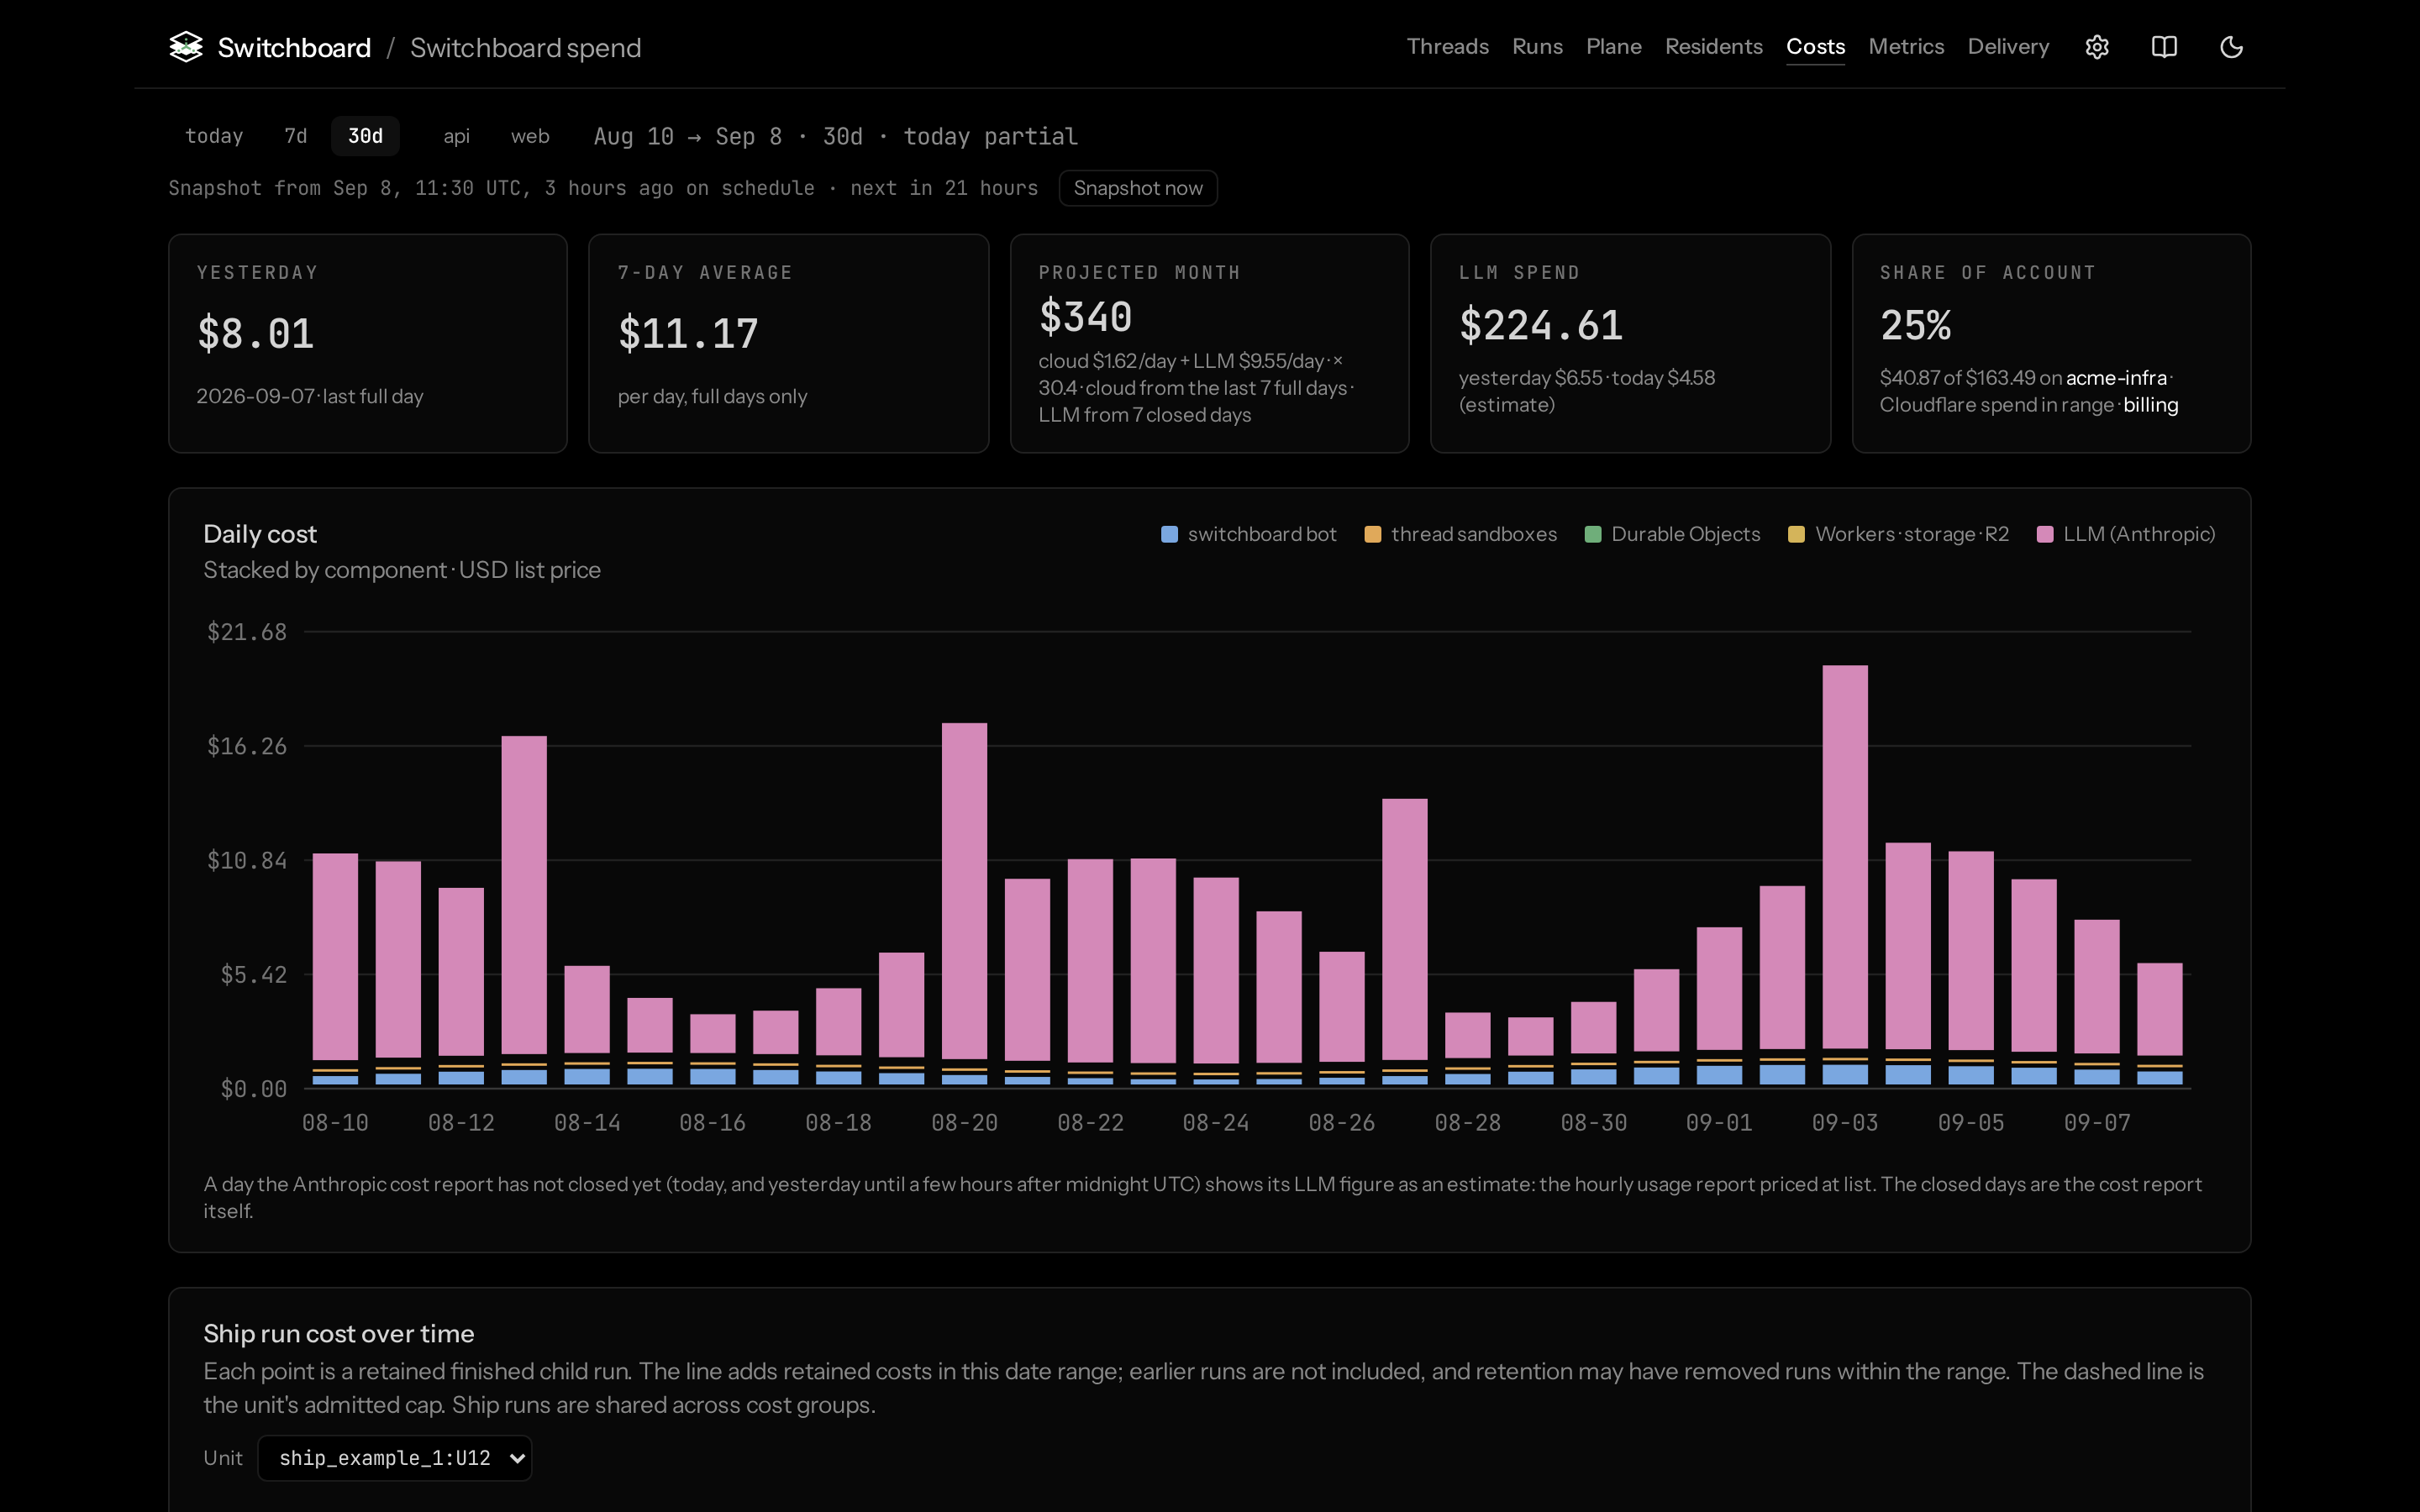
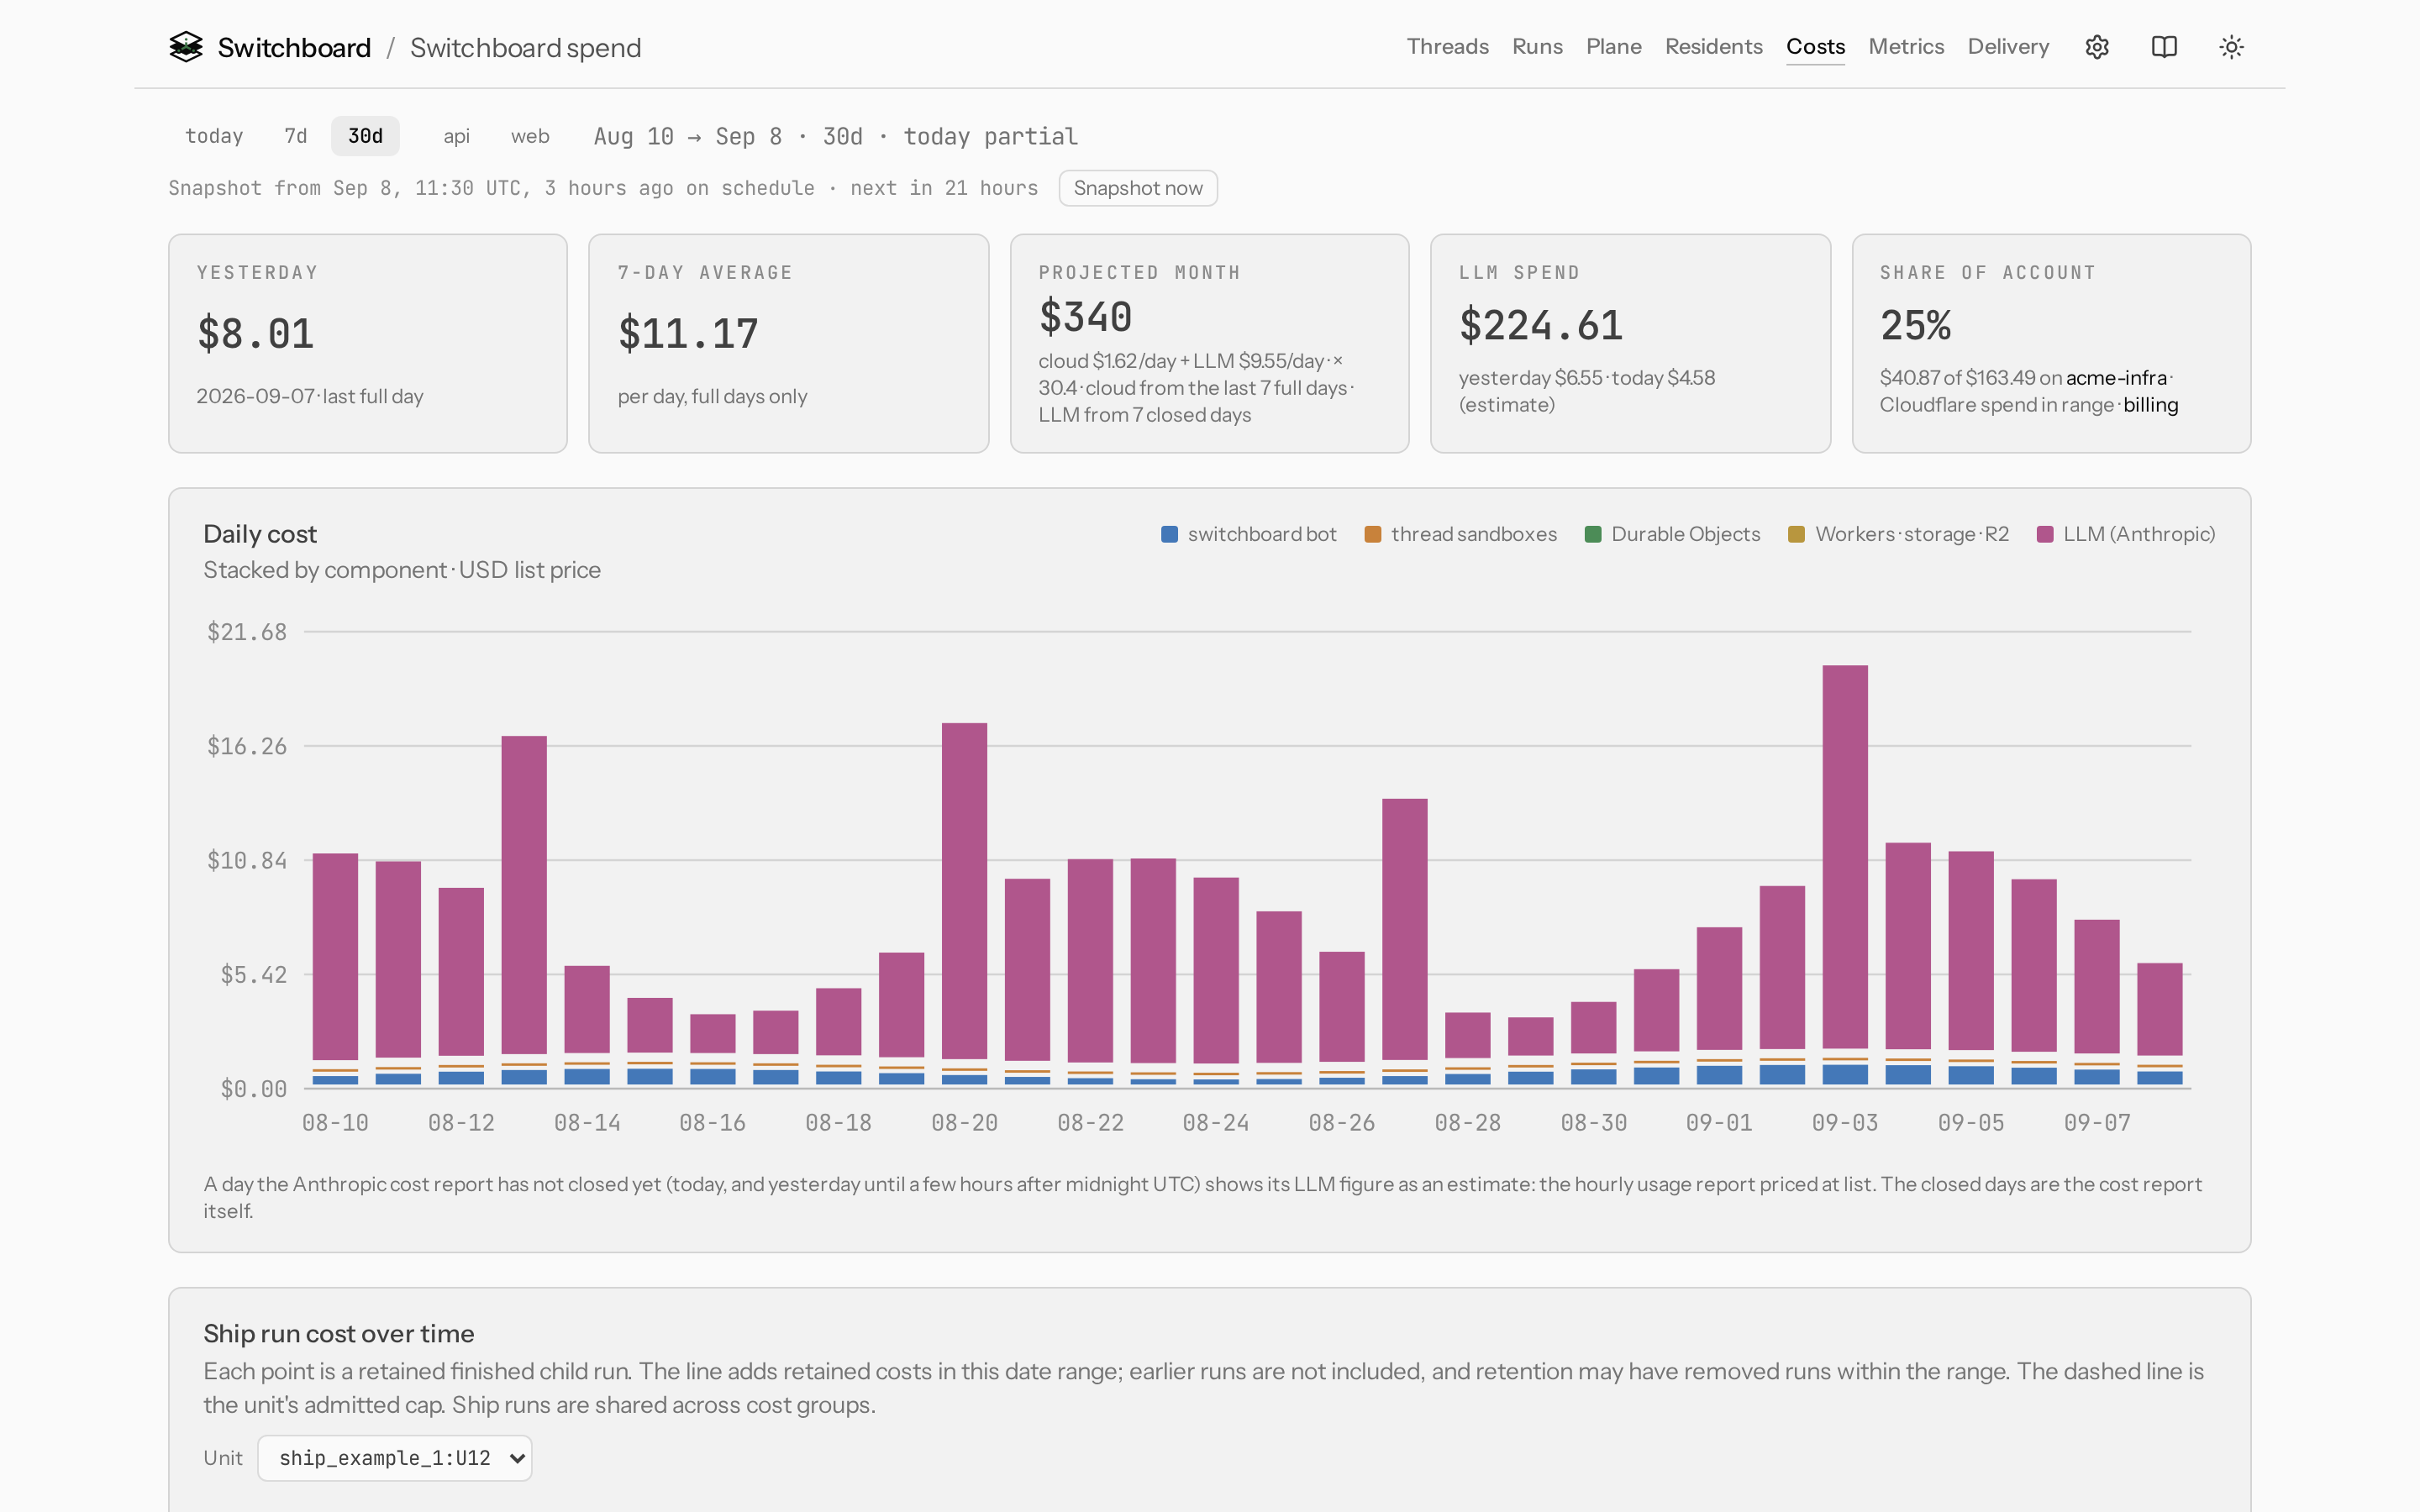
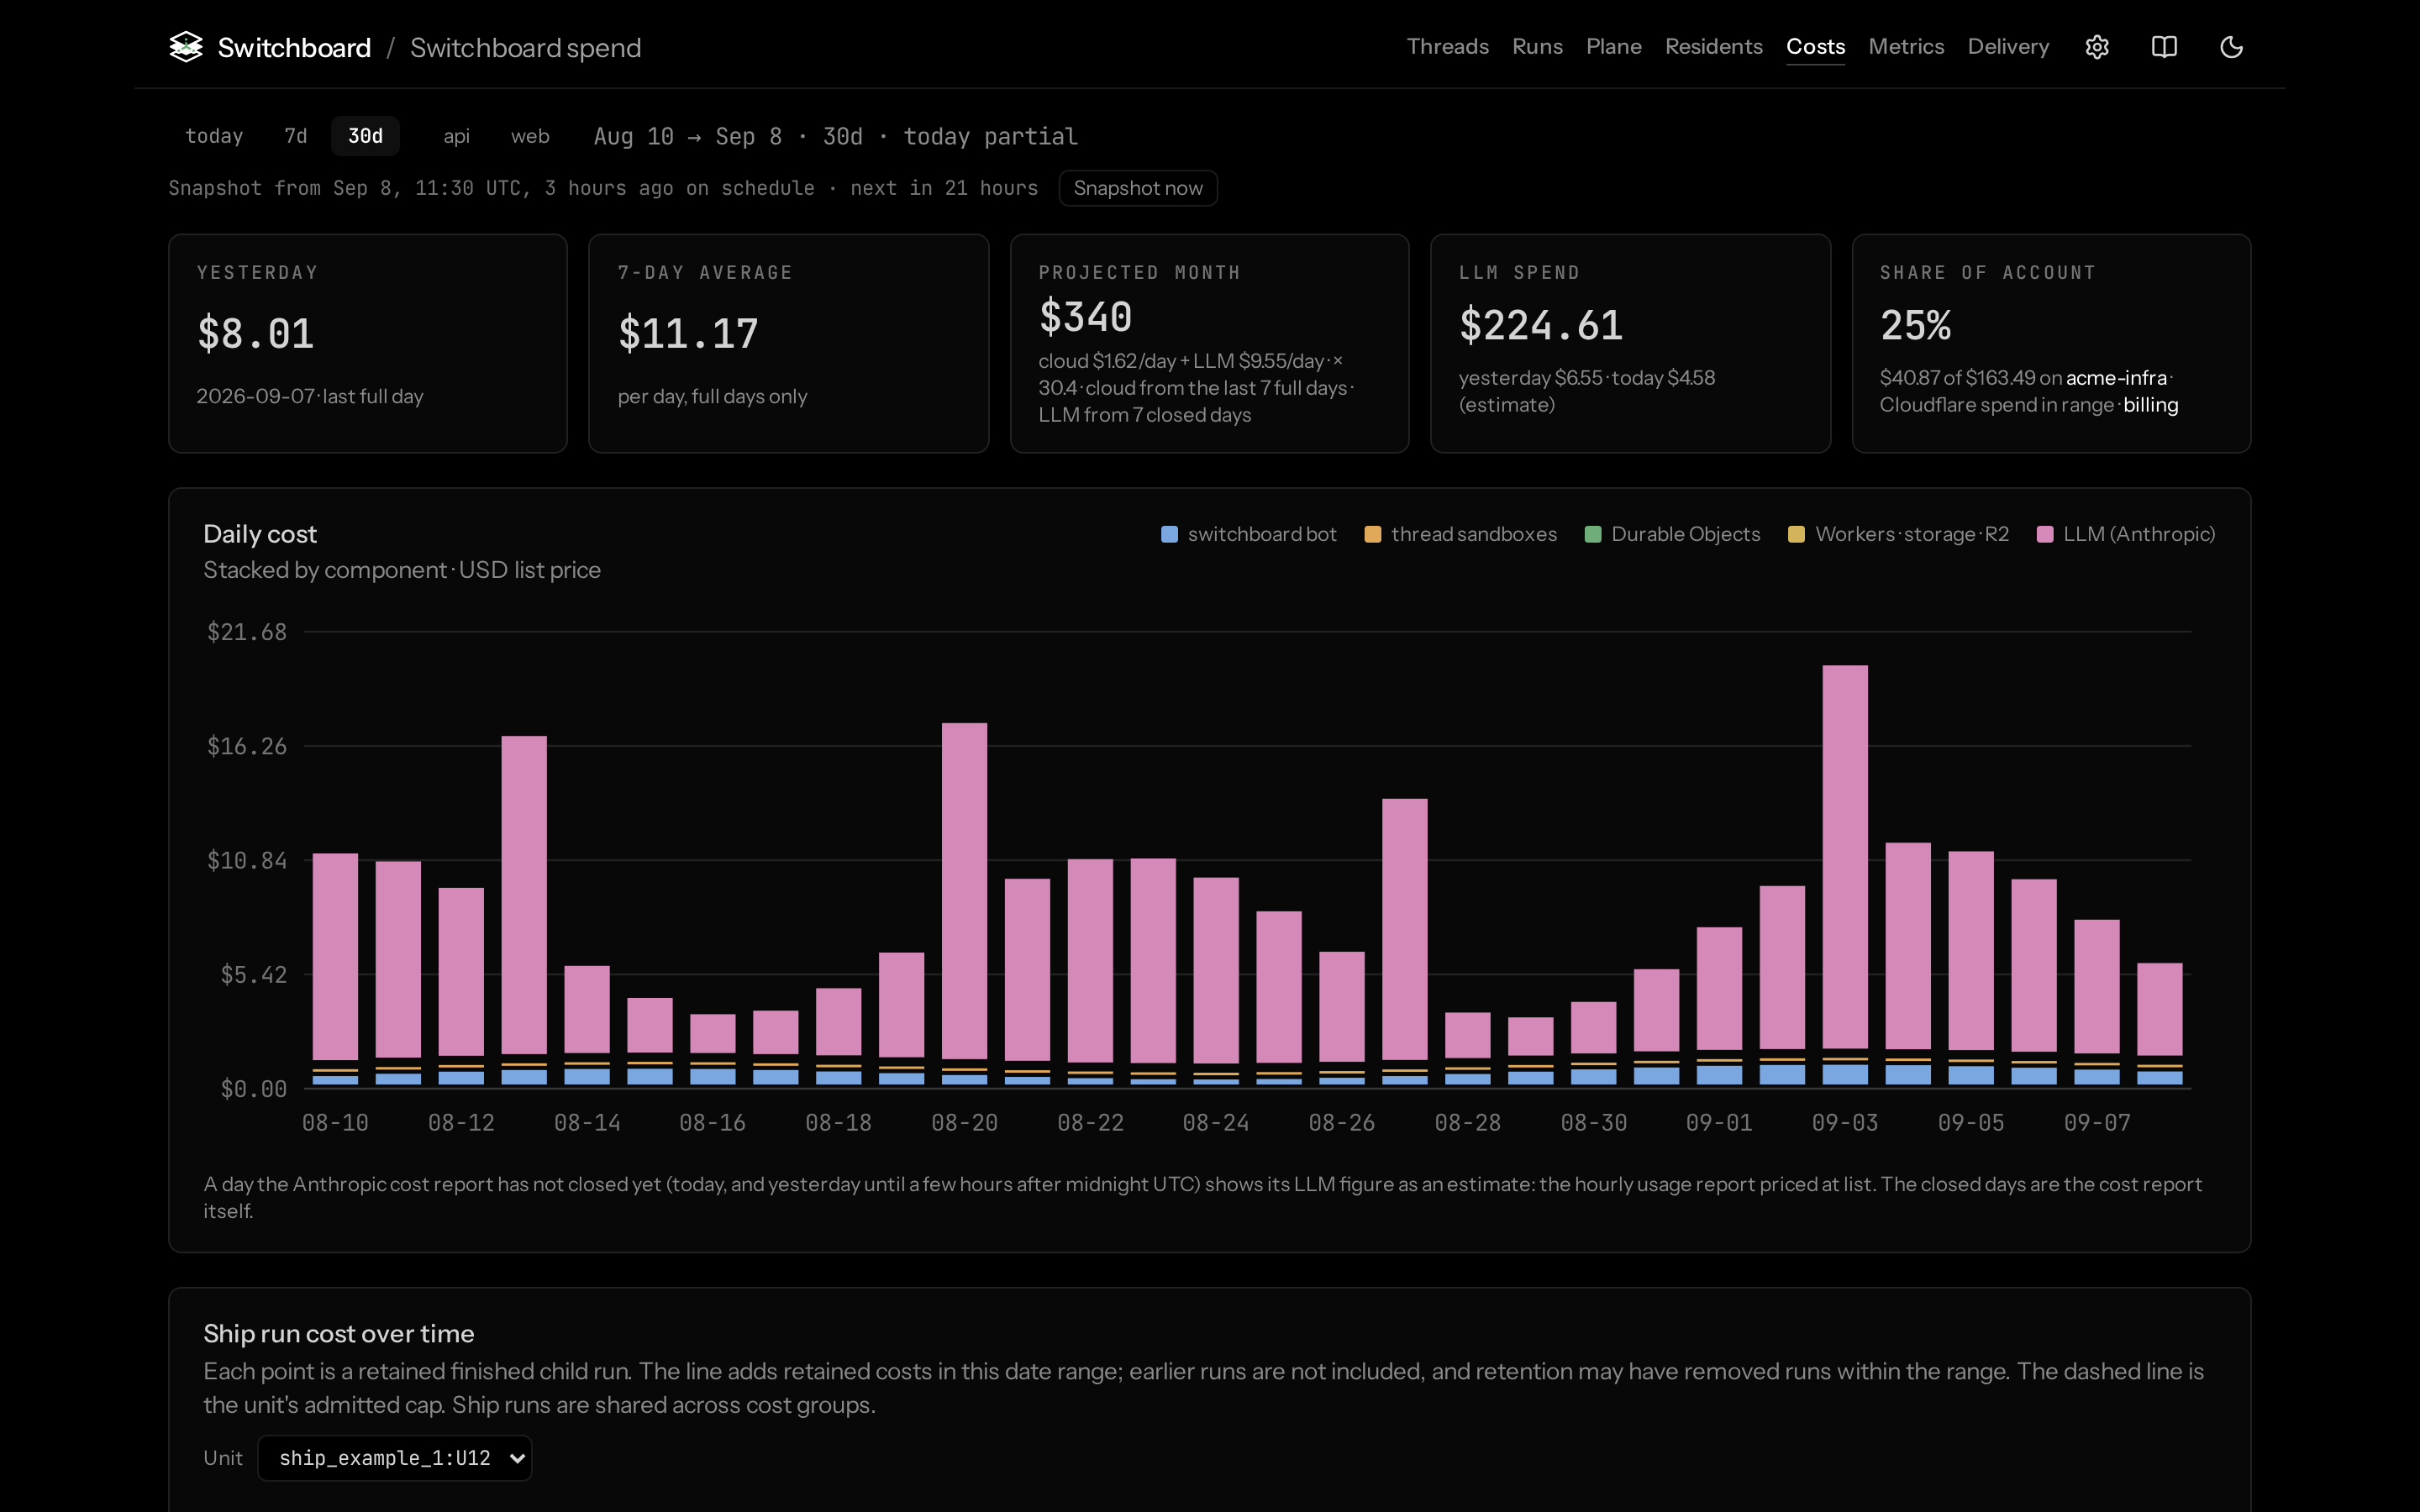
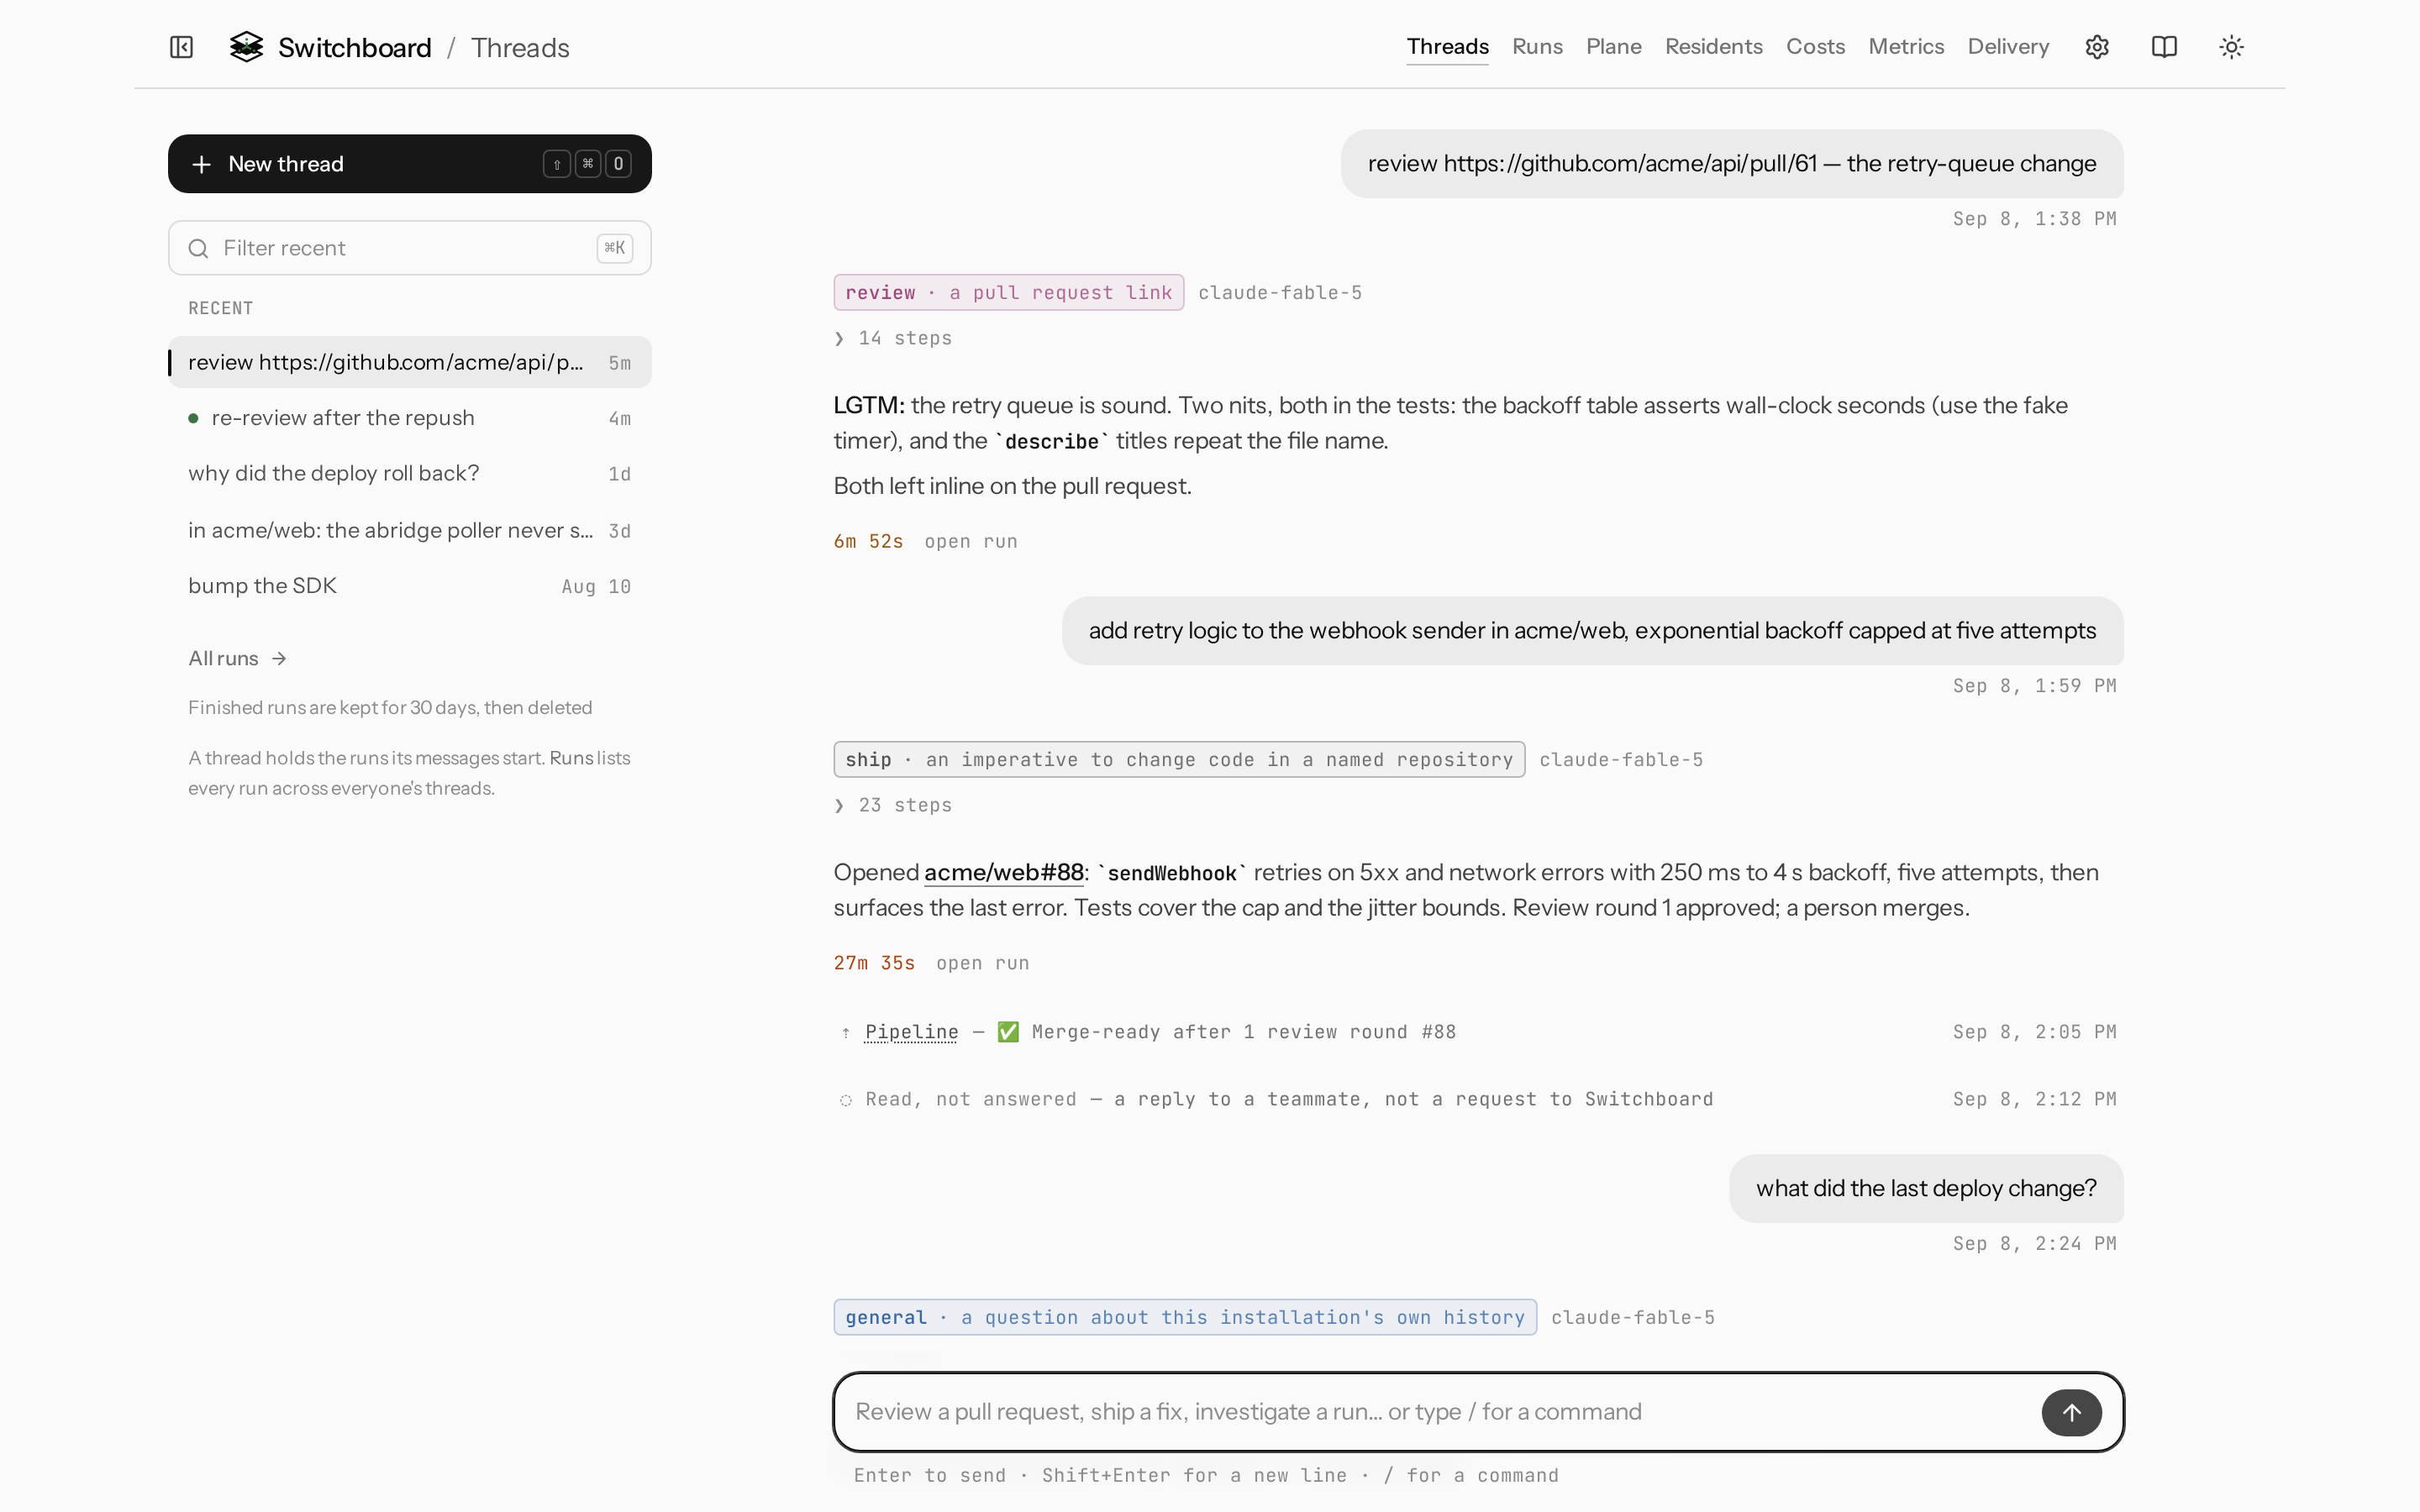
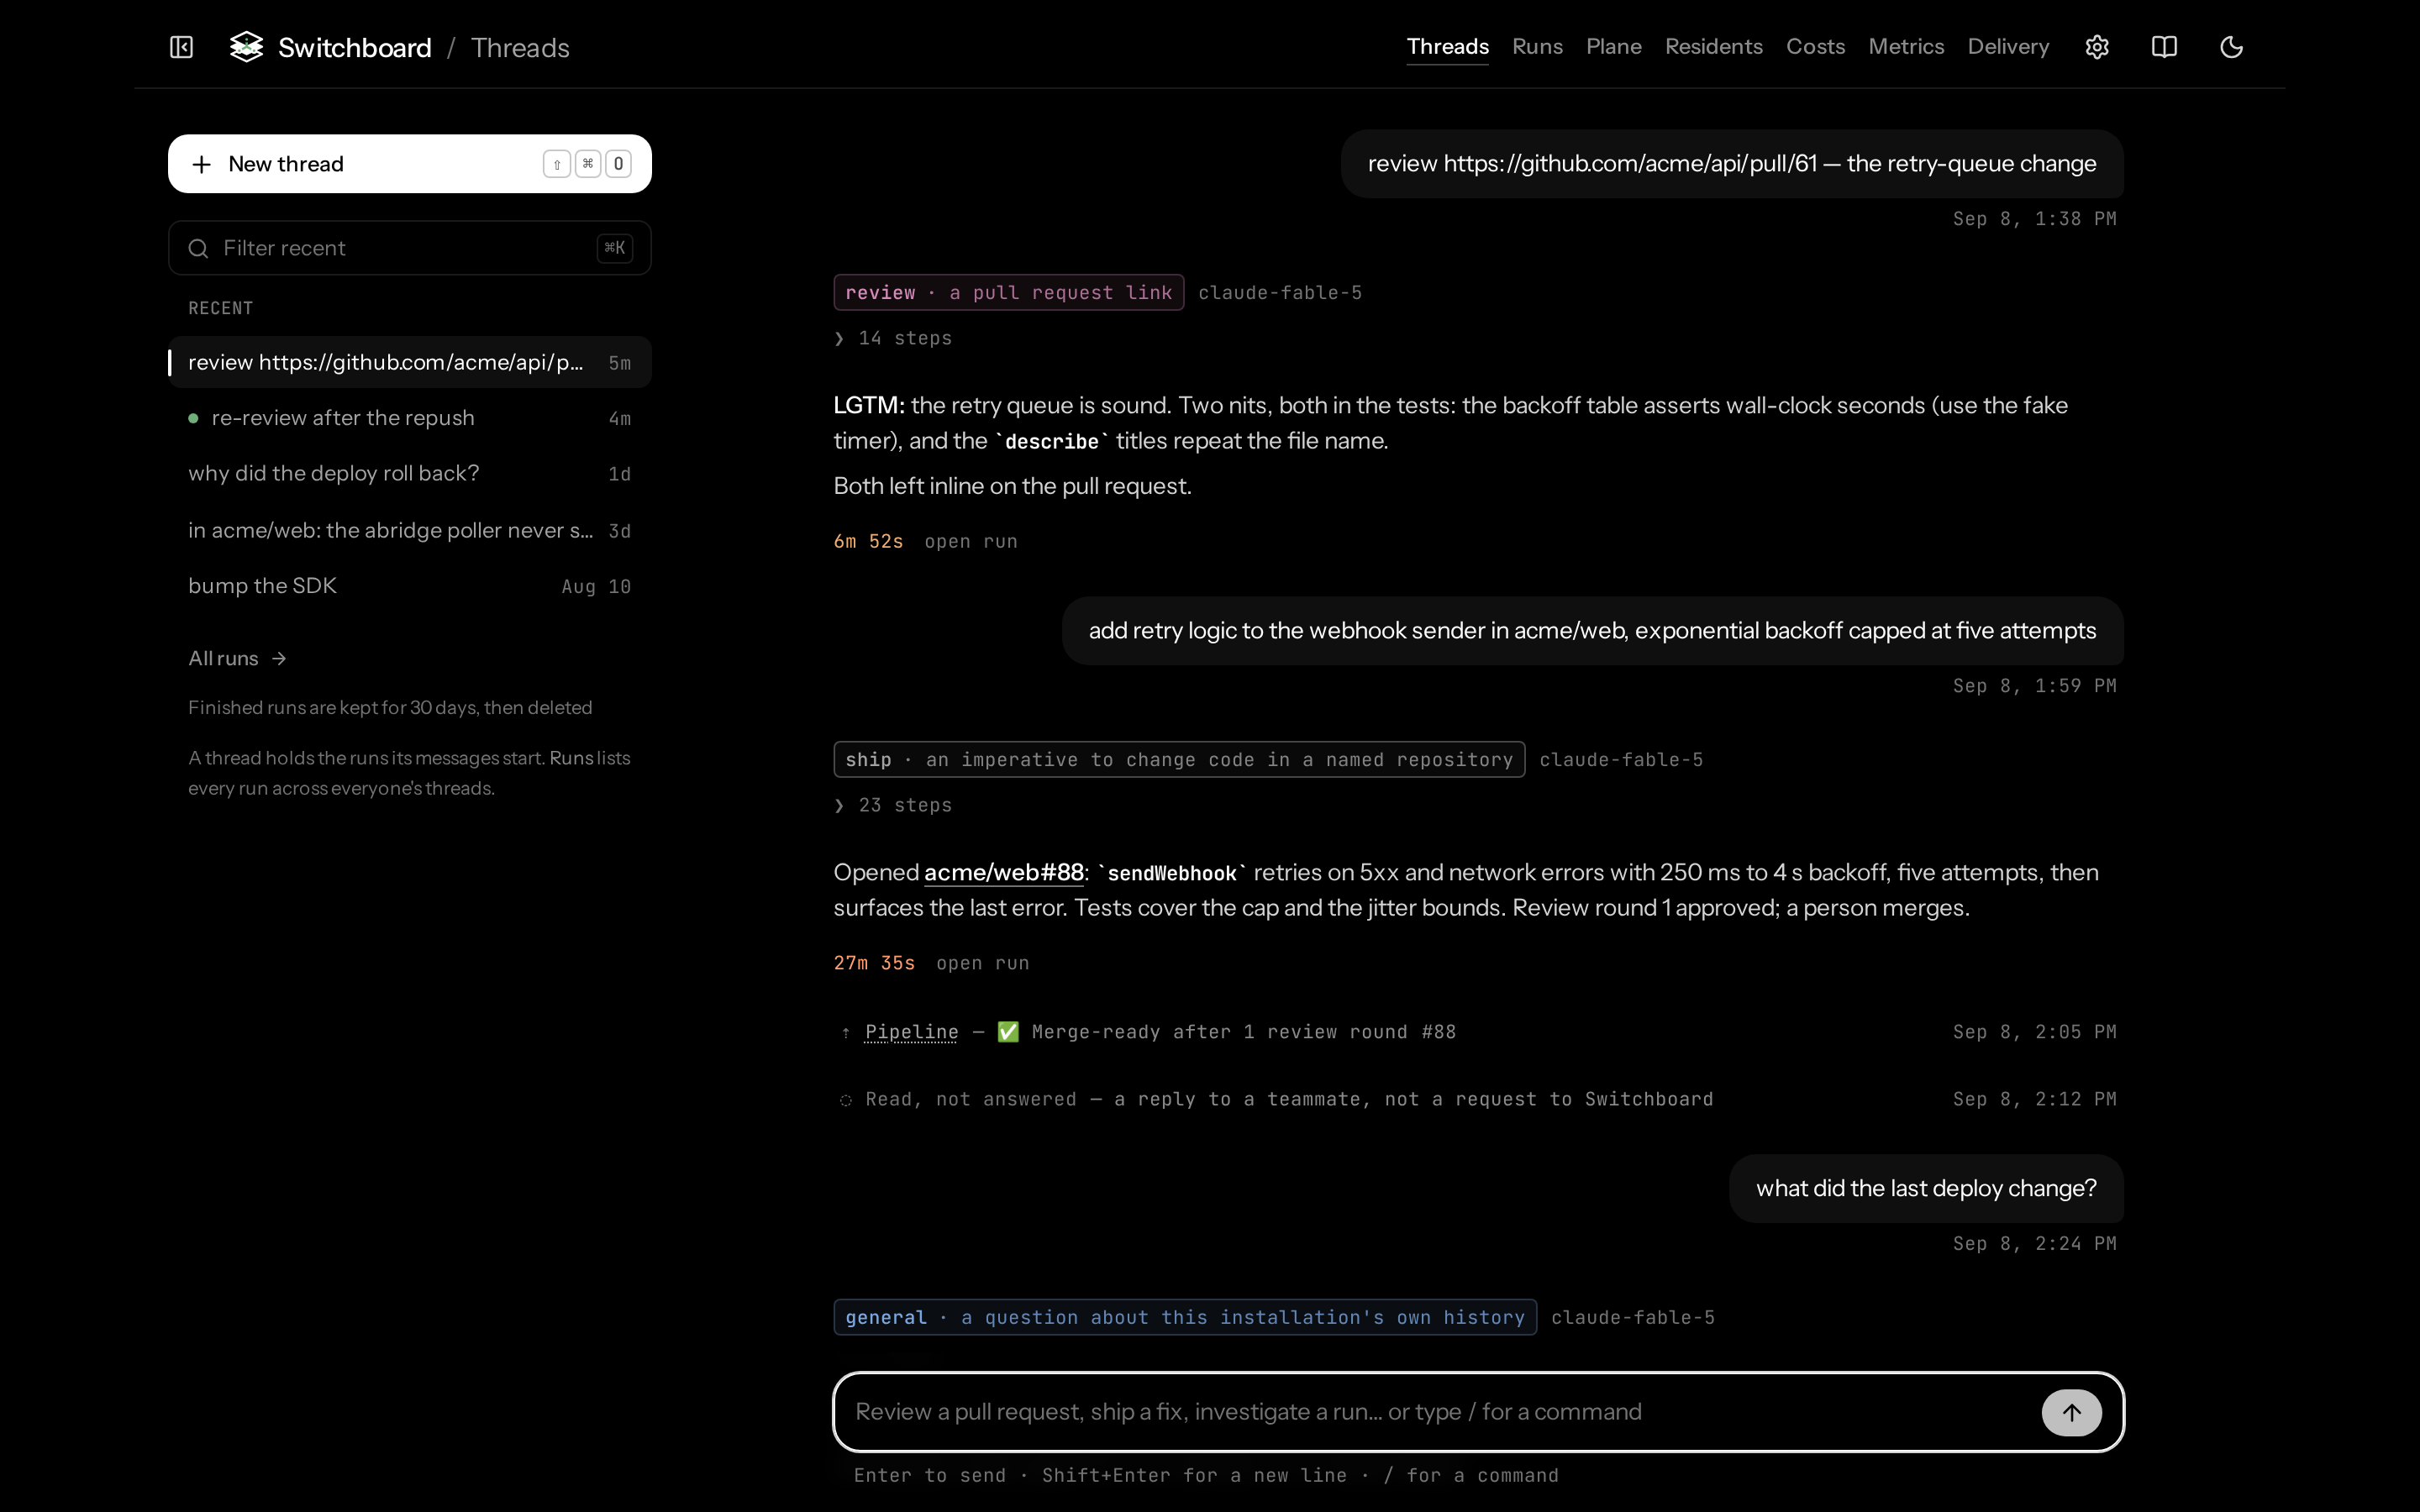
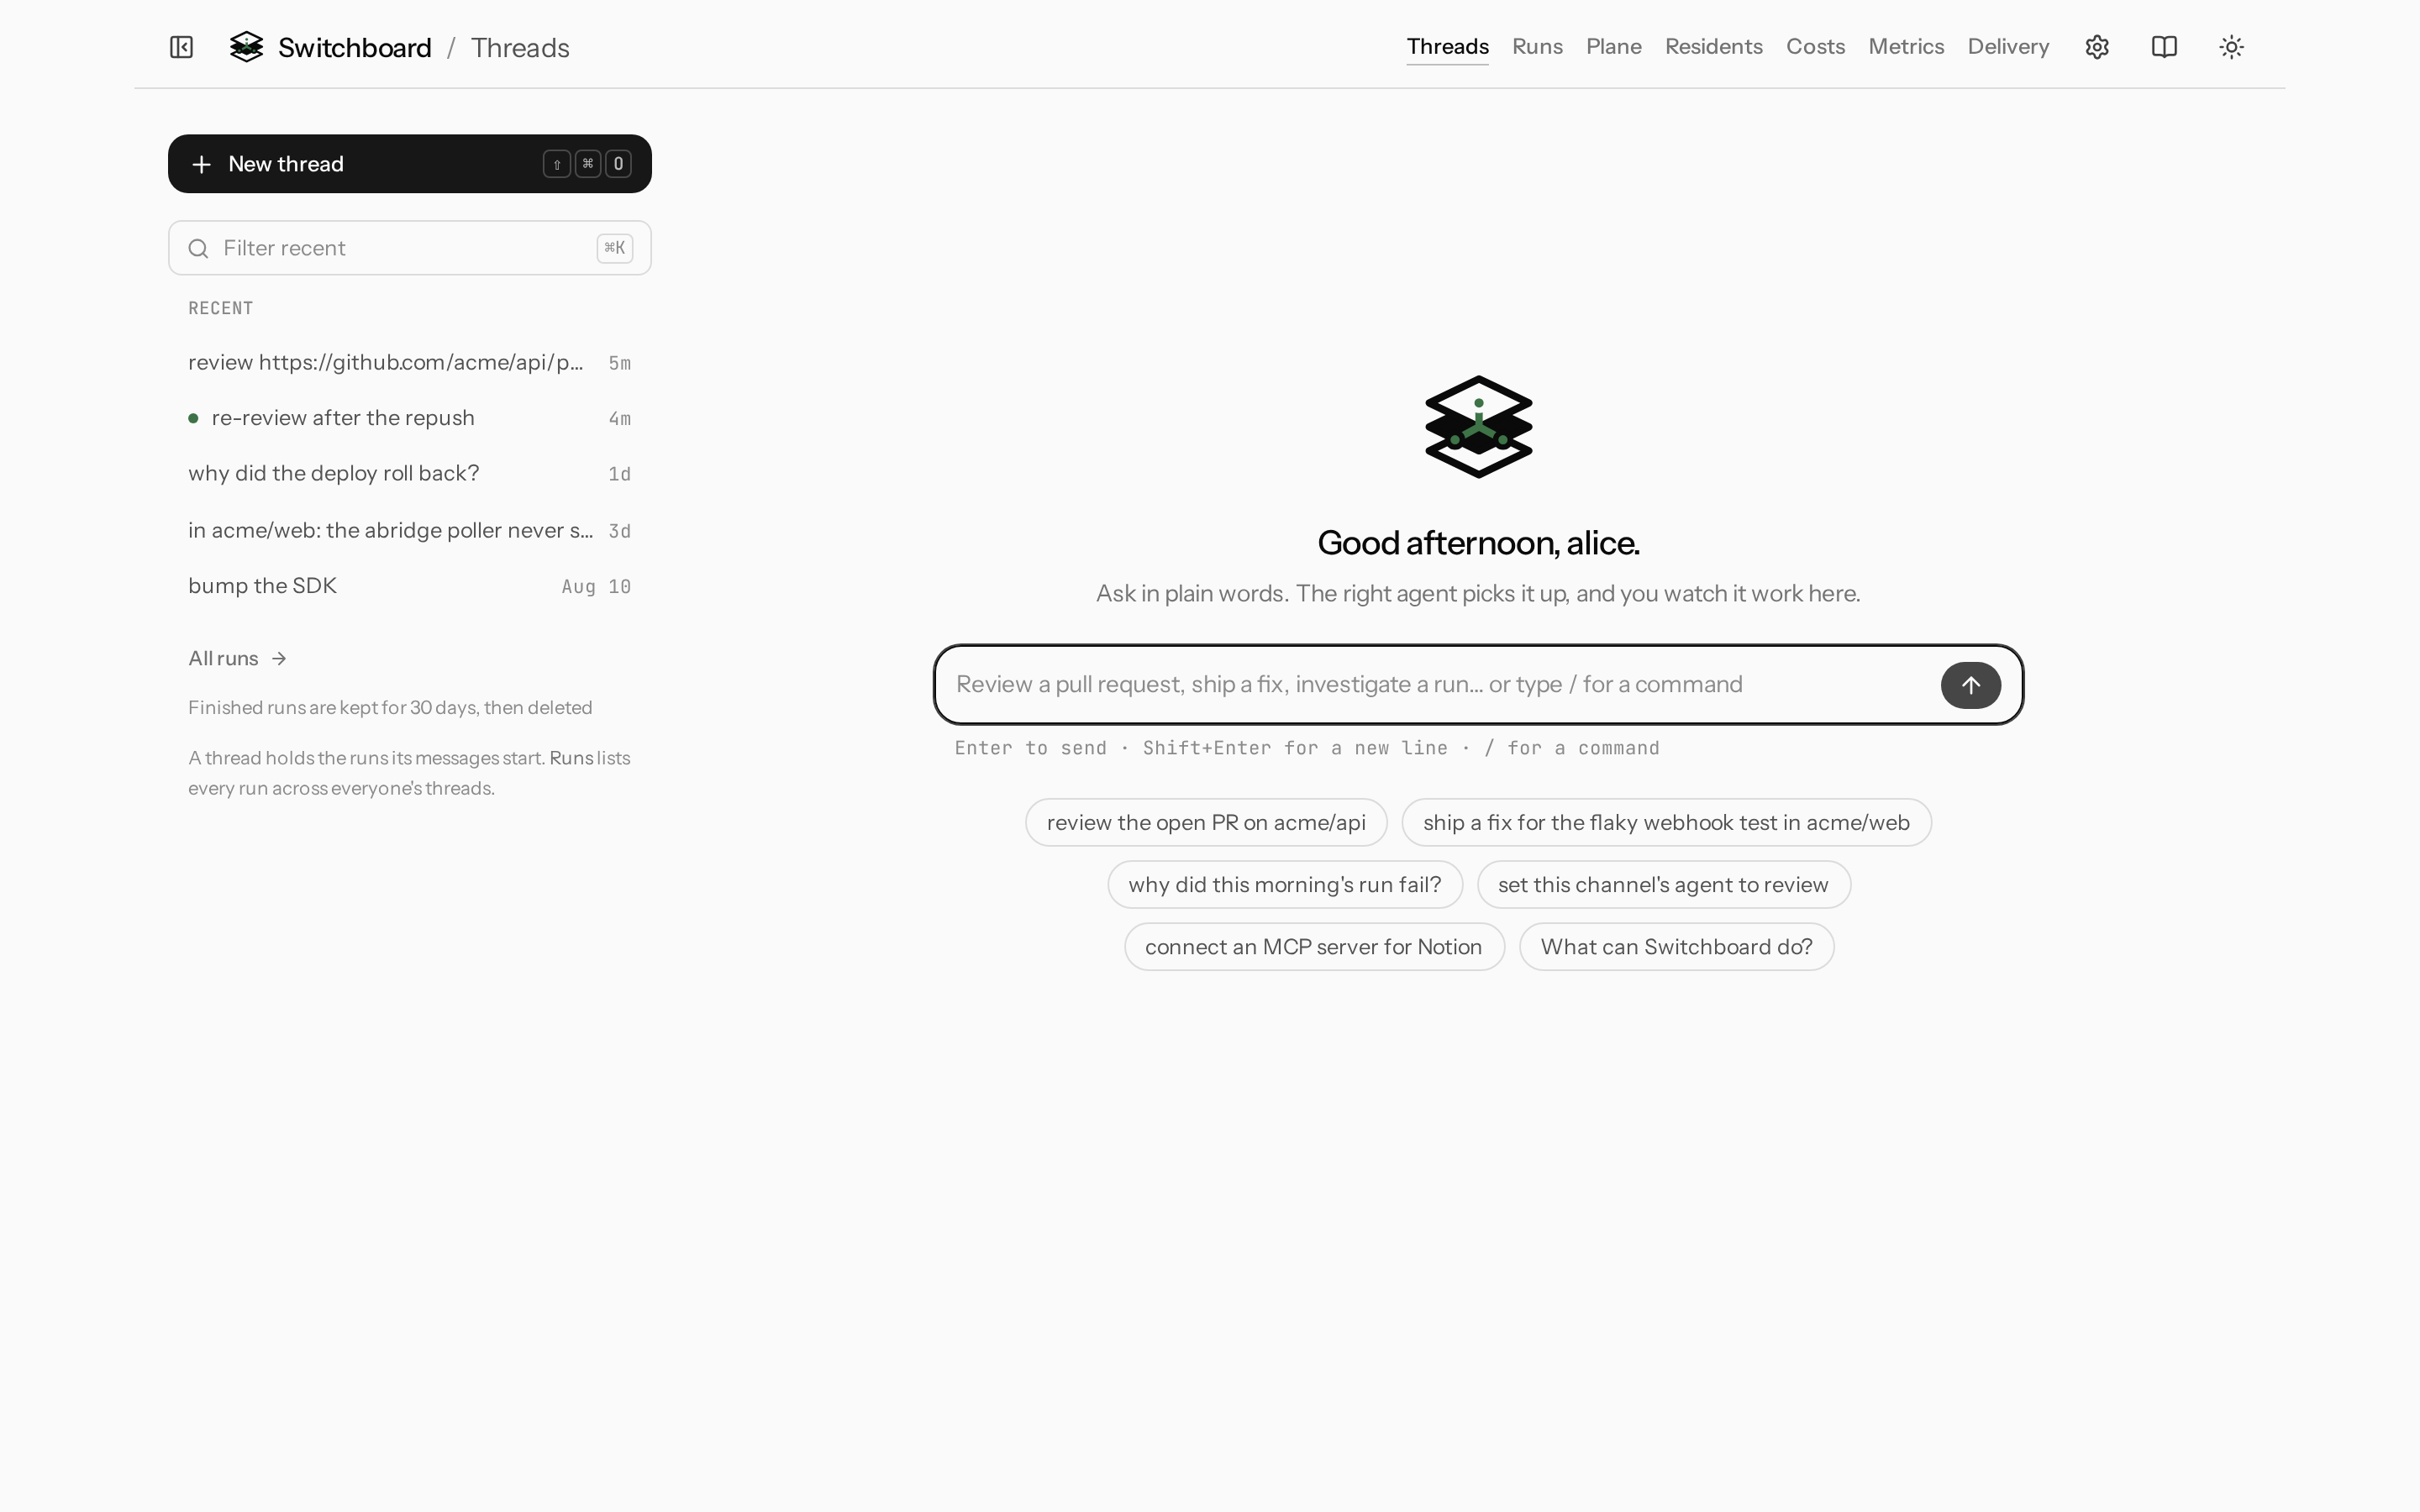
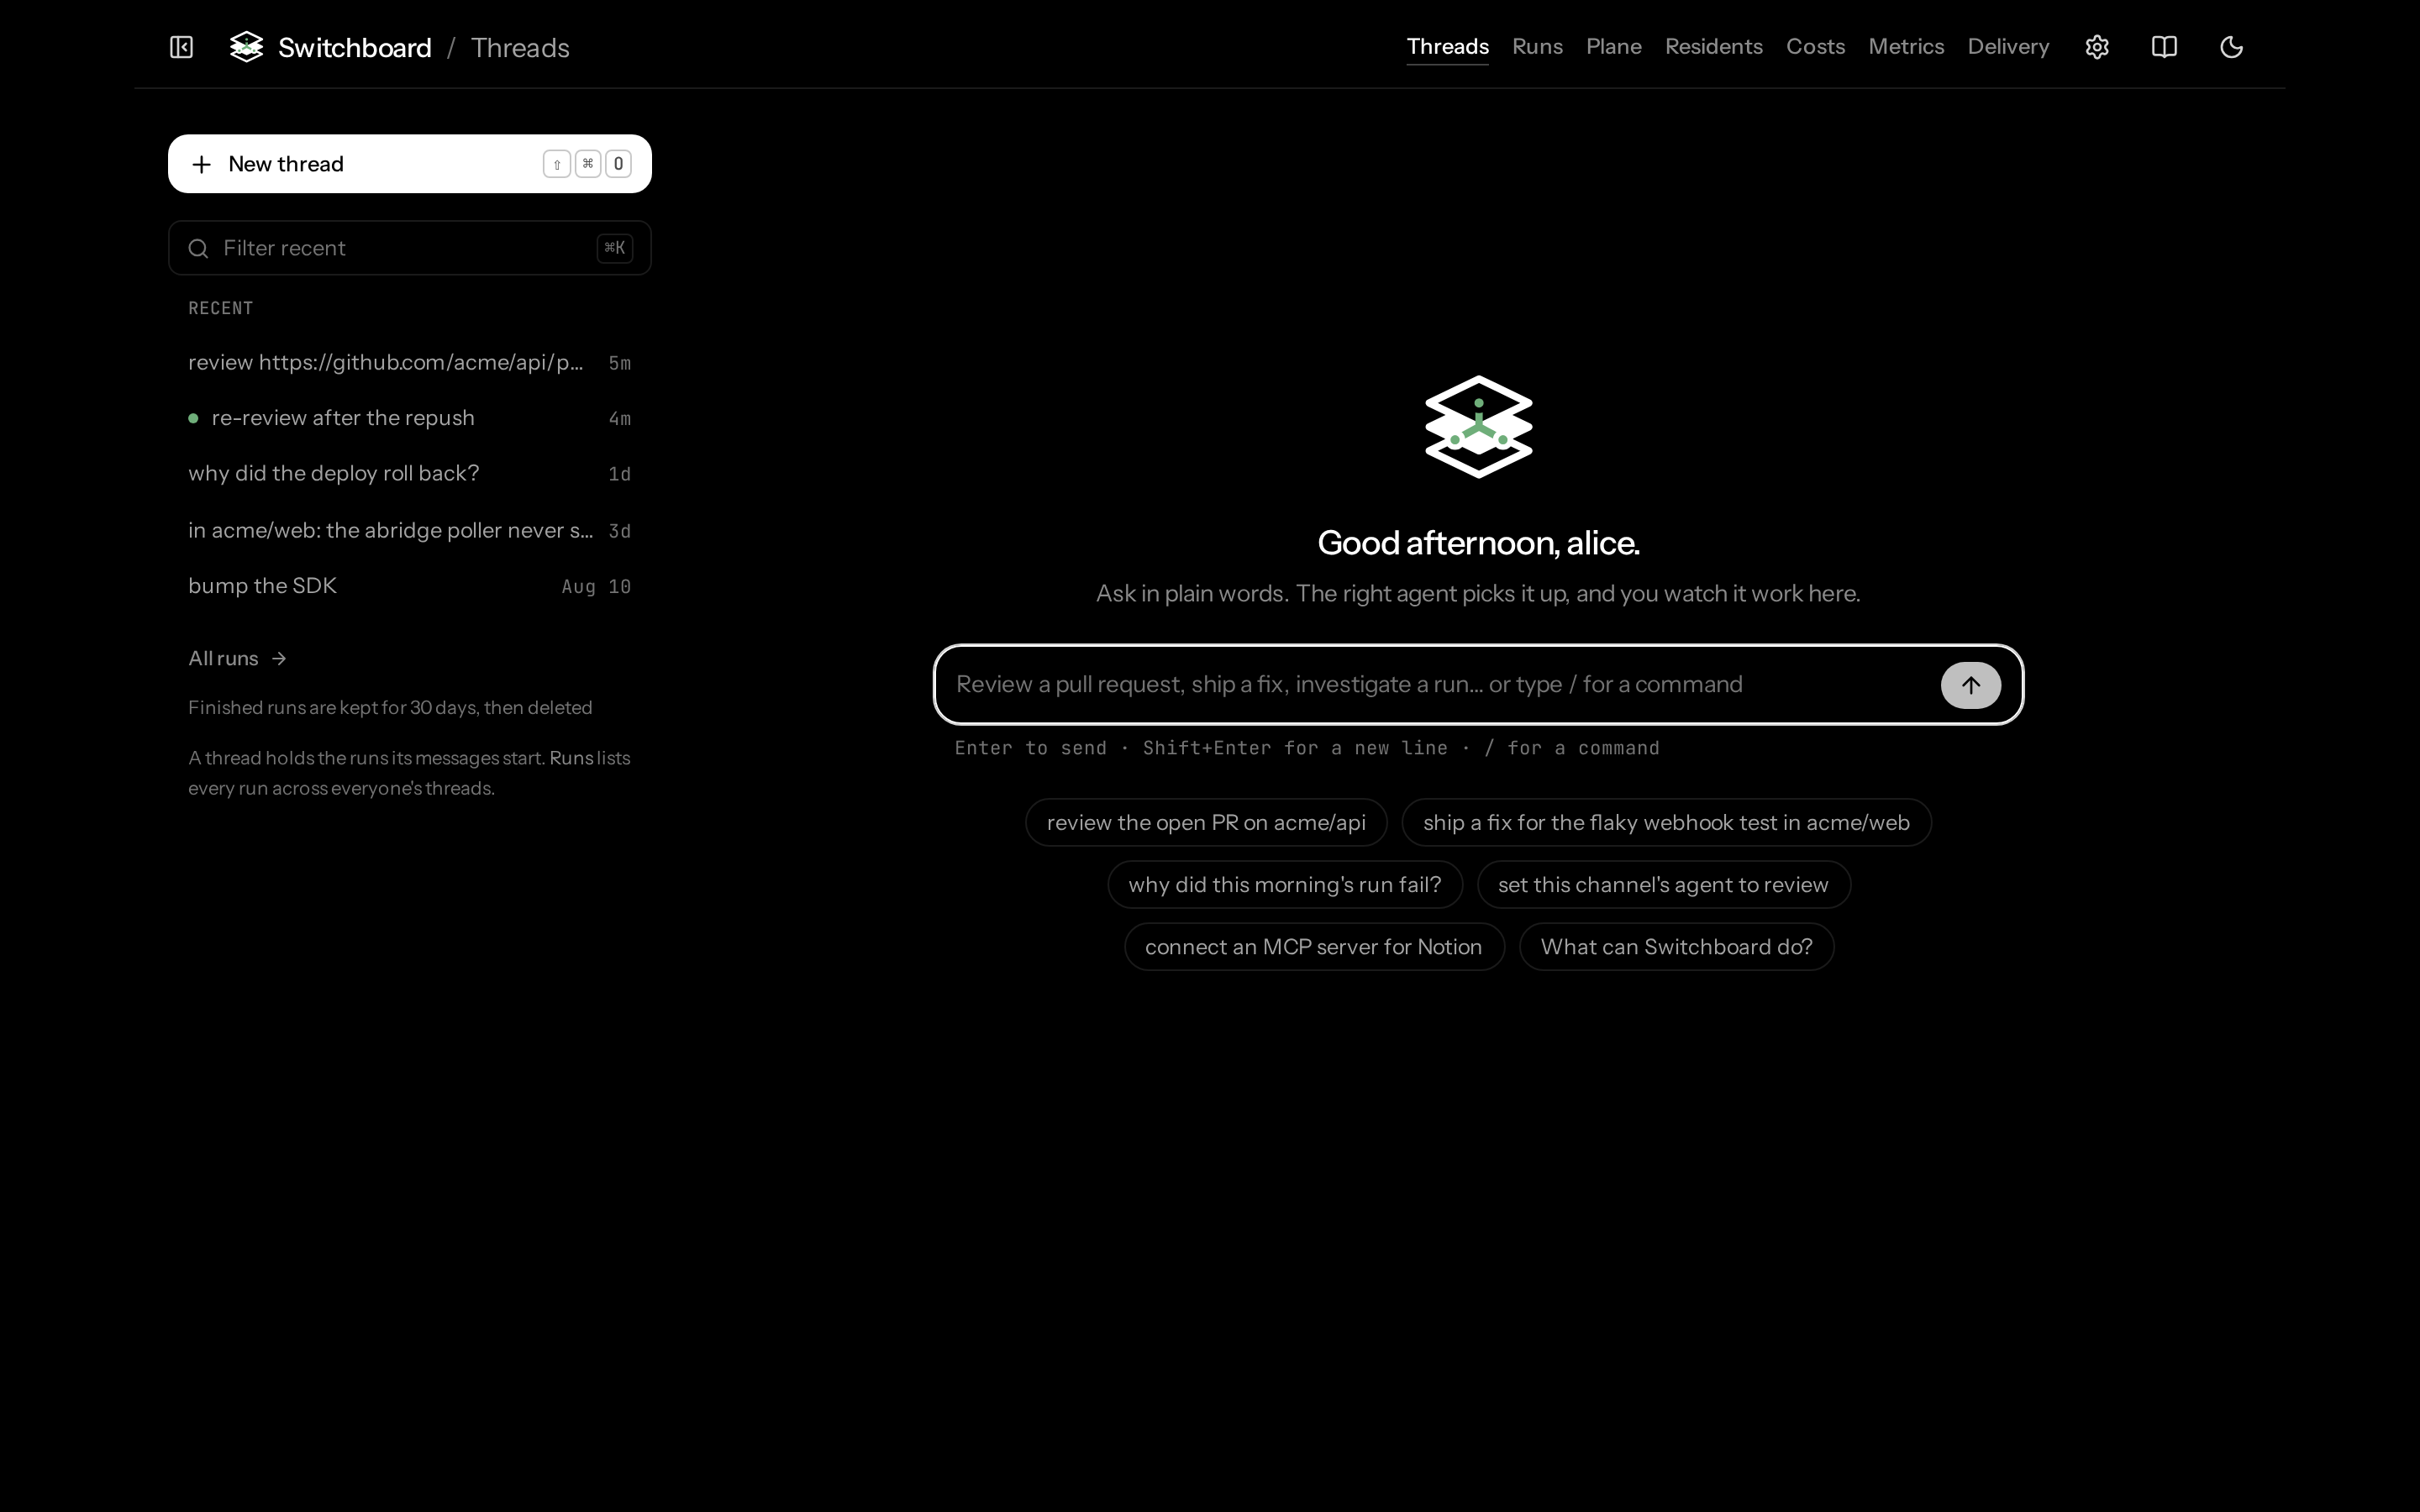
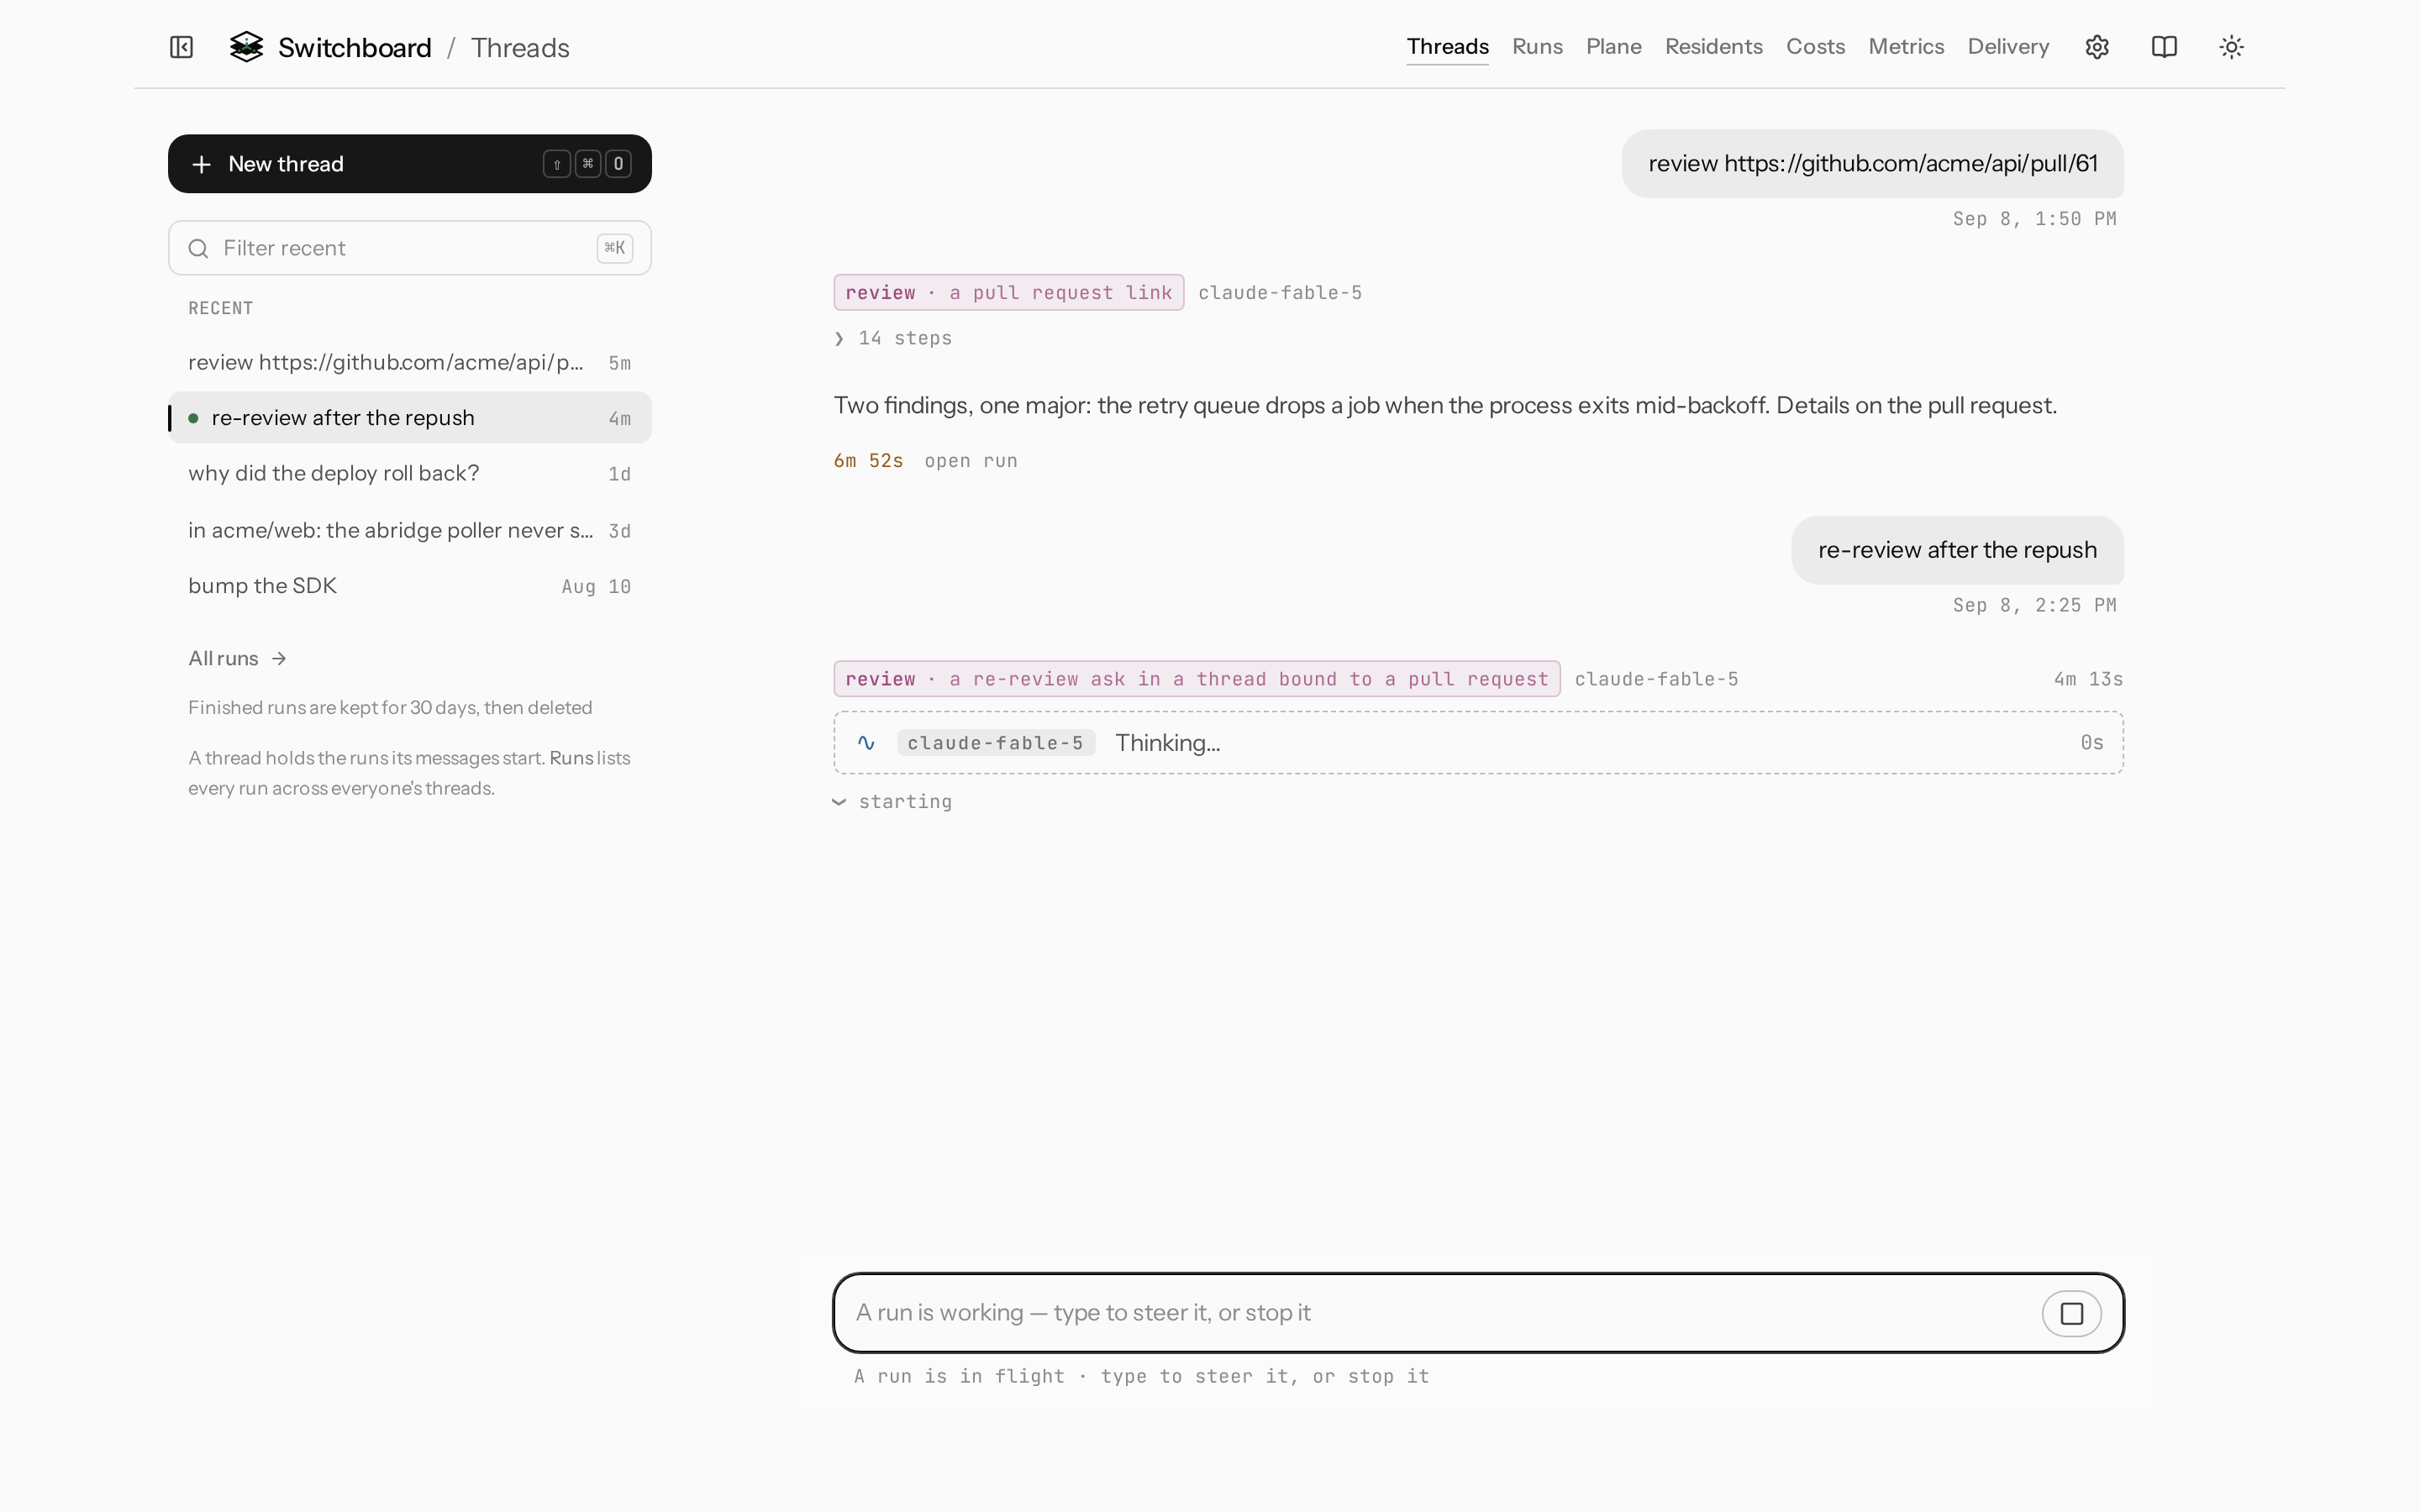
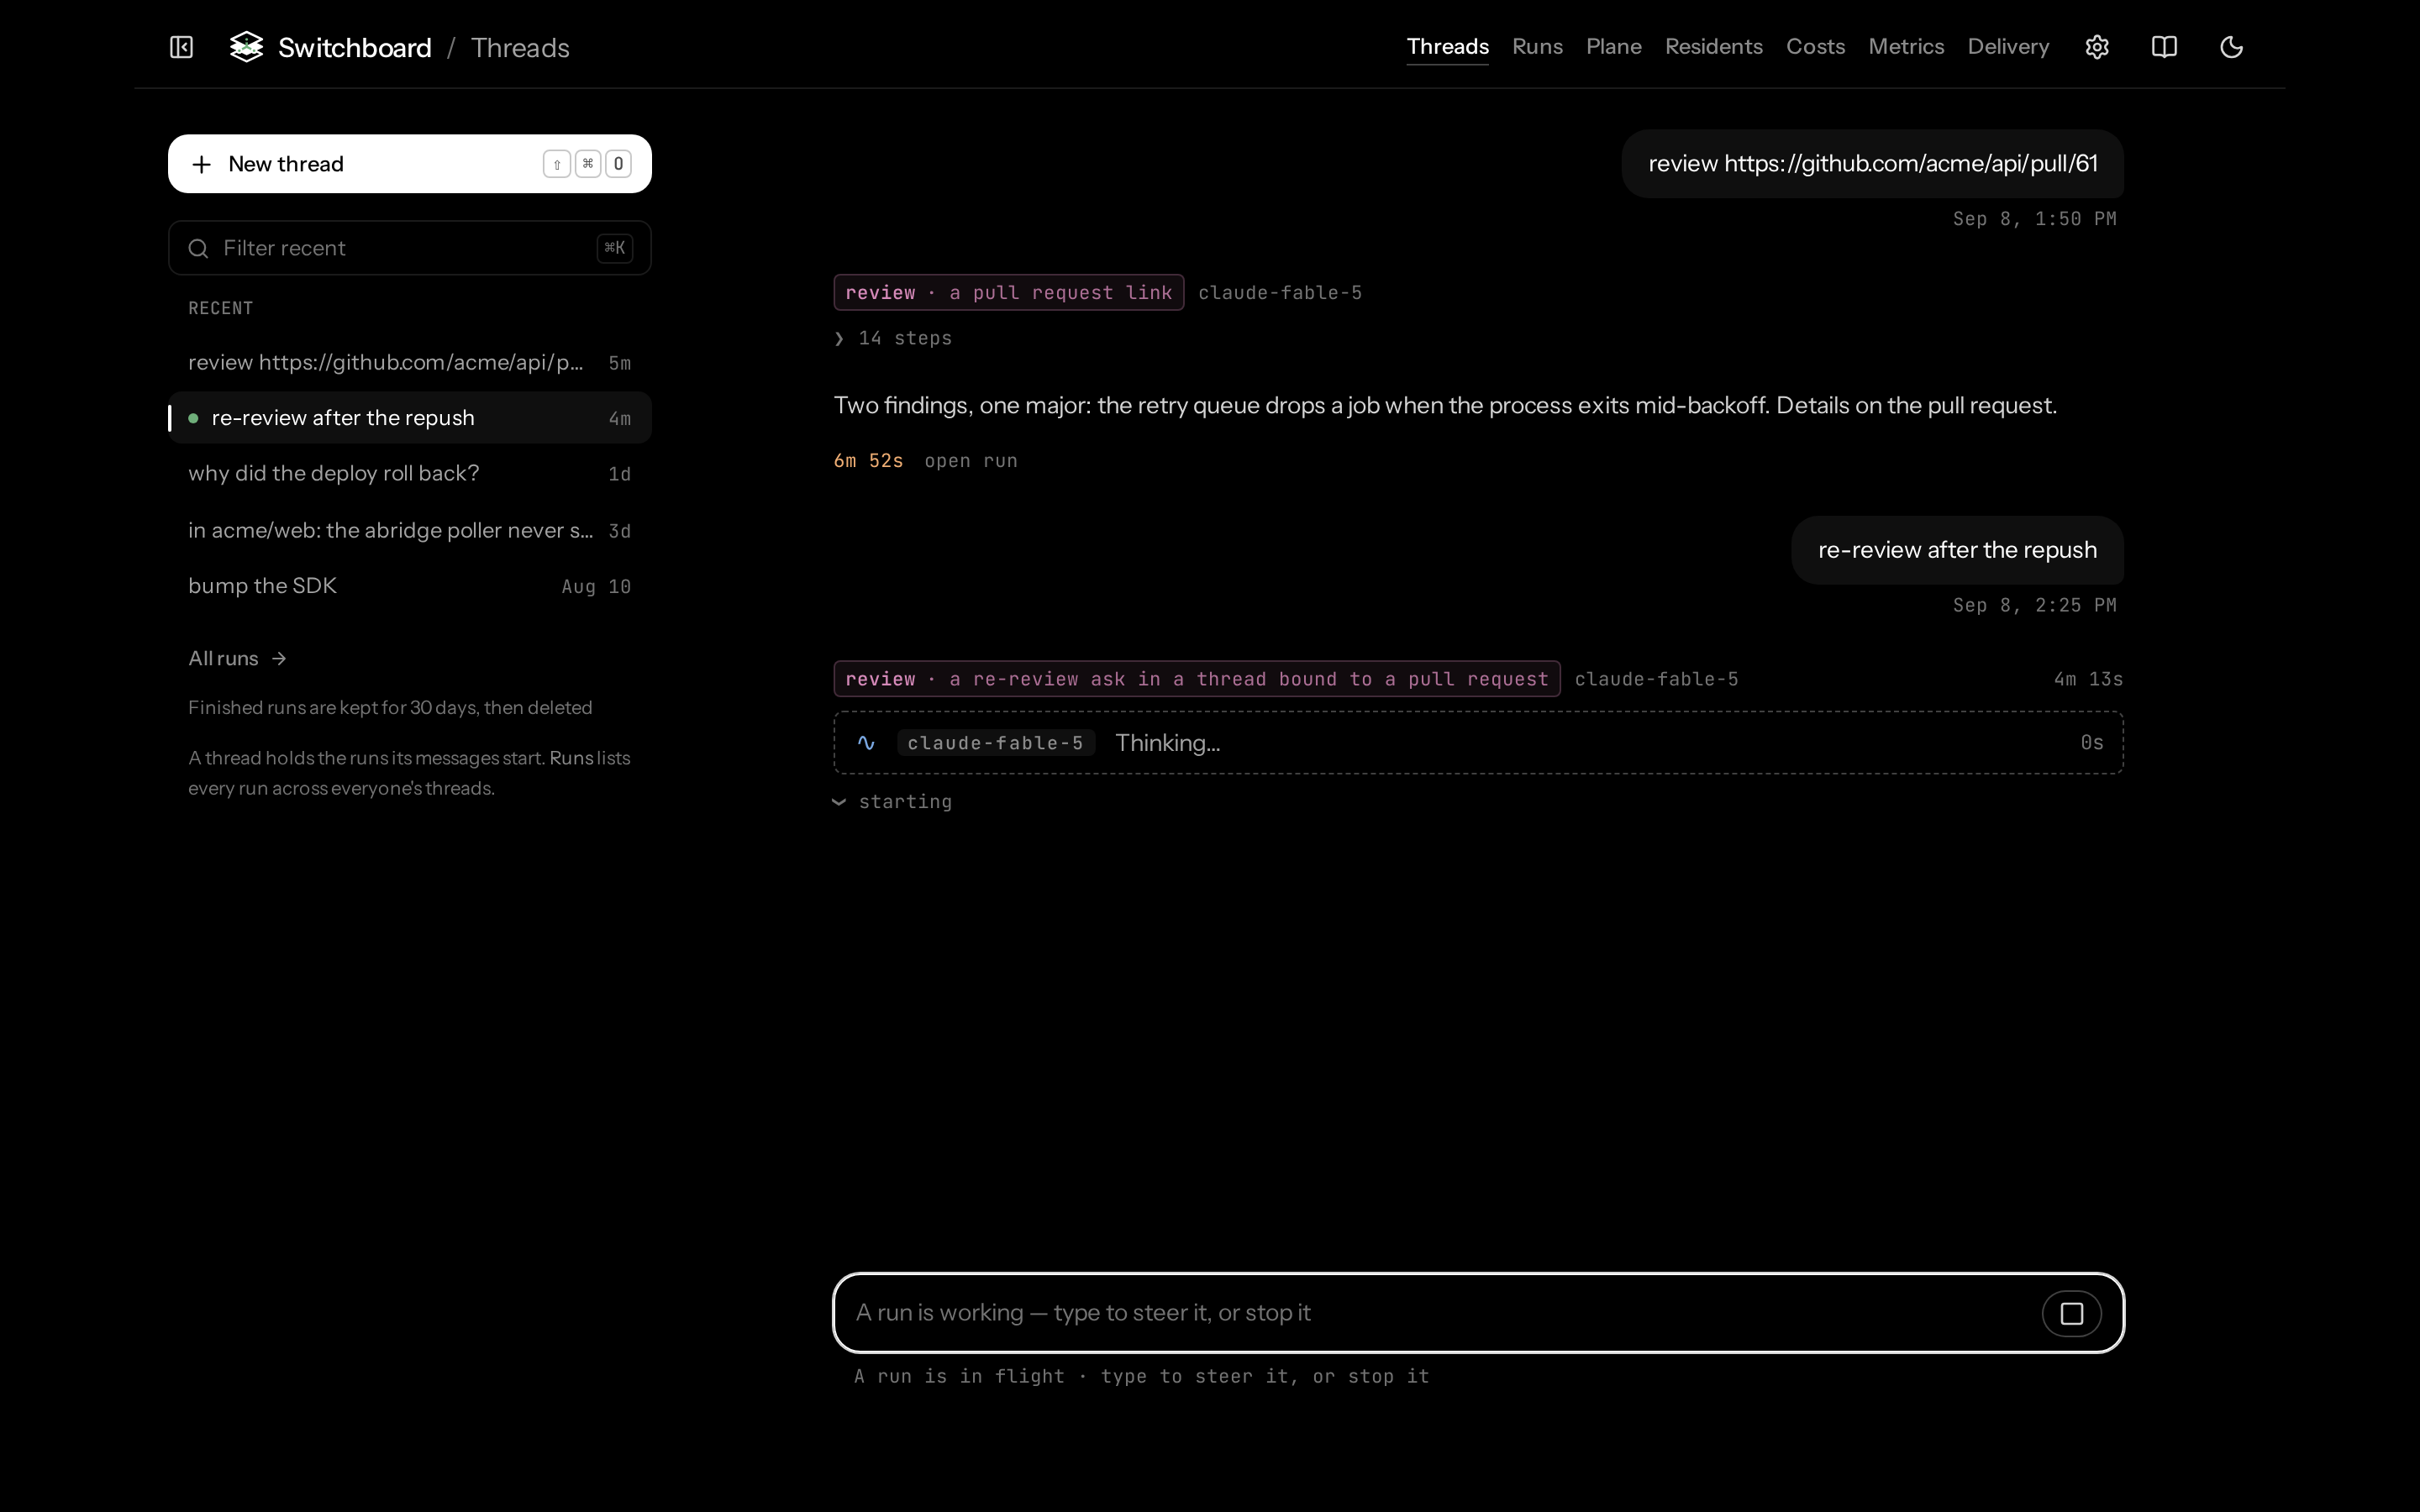
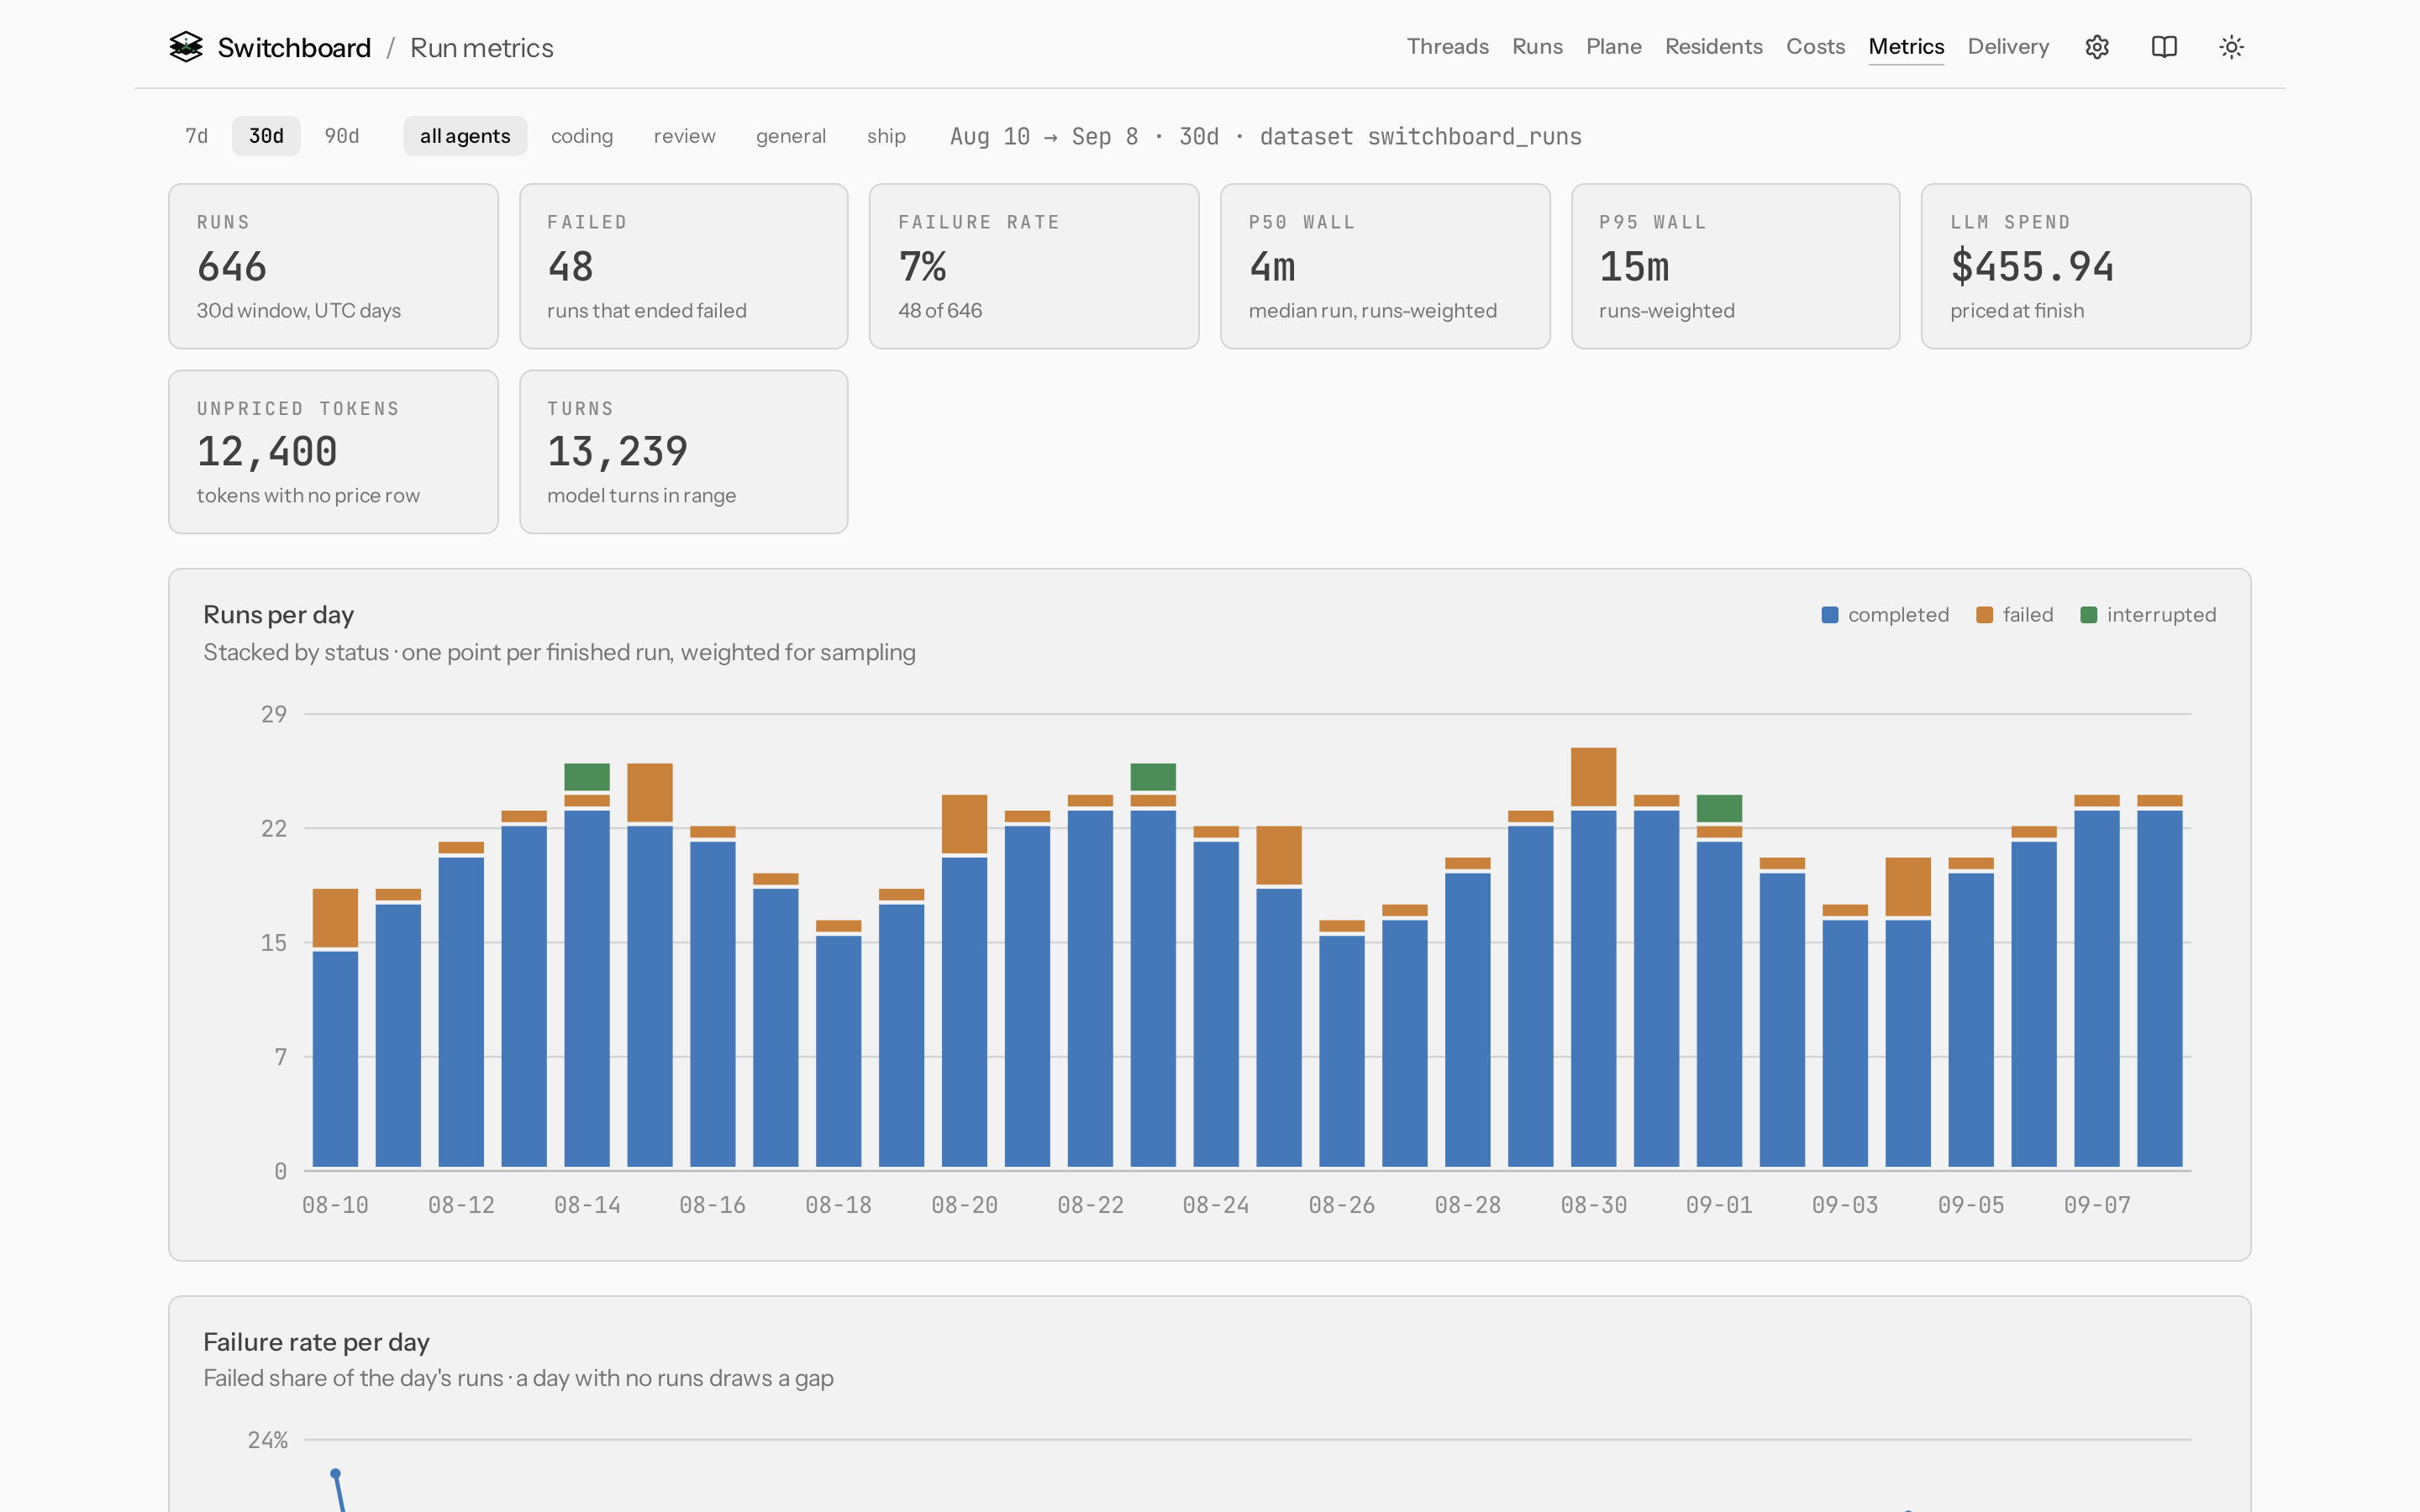
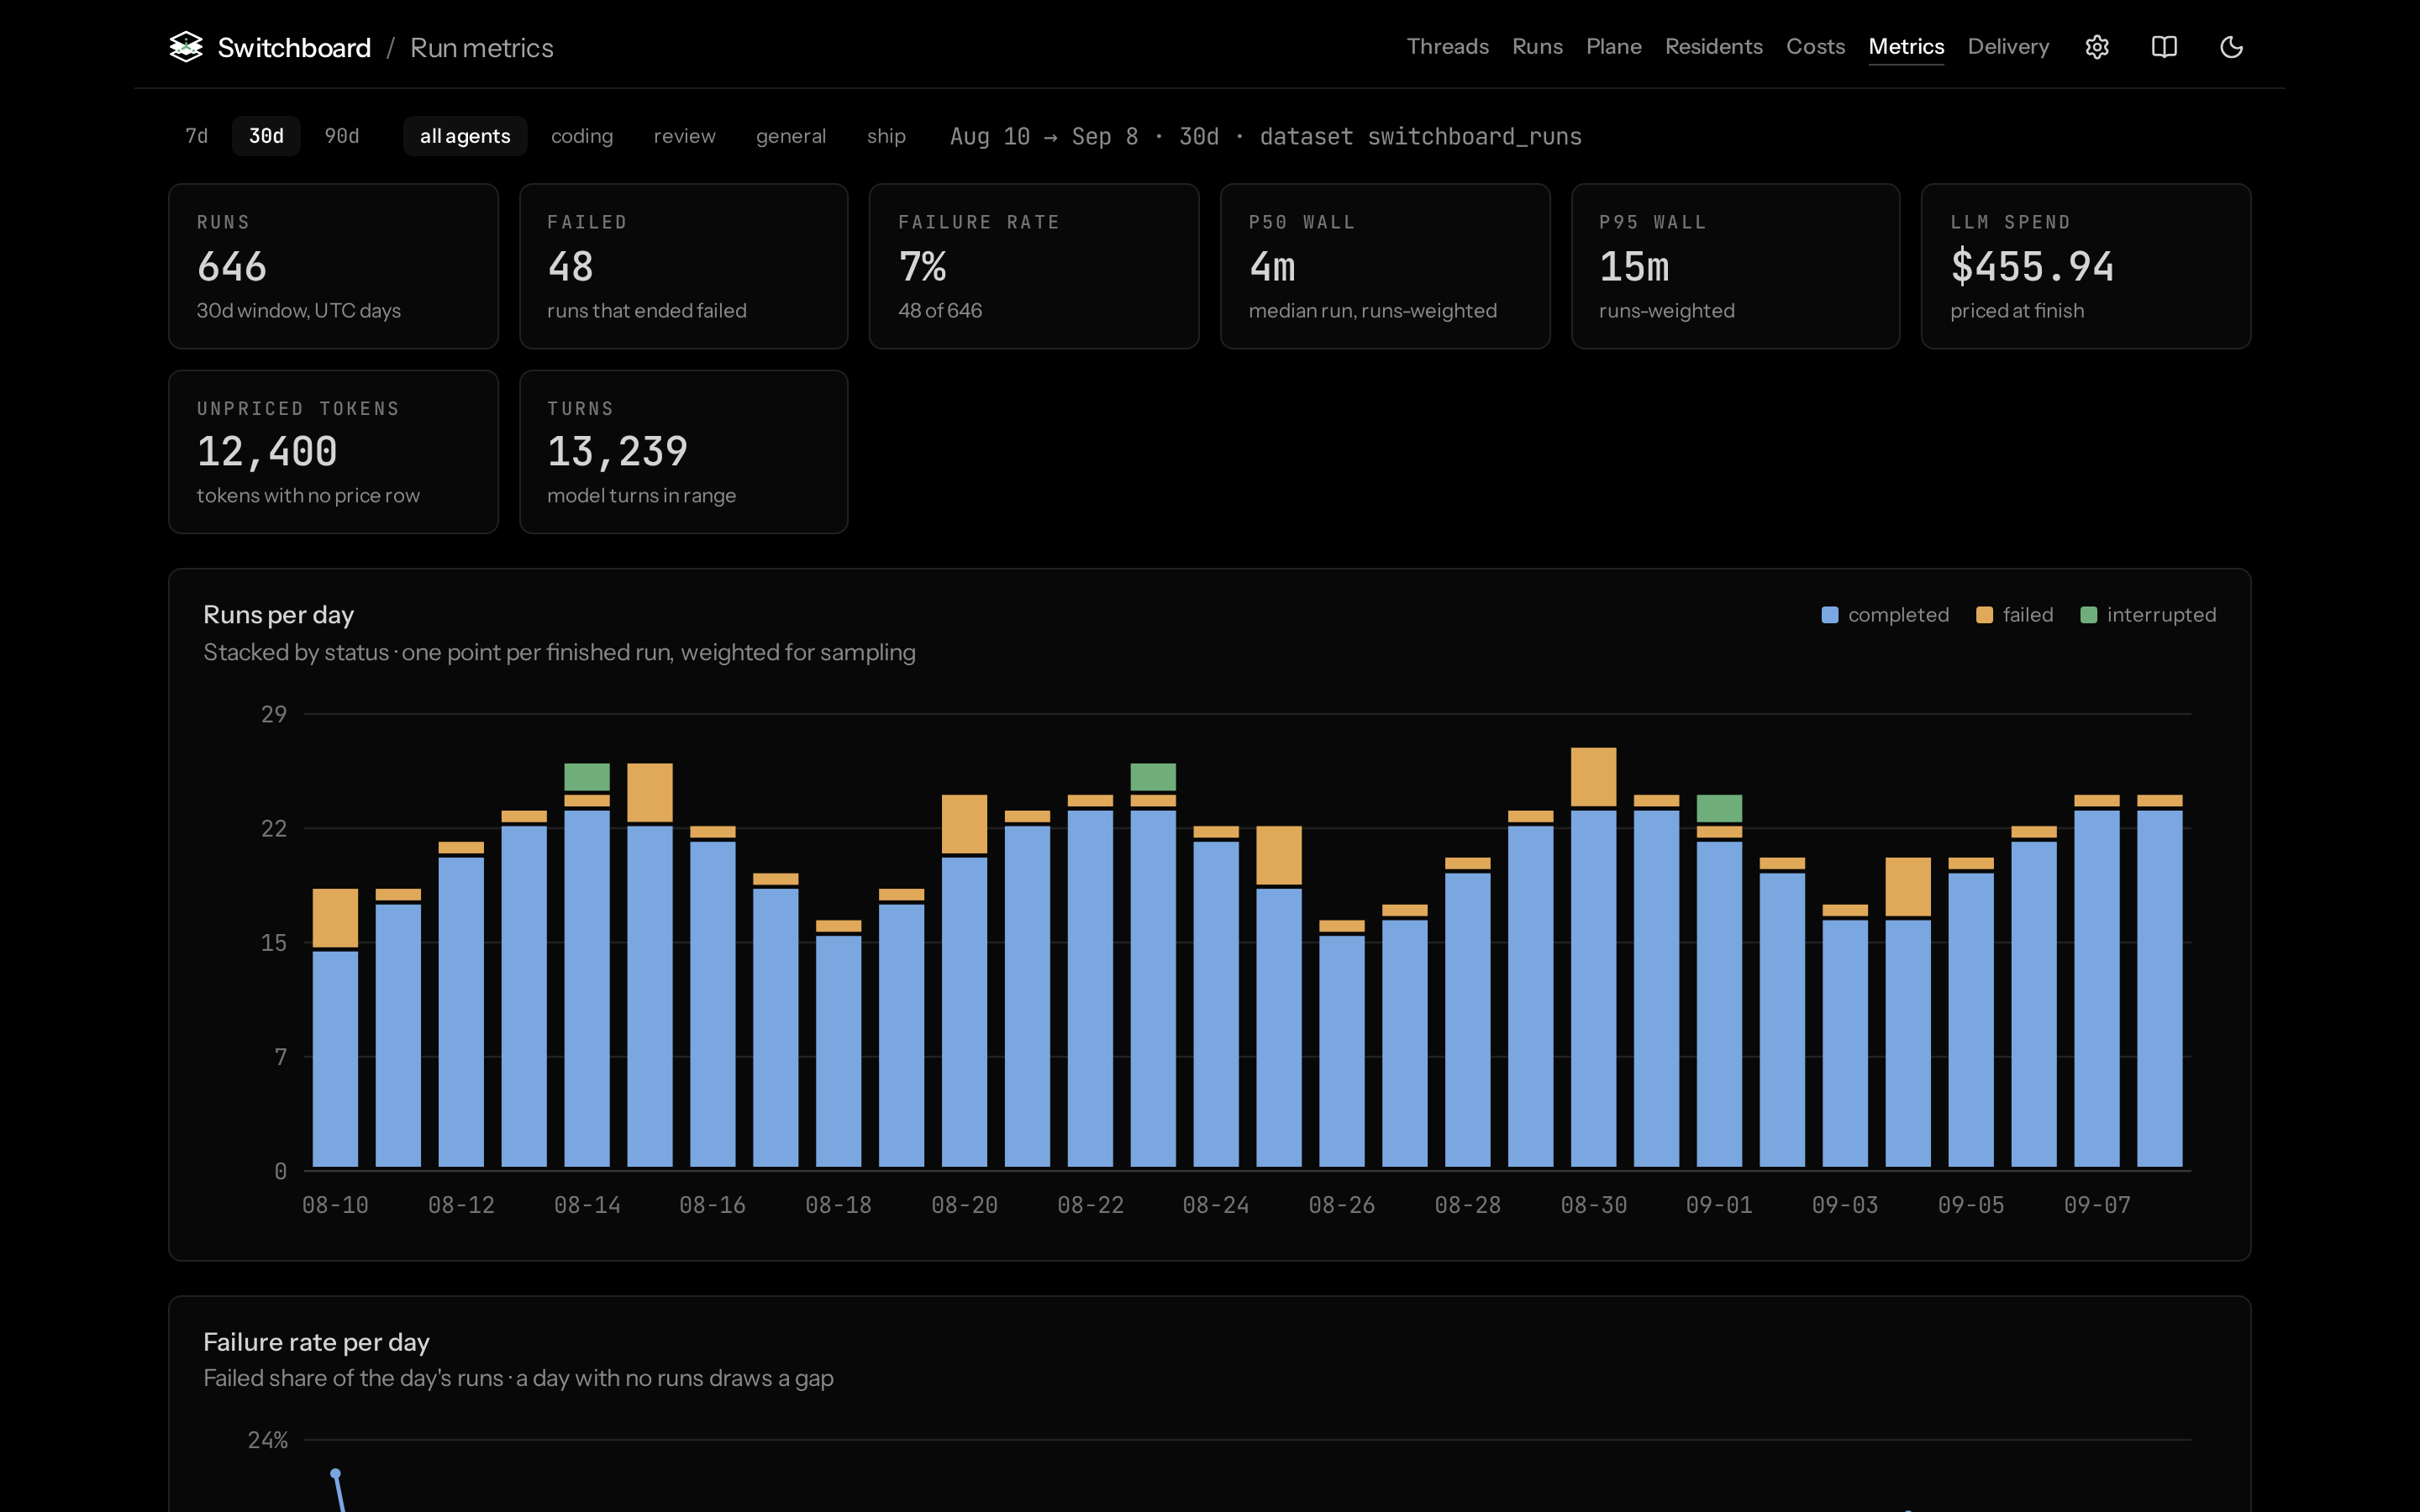
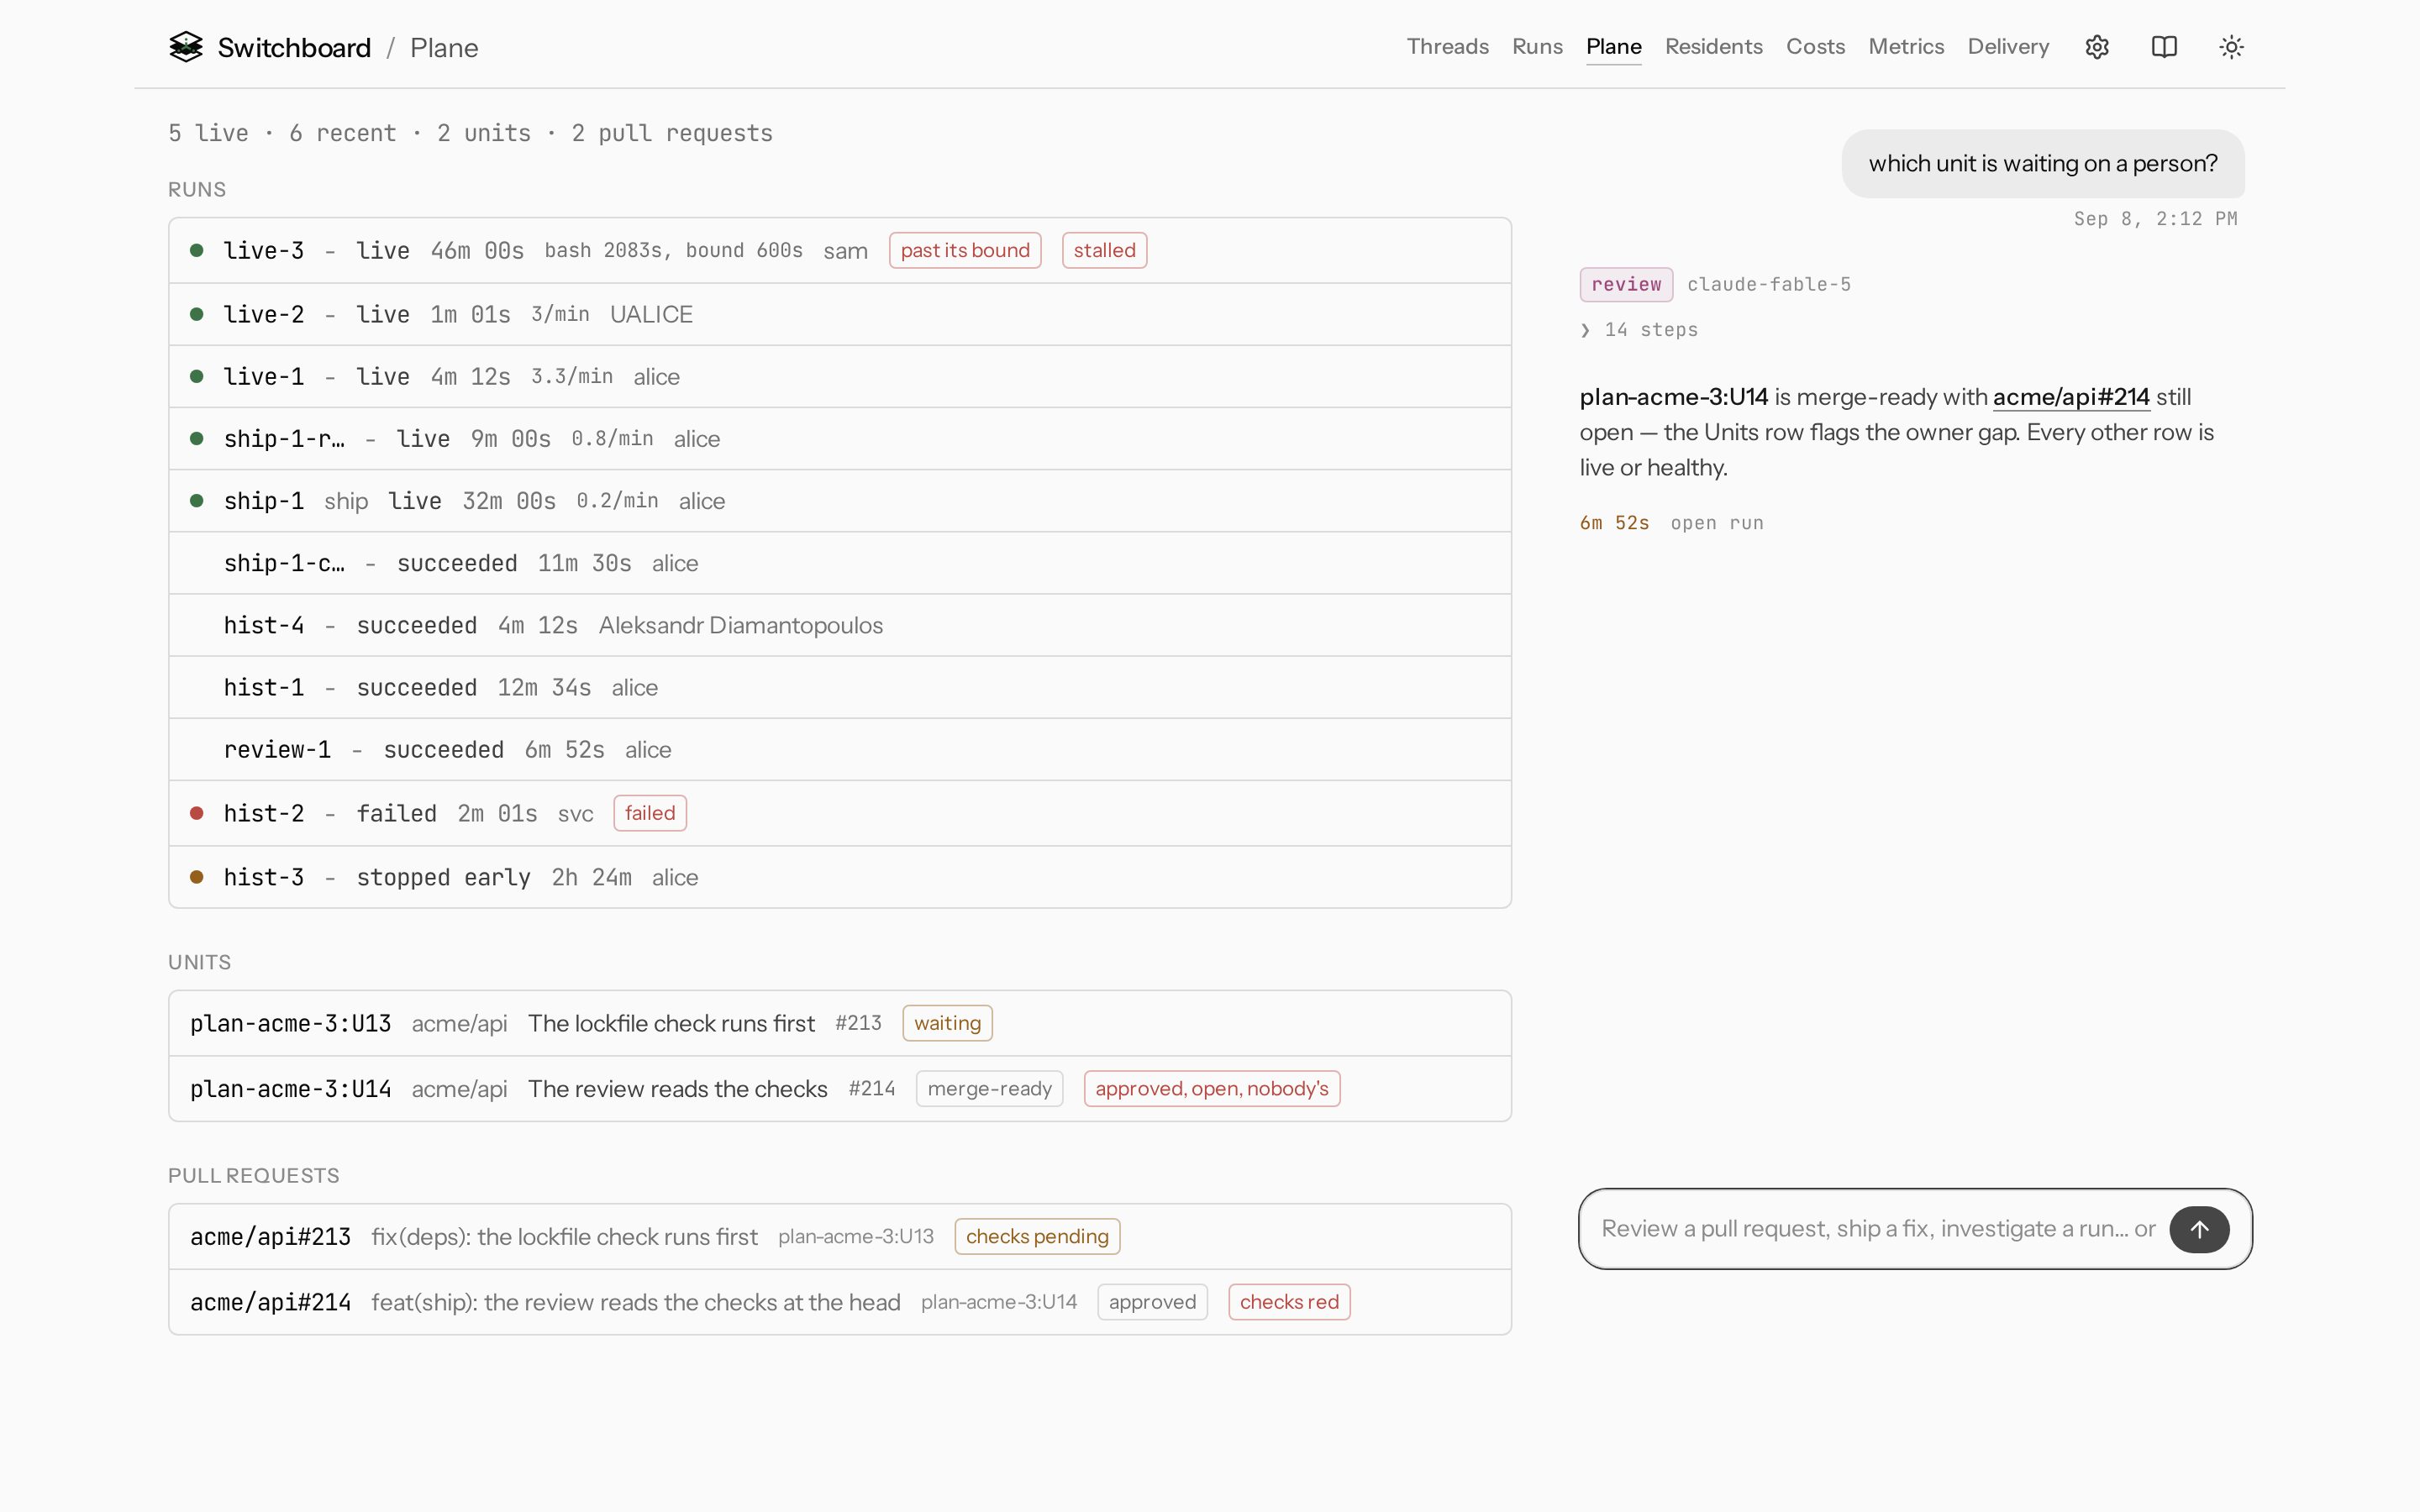
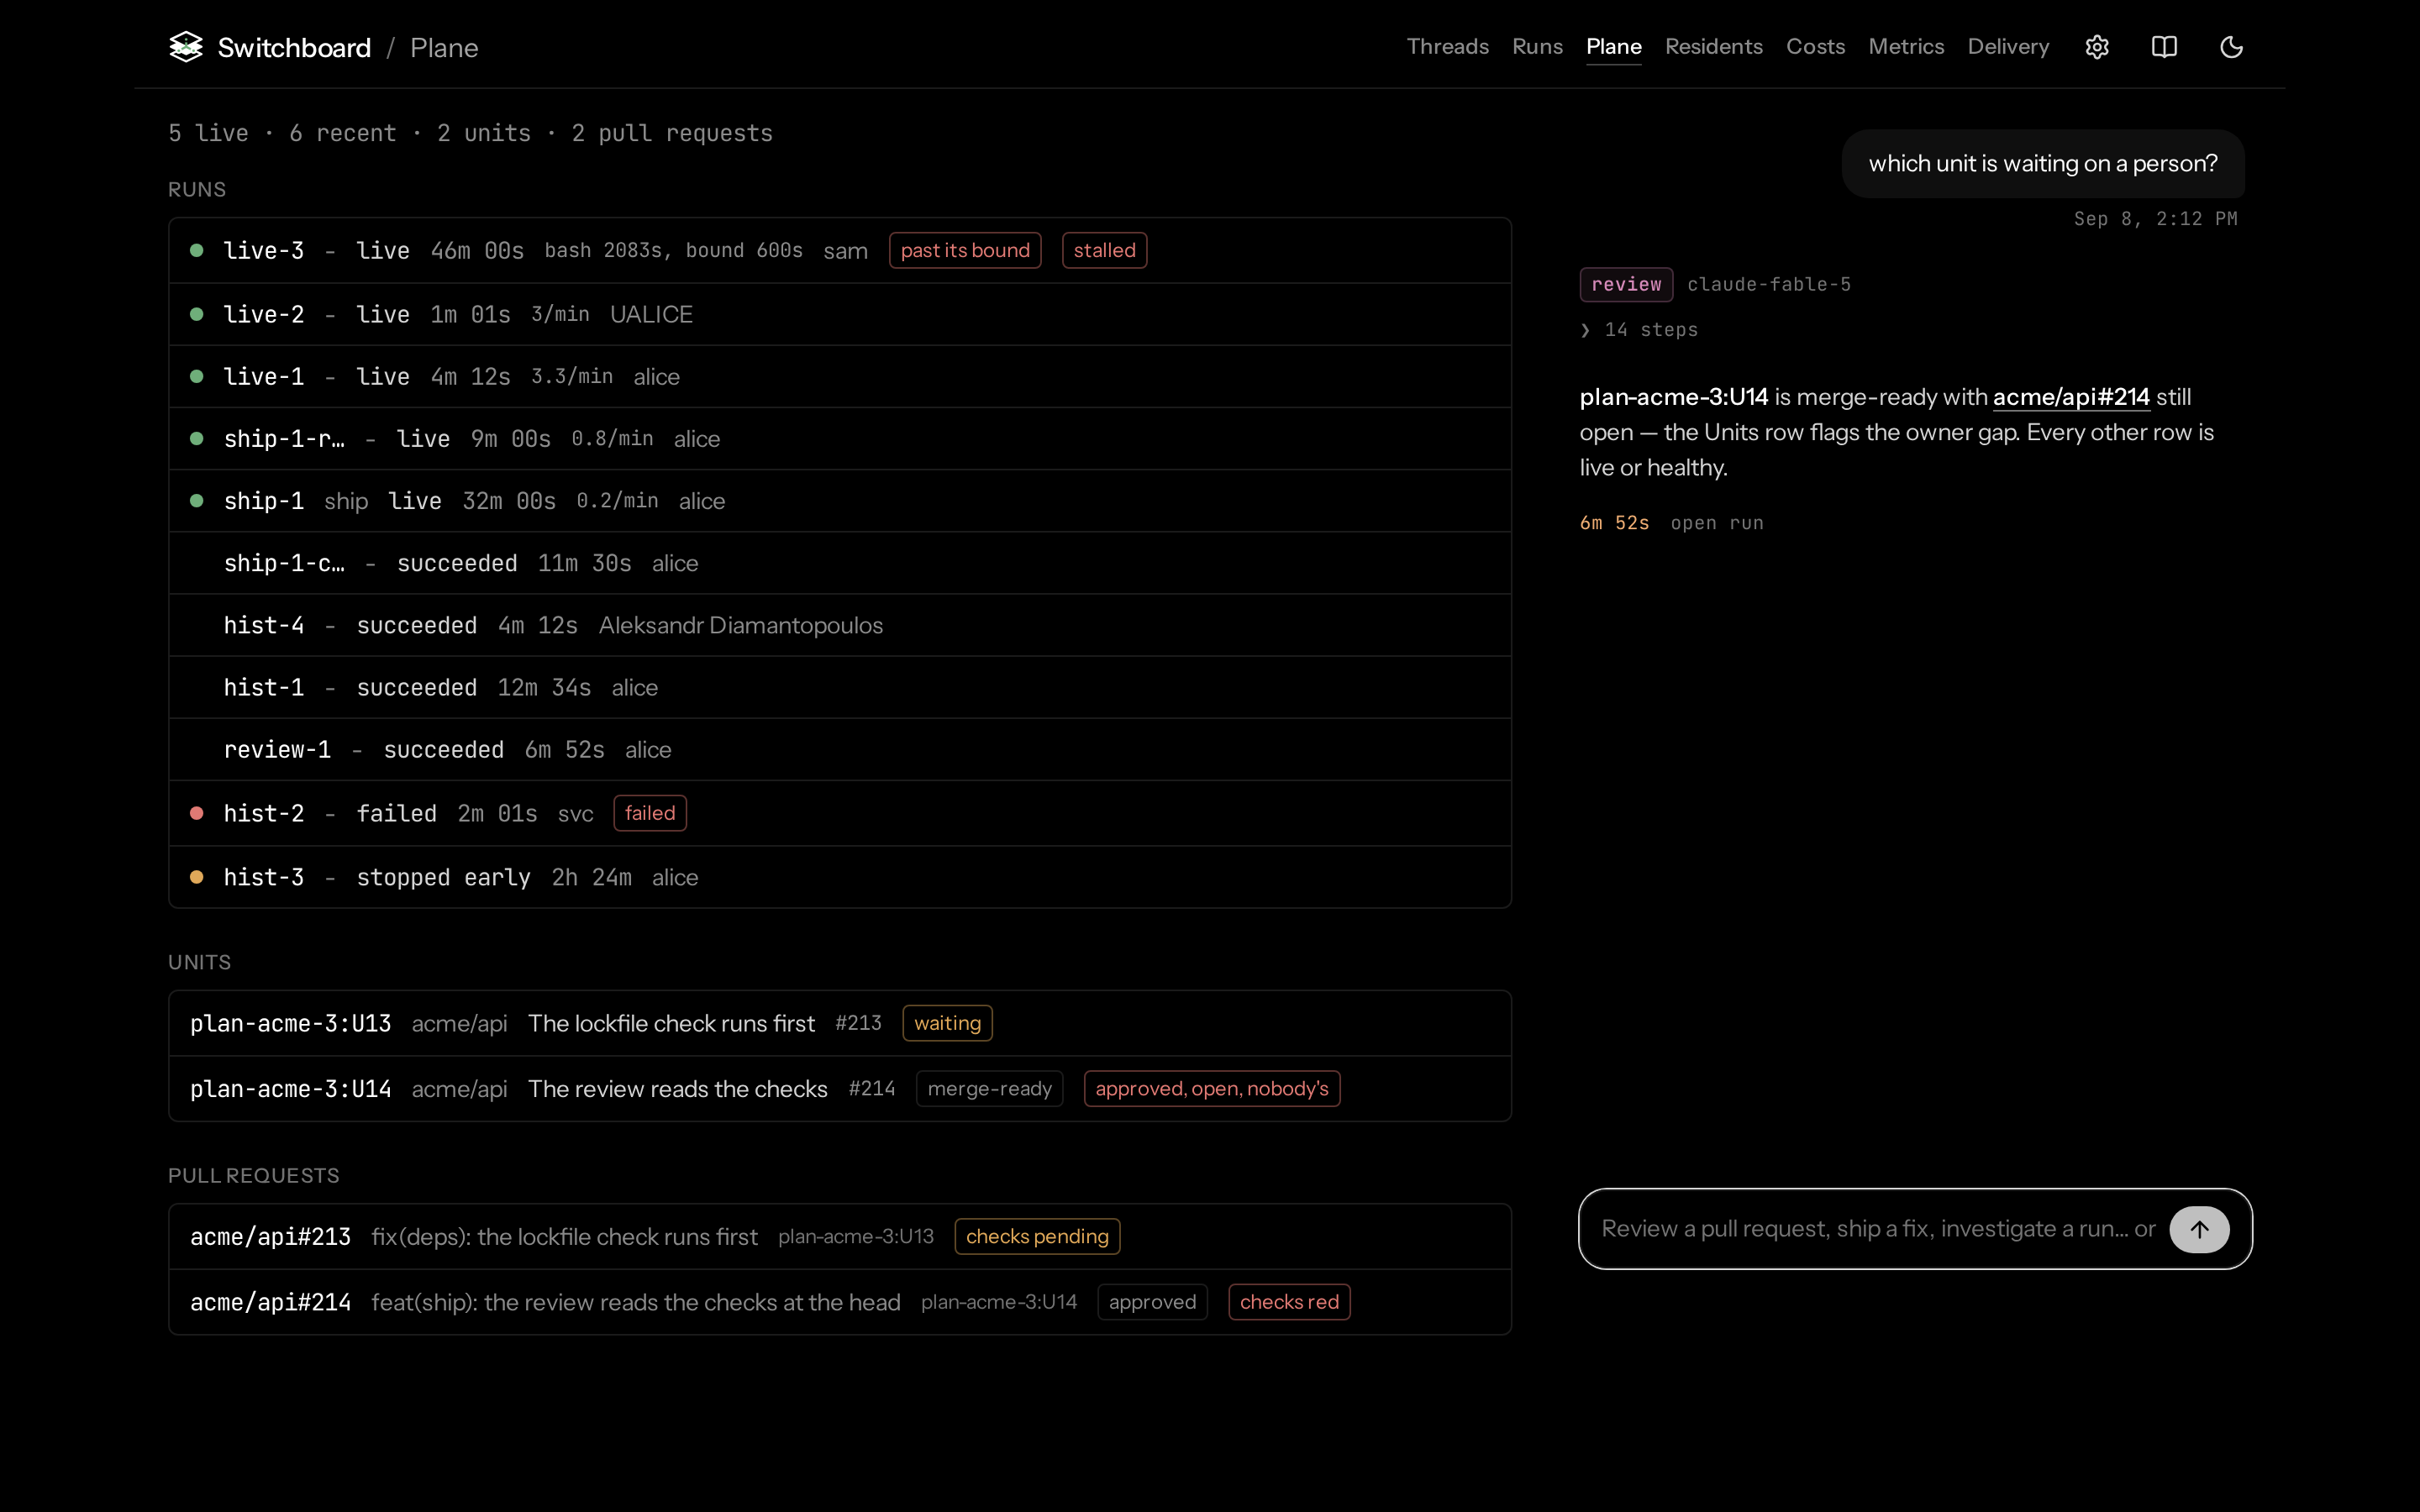
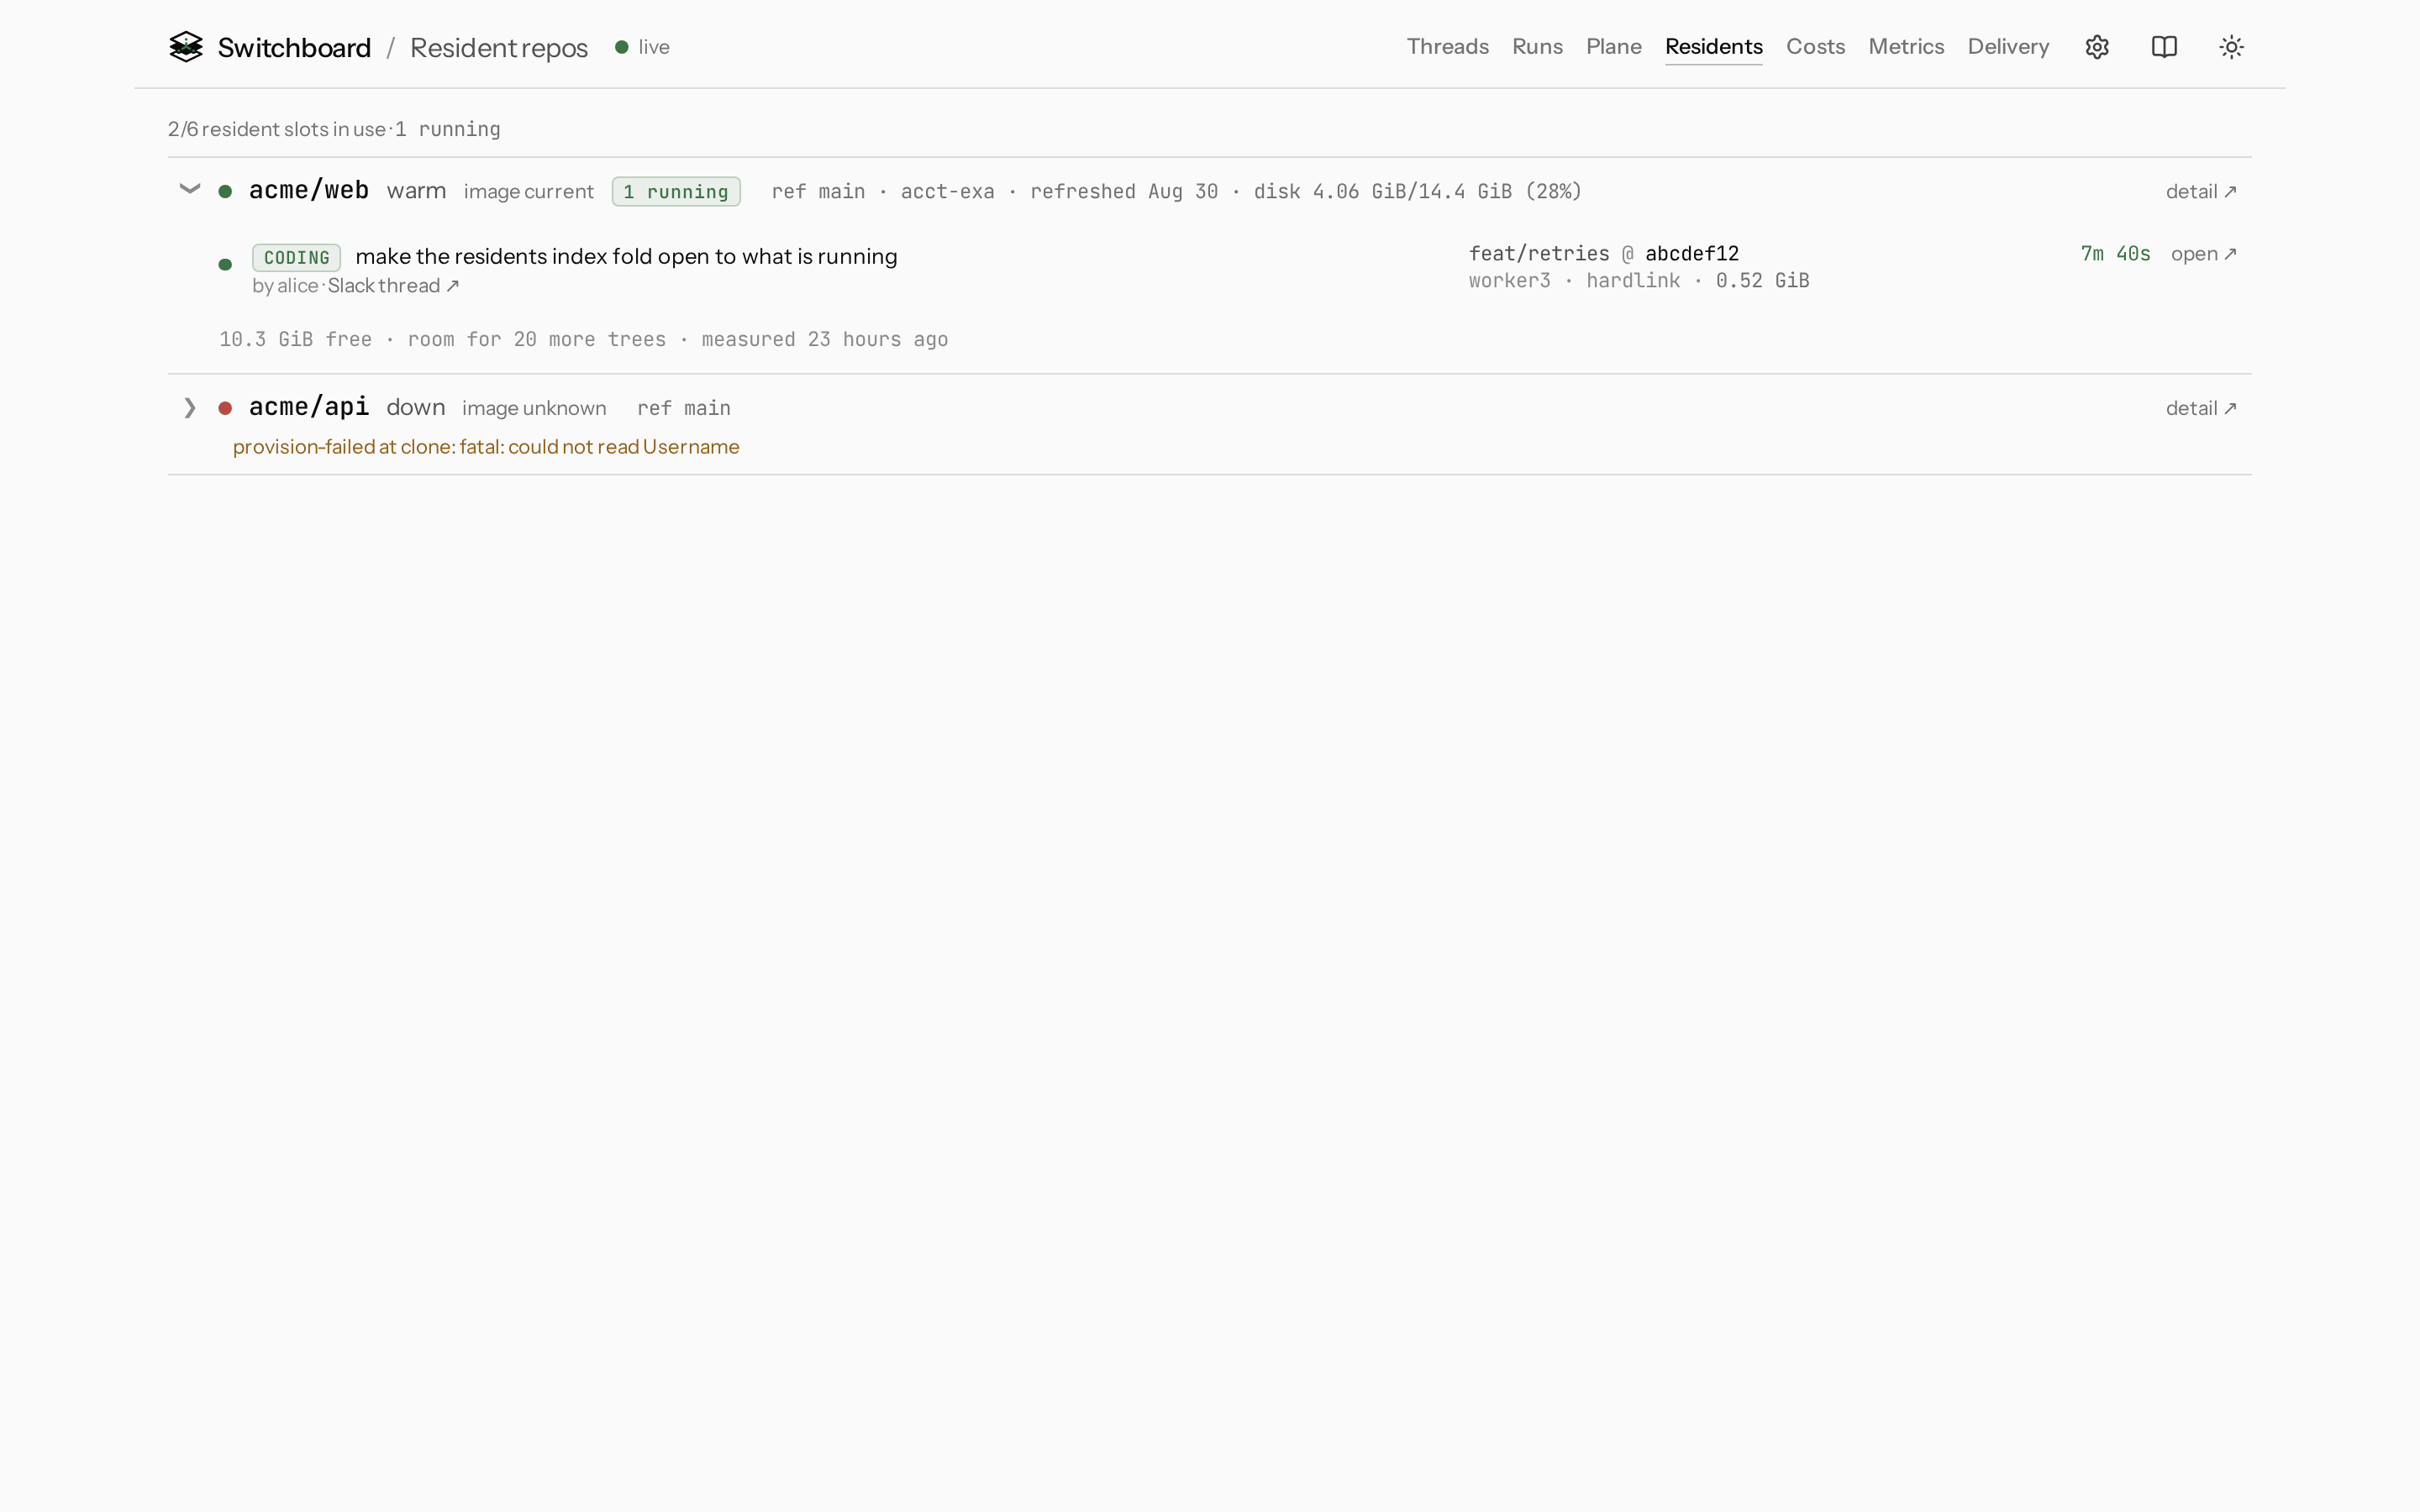
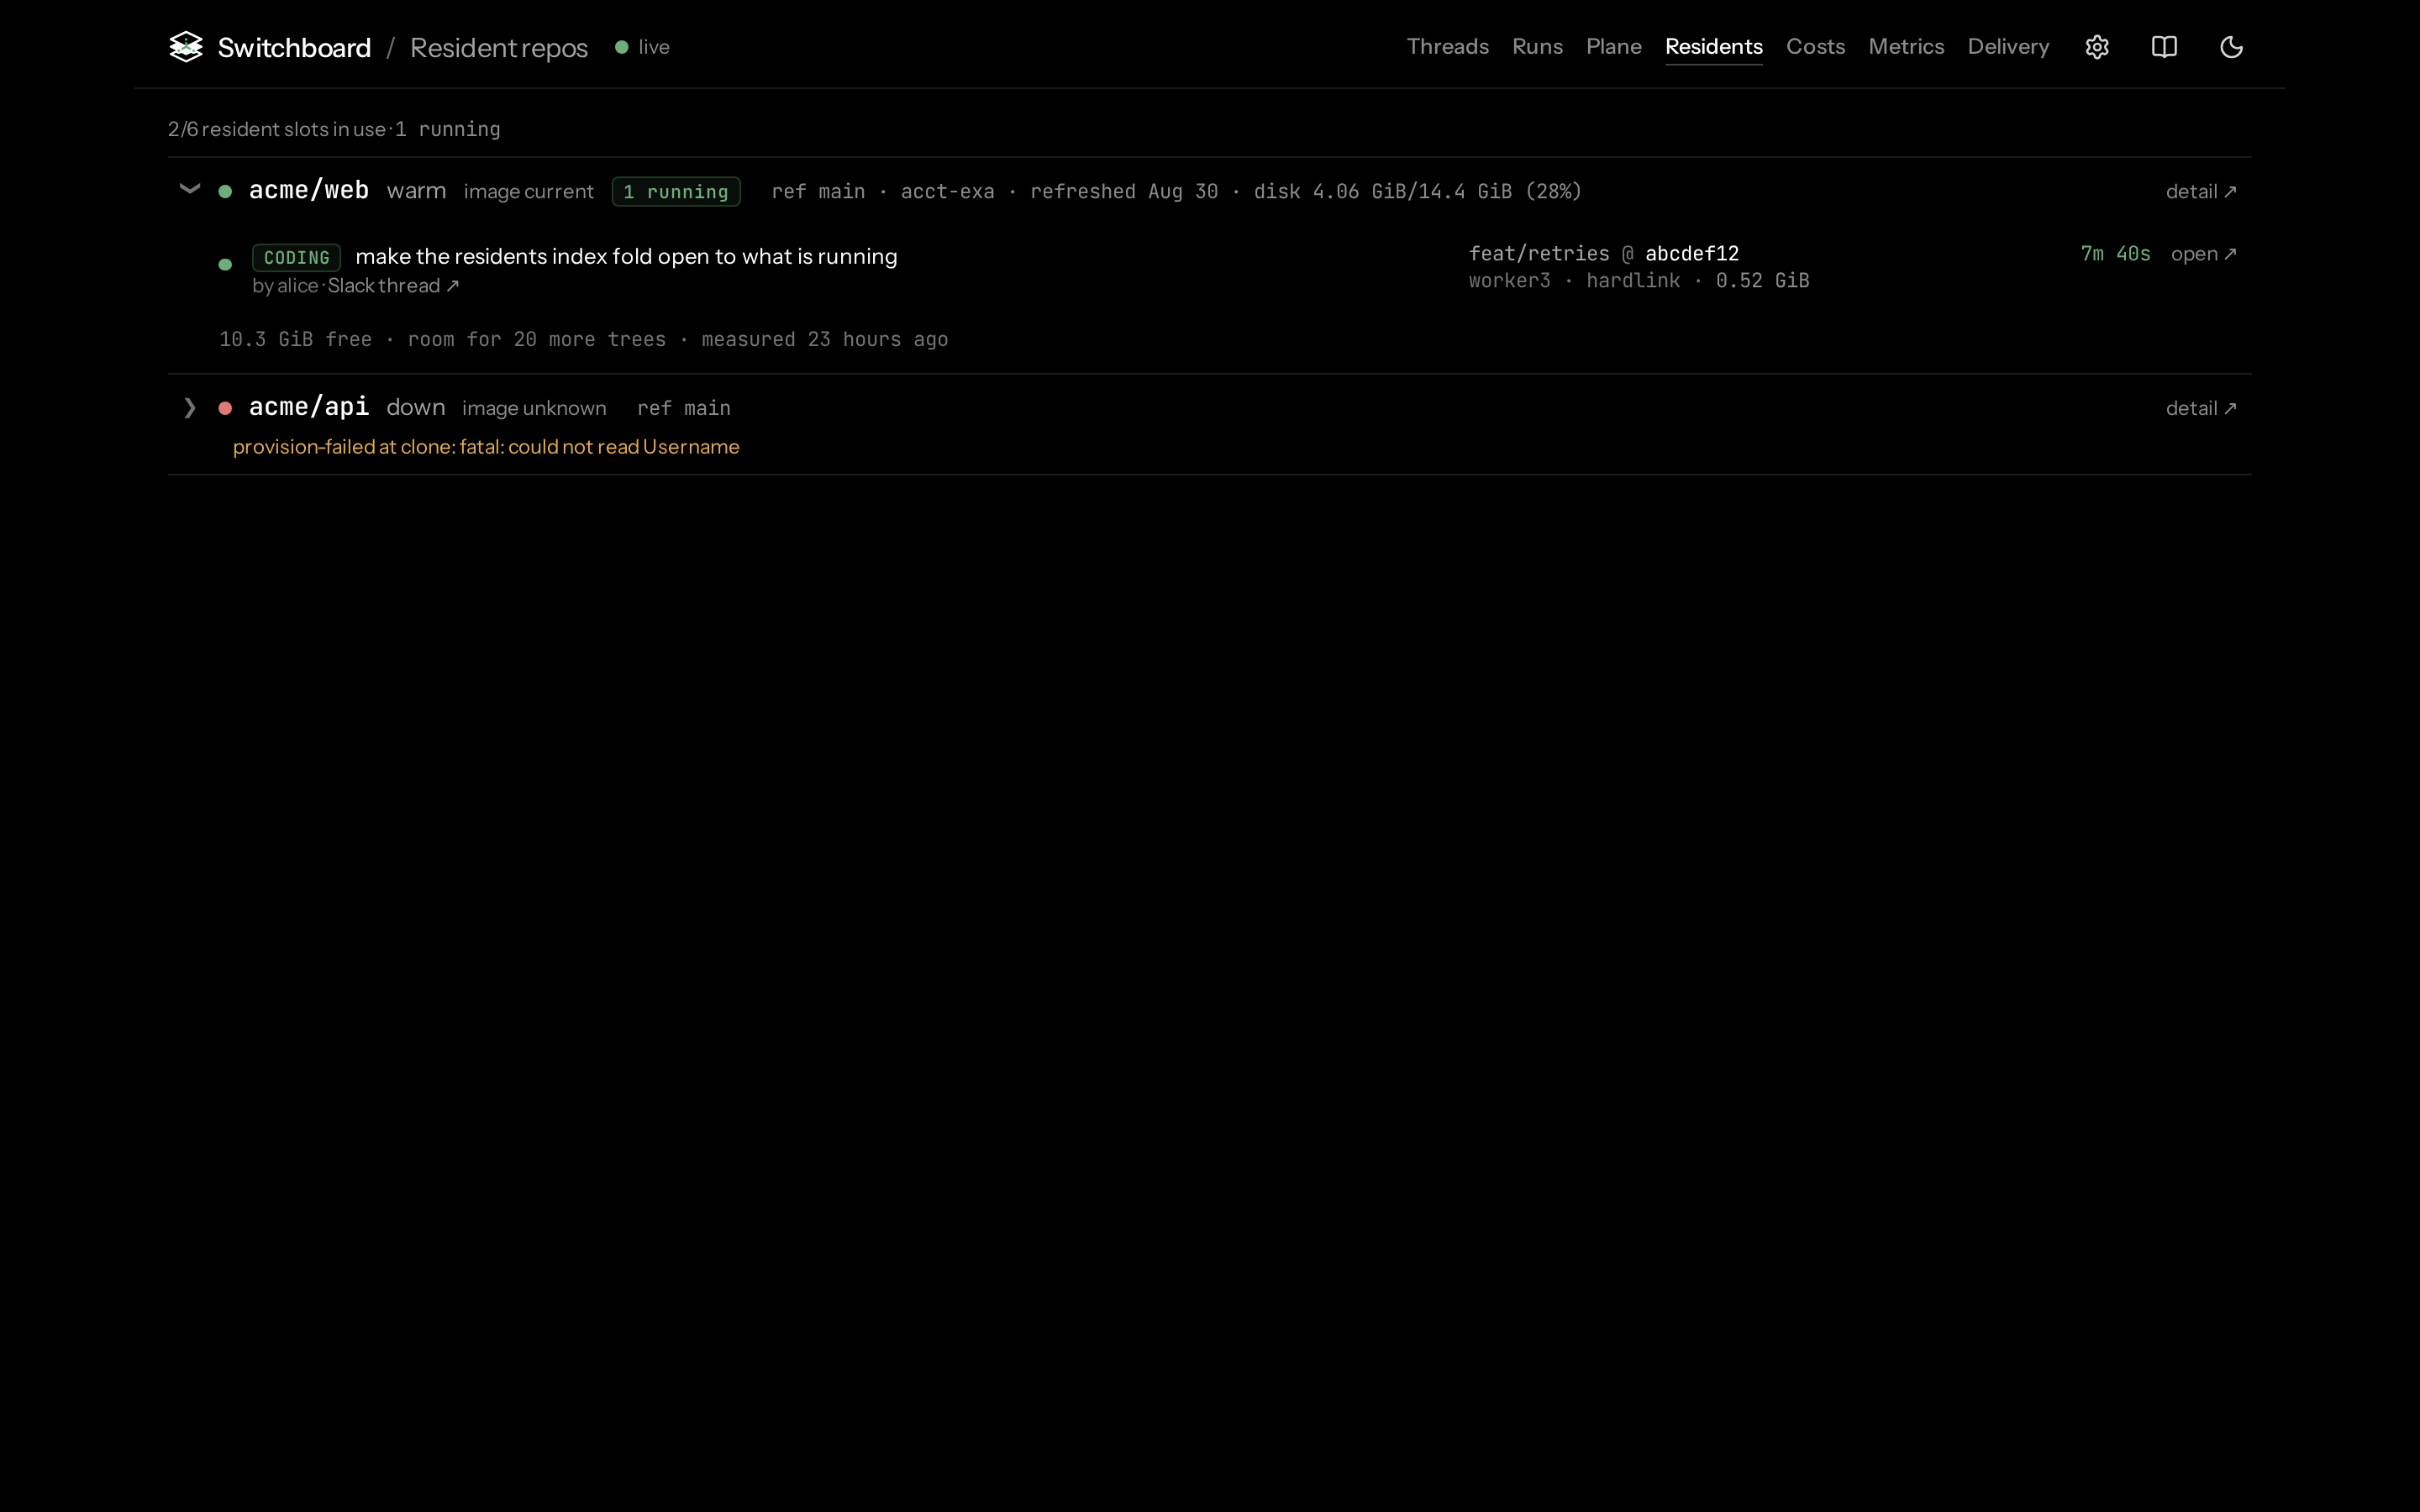
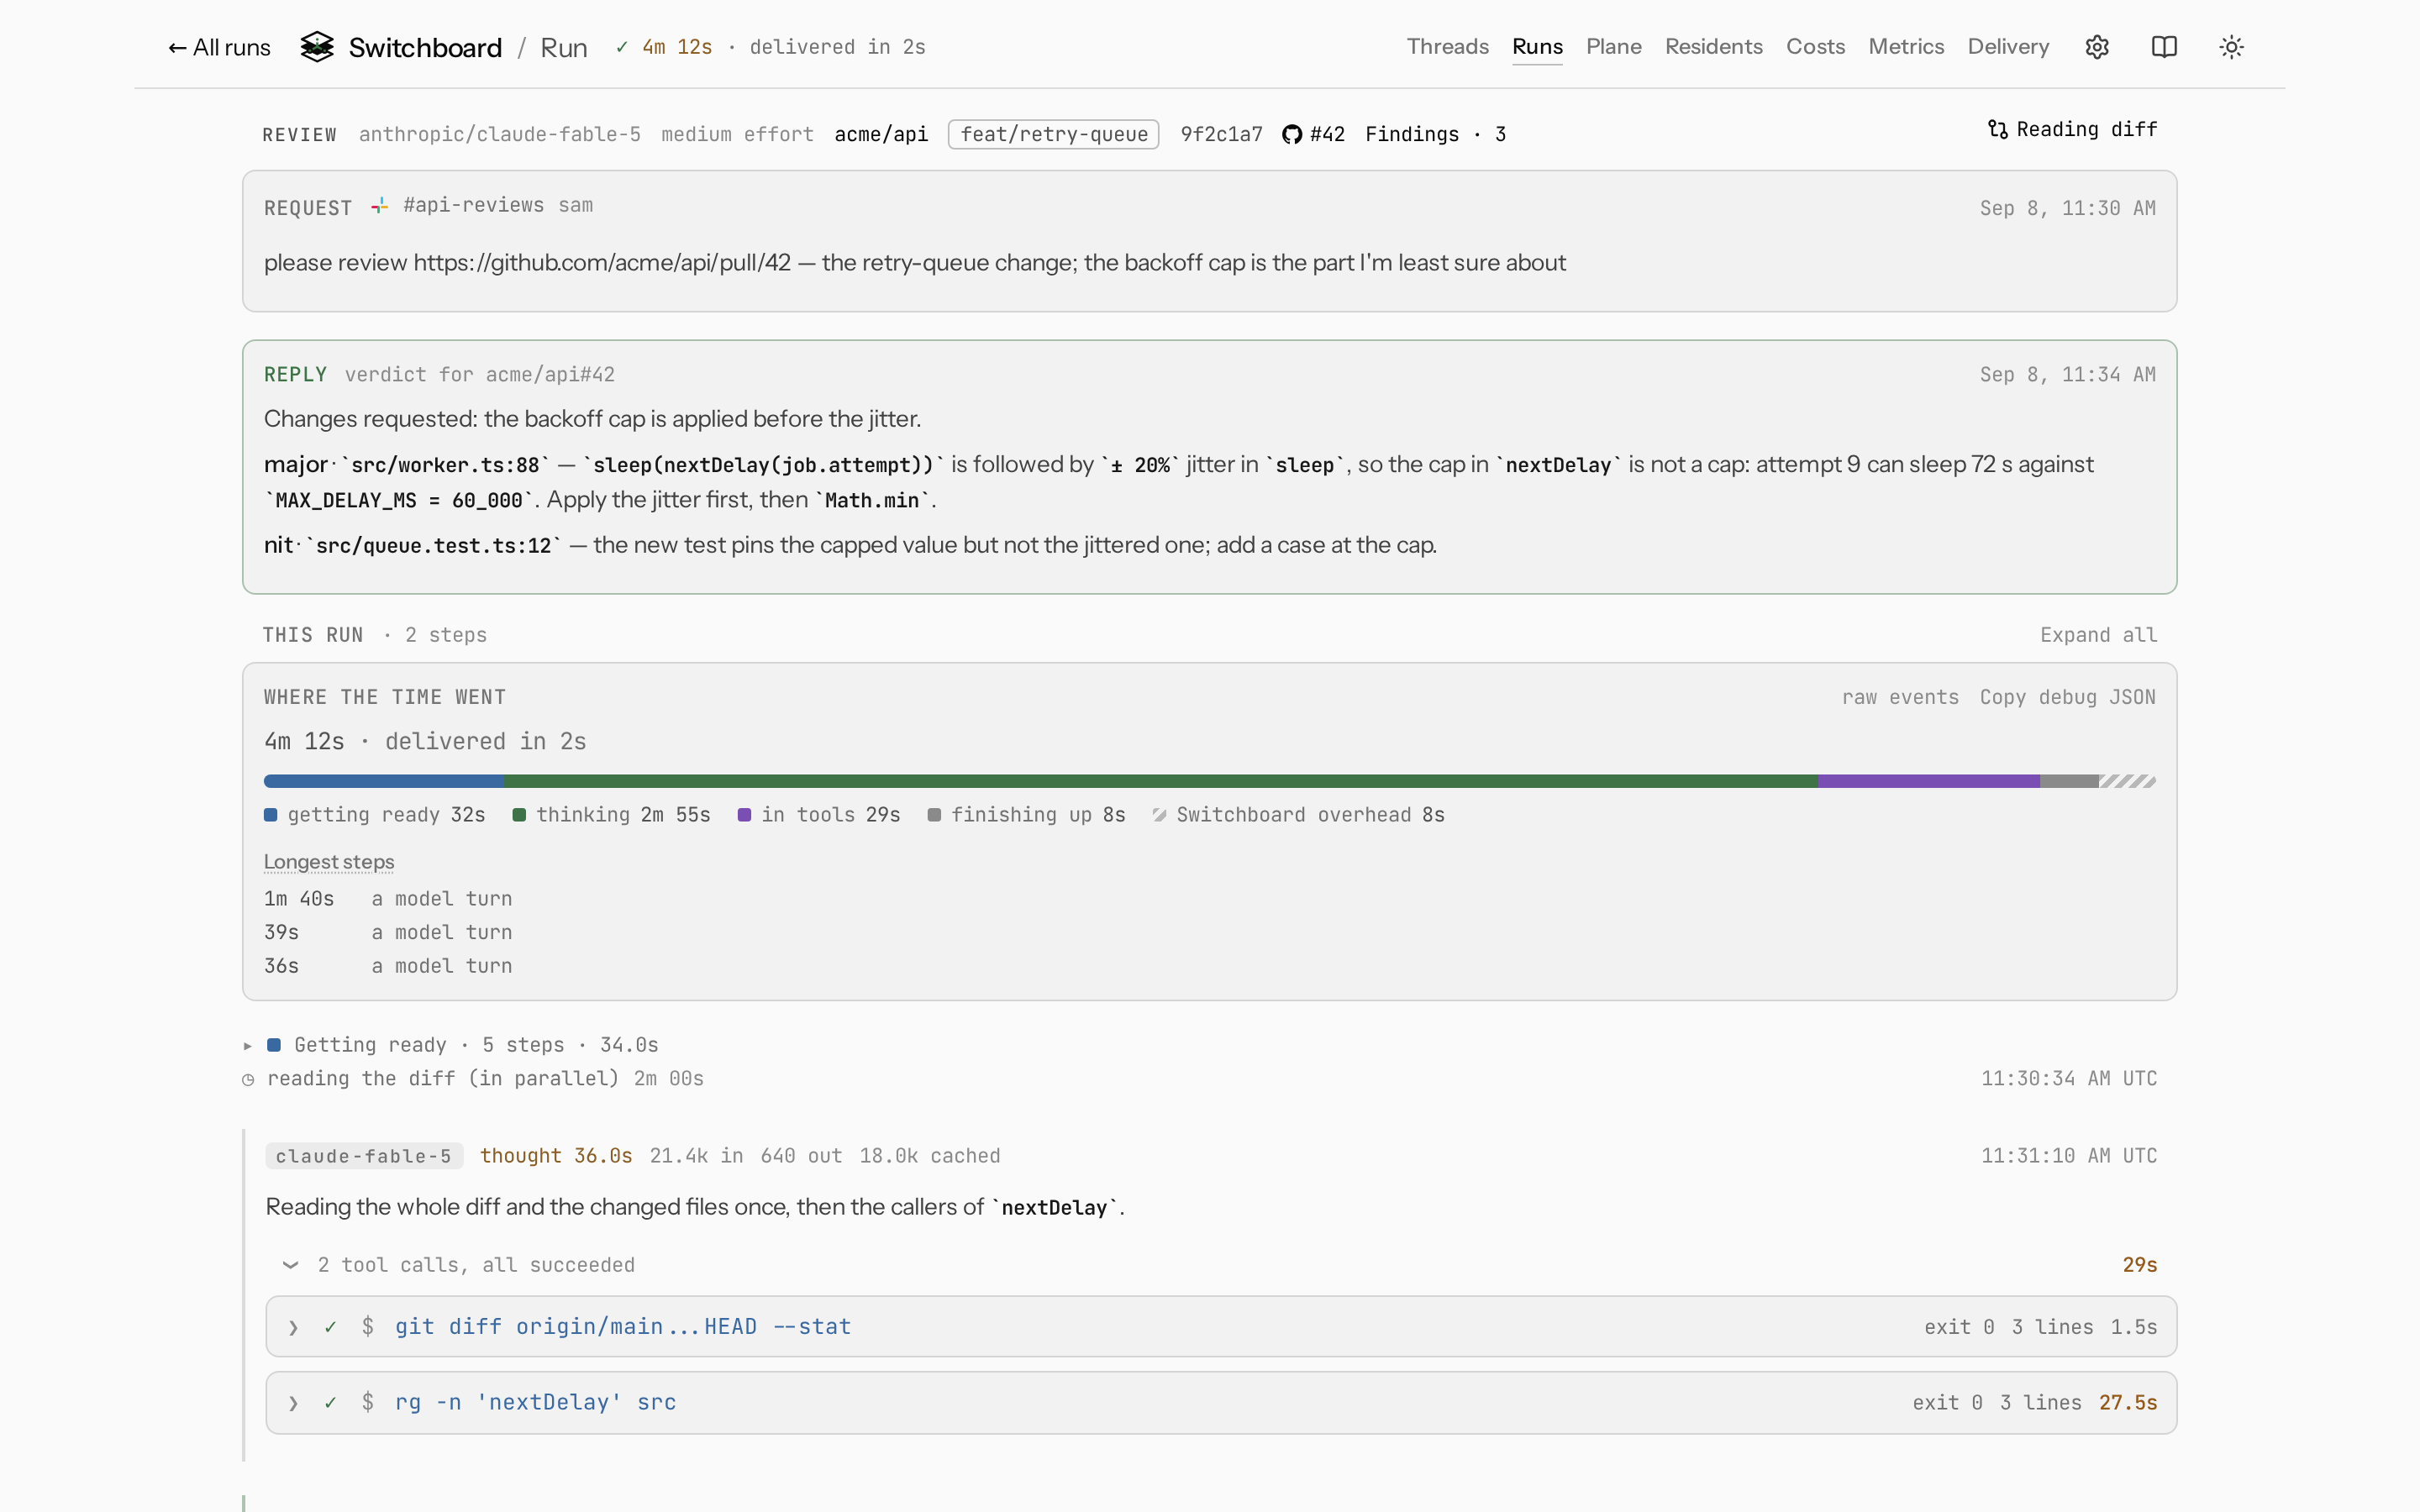
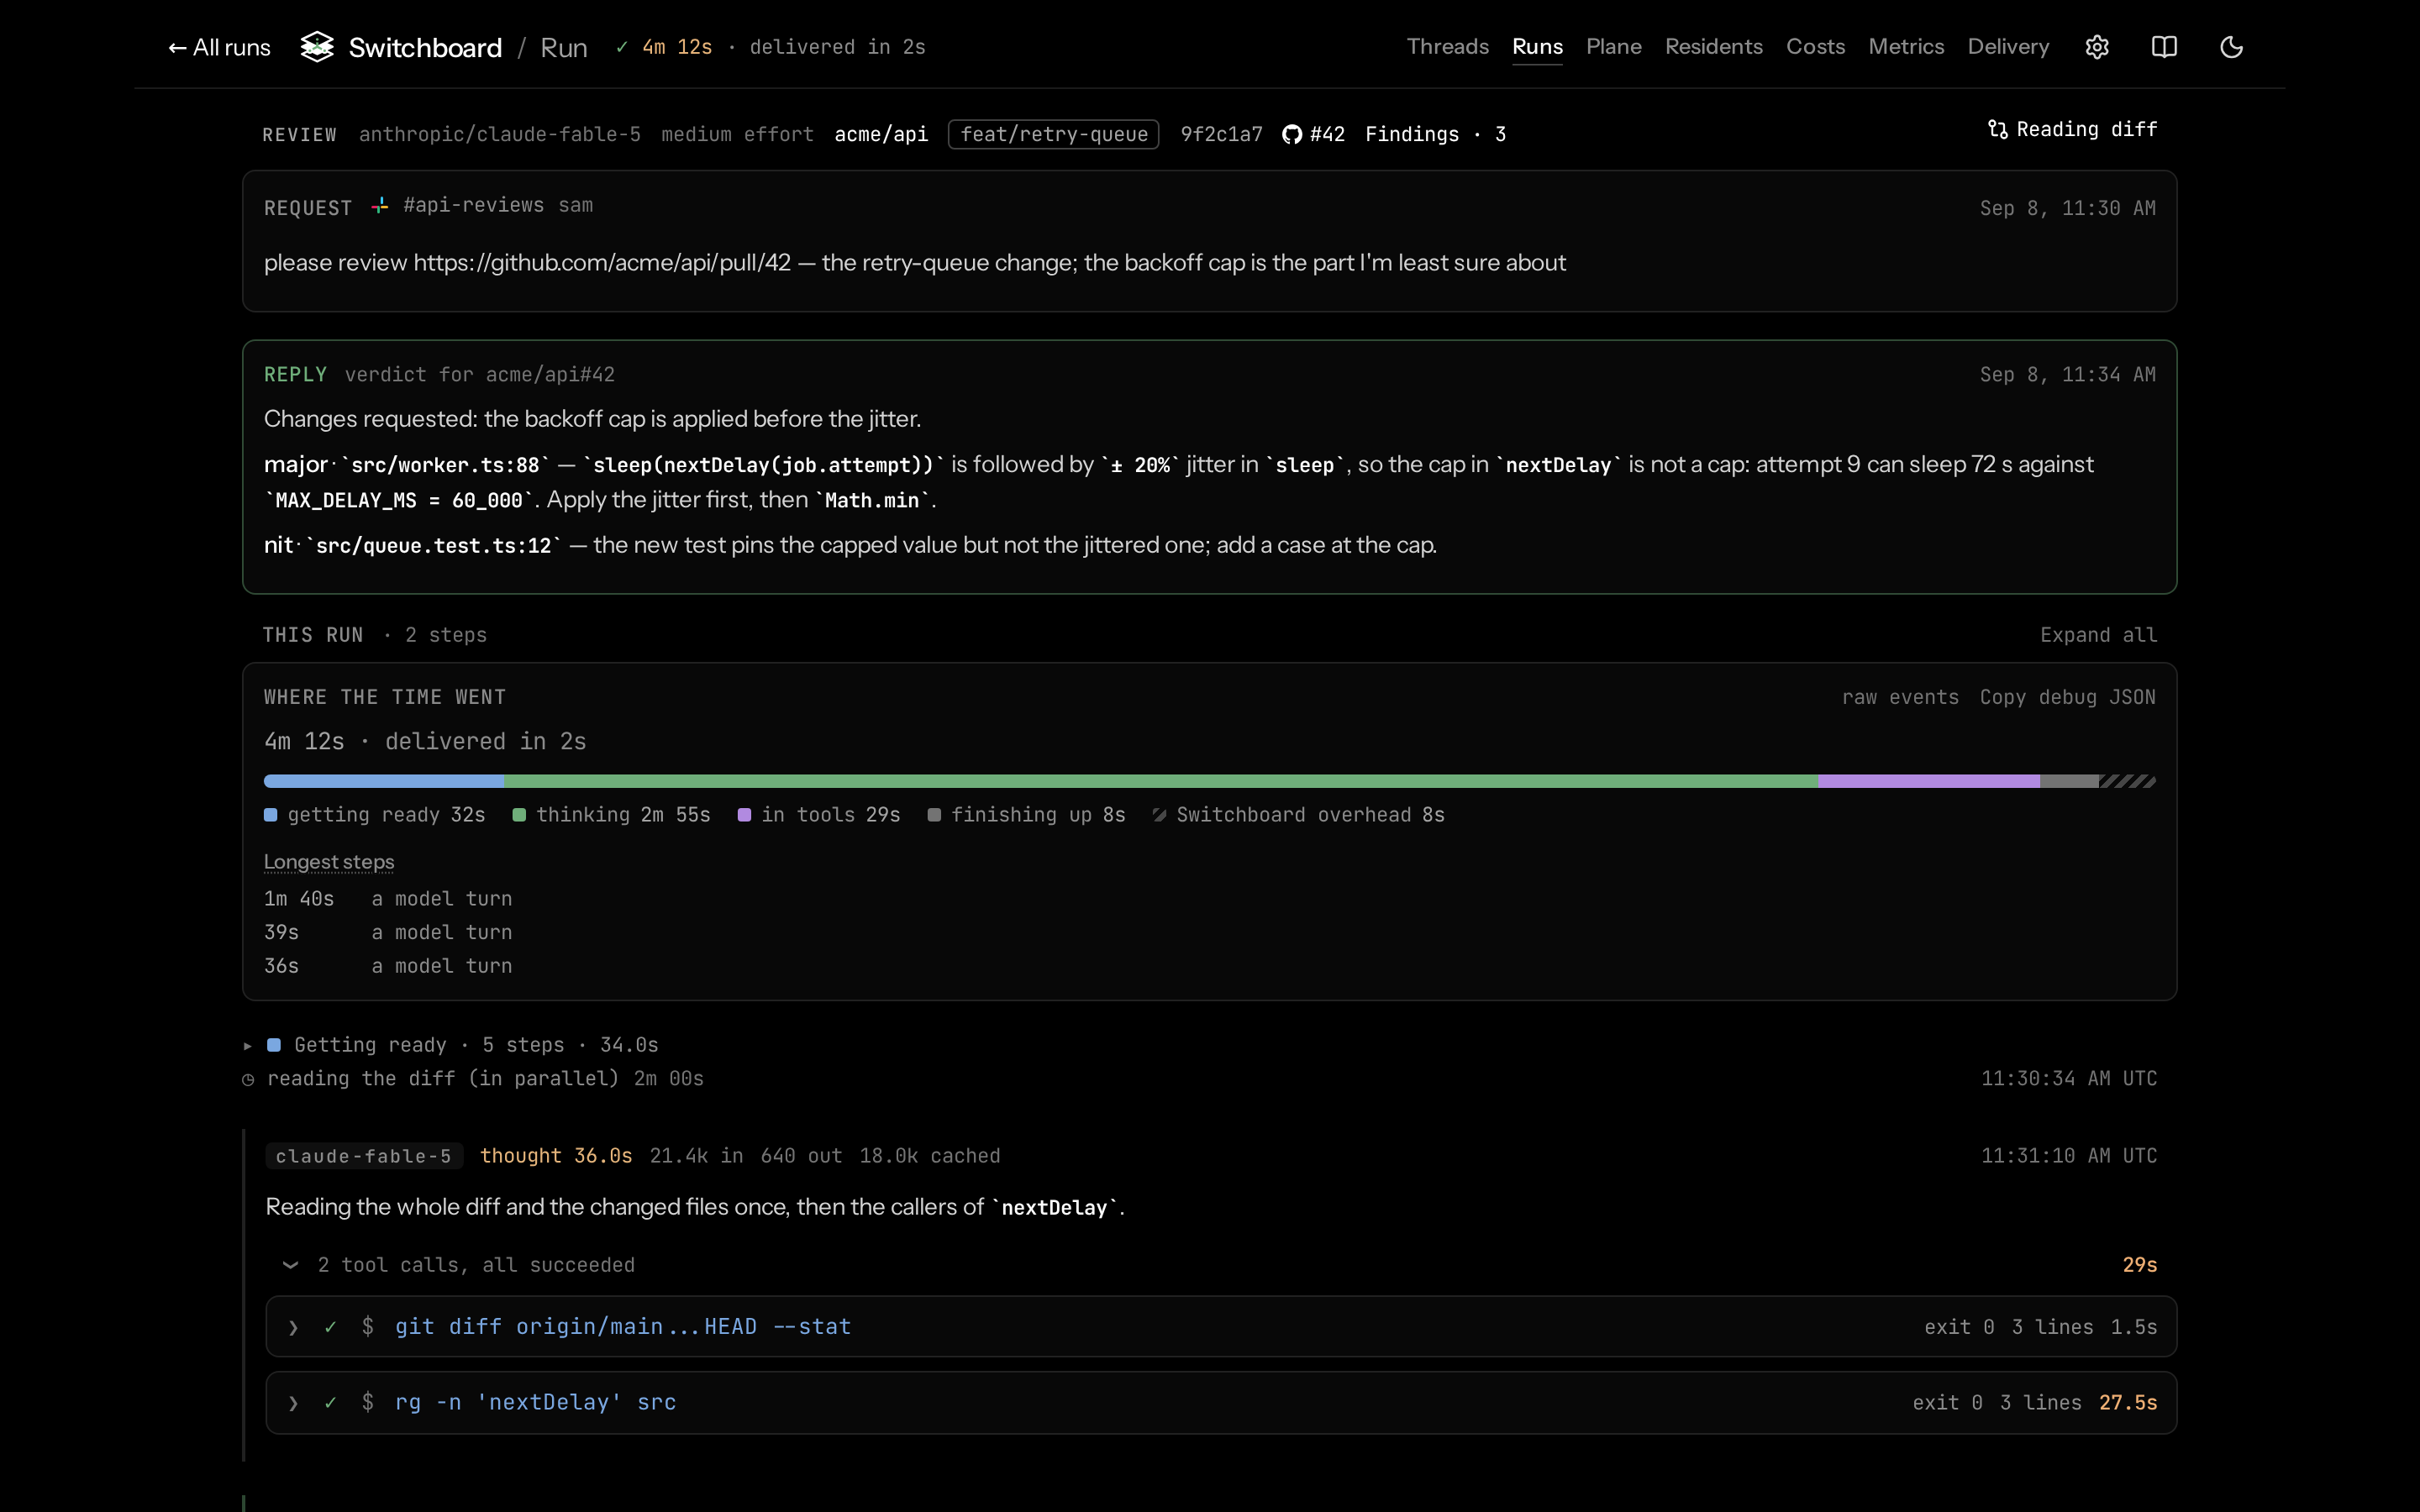
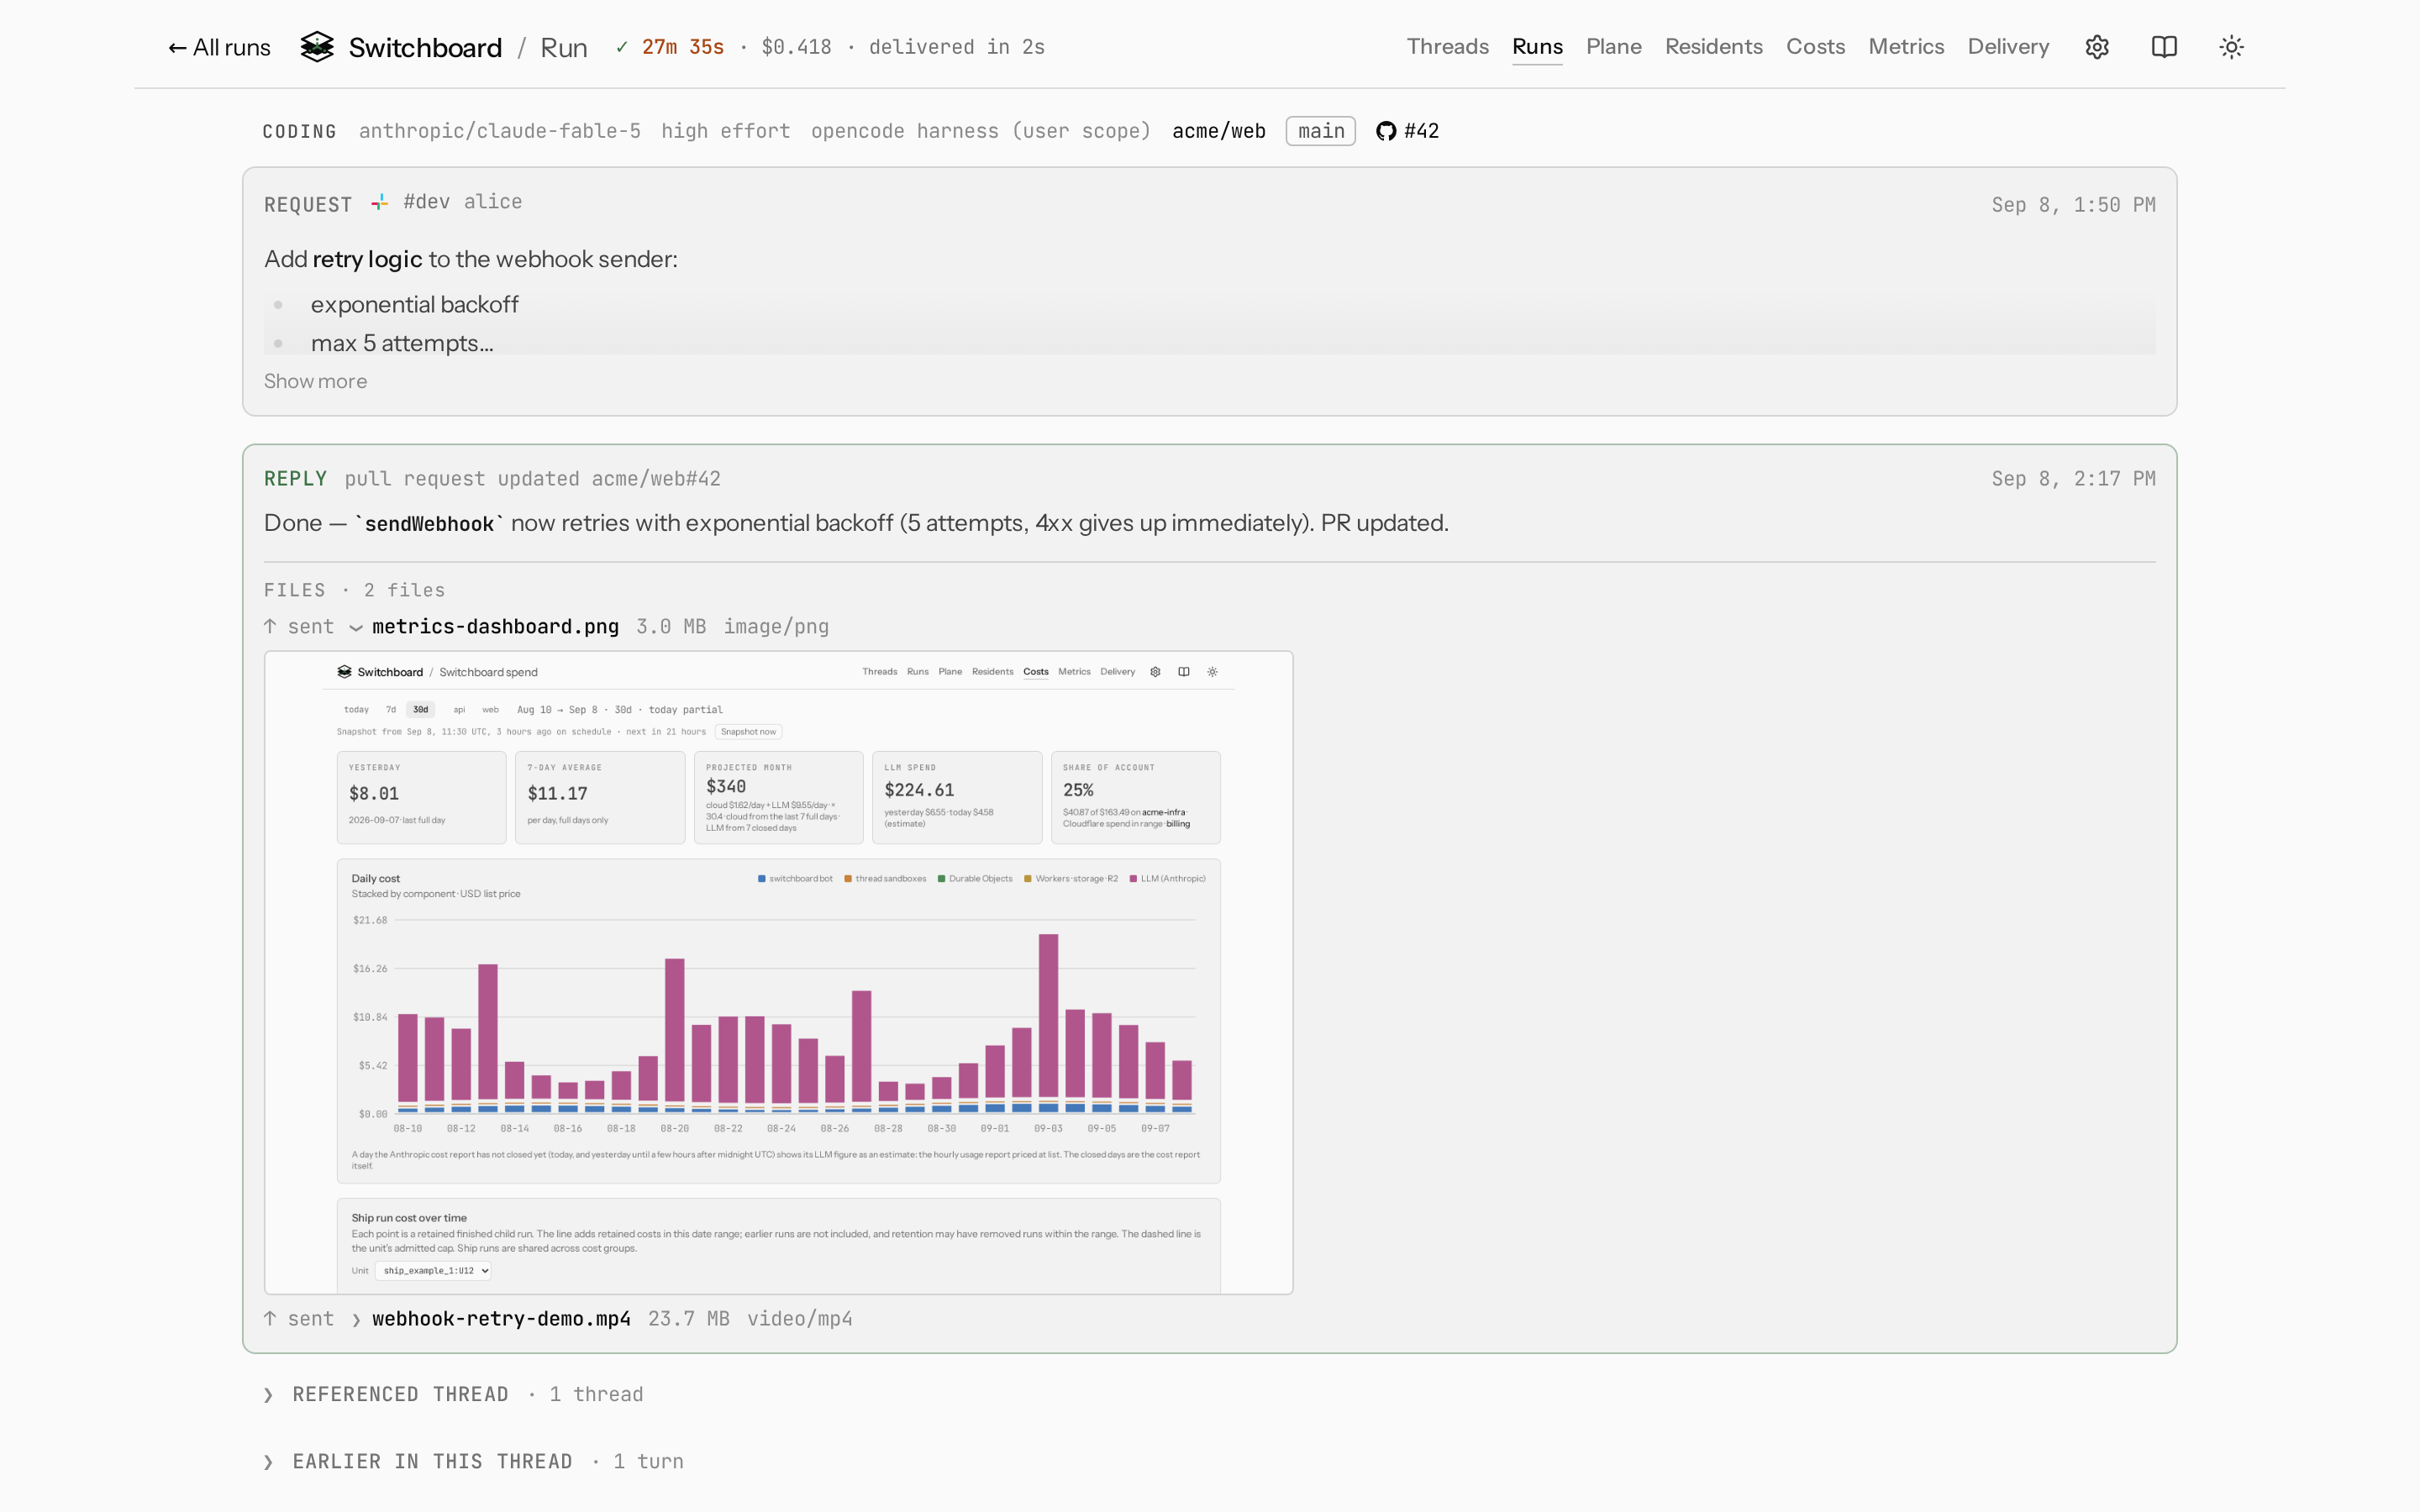
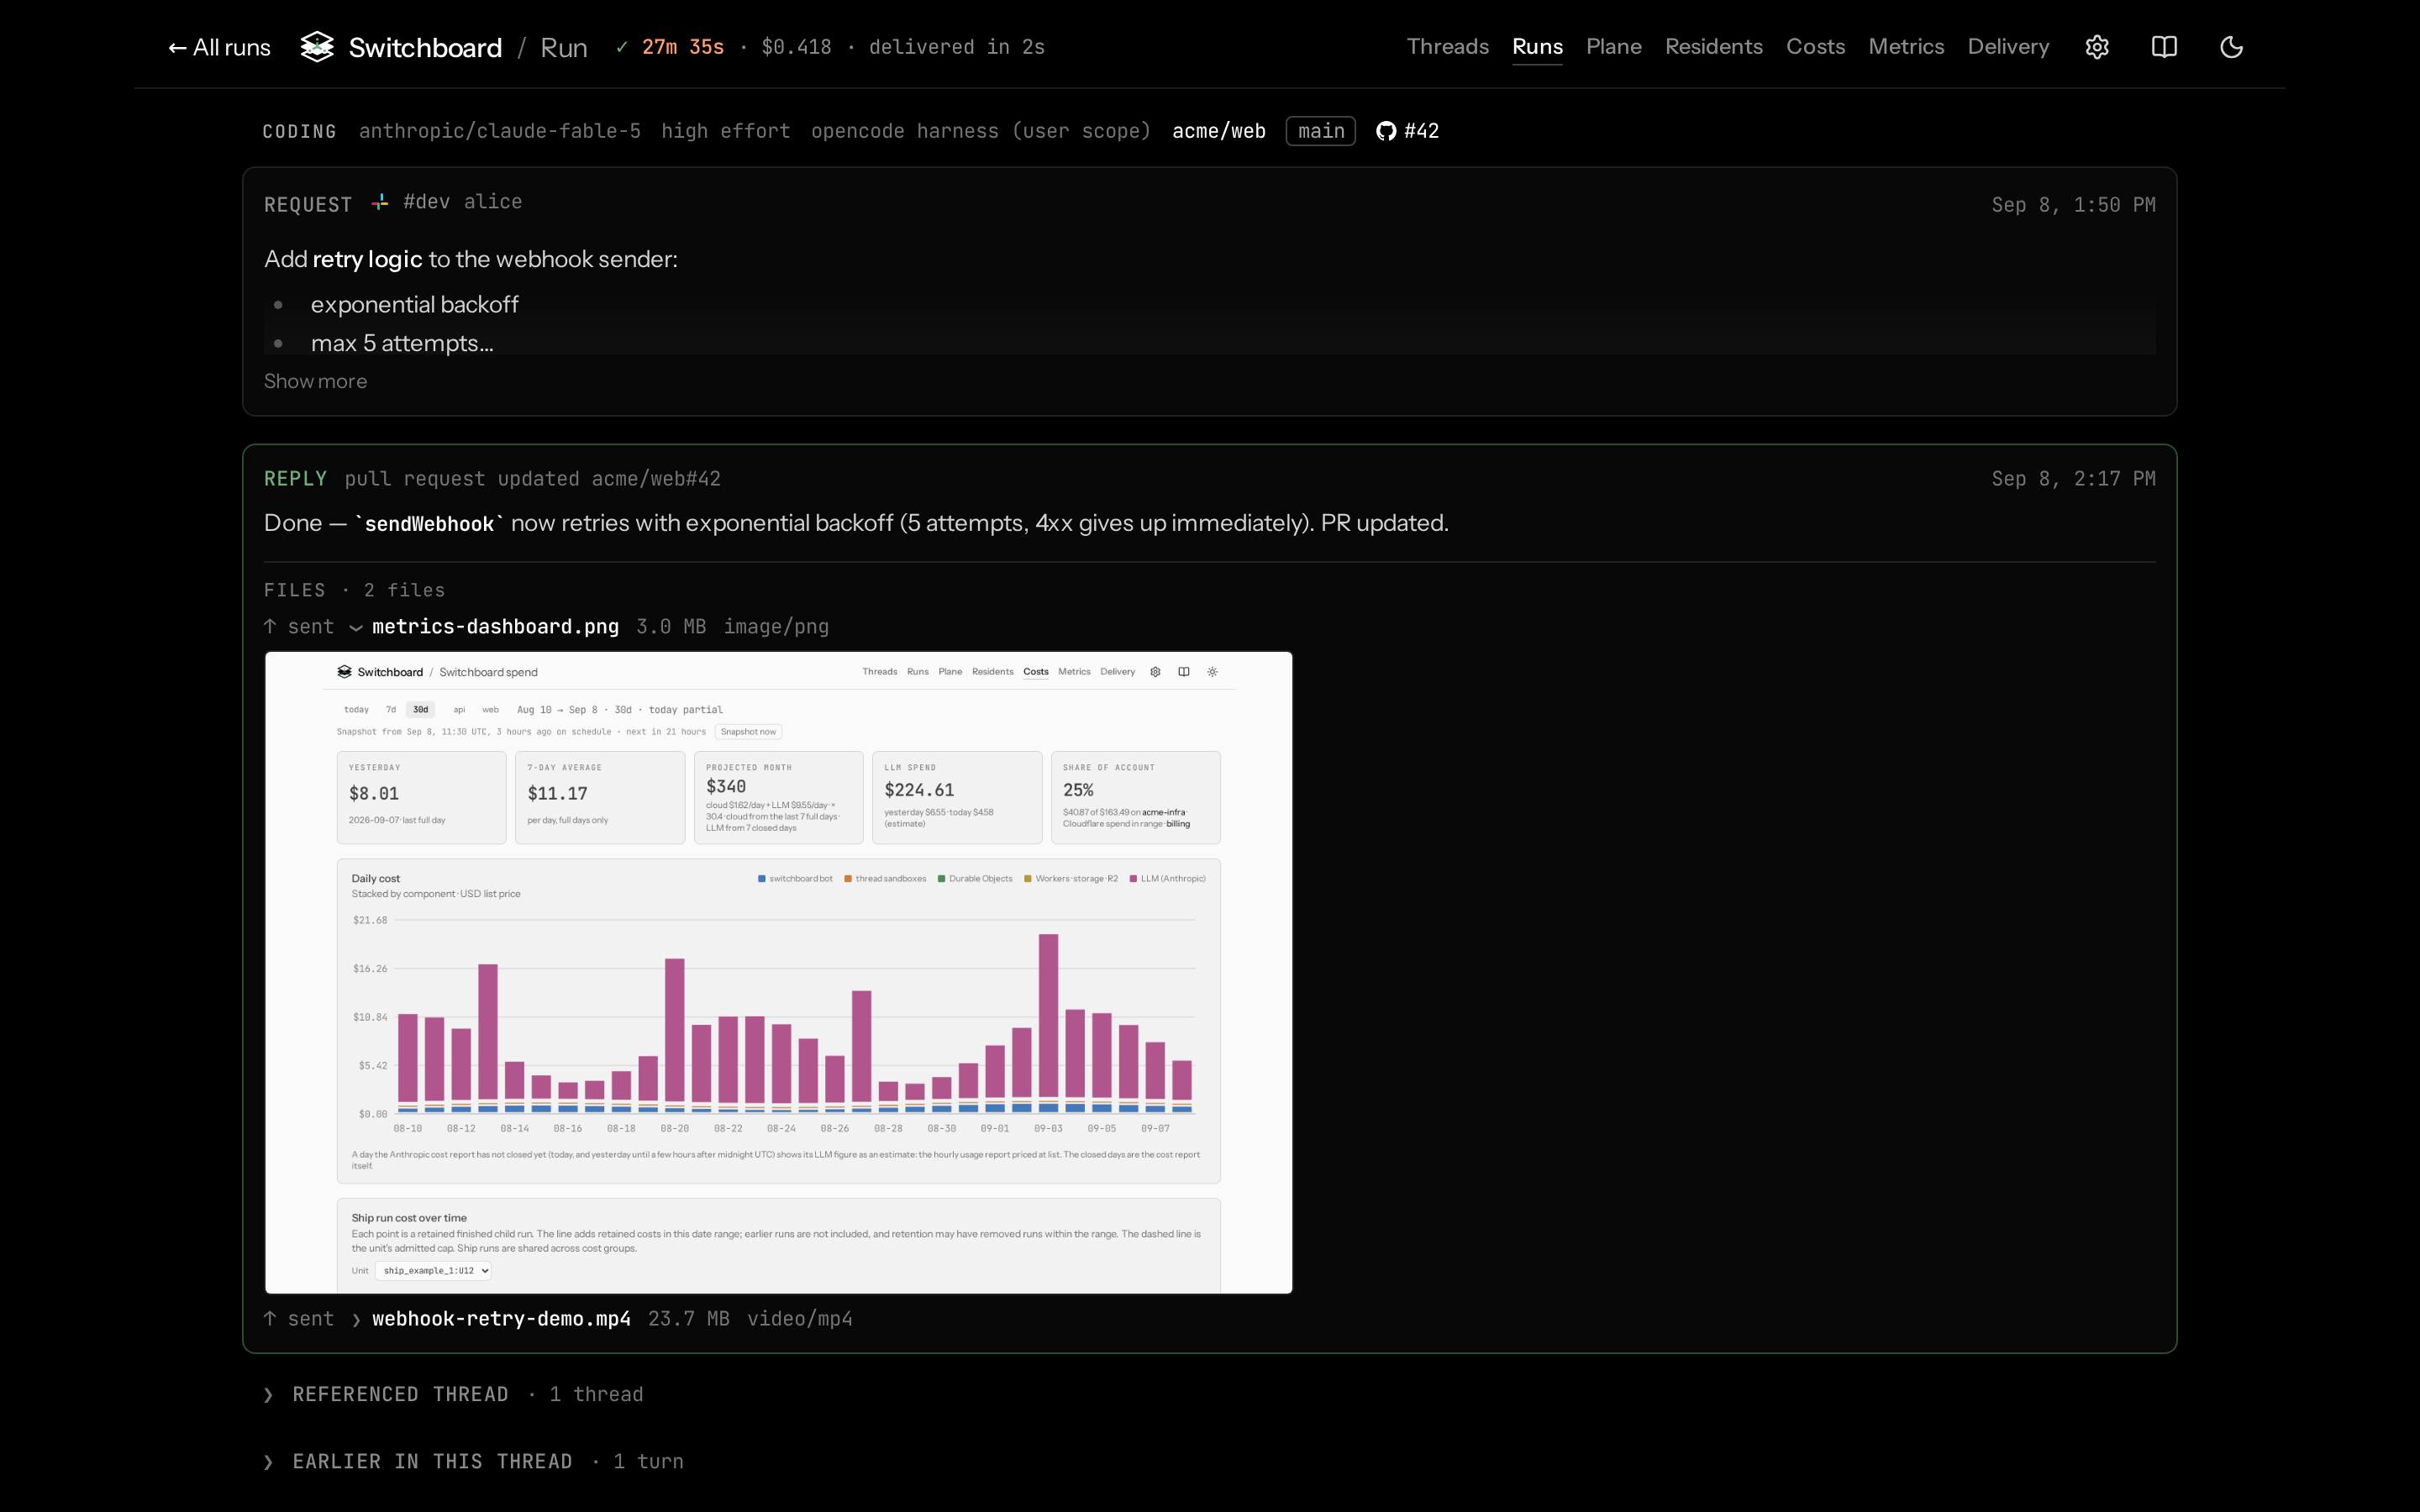
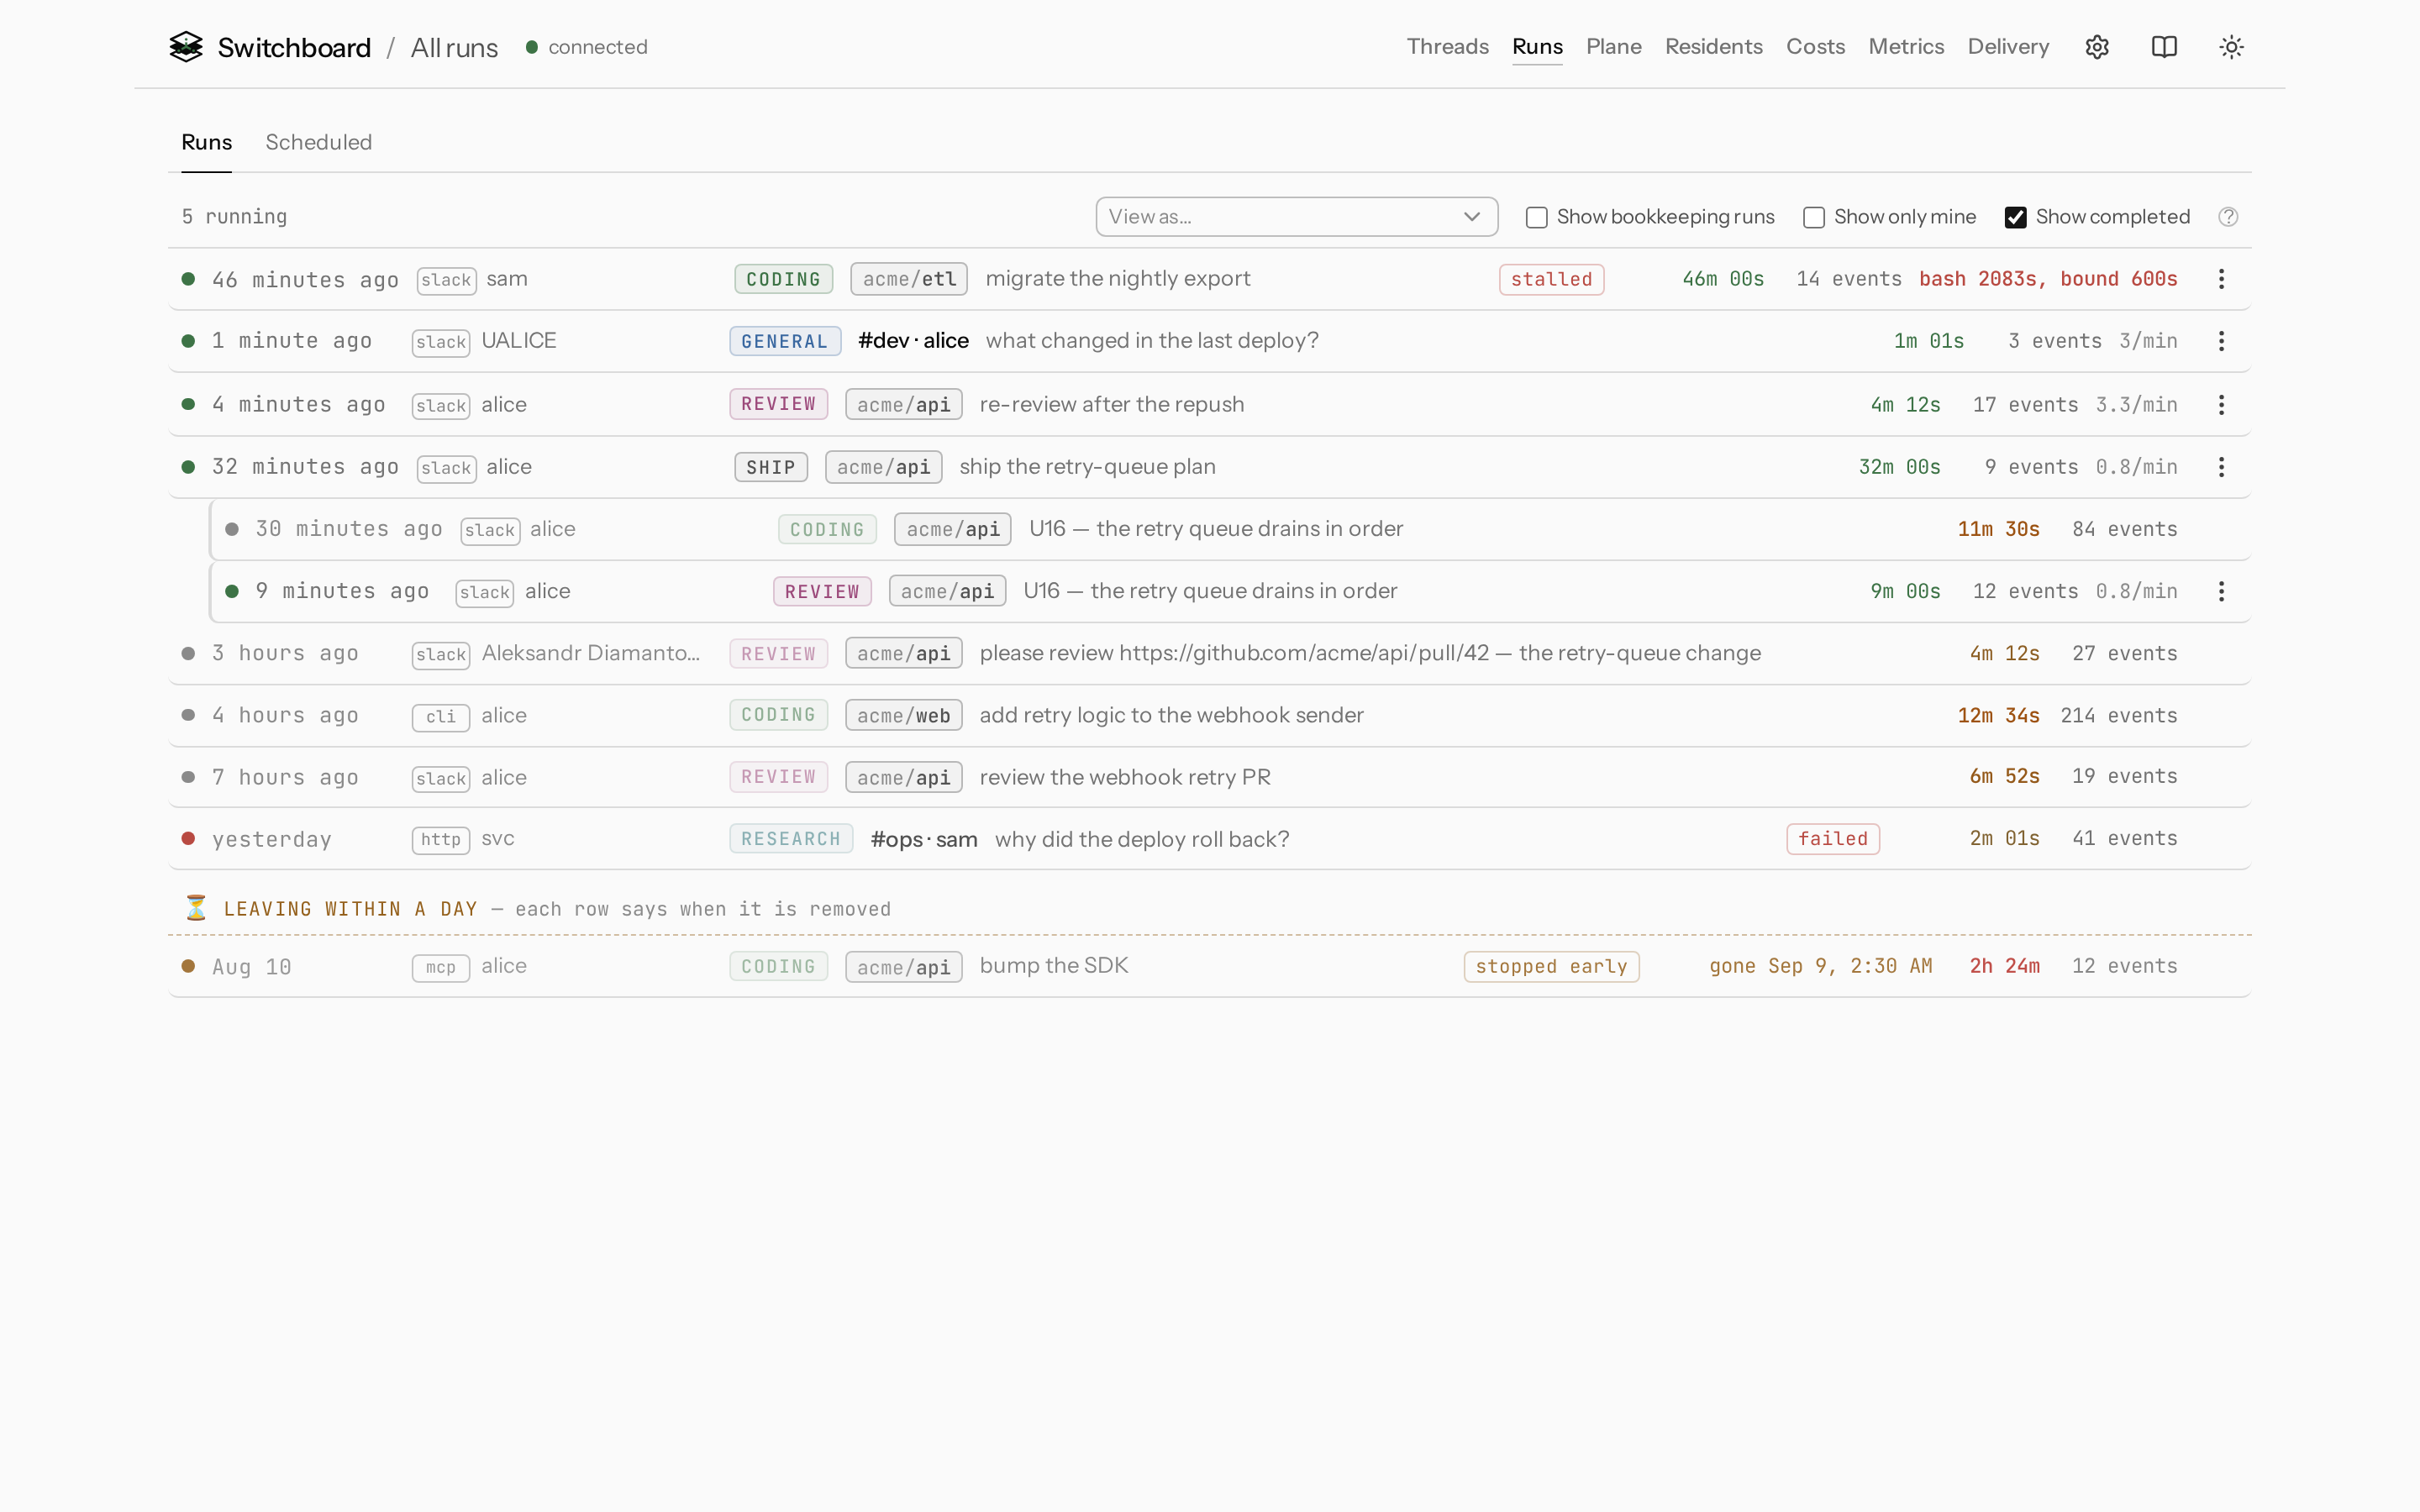
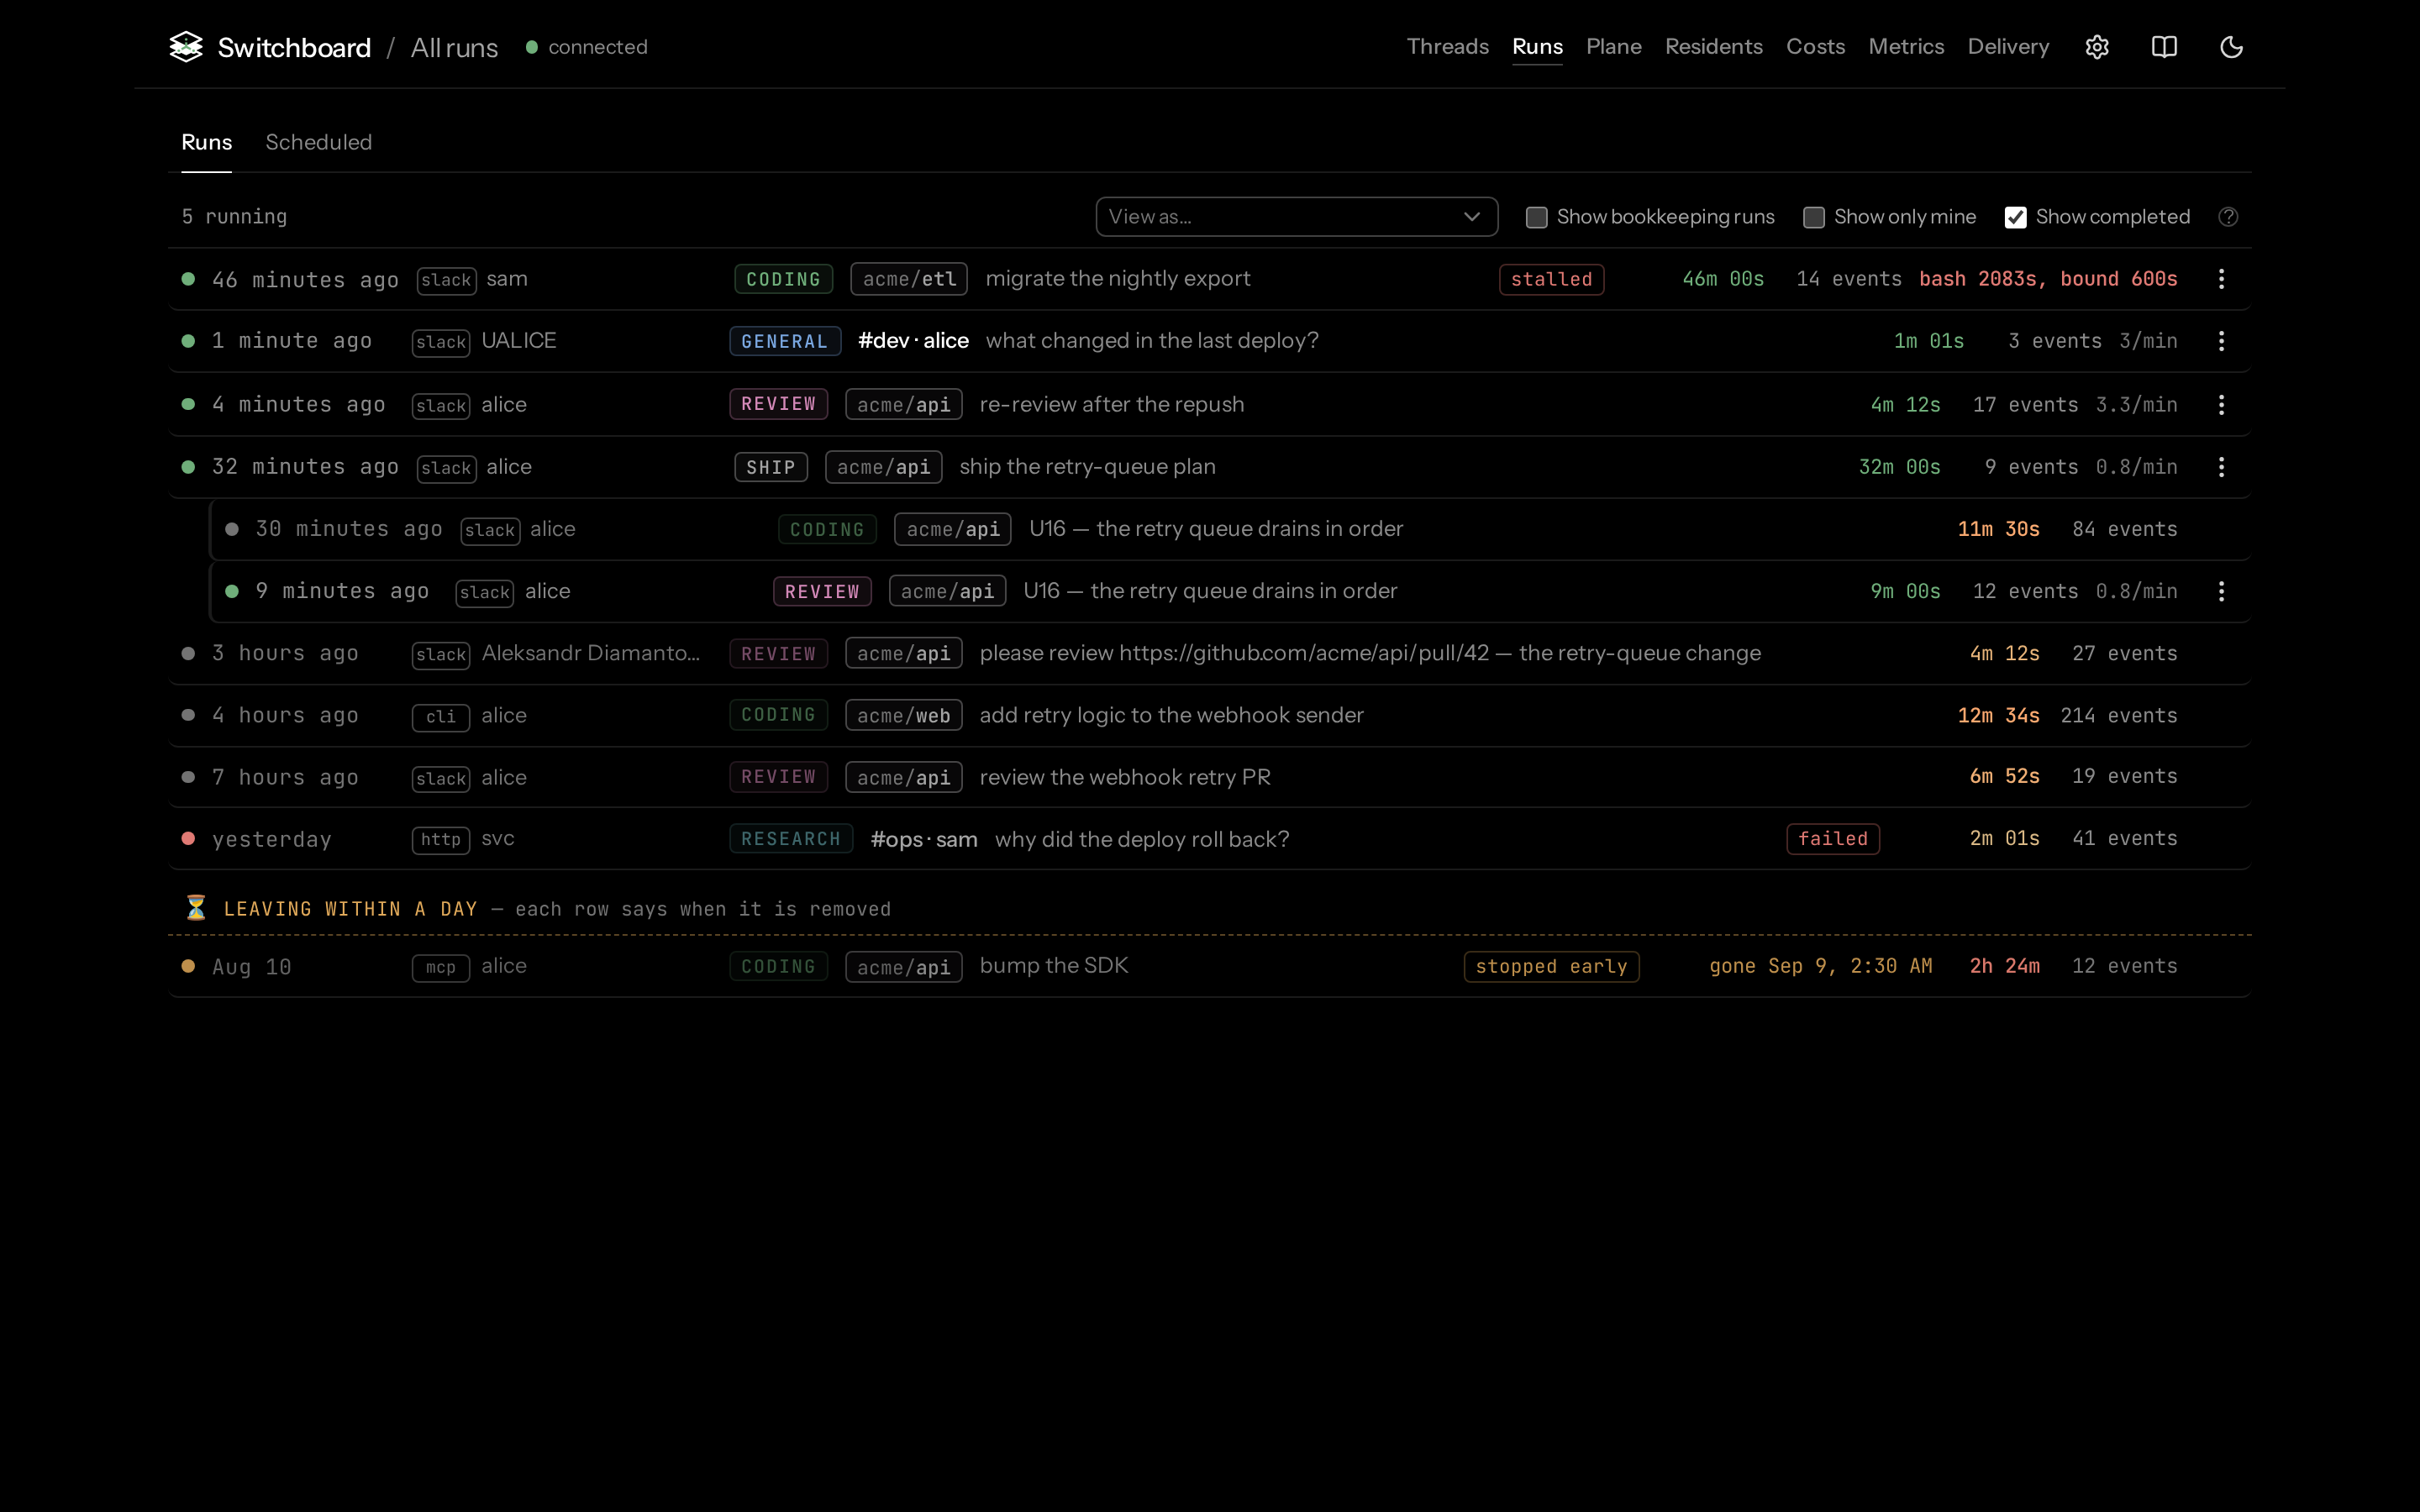
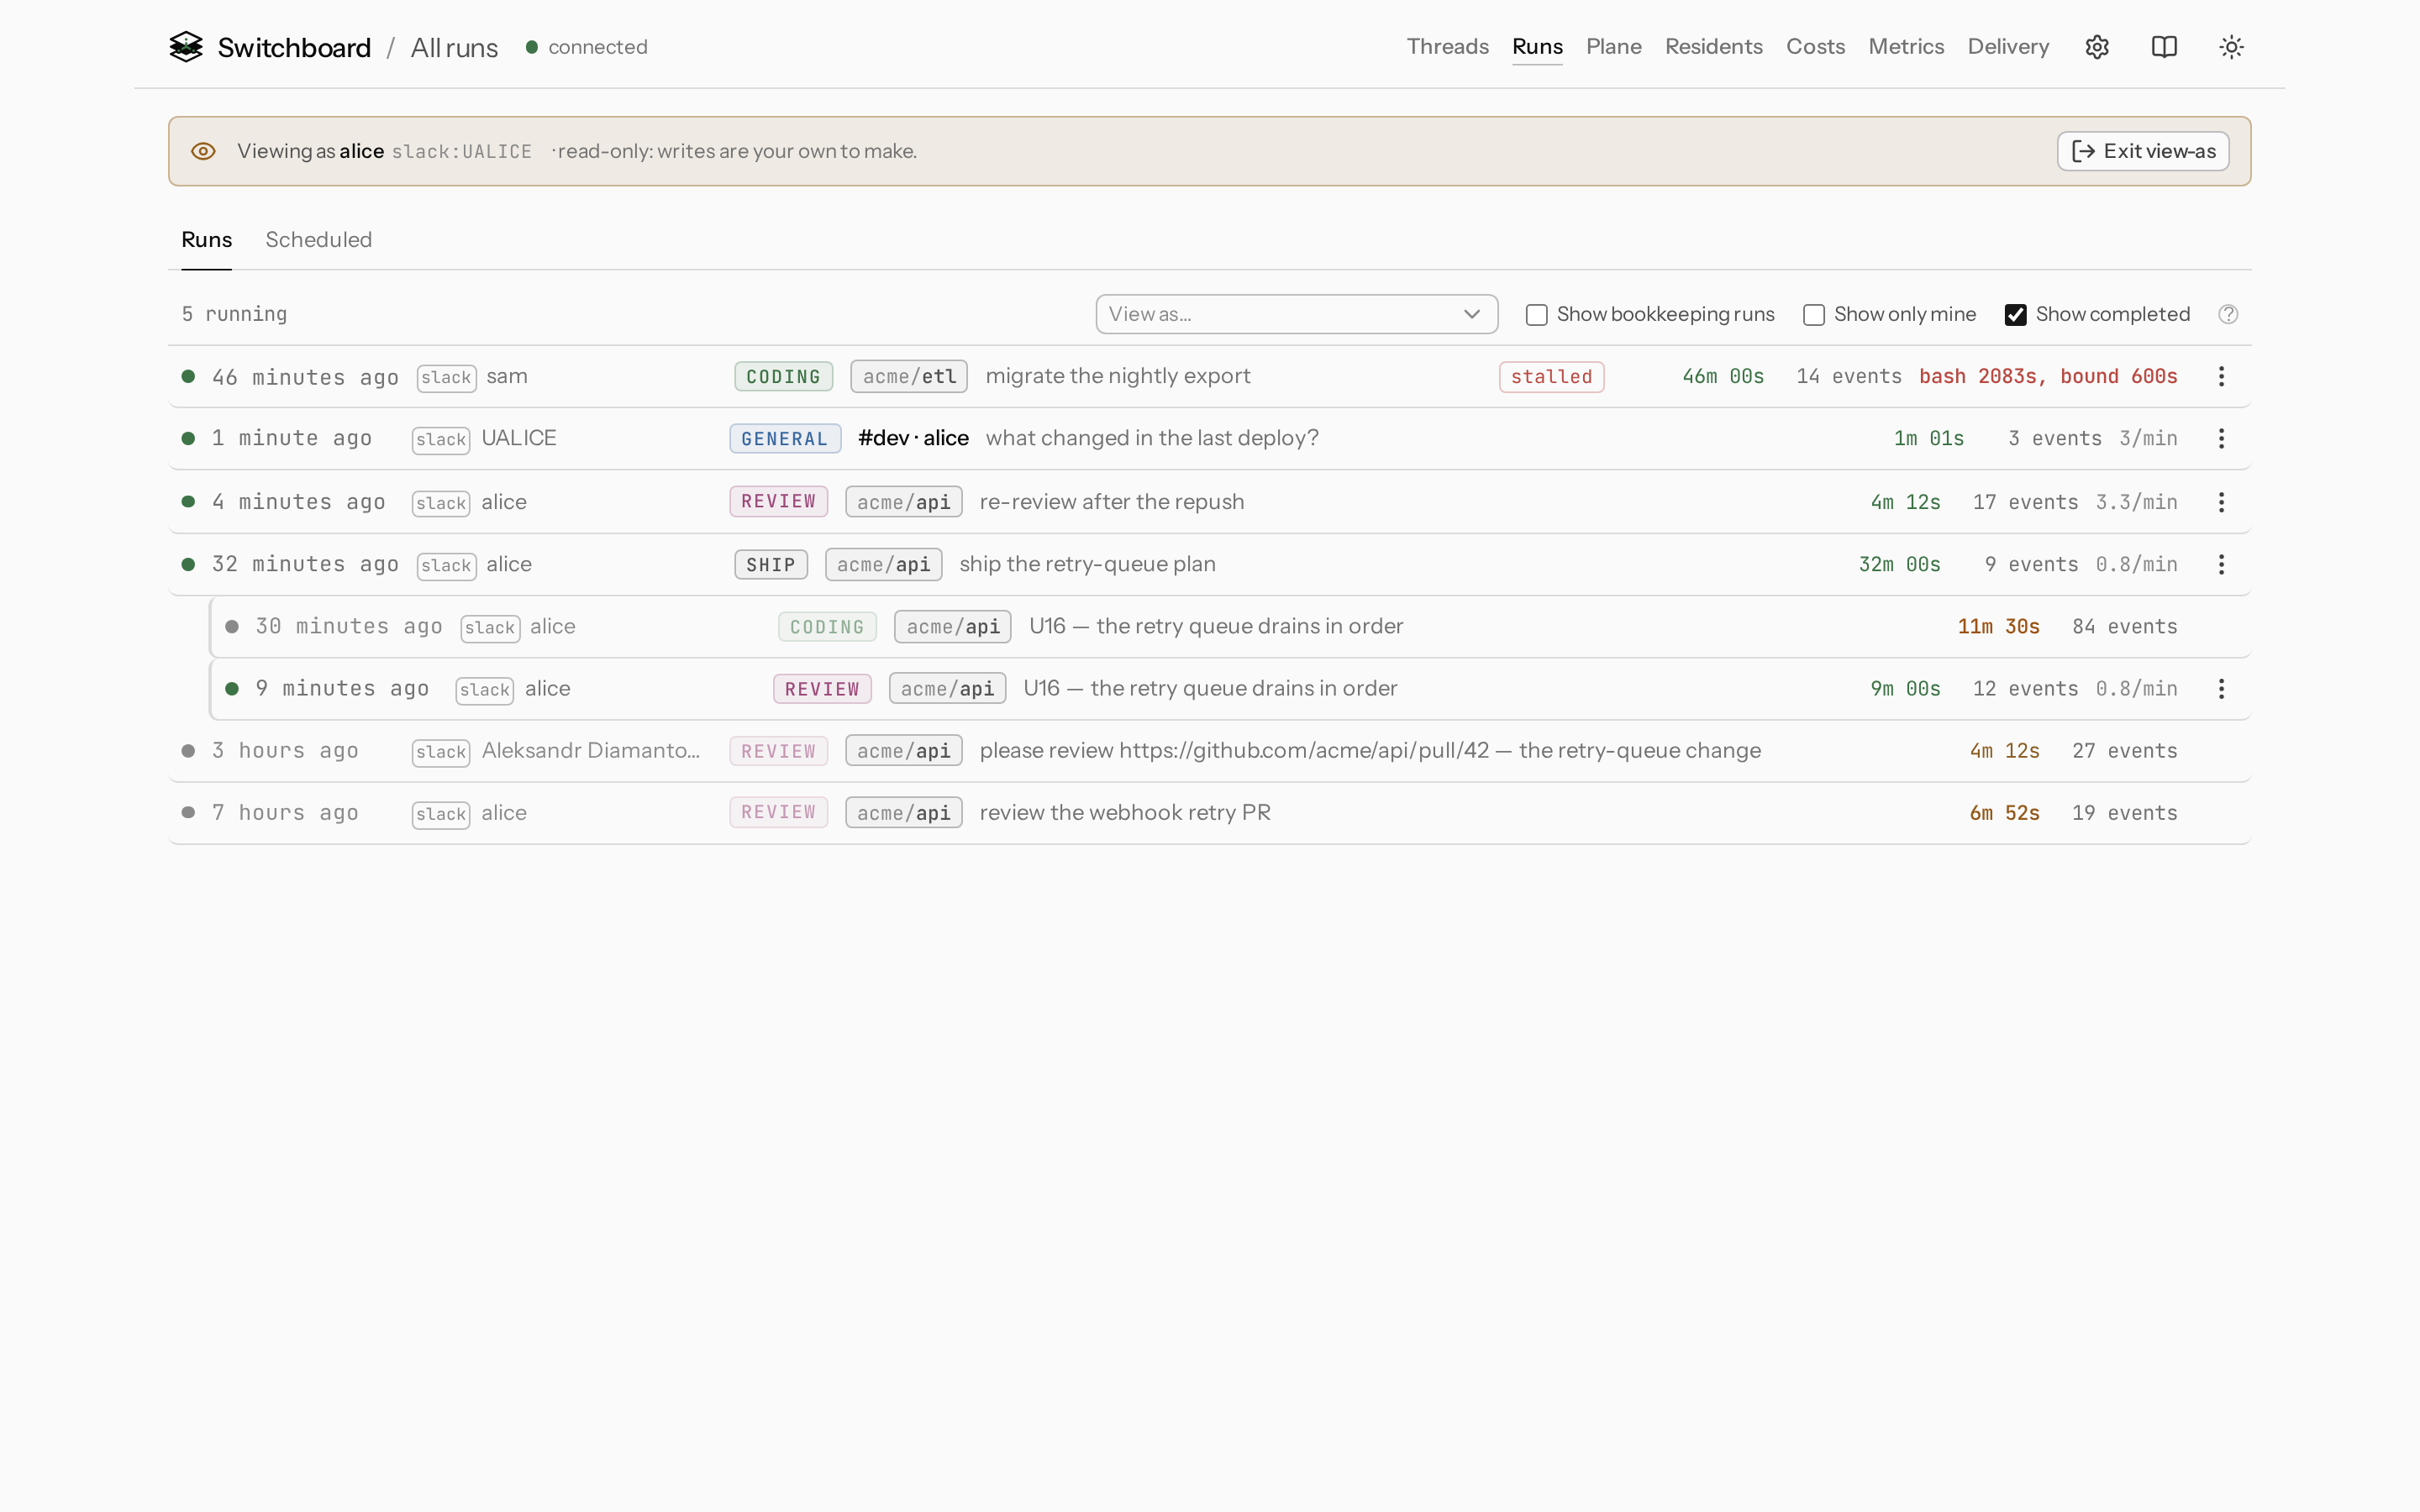
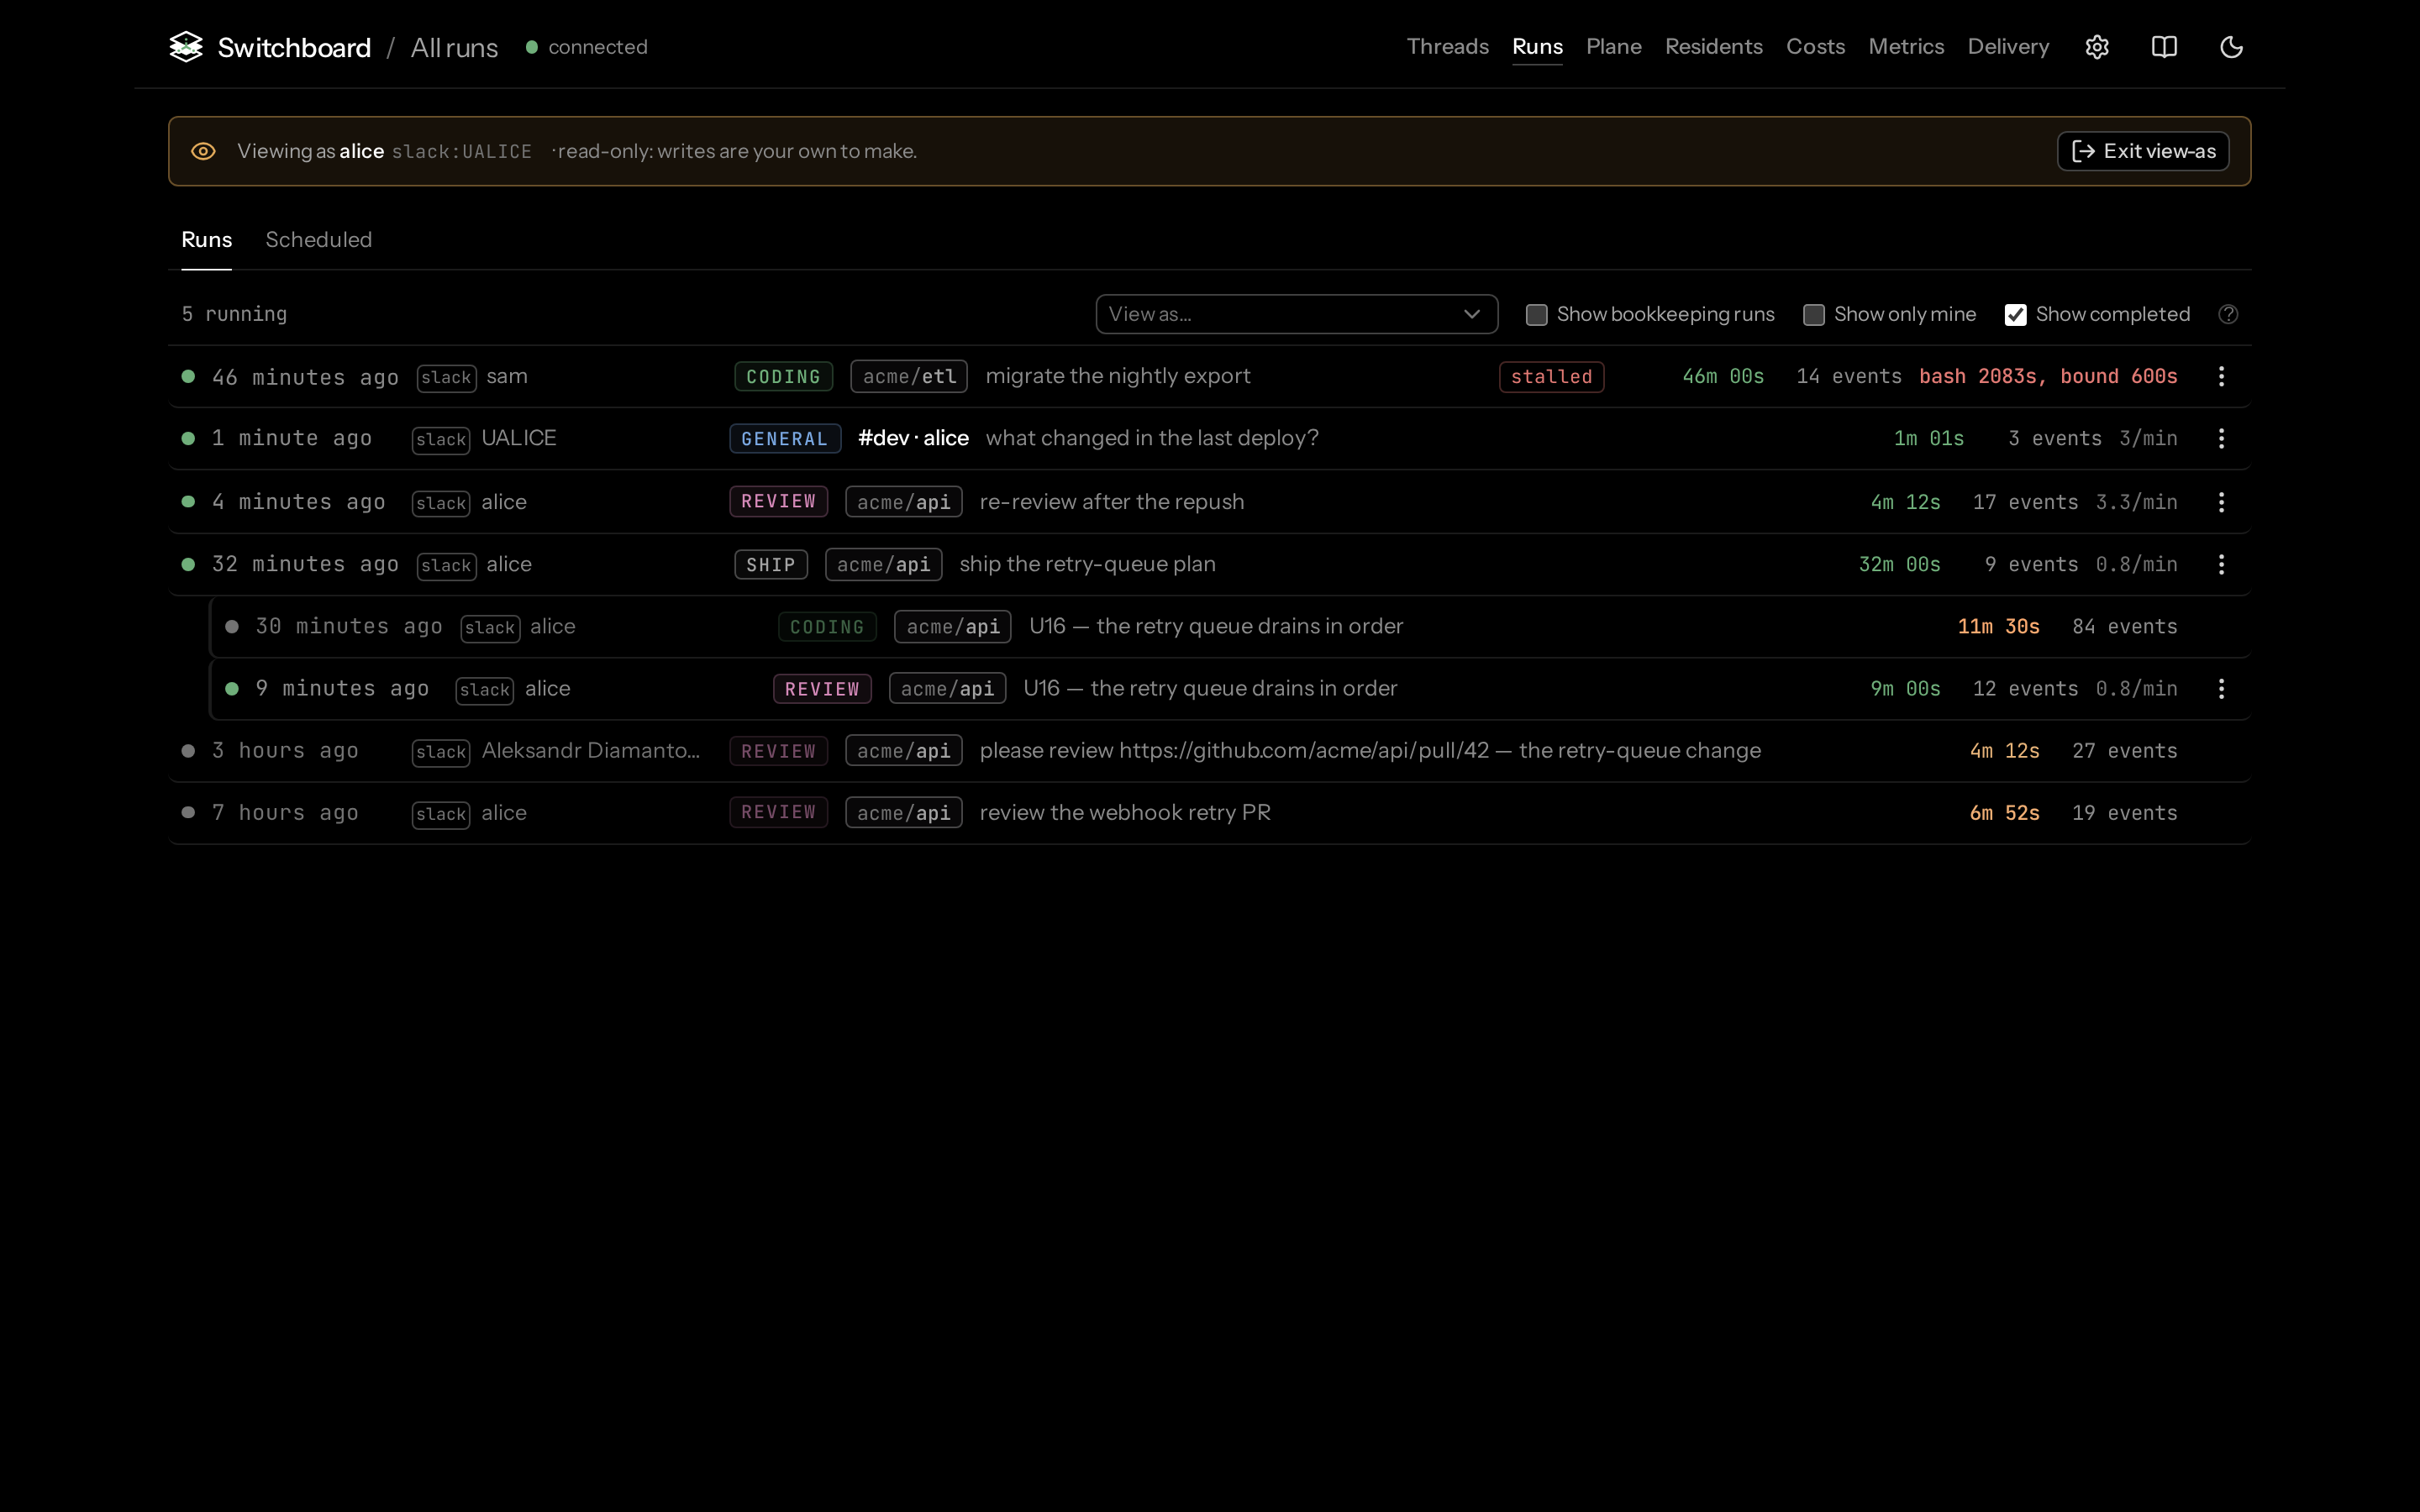
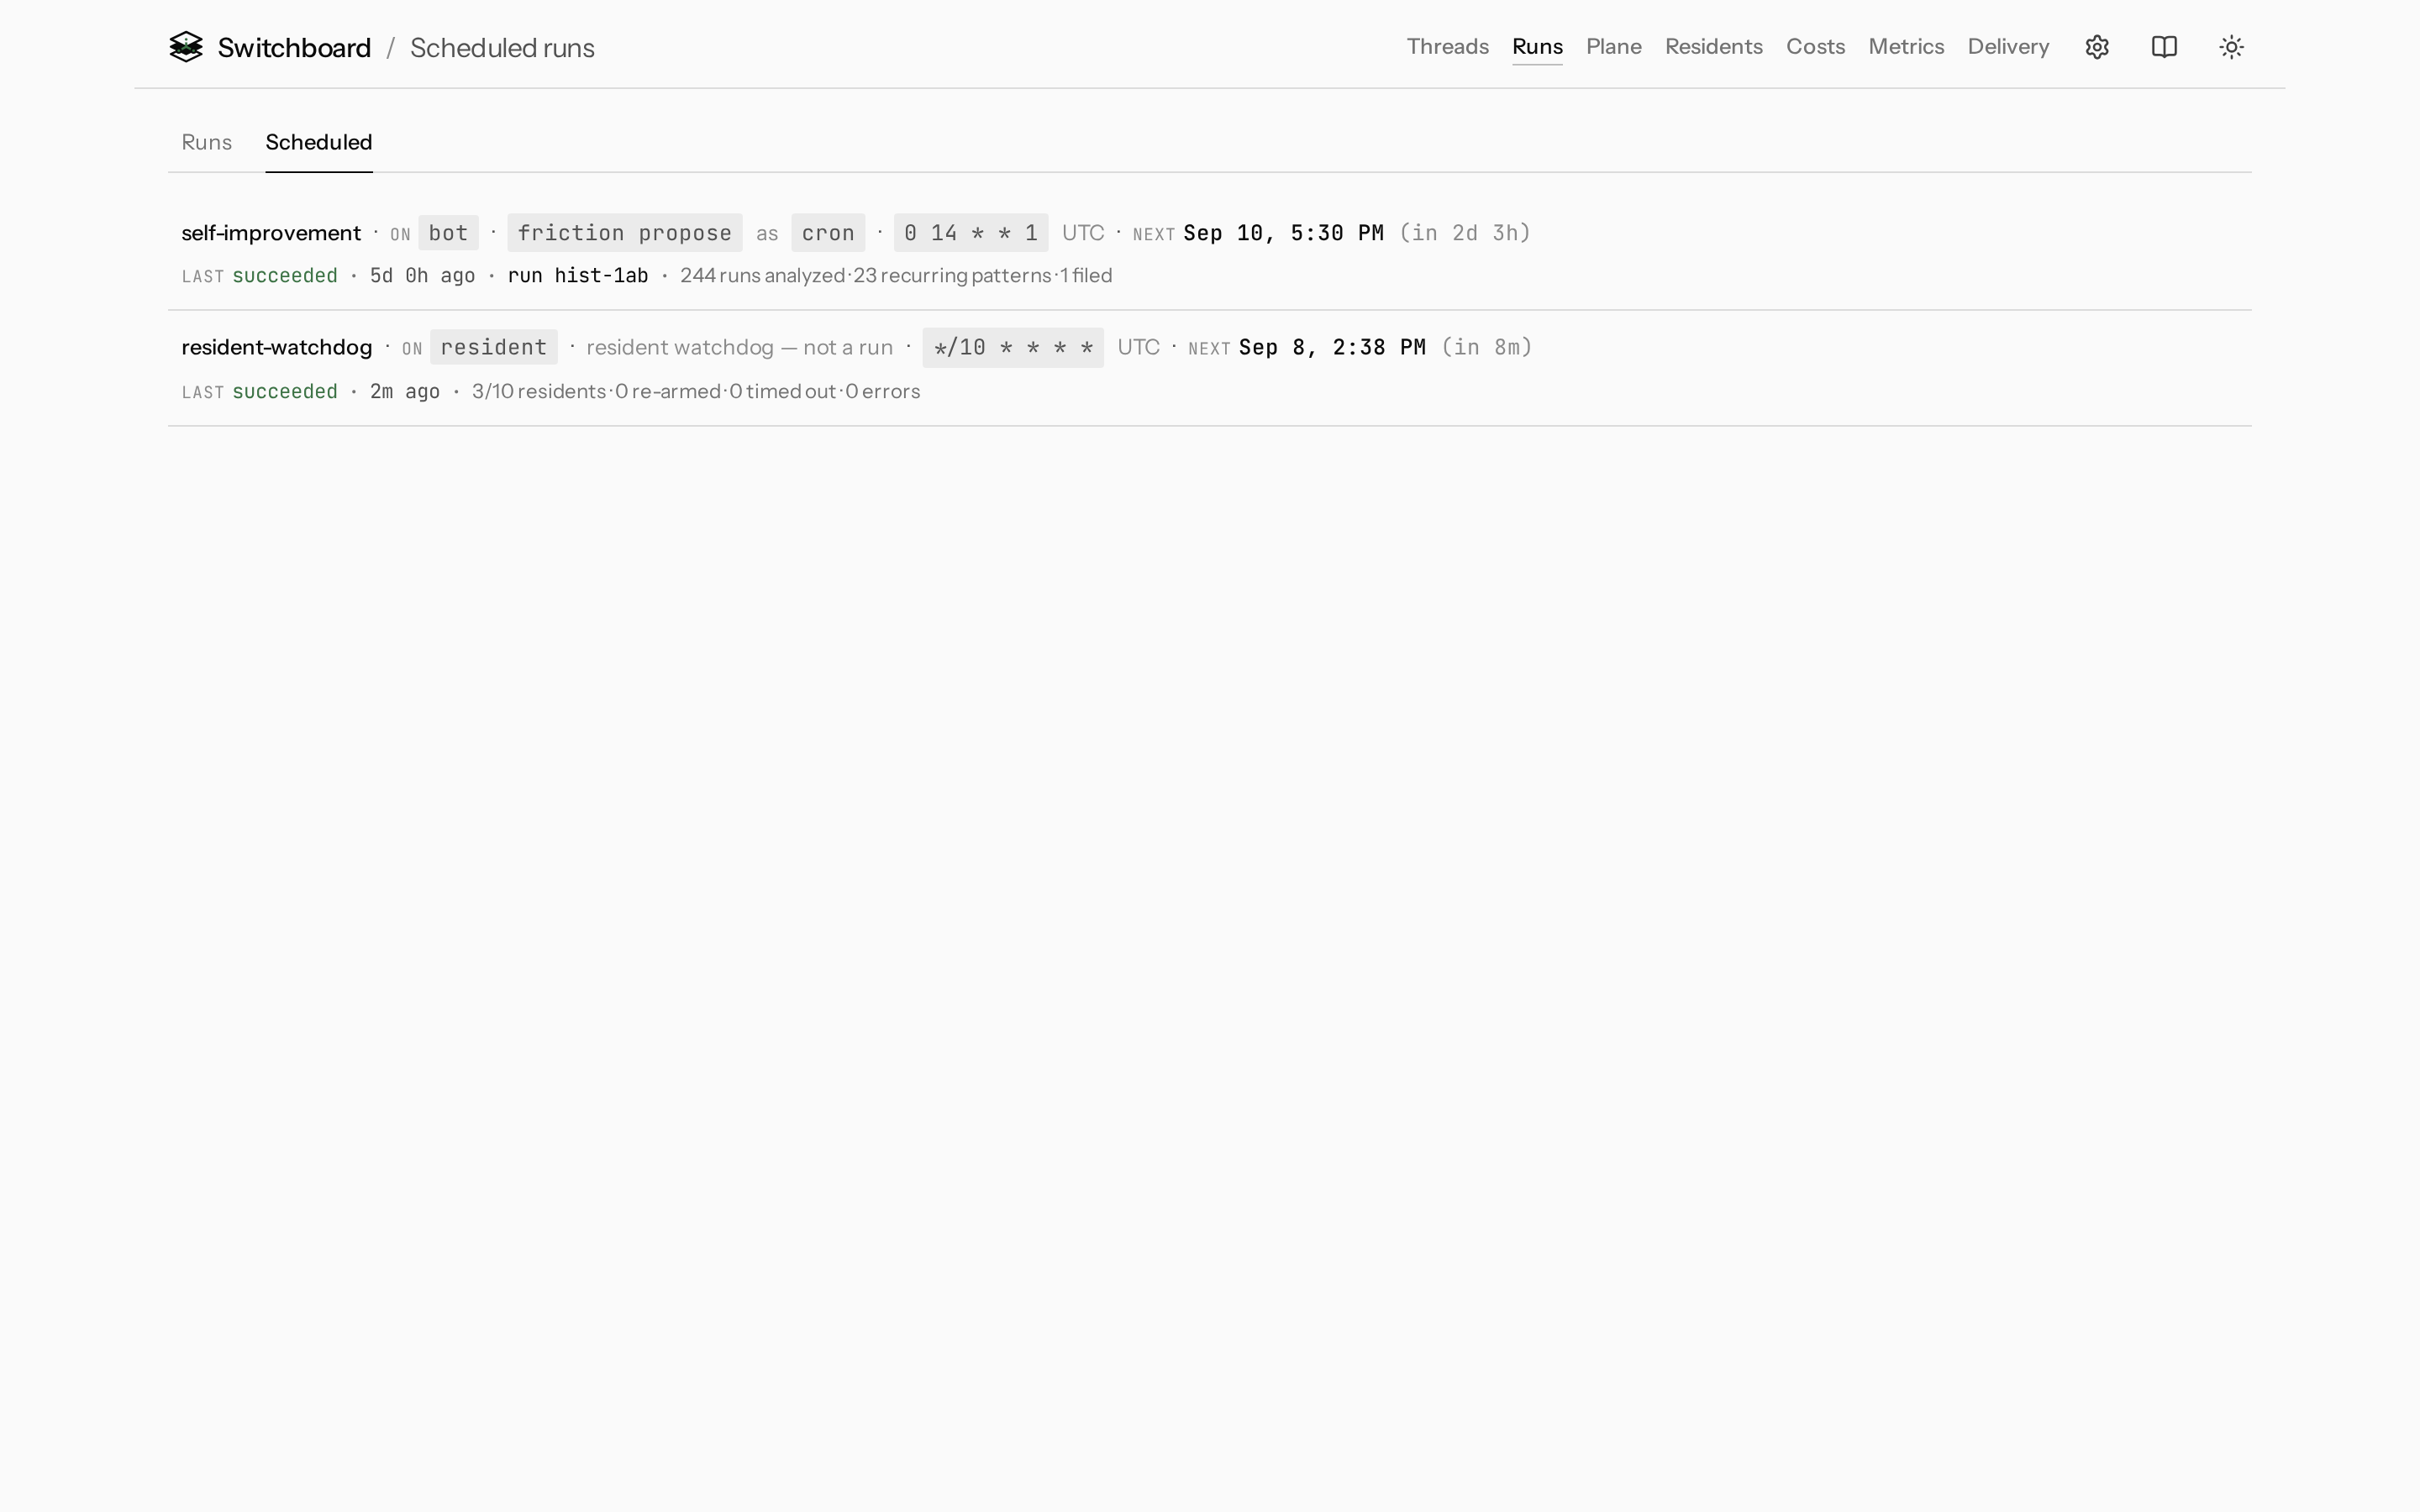
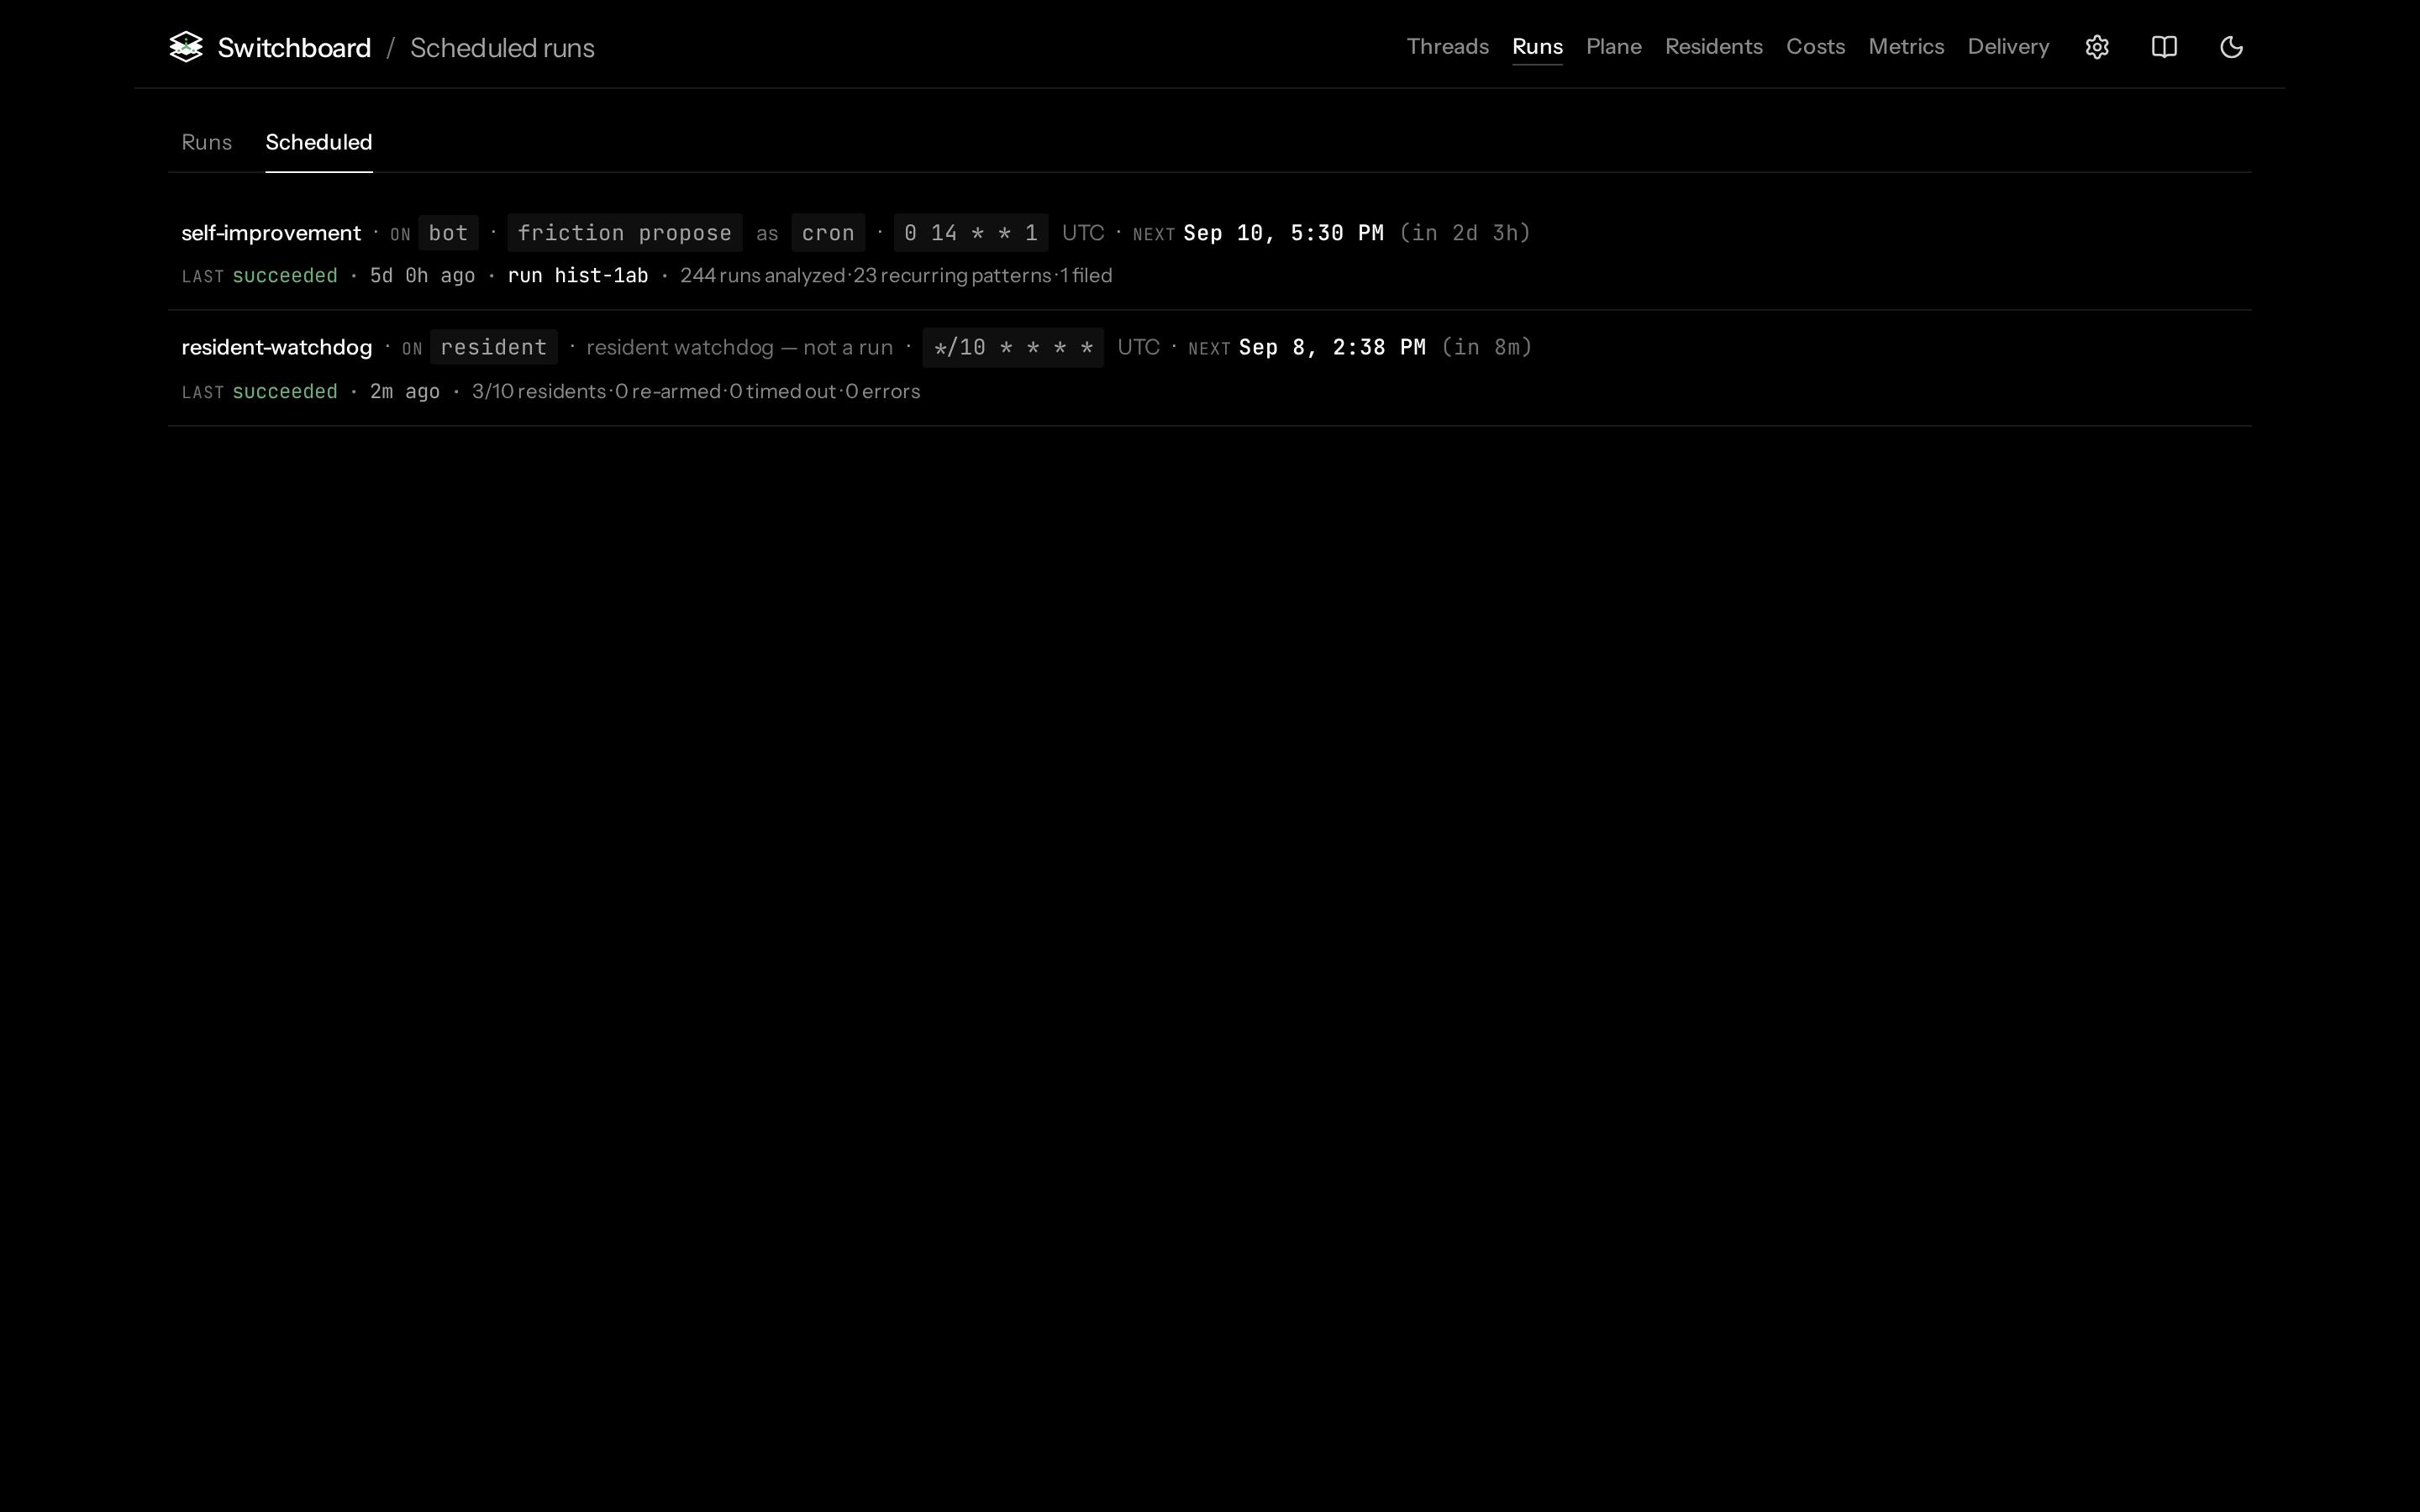
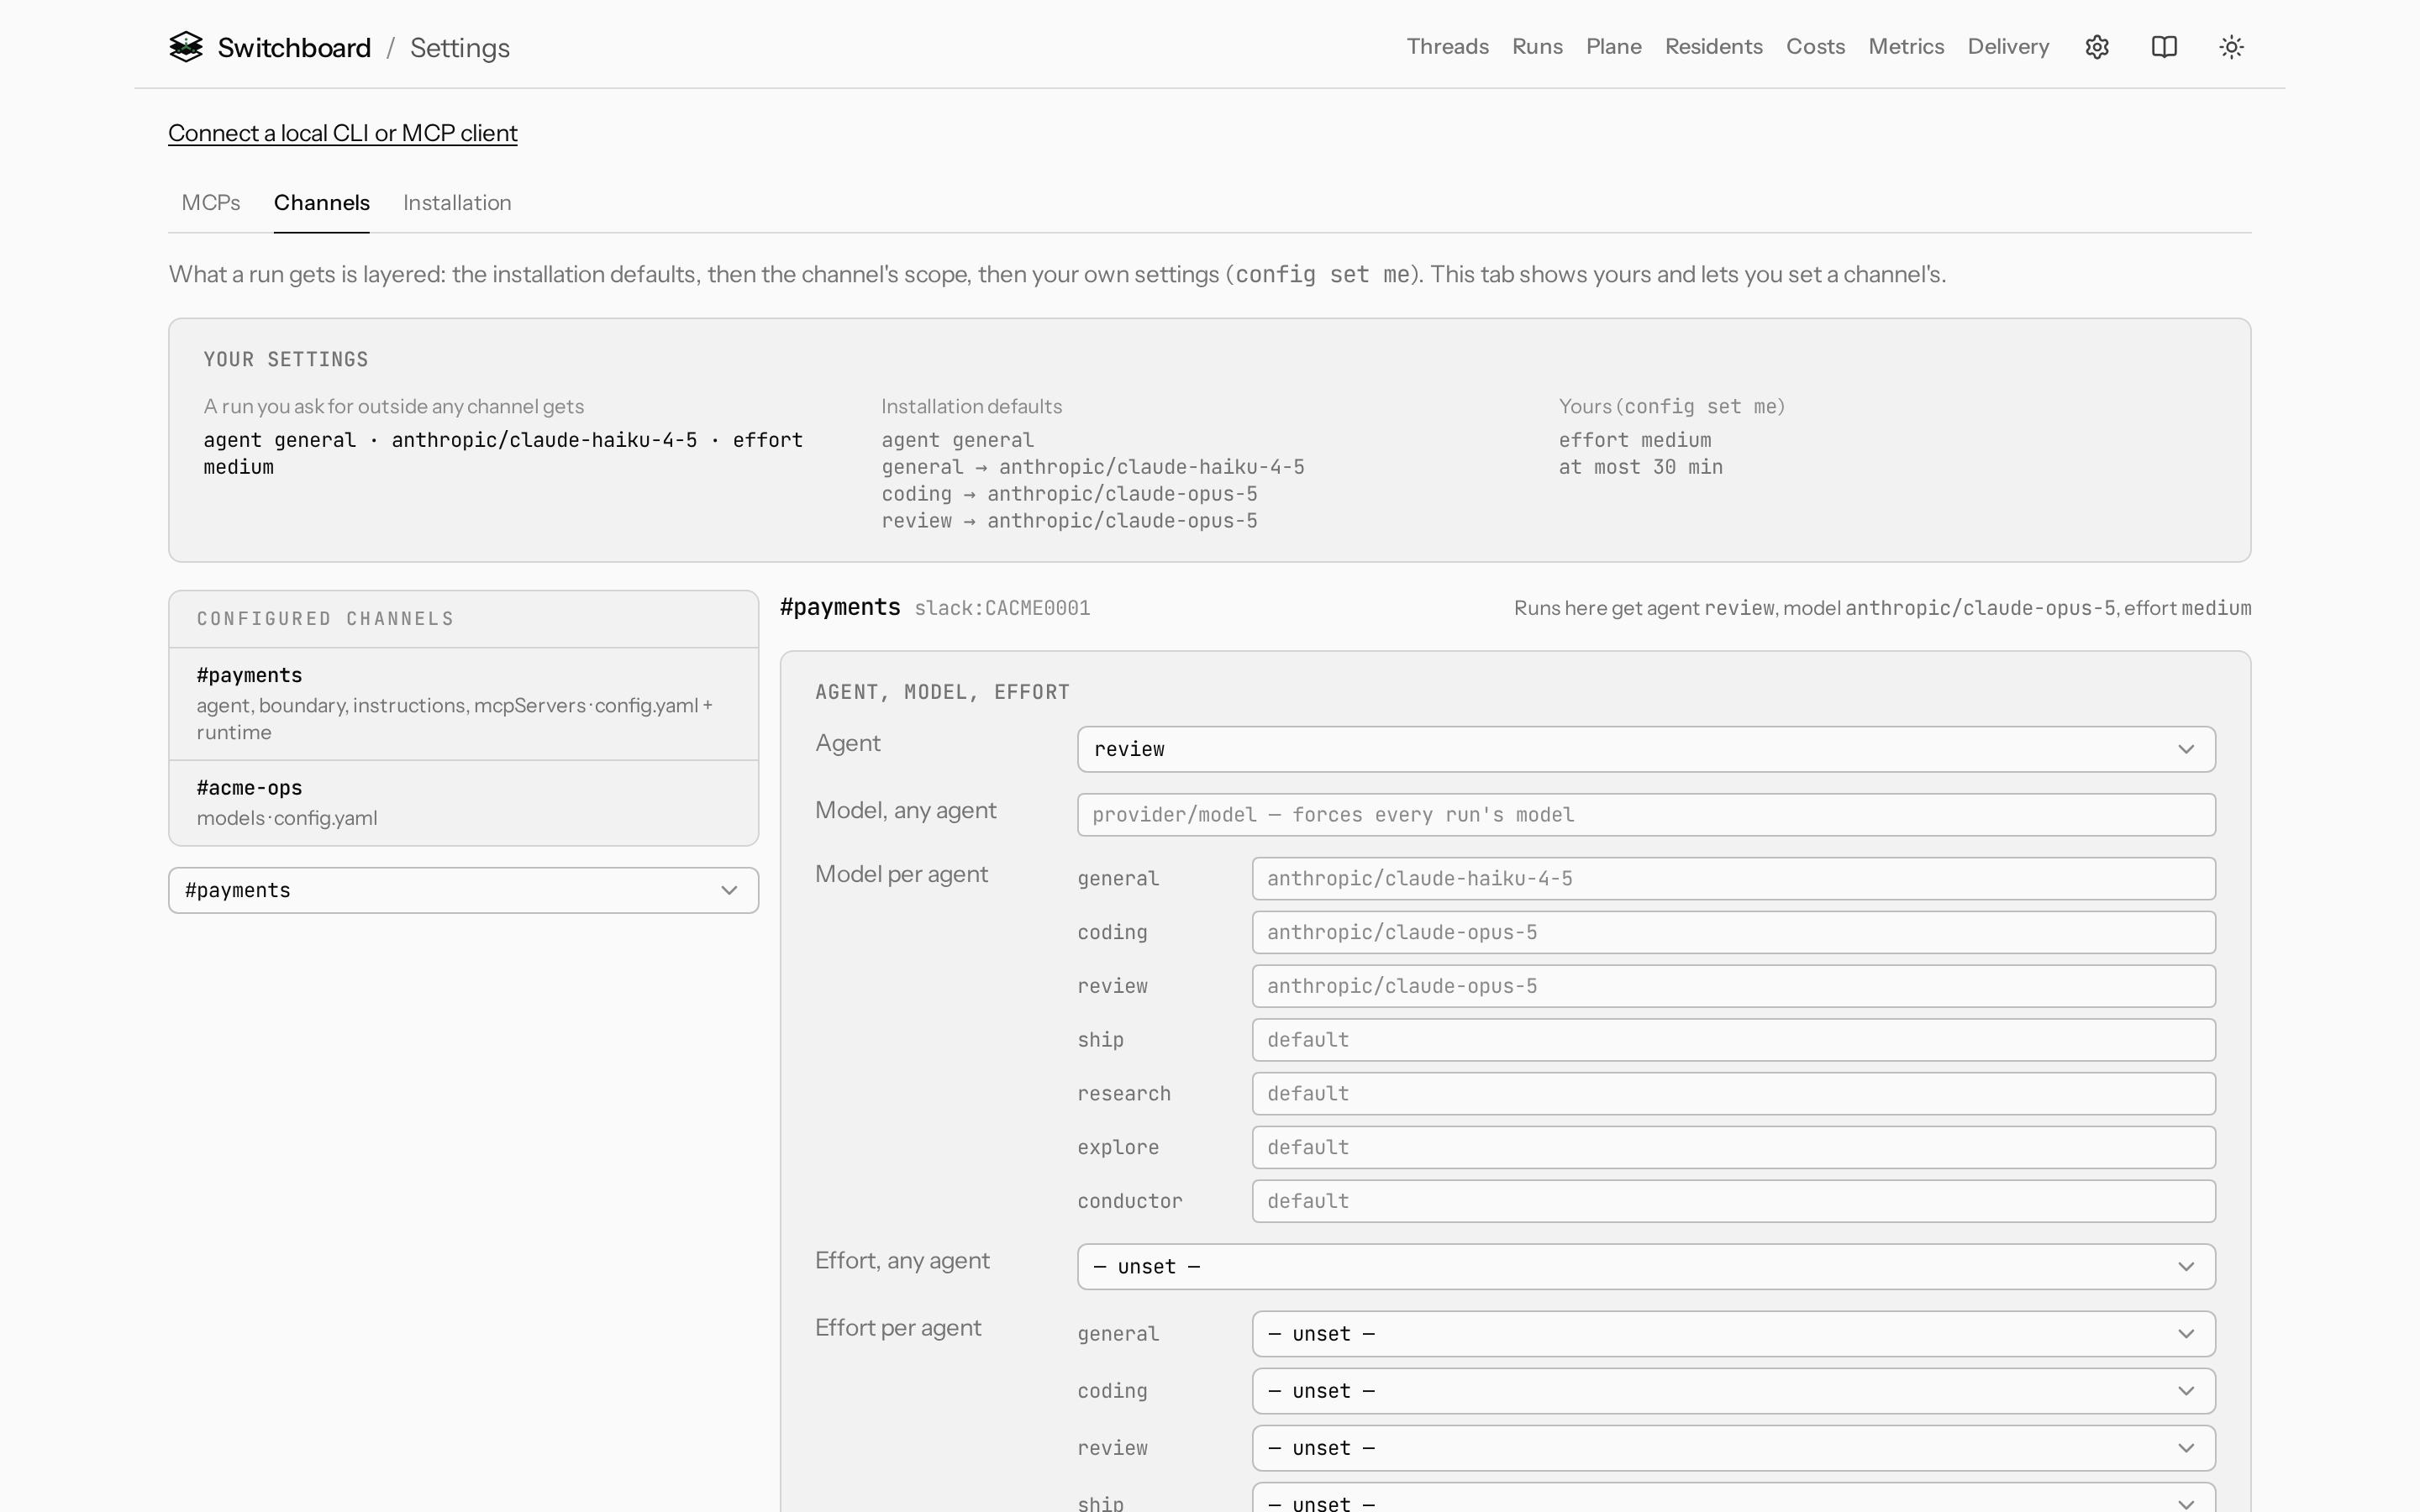
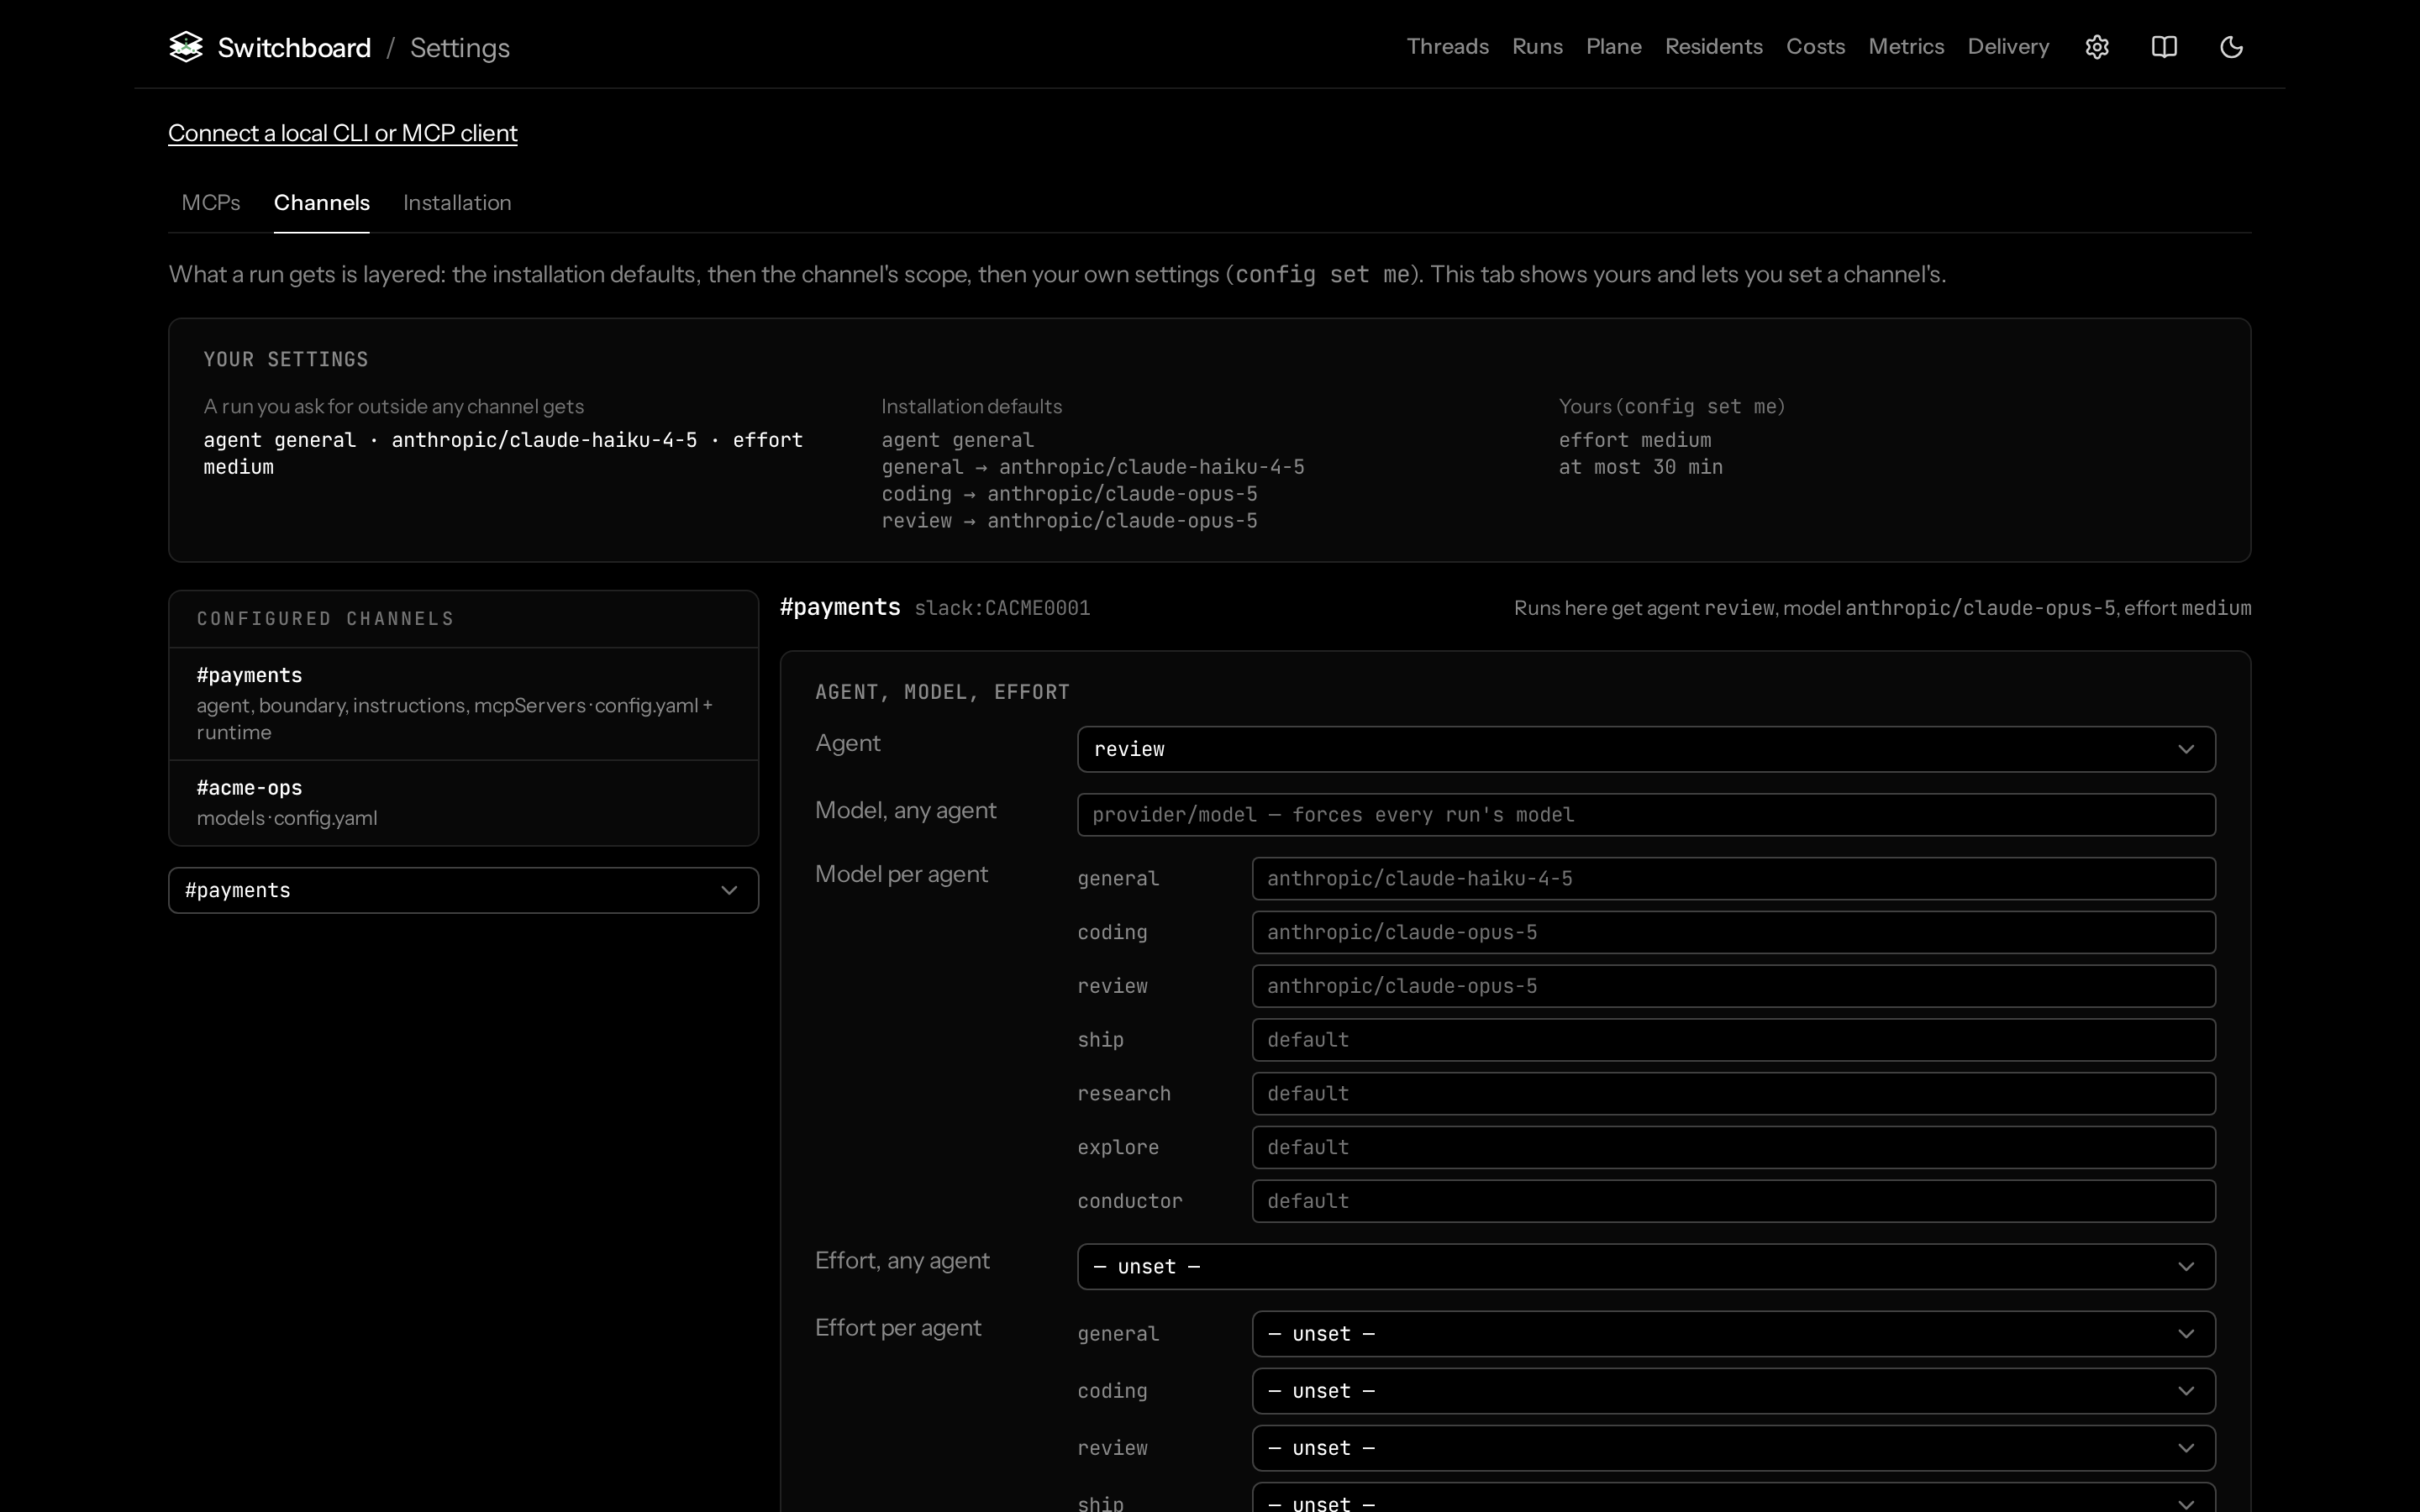
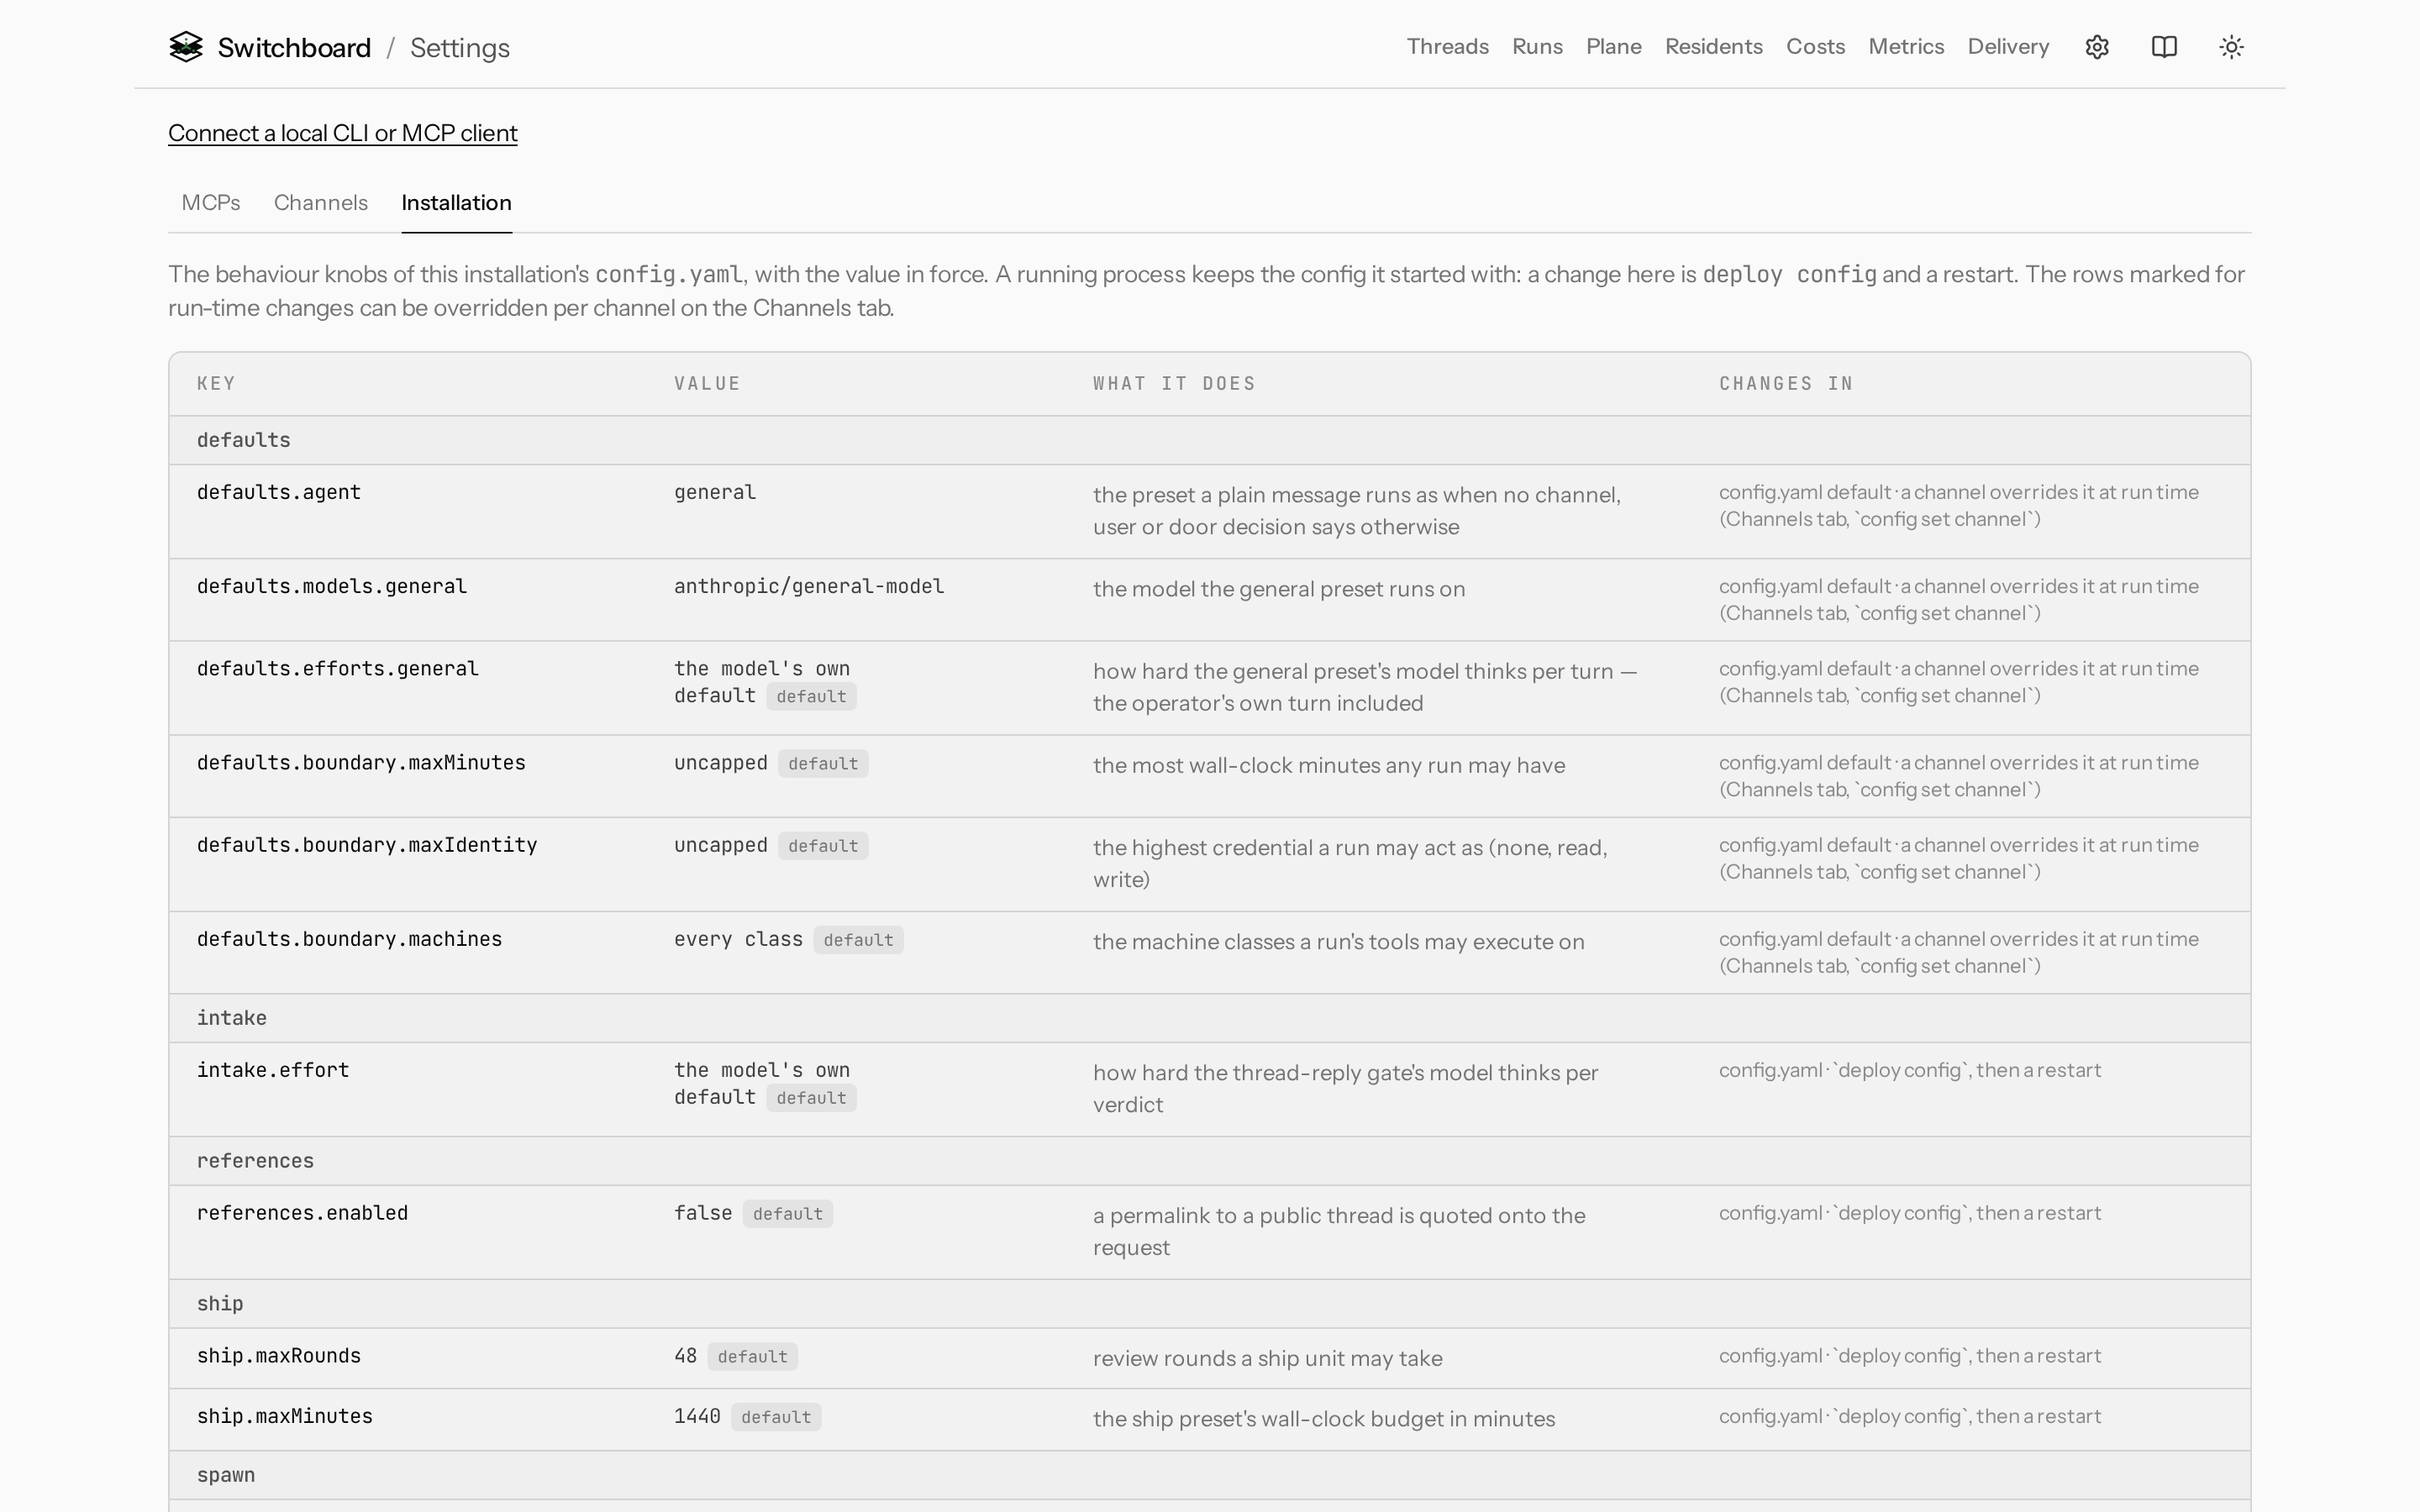
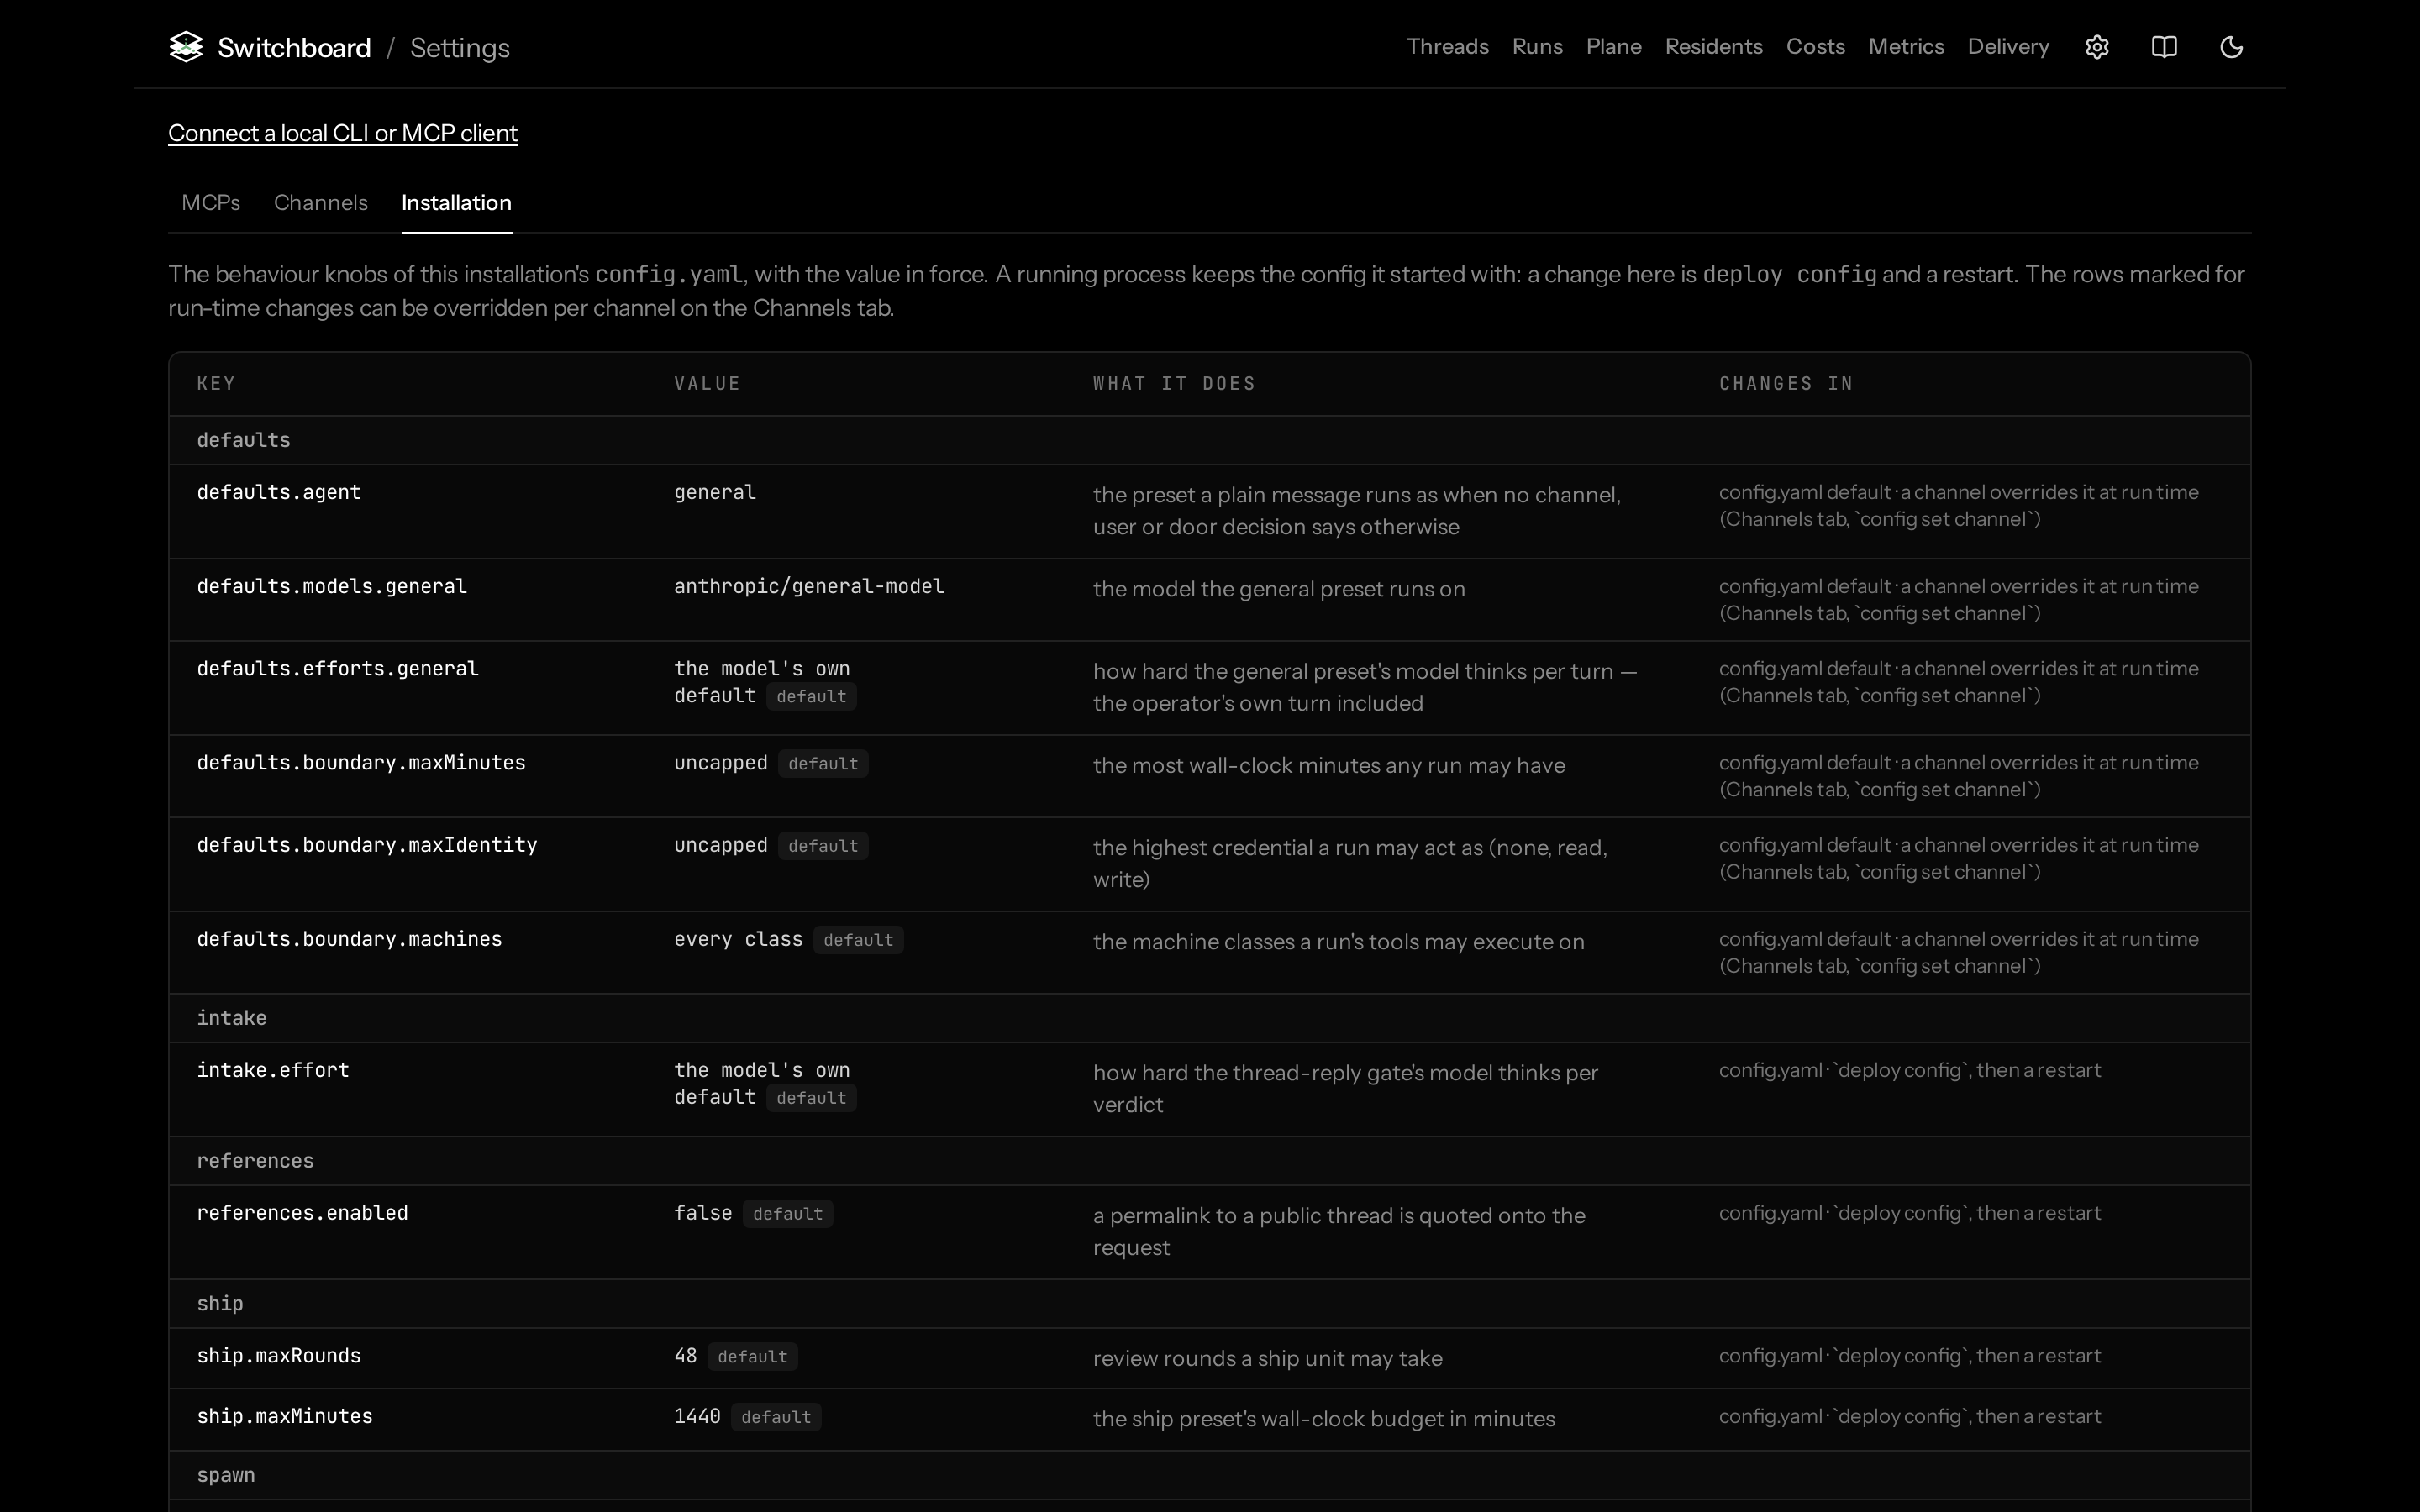
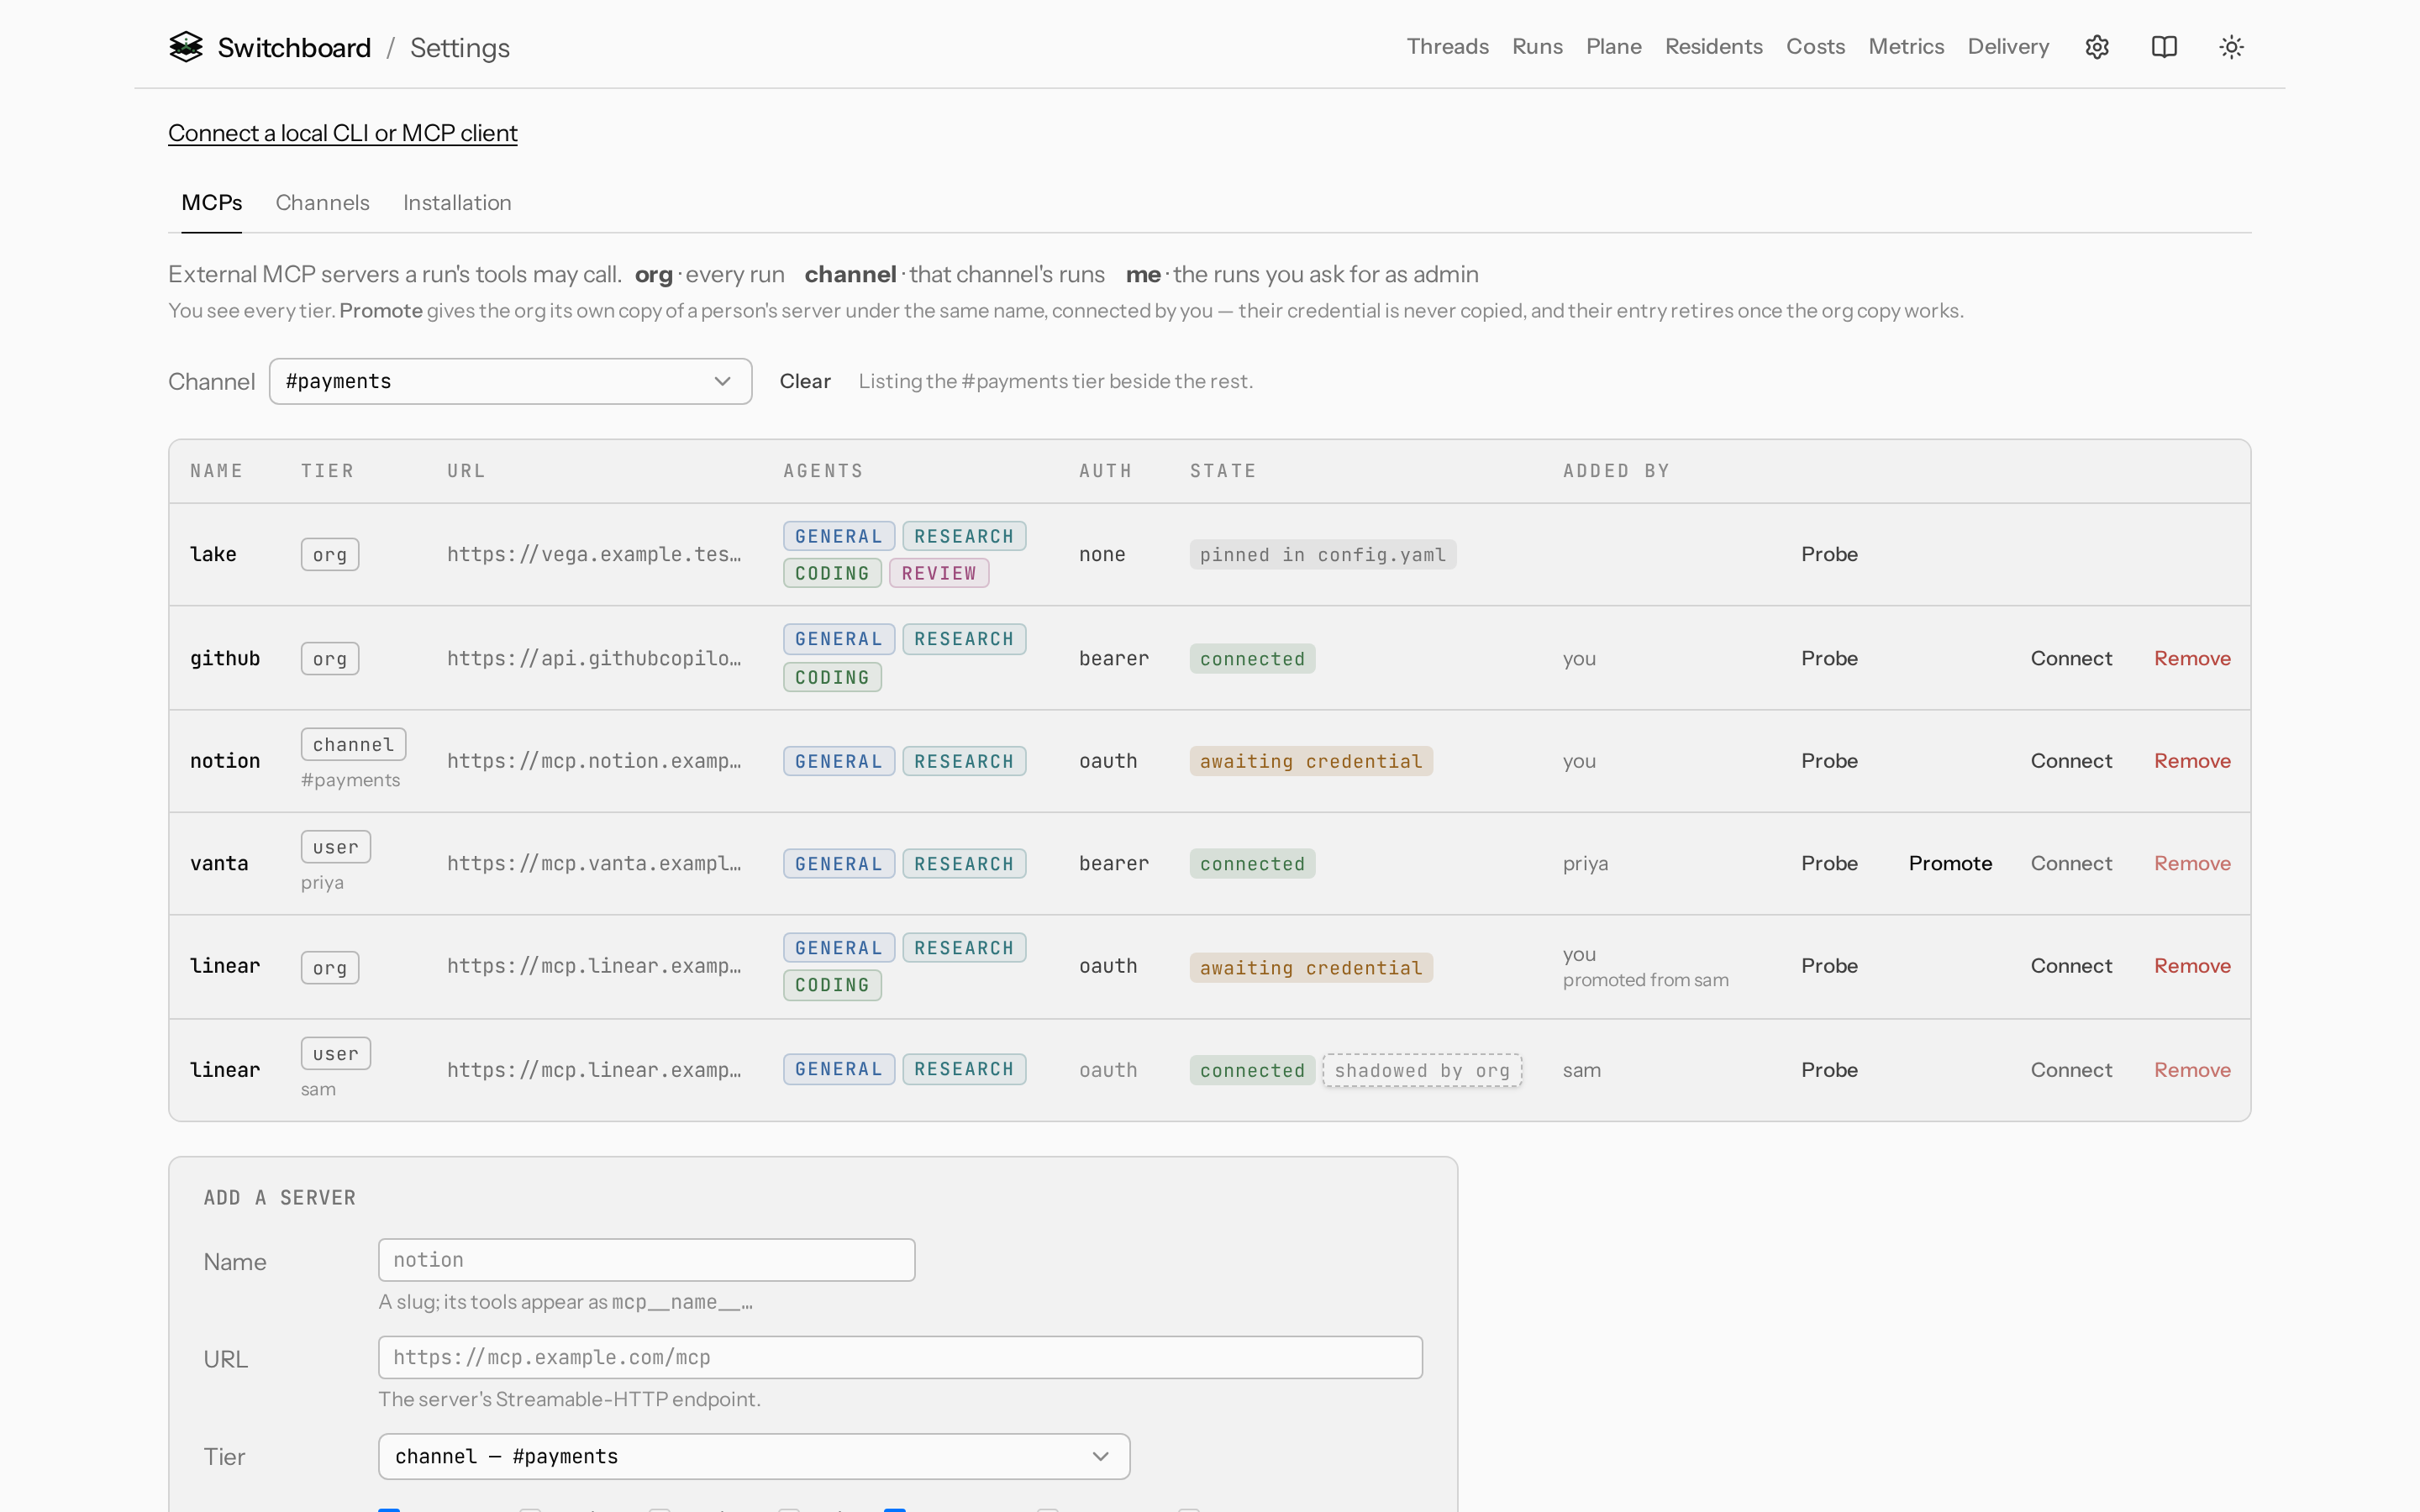
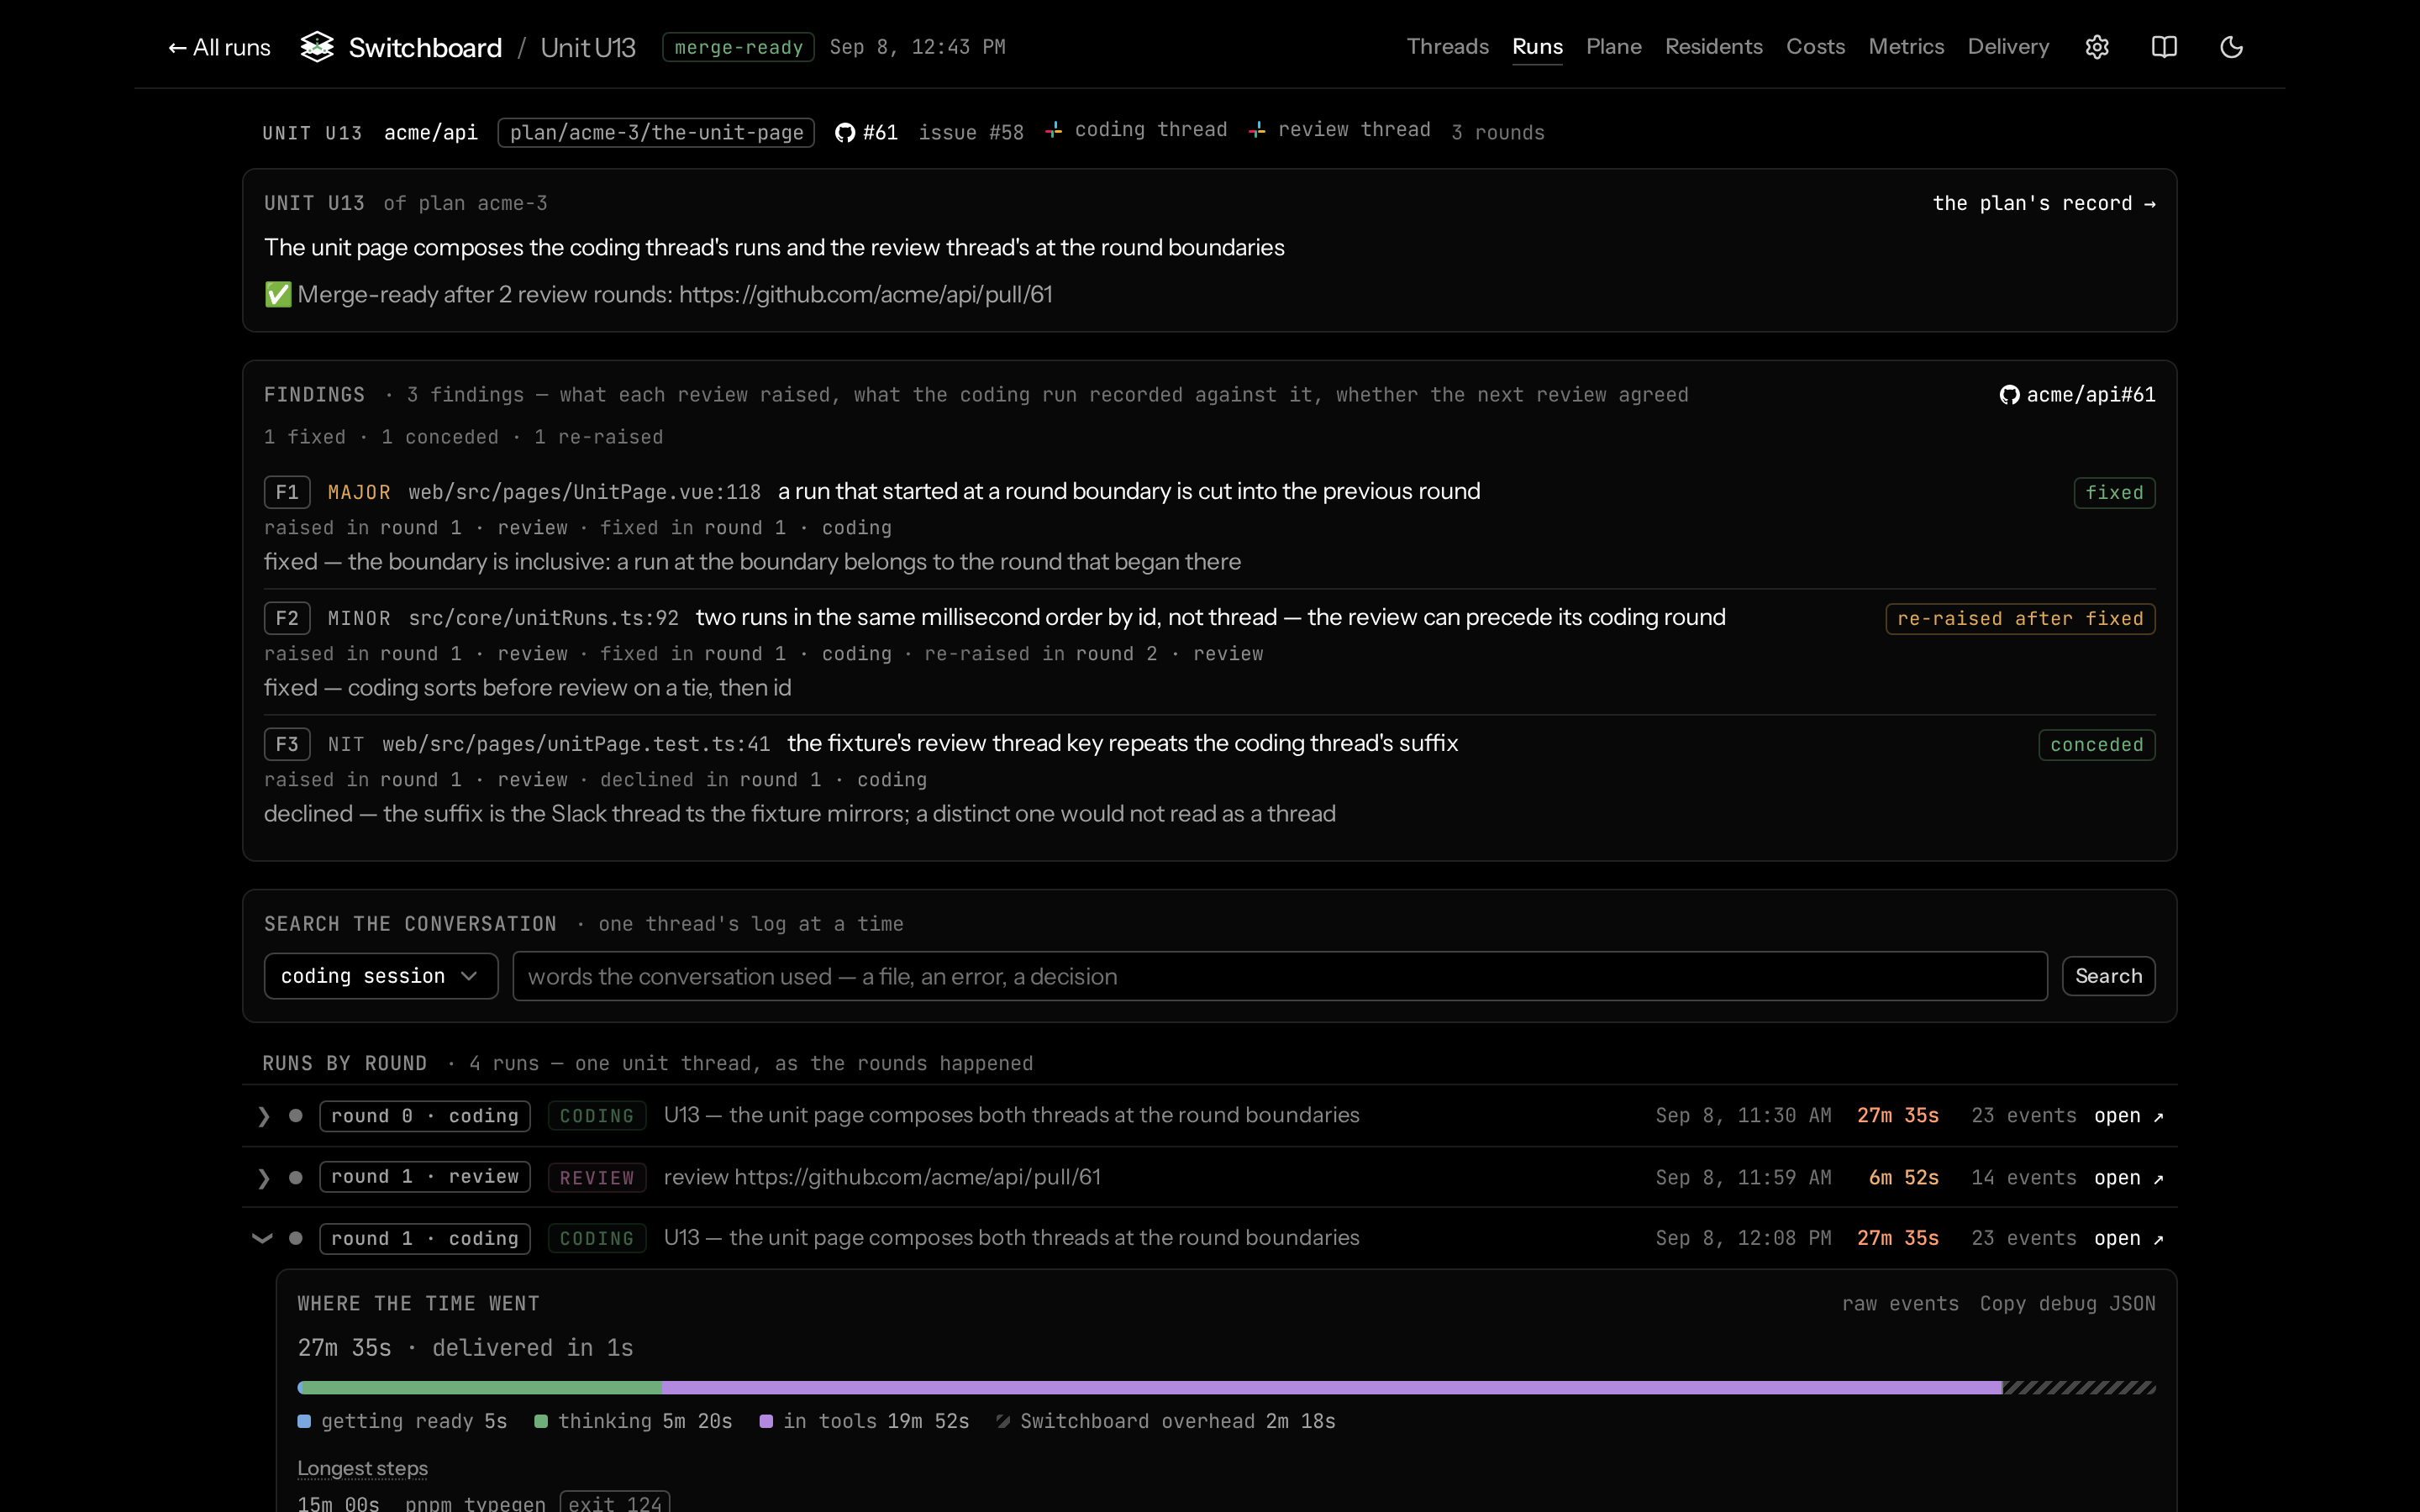
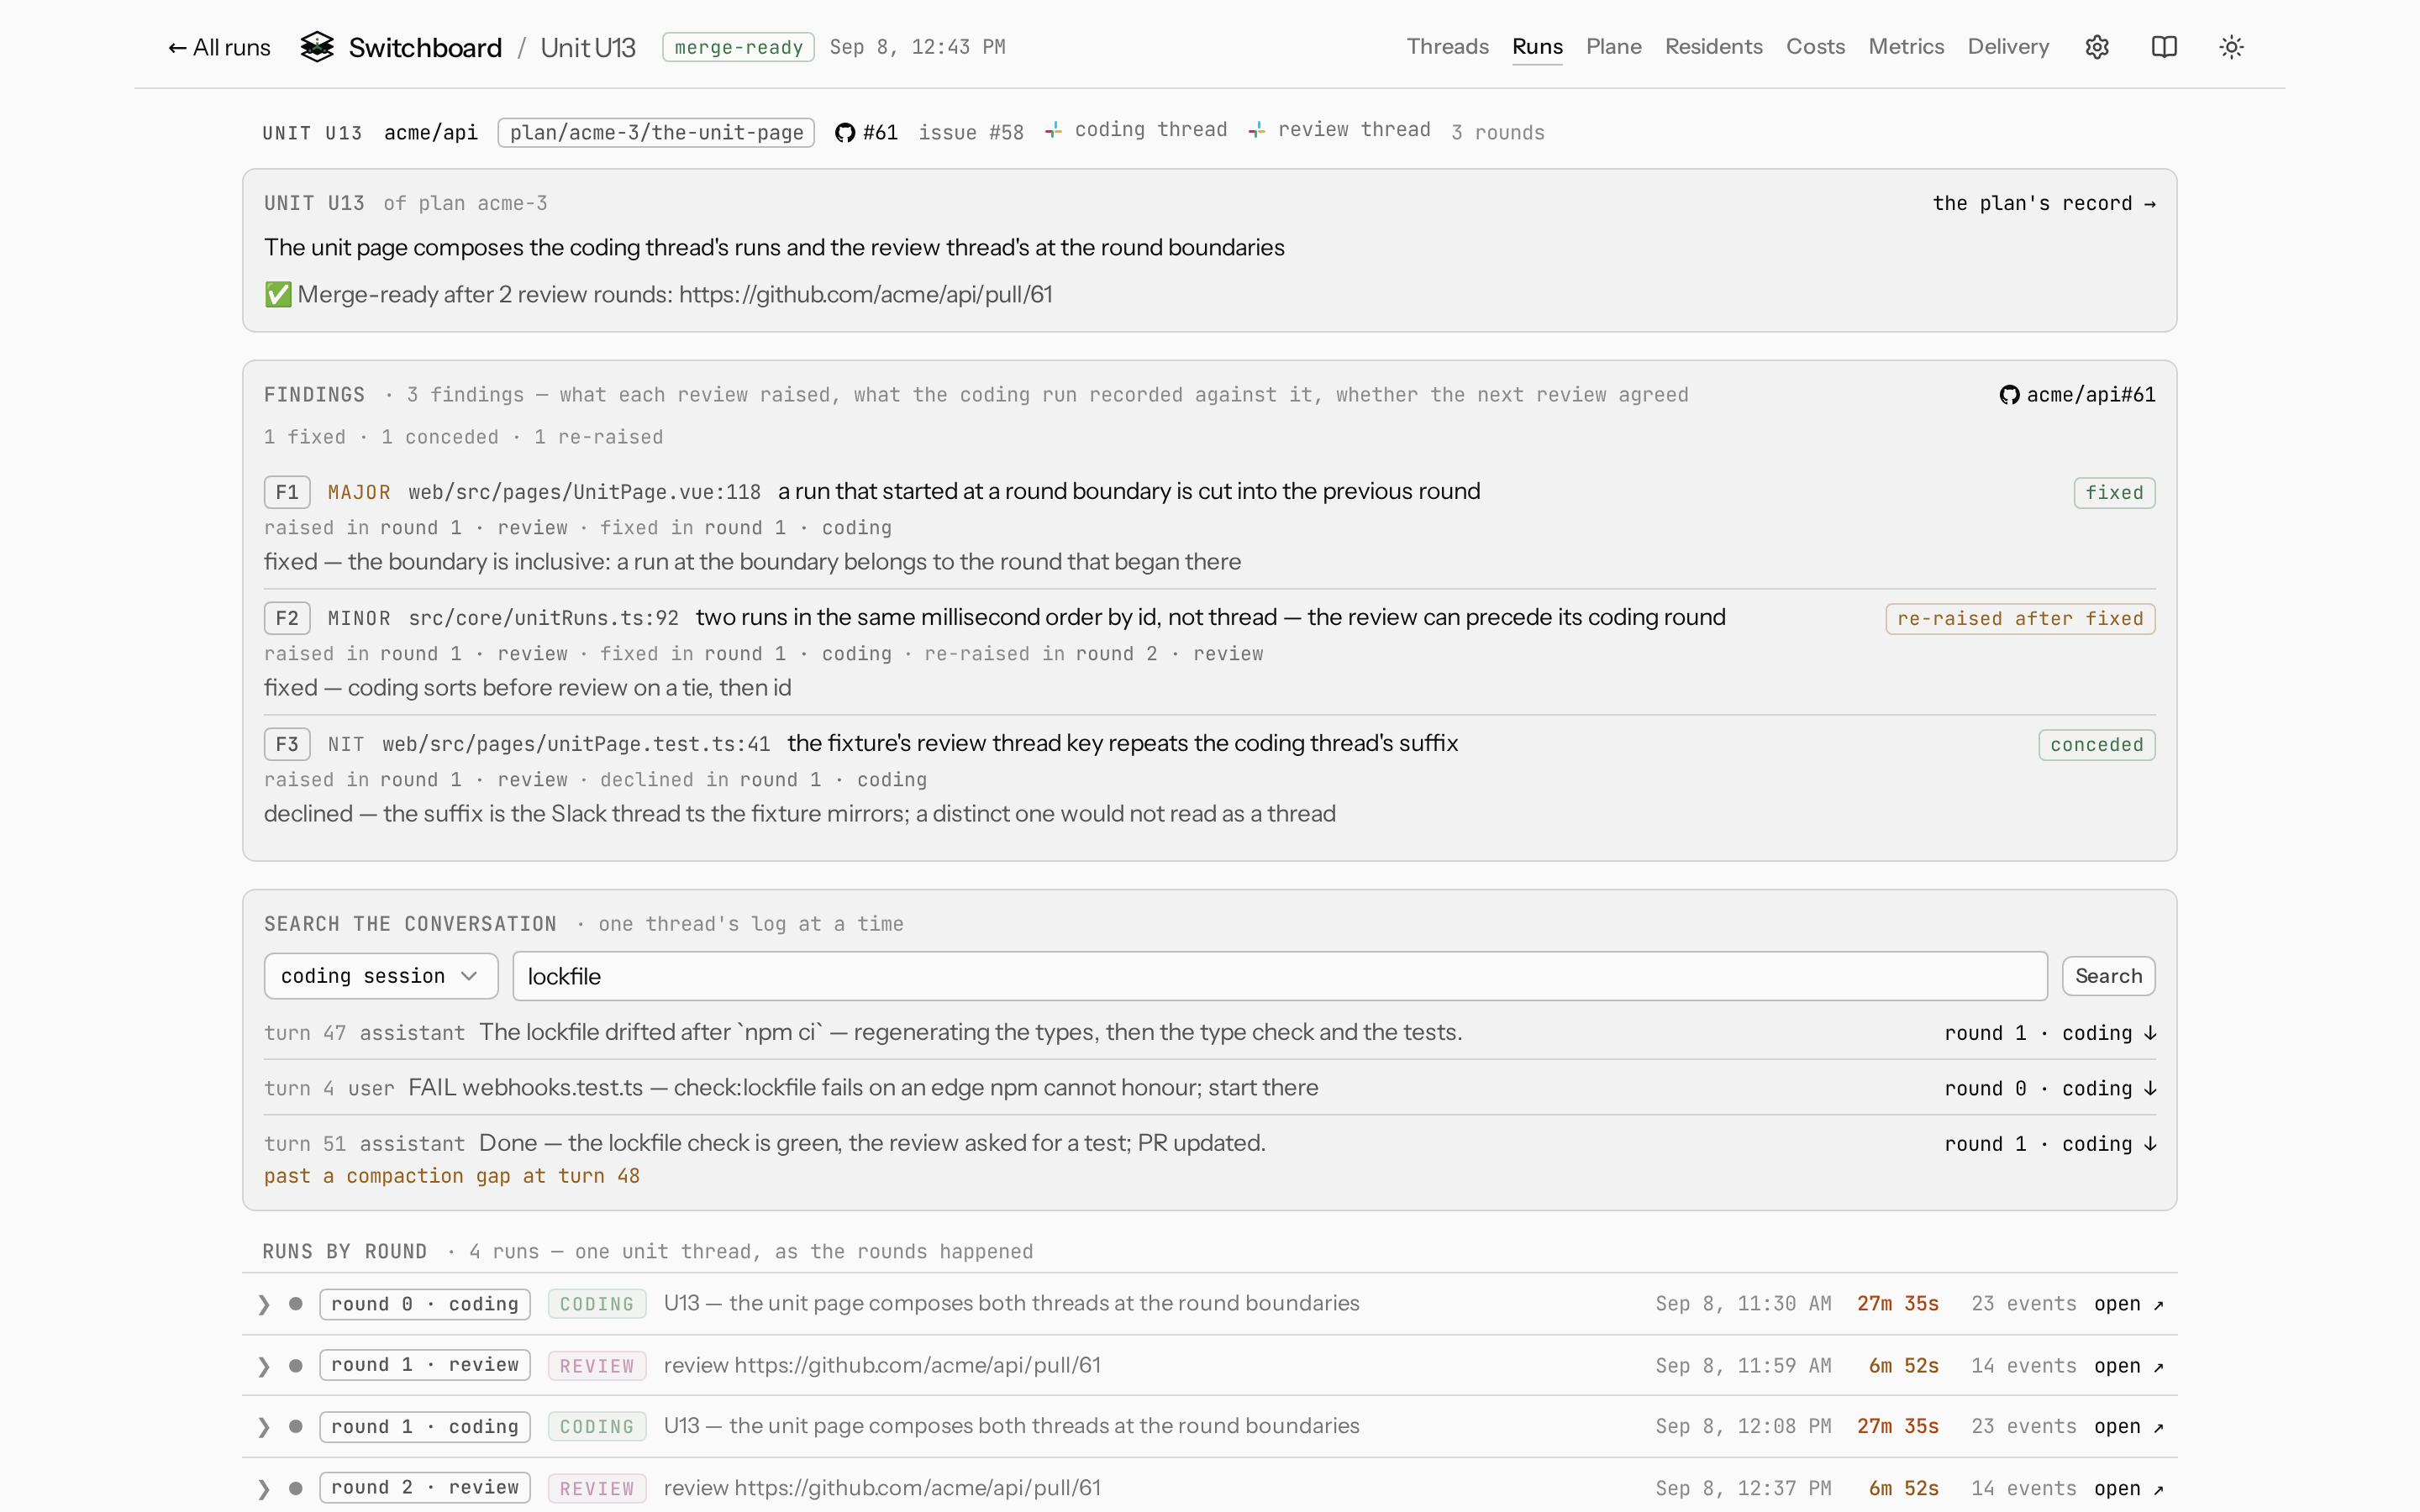
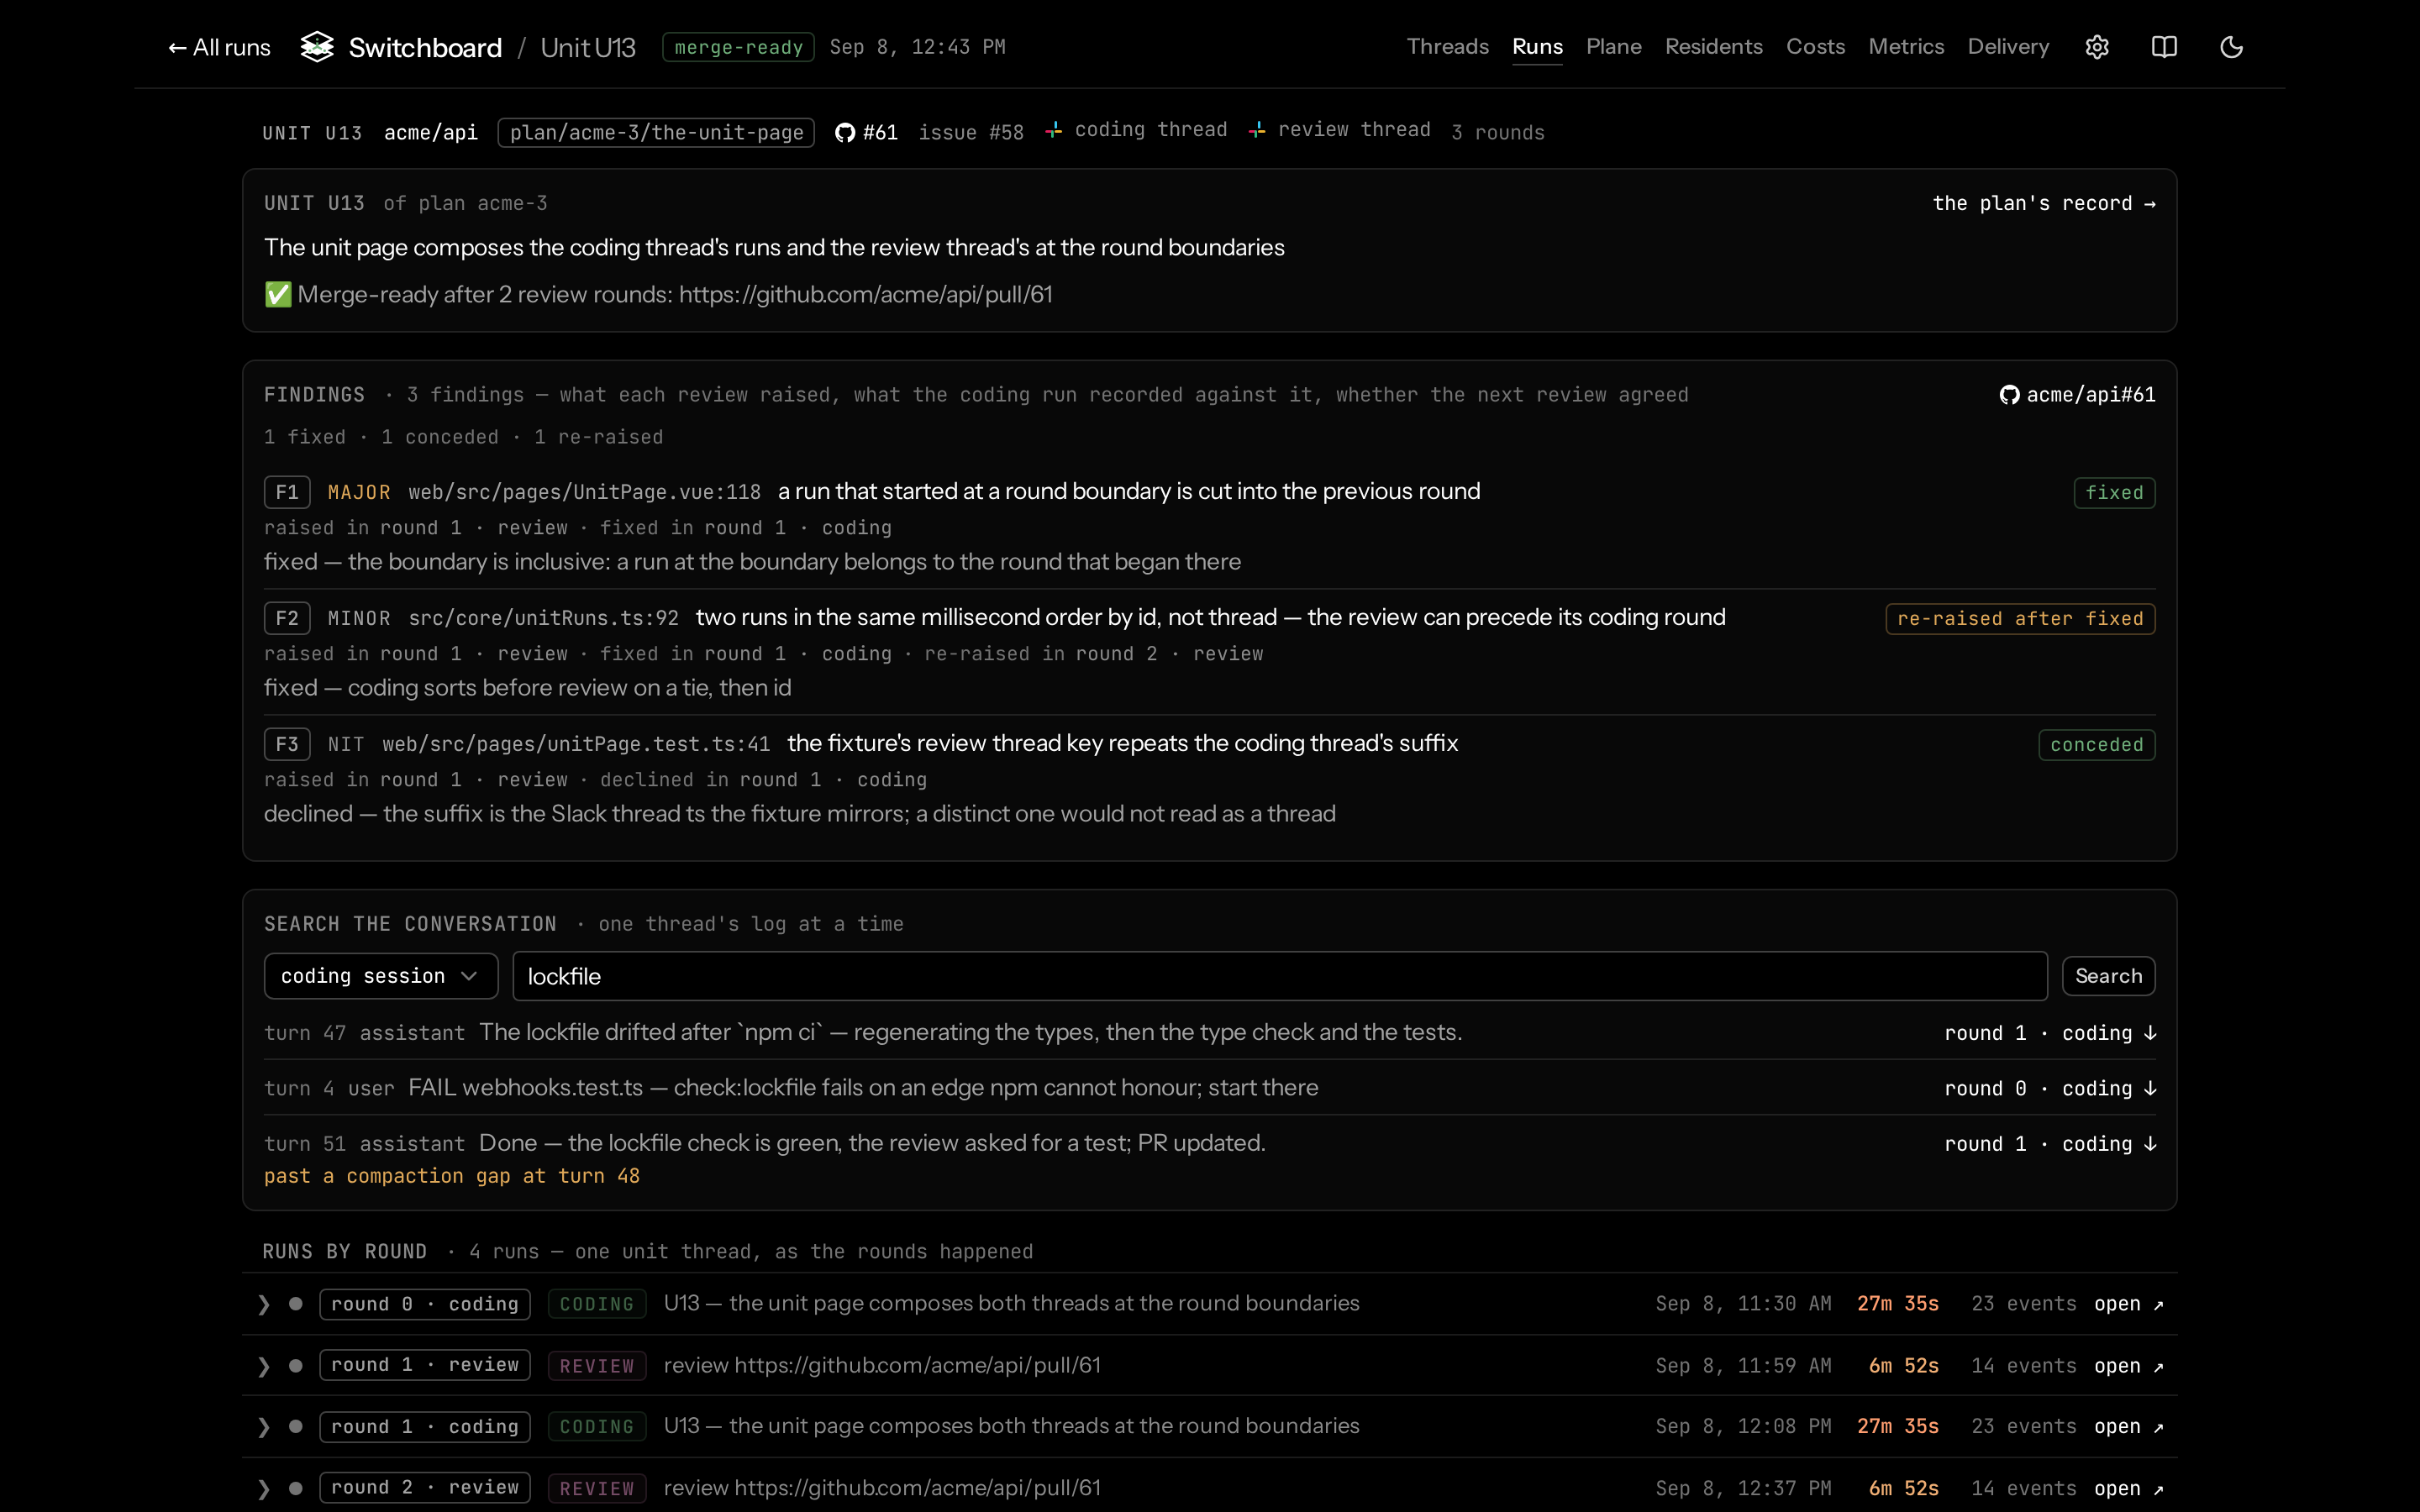
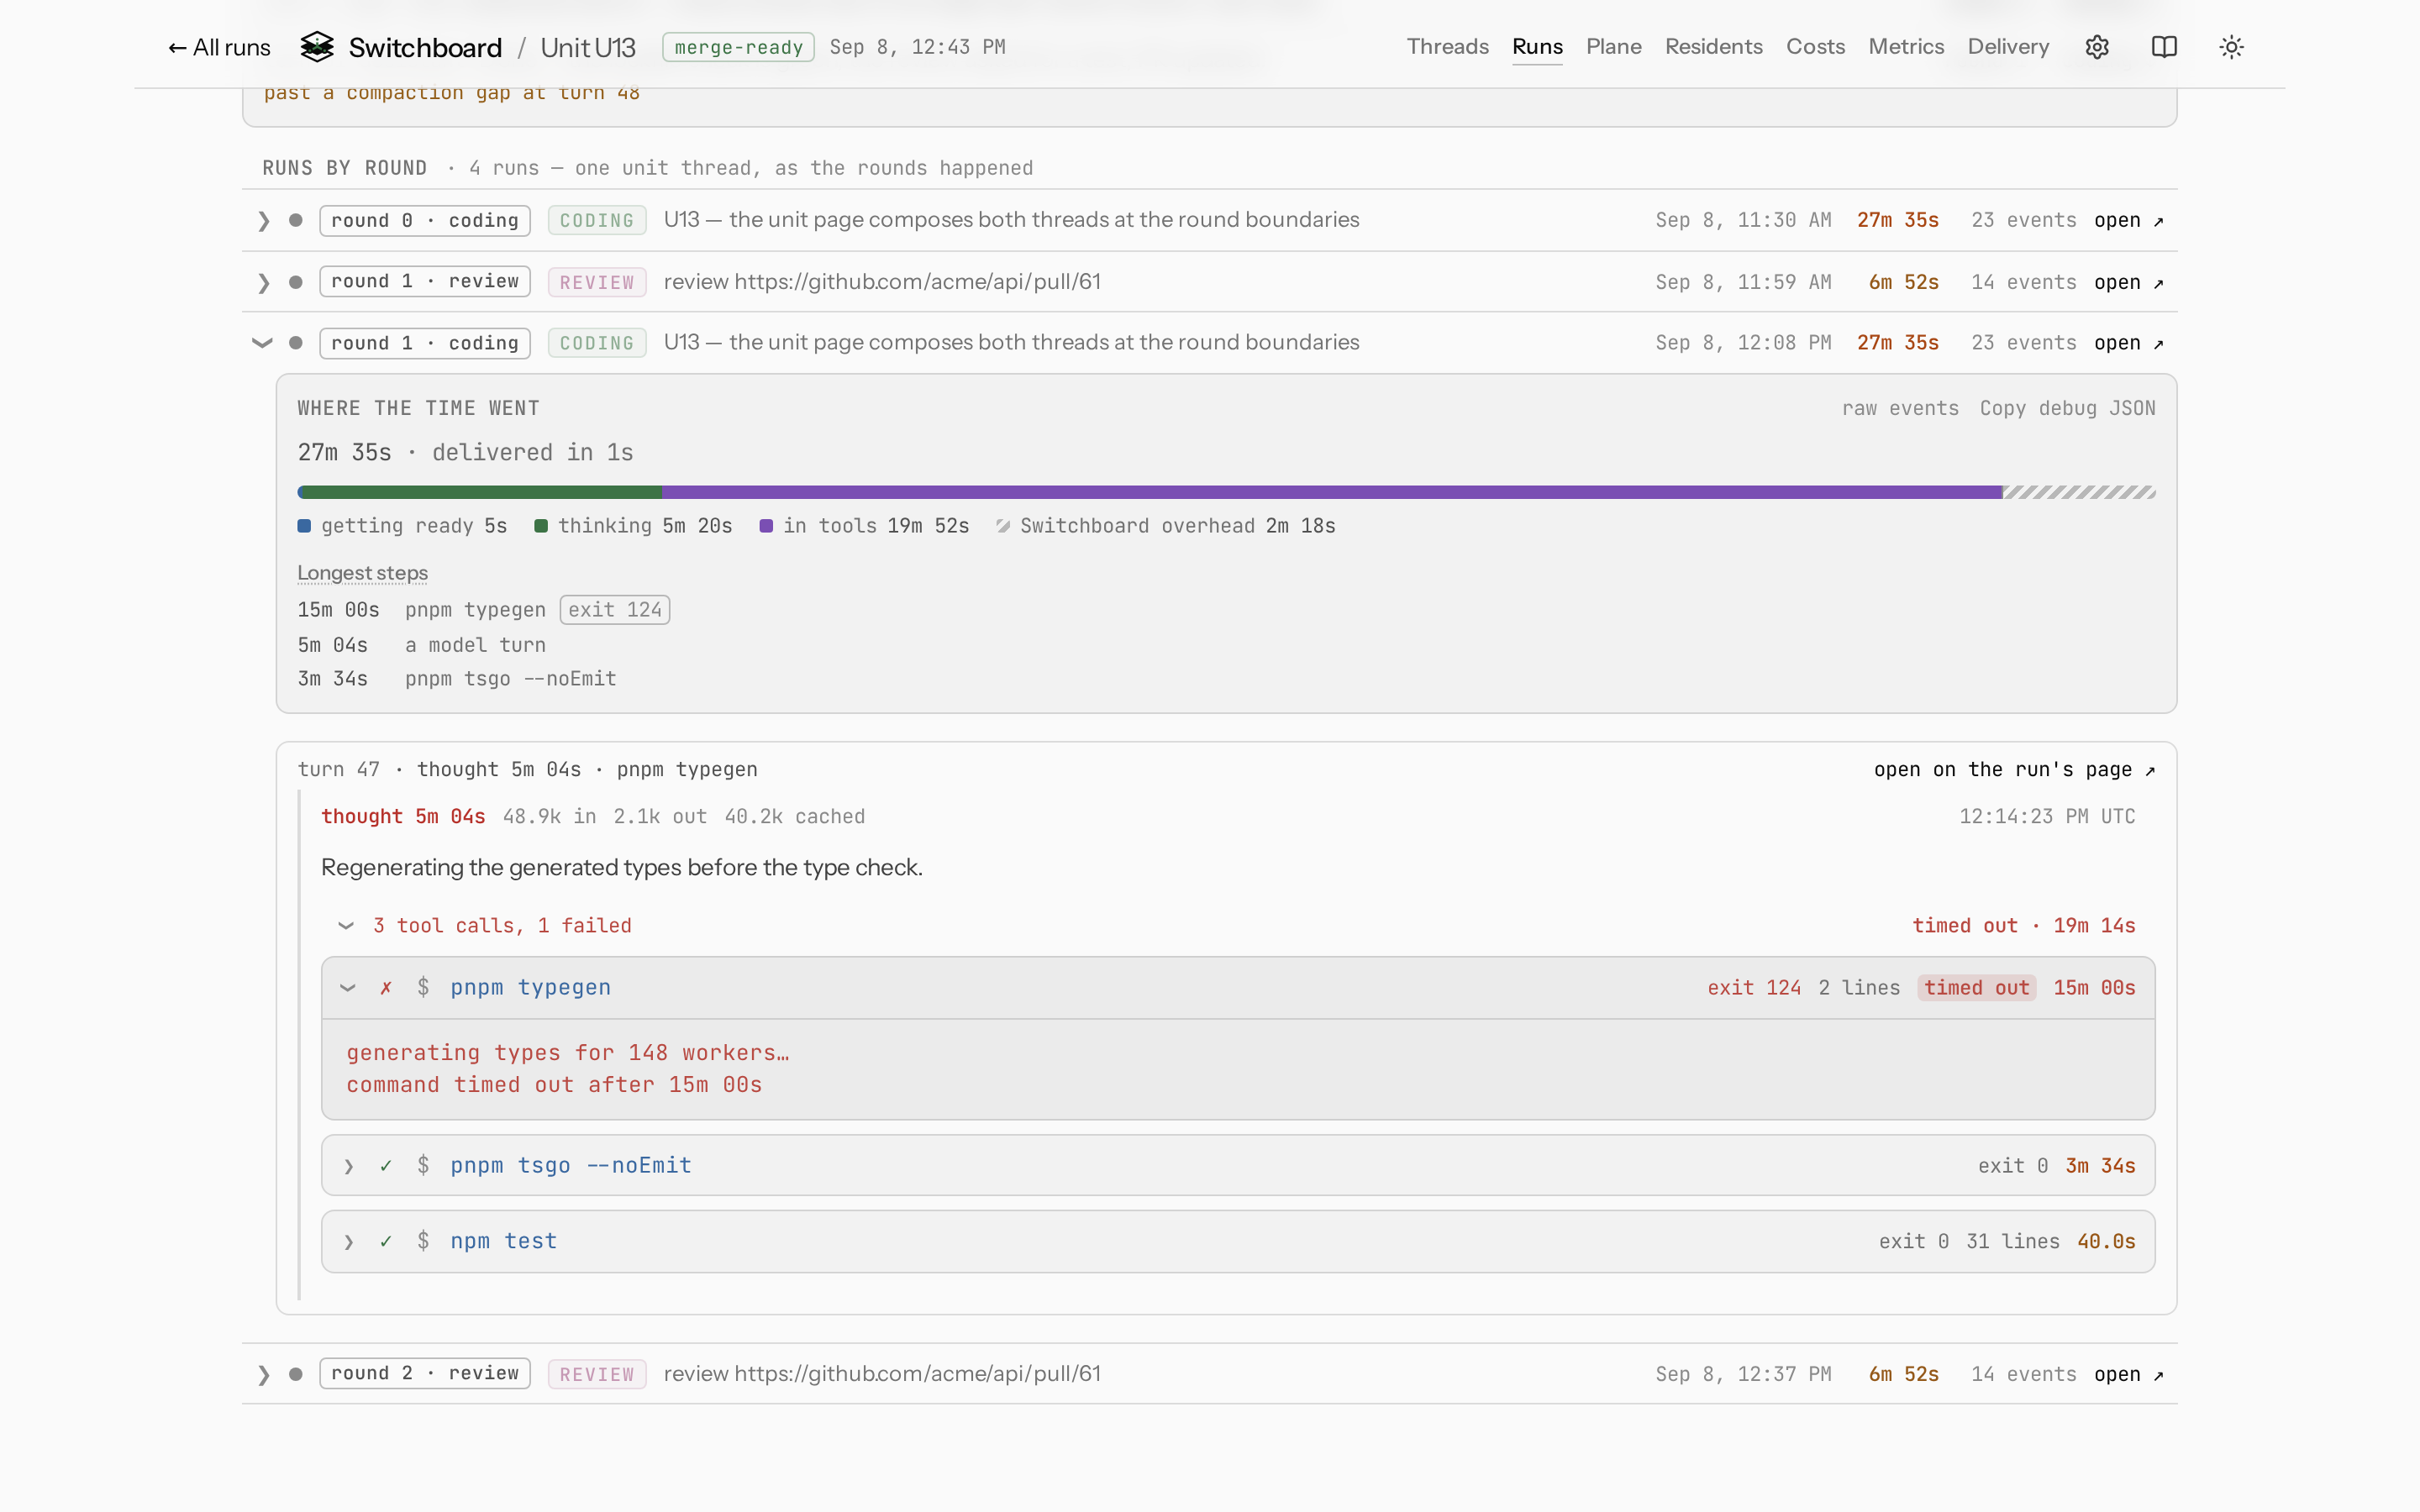
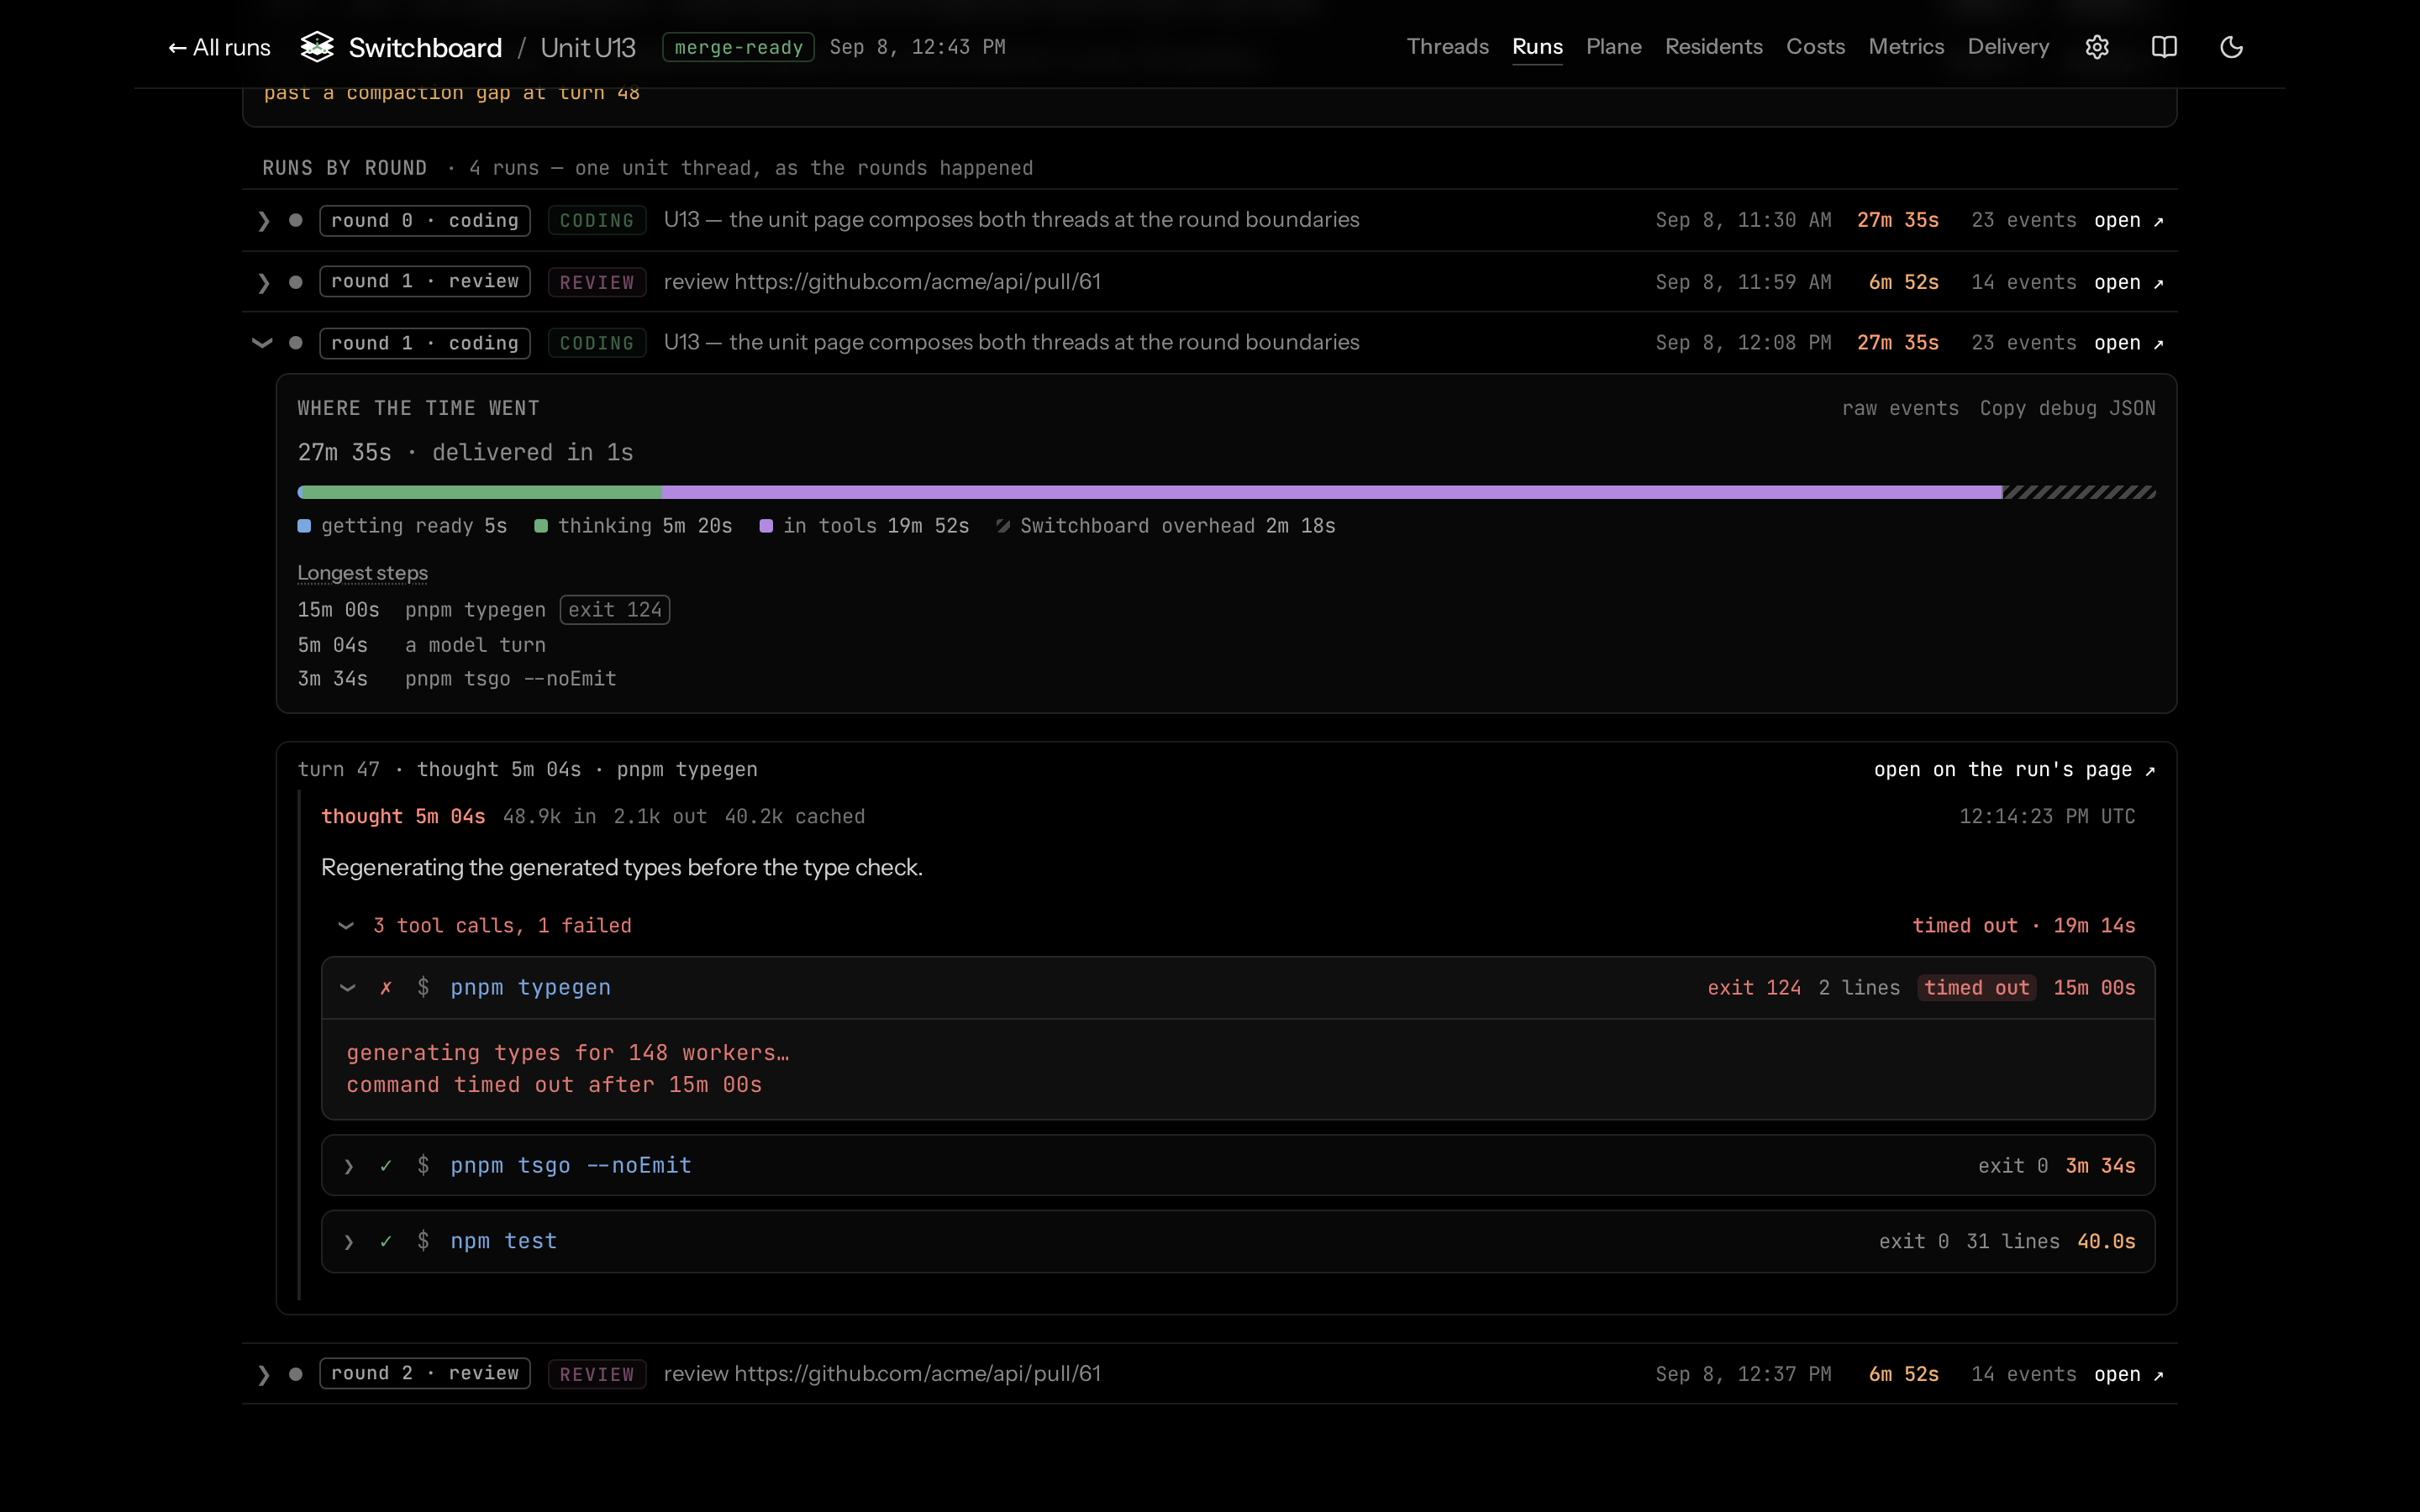
Screenshot regeneration receipt for head All 22 surfaces were rendered in light and dark through Before/after comparisons — main left, regenerated right
Original empty-state detail: All regenerated captures — light and darkConductor page Costs Costs models Costs users Home conversation Home empty Home live Metrics Plane Residents Review page Run page Runs index Runs index viewing as Scheduled Settings channel Settings installation Settings MCPs Unit coding only Unit page Unit search Unit search landed Image URLs are deliberately public, token-free artifact copies and expire under artifact retention. All captures and comparison sheets are also attached to the request thread. |
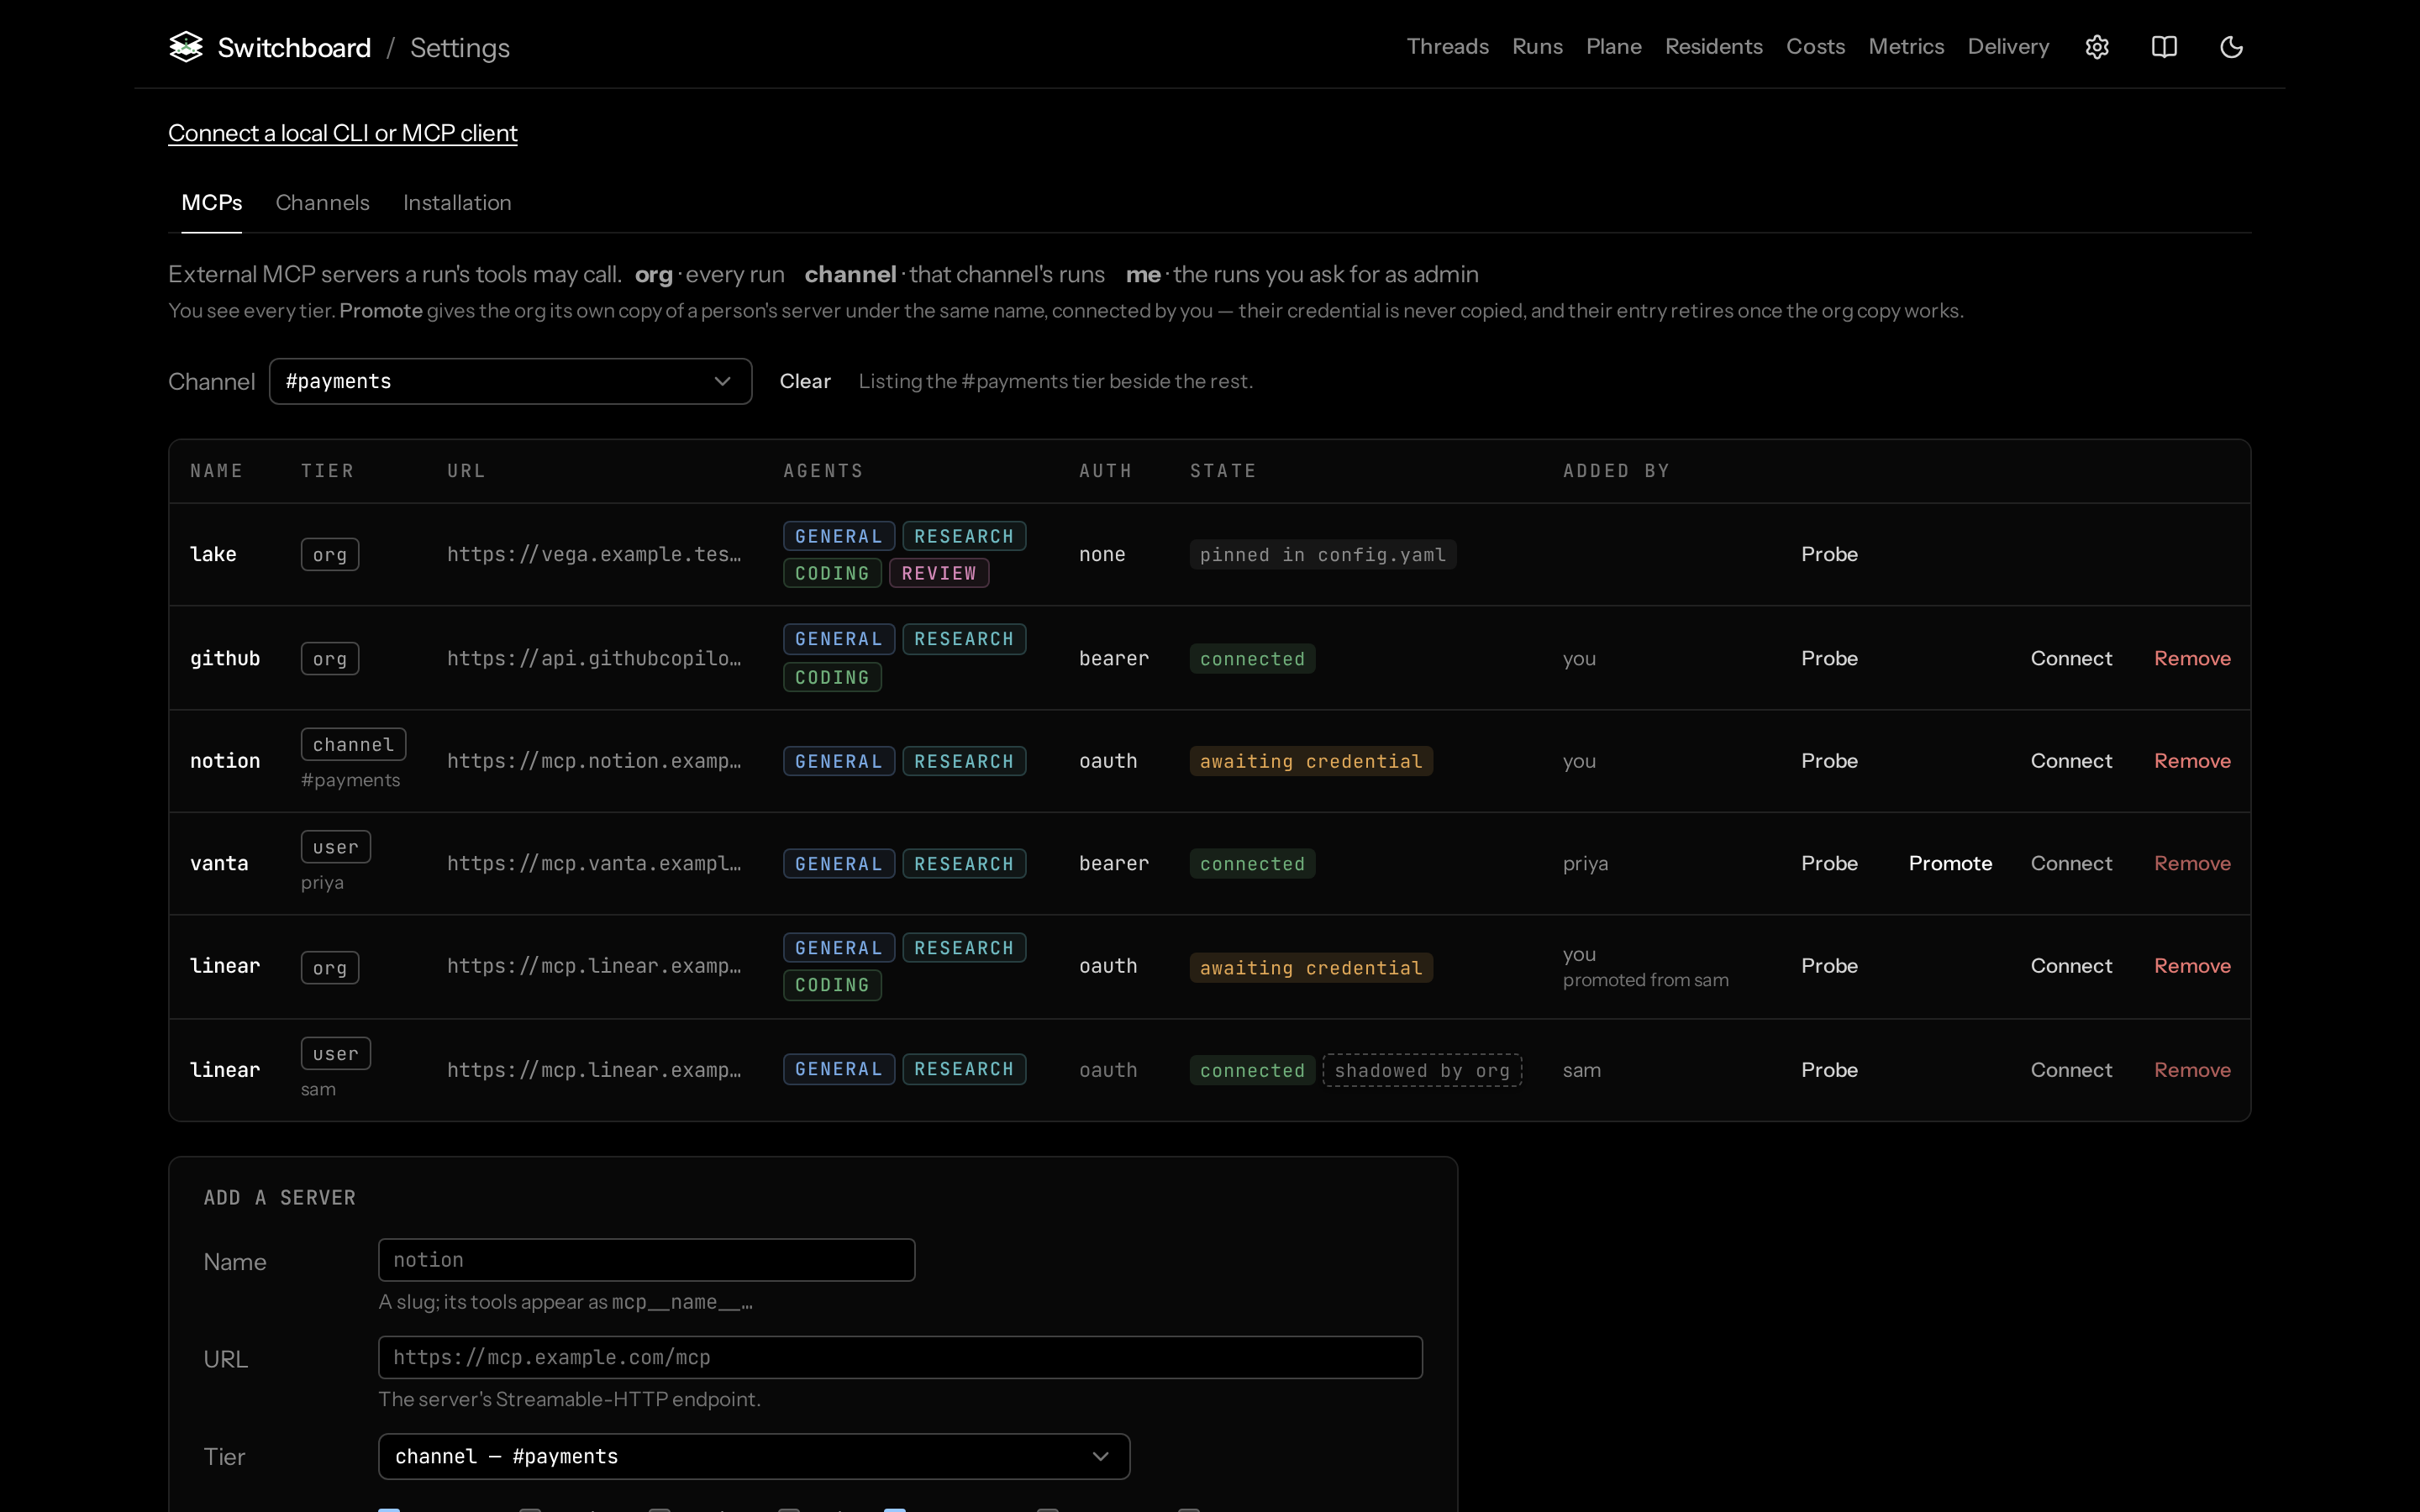
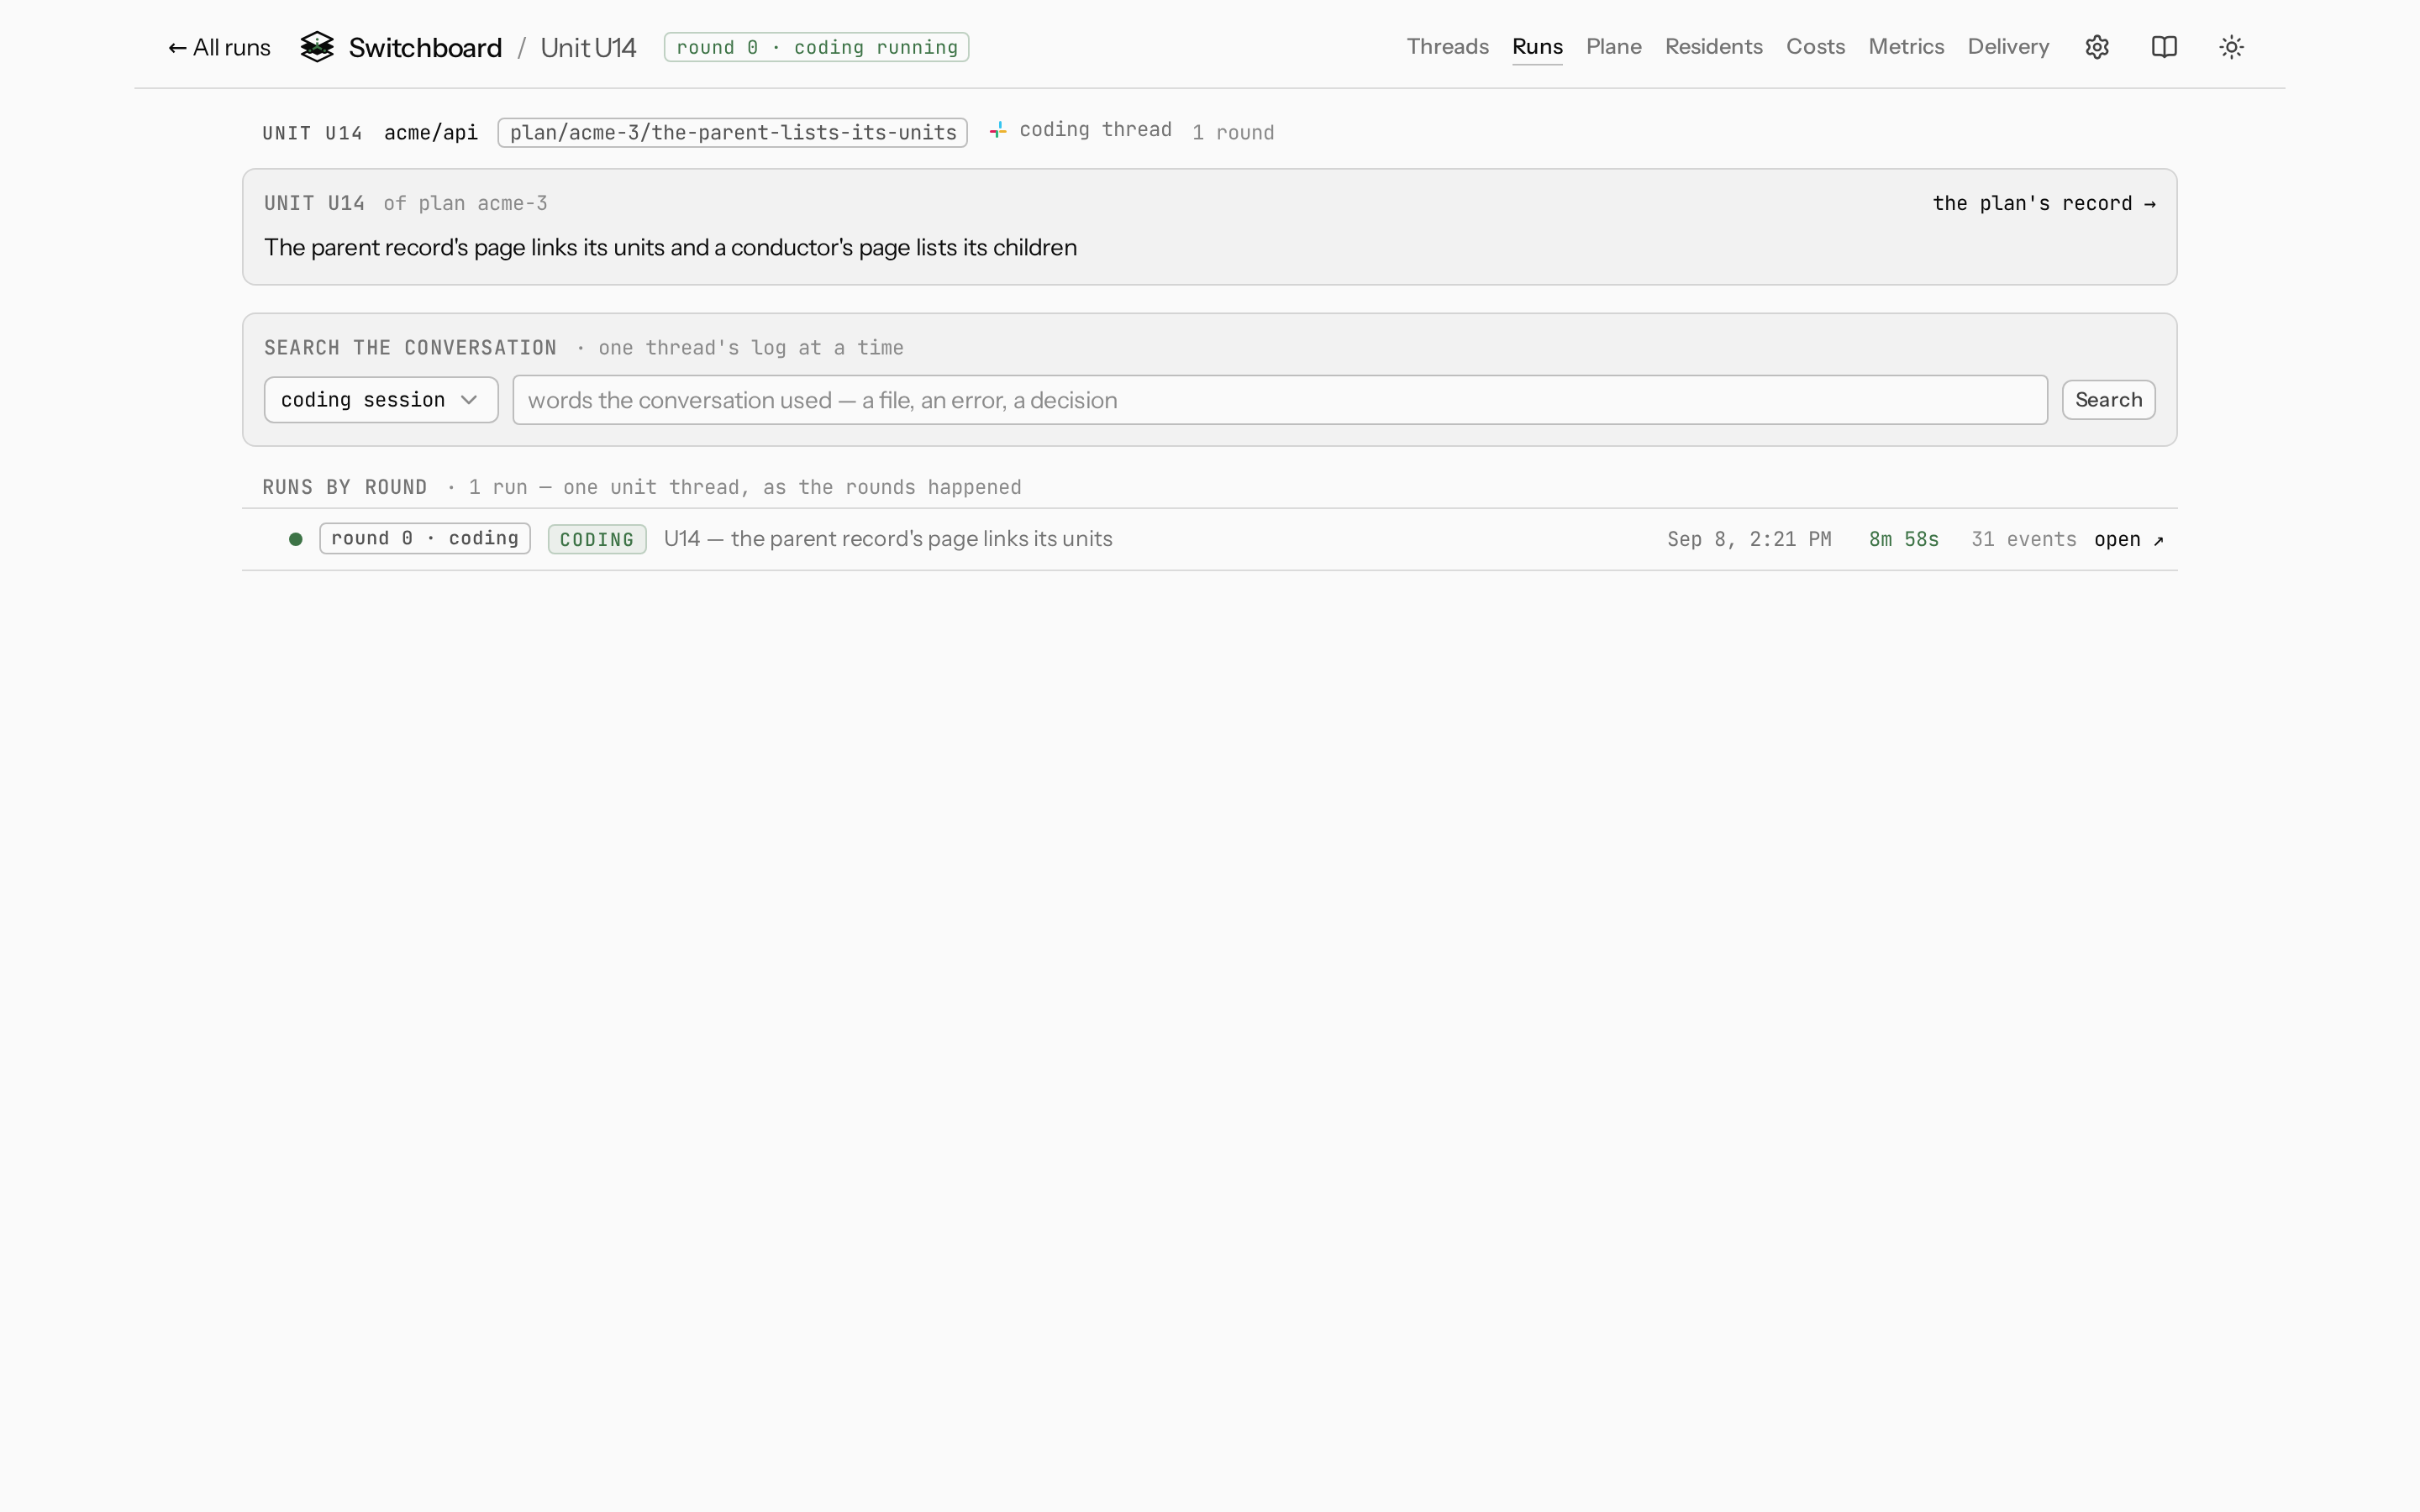
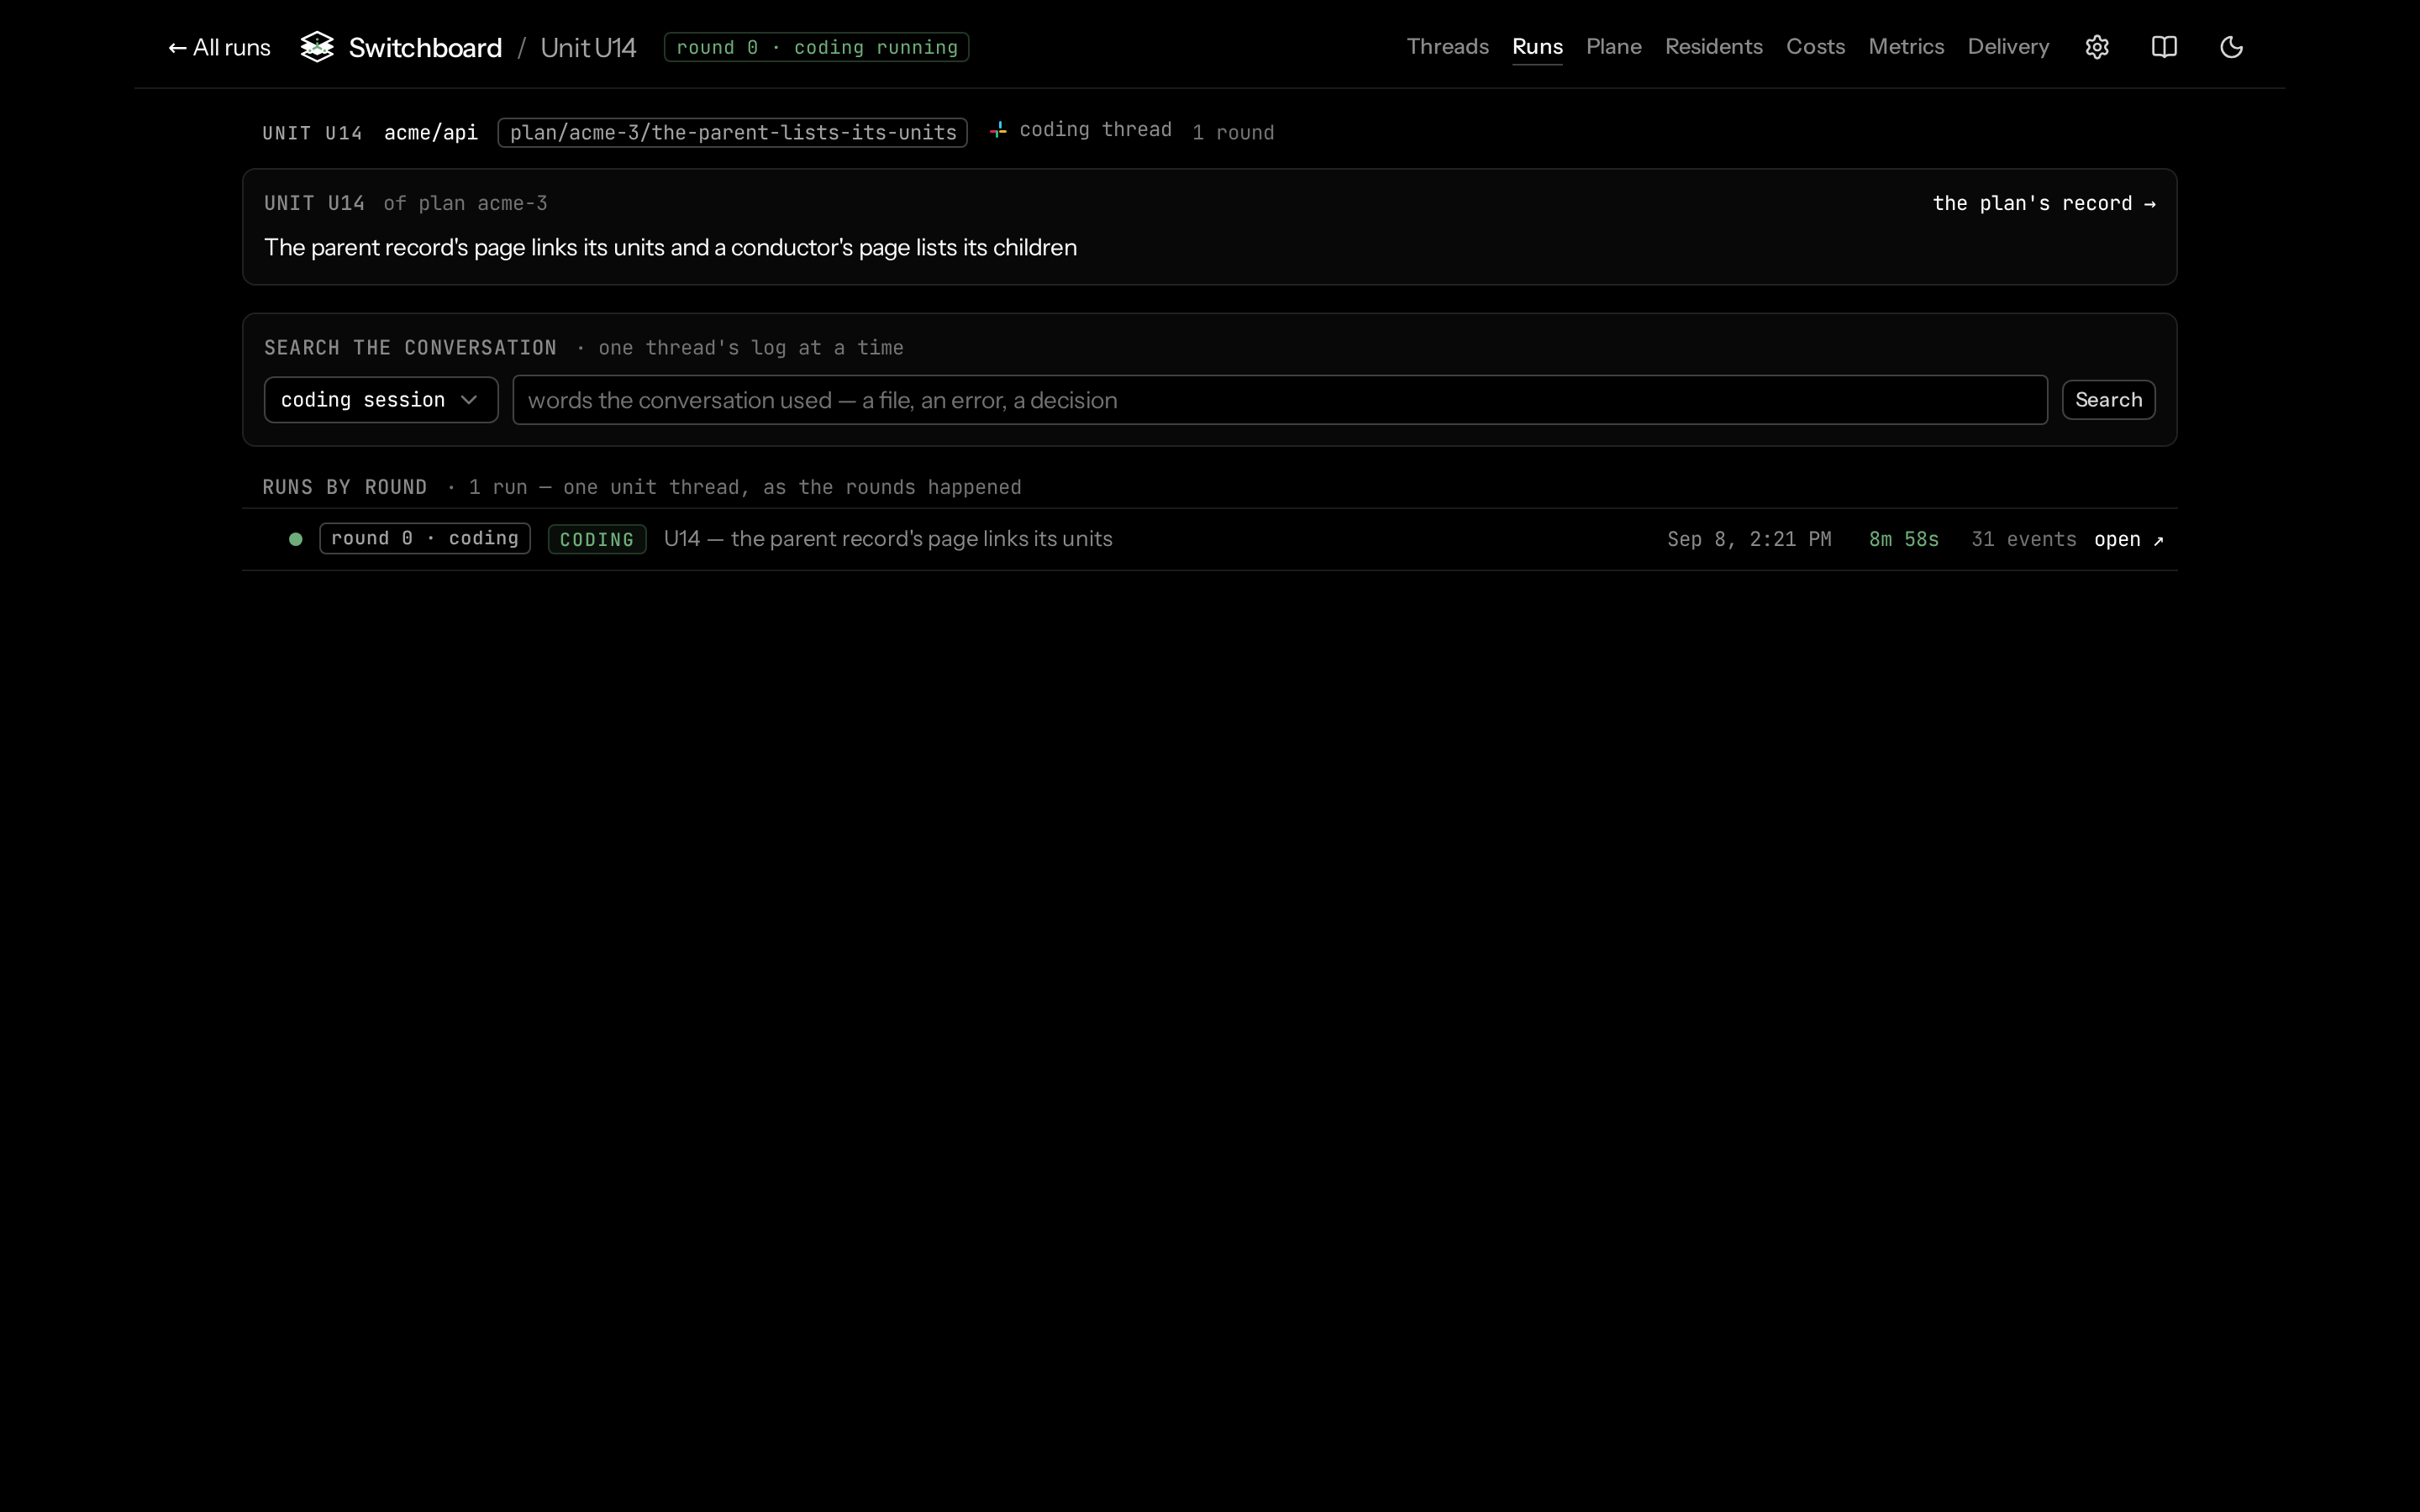
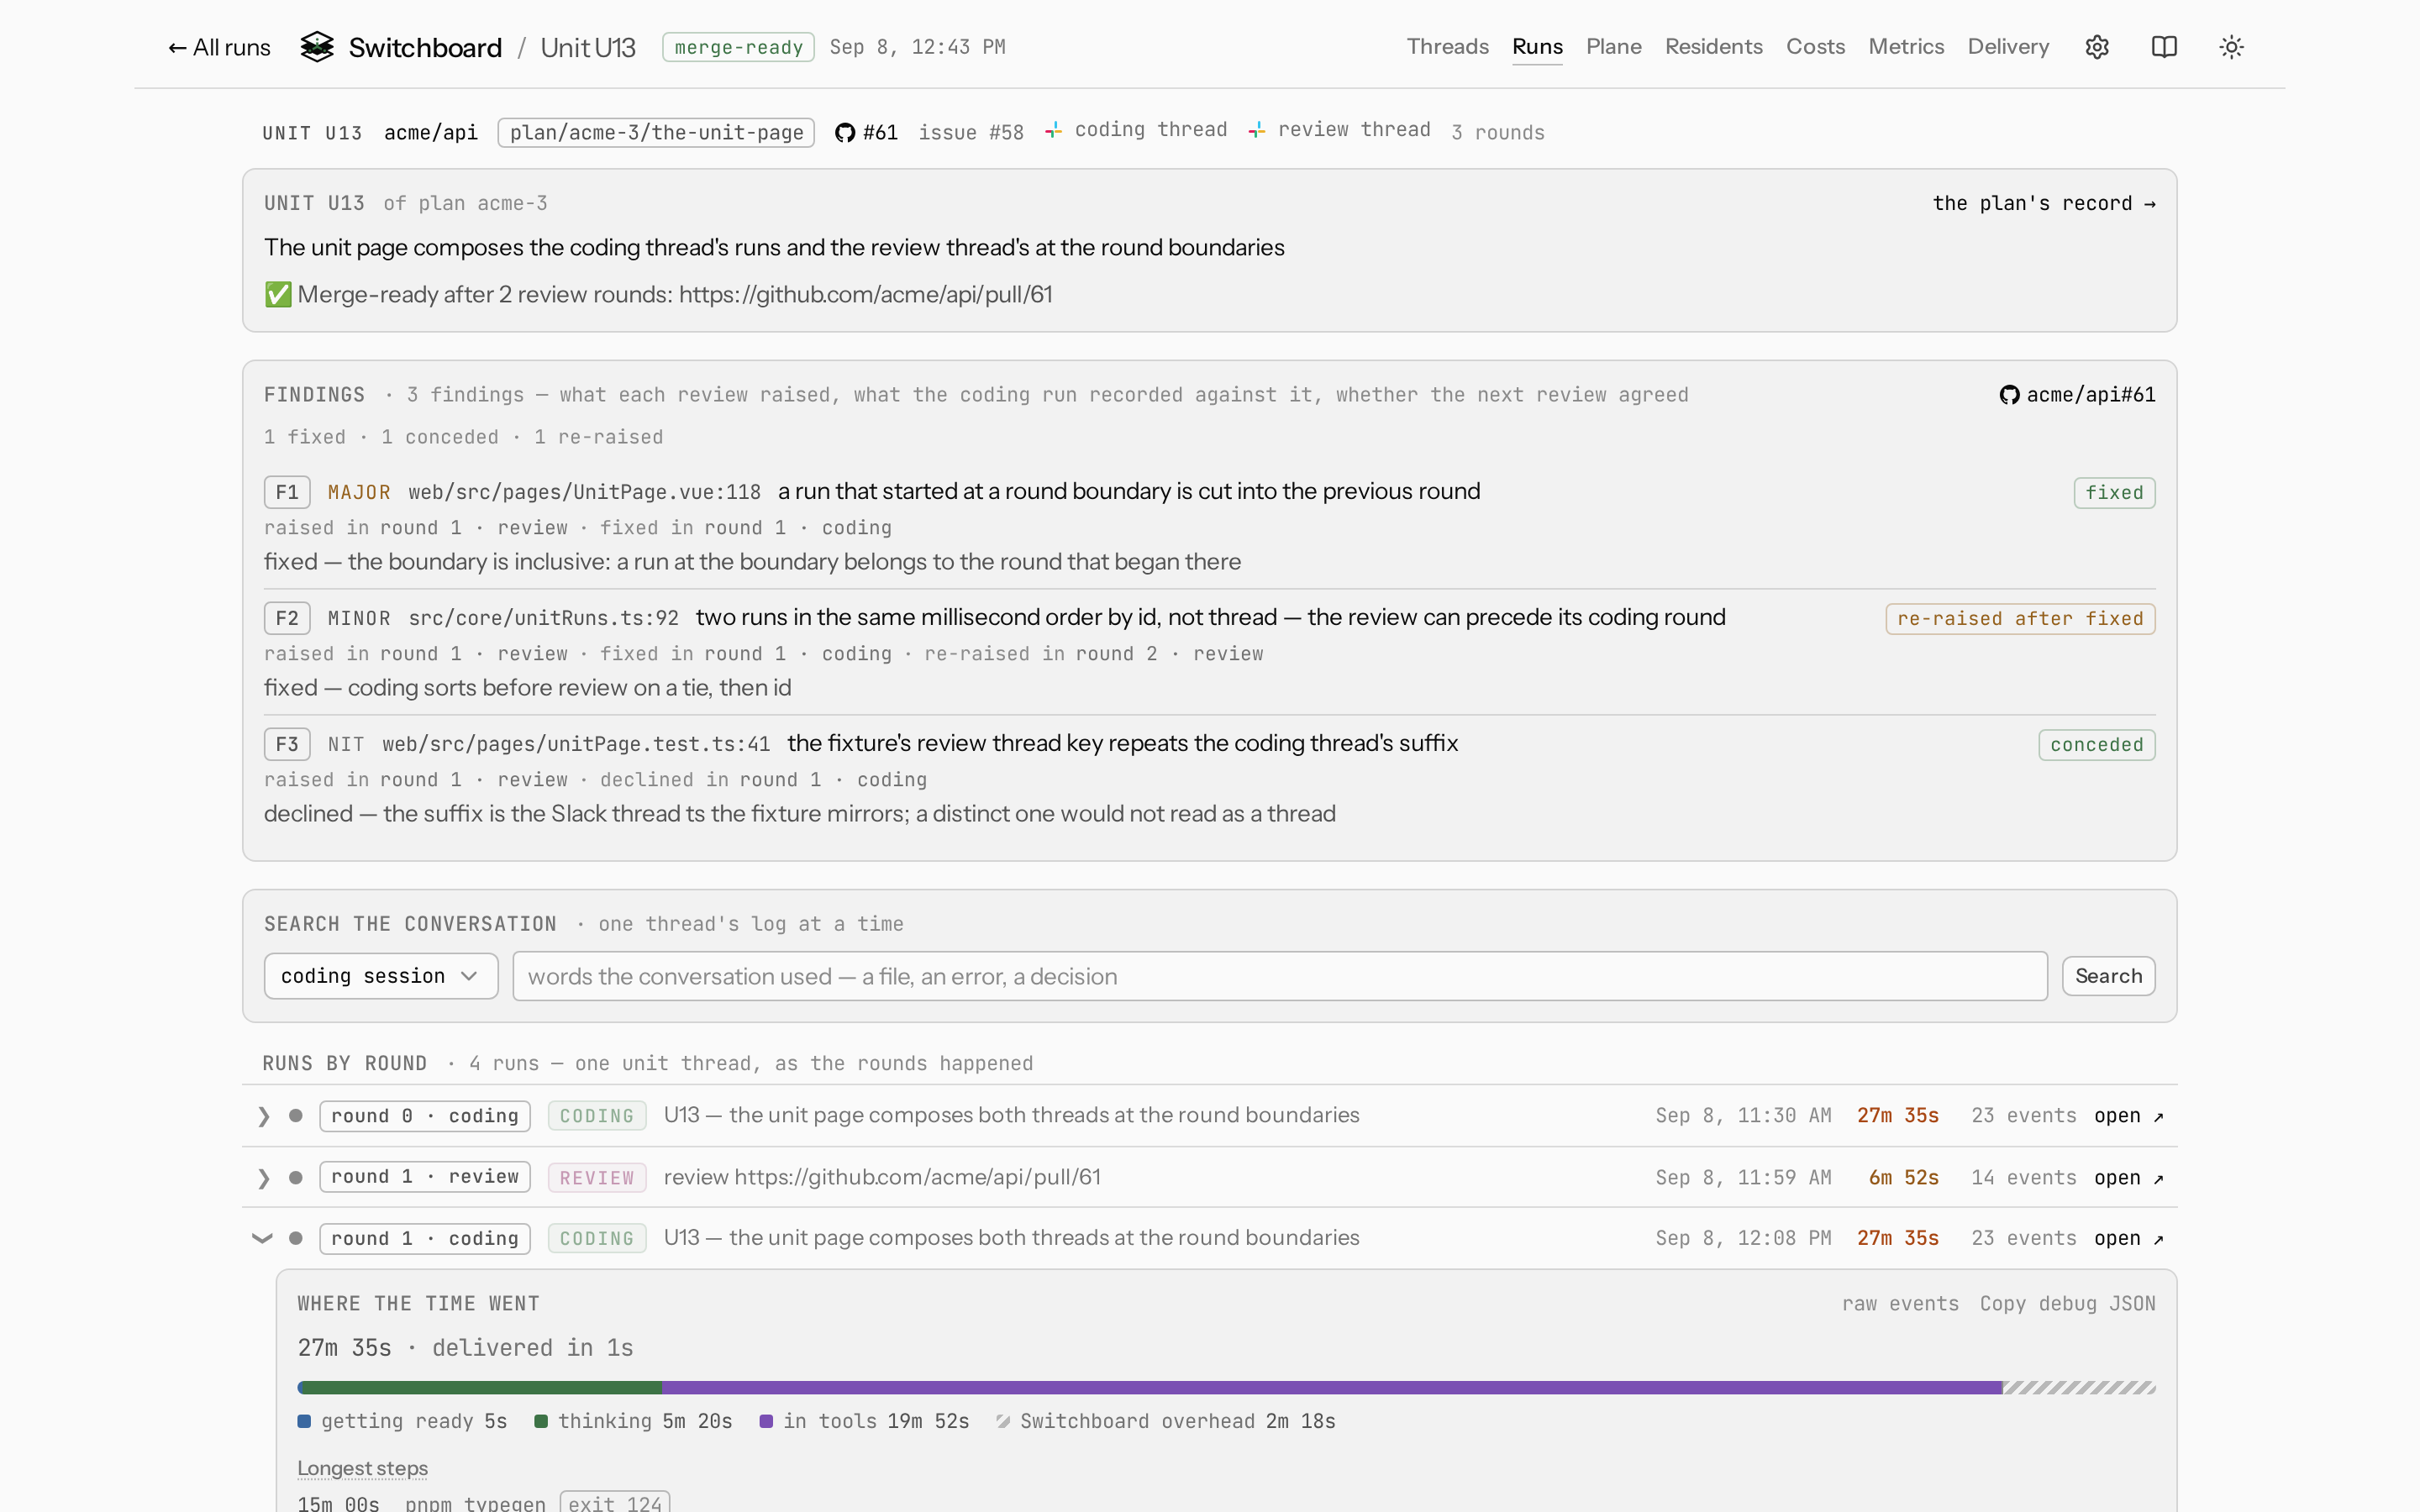
Co-Authored-By: coreplane-switchboard[bot] <318072483+coreplane-switchboard[bot]@users.noreply.github.com>

1 participant

Bumps source-map-js from 1.2.1 to 1.2.2.
Release notes
Sourced from source-map-js's releases.
Changelog
Sourced from source-map-js's changelog.
Commits
0a1d3341.2.24c6fa26Update changelogcf76580Fix denial of service from malicious indexed source maps (CVE-2026-93749) (#79)7899a86Fix crash when executing browser with CSP script-src that don't permit unsafe...Dependabot will resolve any conflicts with this PR as long as you don't alter it yourself. You can also trigger a rebase manually by commenting
@dependabot rebase.Dependabot commands and options
You can trigger Dependabot actions by commenting on this PR:
@dependabot rebasewill rebase this PR@dependabot recreatewill recreate this PR, overwriting any edits that have been made to it@dependabot show <dependency name> ignore conditionswill show all of the ignore conditions of the specified dependency@dependabot ignore this major versionwill close this PR and stop Dependabot creating any more for this major version (unless you reopen the PR or upgrade to it yourself)@dependabot ignore this minor versionwill close this PR and stop Dependabot creating any more for this minor version (unless you reopen the PR or upgrade to it yourself)@dependabot ignore this dependencywill close this PR and stop Dependabot creating any more for this dependency (unless you reopen the PR or upgrade to it yourself)You can disable automated security fix PRs for this repo from the Security Alerts page.
Polylane reviews this pull request when you ask: